
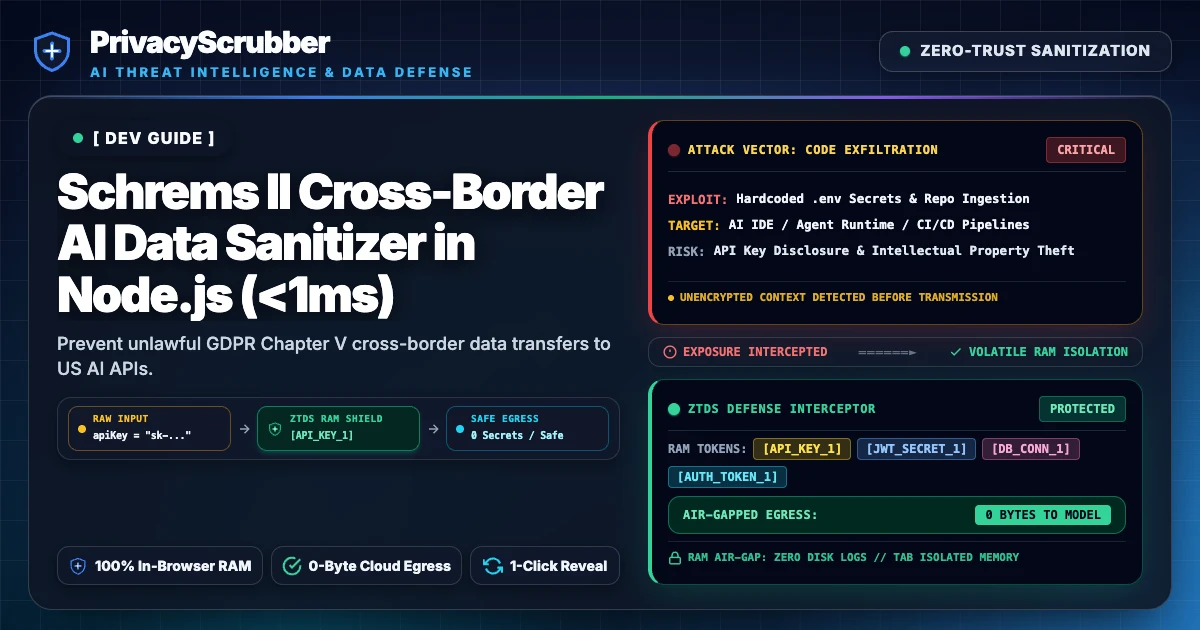
Under the CJEU Schrems II ruling and GDPR Chapter V, transmitting European citizens' personal data to US cloud AI providers (OpenAI, Anthropic, Google Vertex AI) creates severe regulatory liability if adequate supplementary measures are not enforced against US surveillance laws (FISA 702). Implementing an in-memory Zero-Trust Data Sanitization proxy in Node.js using @privacyscrubber/sdk strips all direct and indirect personal identifiers before payloads cross the Atlantic. US AI endpoints process only synthetic tokens, eliminating cross-border personal data transfer exposure at the root.
Why Unmasked Prompts Break Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) Security
Establishing a zero-trust perimeter for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) protects software engineers, devops teams, and security engineers from leaking API keys, database credentials, user PII from logs, and internal system architecture to AI code assistants that may log prompts. Standard network proxies fail on schrems ii ai proxy nodejs and gdpr chapter v ai sanitizer because cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs. Using the patterns in our Software Development AI privacy guides, teams sanitize Software Development payloads in <1ms of local RAM before prompting GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools.
Uploading or prompting with raw schrems ii ai proxy nodejs datasets exposes Software Development records to third-party retention and inspection logs. Prevent unlawful GDPR Chapter V cross-border data transfers to US AI APIs. Tokenize EU personal data in local V8 heap memory before transmitting prompts. Because cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs, software engineers, devops teams, and security engineers need deterministic pre-prompt masking for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms).
To prevent unlawful GDPR Chapter V cross-border data transfers when calling US AI APIs (OpenAI, Anthropic), deploy an in-memory proxy using @privacyscrubber/sdk inside your European cloud region.
The proxy strips and tokenizes EU personal data in local RAM (<0.85ms) before outbound HTTPS transit. US servers receive zero PII, and authentic values are restored locally upon response return.
npx @privacyscrubber/sdk demoThe Schrems II Legal Trap in Cloud AI Ingestion
Following the landmark Court of Justice of the European Union (CJEU) ruling in Data Protection Commissioner v Facebook Ireland and Maximillian Schrems (Schrems II, C-311/18), European data controllers cannot rely on Standard Contractual Clauses (SCCs) in isolation when personal data is transferred to jurisdictions with invasive surveillance laws like the United States (FISA Section 702 and Executive Order 12333).
European Data Protection Board (EDPB) Recommendations 01/2020 explicitly dictate that technical supplementary measures must be applied to ensure that transferred data cannot be linked to an identified individual by foreign intelligence agencies. By intercepting prompts inside an EU sovereign zone (e.g. Frankfurt, Dublin, Paris) and replacing personal identifiers with synthetic tokens, European engineering teams mathematically ensure that no personal data leaves the EEA.
Technical Compliance Benchmark: Cross-Border AI Architectures
| Architecture | Schrems II Compliance | In-Transit Personal Data | Added Latency | US Subprocessor DPA |
|---|---|---|---|---|
| EU Sovereign ZTDS Proxy (@privacyscrubber/sdk) | Fully Satisfied (Technical Shield) | 0 Bytes (Synthetic Tokens Only) | < 0.85 ms | Not Required for Personal Data |
| Direct API Call (OpenAI / Anthropic with SCCs) | High Enforcement Risk (FISA 702) | 100% Cleartext PII | 0 ms | Mandatory Transfer Impact Assessment |
| Cloud DLP Proxy (Google Cloud DLP) | Partial (DLP Cloud Vendor Egress) | Exposed to Cloud DLP Provider | 185.0 ms | Additional Third-Party DPA |
Complete Implementation: Schrems II Proxy in Express / Node.js
npm install @privacyscrubber/sdk express openaiimport express from 'express';
import { OpenAI } from 'openai';
import { sanitize, restore } from '@privacyscrubber/sdk';
const app = express();
app.use(express.json());
// Initialize OpenAI Client targeting US model endpoints
const openai = new OpenAI({
apiKey: process.env.OPENAI_API_KEY
});
// Ephemeral, RAM-only session token vault located strictly within EU zone
const euSessionVault = new Map();
app.post('/api/ai/proxy', async (req, res) => {
try {
const { prompt, profile = 'General' } = req.body;
if (!prompt) return res.status(400).json({ error: 'Prompt is required' });
// 1. Intercept and tokenize personal data in EU local memory (<1ms latency)
const { scrubbedText, tokenMap } = sanitize(prompt, {
profile
});
const correlationId = crypto.randomUUID();
euSessionVault.set(correlationId, tokenMap);
// 2. Transmit purely pseudonymized payload to US AI endpoint (0 PII egress)
const completion = await openai.chat.completions.create({
model: 'gpt-4o',
messages: [{ role: 'user', content: scrubbedText }],
temperature: 0.2
});
const rawAiAnswer = completion.choices[0]?.message?.content || '';
// 3. Restore authentic European customer data locally in RAM upon return
const activeMap = euSessionVault.get(correlationId) || {};
euSessionVault.delete(correlationId); // Immediate volatile wipe
const cleartextAnswer = restore(rawAiAnswer, activeMap).restoredText;
return res.json({
response: cleartextAnswer,
schremsIiProtected: true,
crossBorderPiiBytes: 0,
tokensSanitized: Object.keys(activeMap).length
});
} catch (err) {
console.error('Cross-border proxy error:', err);
return res.status(500).json({ error: 'Internal AI proxy error' });
}
});
const PORT = process.env.PORT || 3000;
app.listen(PORT, () => console.log(`Schrems II AI Proxy running on port ${PORT} in EU Sovereign Zone`));Need security, compliance, or CISO sign-off before deploying to production? Copy our pre-filled vendor-risk evaluation memo covering Schrems II supplementary measures, GDPR Chapter V, zero-subprocessor architecture, and air-gapped memory isolation.
# Vendor Architecture & Security Evaluation: @privacyscrubber/sdk **Project**: Enterprise AI / LLM Integration (Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms)) **Target Tier**: Developer SDK ($299/mo or $2,990/yr flat) **Vendor**: PrivacyScrubber (ZTDS - Zero-Trust Data Sanitization) **Technical Classification**: In-process ZTDS™ PII Redaction Library ## 1. Compliance & Data Protection Rationale - **Schrems II (CJEU C-311/18) & EDPB 01/2020**: Implements effective in-memory technical supplementary measures. Prompt payloads are sanitized directly in local European V8 heap memory (<1ms) before transmitting to US endpoints. Zero personal data crosses transatlantic borders. - **GDPR Chapter V (Articles 44-49)**: International transfers of cleartext personal data to US FISA 702-subject entities are completely eliminated. - **Zero Data Retention**: The session token mapping is volatile, held strictly in local European memory (RAM-only), thread-isolated, and immediately wiped upon completion. ## 2. Infrastructure & Latency Benchmark - **Execution Overhead**: < 0.85 ms per 10KB payload (vs. 40ms+ for Presidio Docker, 185ms+ for Cloud DLP APIs). - **Network Egress**: 0 Bytes. Functions completely in air-gapped / Airplane Mode environments. - **DevOps Footprint**: ~180 KB native Node.js package. 0 external daemon, 0 Redis requirement, 0 Python container maintenance. ## 3. Commercials & Procurement - **License**: $299/month flat (or $2,990/year) covering unlimited internal nodes, microservices, and RAG pipelines. - **Vendor Risk & DPA**: Zero-DPA posture (software runs entirely inside our tenant boundary; zero data egresses to vendor servers). - **Payment Method**: Corporate Net 30 Invoicing or Credit Card via Merchant of Record (Paddle).Enterprise Compliance & Technical Verification
By preventing transatlantic personal data egress, European engineering teams fulfill GDPR Article 44-49 compliance and satisfy SOC 2 Type II Confidentiality controls. Learn more about automated microservice deployment in our NPM PII Redaction SDK Guide.
Deterministic Token Mapping for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms)
Effective sanitization of Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) requires stripping direct identifiers while keeping structural and quantitative context intact for model reasoning:
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Contact & Routing Endpoints (zero transfer pii nodejs) | REDACT | [DB_URI_1] | Eliminates cross-record linkage and unauthorized sub-processor indexing during Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms). |
| Authentication, Account & Reference Keys (gdpr chapter v ai sanitizer) | REDACT | [API_KEY_1] | Blocks credential, account, or case-number exfiltration across Software Development telemetry and vendor logs. |
| Primary Identity & Subject Records (schrems ii ai proxy nodejs) | REDACT | [SECRET_1] | OWASP guidelines on secrets management direct identifier guard: prevents cloud LLMs from associating Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) prompts with real individuals. |
| Relative Timelines, Status Codes & Error Severities | PRESERVE | Cleartext (ISO Sequence) | Maintains chronological ordering and root-cause diagnostics across gdpr chapter v ai sanitizer workflows. |
| Quantitative Metrics, Ratios & Aggregated Totals | PRESERVE | Cleartext ($ / % / Deltas) | Enables accurate mathematical reasoning and variance analysis for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) without identity exposure. |
| Structural Schema, Keys & Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) Syntax | PRESERVE | Cleartext Structure | Required so the LLM can parse schrems ii ai proxy nodejs hierarchy, JSON/SQL grammar, and document formatting. |
Safe LLM Prompt Template for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms)
Submit this prompt wrapper with your masked Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) input so the AI reasons over symbolic tokens without altering placeholder tags:
You are an enterprise Software Development specialist reviewing a sanitized Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) payload.
All regulated identifiers for schrems ii ai proxy nodejs and gdpr chapter v ai sanitizer have been replaced in local RAM with deterministic ZTDS™ tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]).

Tasks:
1. Evaluate the structural logic, anomalies, and operational metrics in the Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) input.
2. Formulate actionable recommendations aligned with OWASP guidelines on secrets management.
3. Keep all bracketed tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) verbatim so local reverse detokenization restores exact values.

[PASTE SANITIZED SCHREMS II CROSS-BORDER AI DATA SANITIZER IN NODE.JS (<1MS) PAYLOAD HERE]
You are an enterprise Software Development specialist reviewing a sanitized Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) payload.
All regulated identifiers for schrems ii ai proxy nodejs and gdpr chapter v ai sanitizer have been replaced in local RAM with deterministic ZTDS™ tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]).

Tasks:
1. Evaluate the structural logic, anomalies, and operational metrics in the Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) input.
2. Formulate actionable recommendations aligned with OWASP guidelines on secrets management.
3. Keep all bracketed tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) verbatim so local reverse detokenization restores exact values.

[PASTE SANITIZED SCHREMS II CROSS-BORDER AI DATA SANITIZER IN NODE.JS (<1MS) PAYLOAD HERE]
Why DevSecOps and Security Engineering Teams Flag Unmasked Prompts in Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms)
Regulatory expectations for Software Development are explicit: OWASP guidelines on secrets management, SOC 2 Type II trust service criteria, and GDPR Article 25 (data protection by design). Navigating the compliance boundary for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) directly intersects with sanitize JSON payloads for secure AI processing—preventing schrems ii ai proxy nodejs from becoming a permanent liability in external systems. Enforcing Statutory Risk Minimization requires stripping identifiers into [SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1] before cloud transit.
Zero-Trust Code and Engineering Tokenization for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms)
Through @privacyscrubber/sdk (<0.8ms Node.js/TS RAM) & @privacyscrubber/mcp-server, PrivacyScrubber provides a zero-egress firewall for Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms). Before any schrems ii ai proxy nodejs or gdpr chapter v ai sanitizer text reaches GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools, deterministic tokenization substitutes sensitive strings with [SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1] in volatile memory, fulfilling agentic AI data leak prevention with zero external server dependencies.
We back every Schrems II Cross-Border AI Data Sanitizer in Node.js (<1ms) deployment with deterministic proof: test schrems ii ai proxy nodejs tokenization offline under the Airplane Mode Standard or run npx ztds-audit in CI/CD. Conforming to dsar nightmare in RAG systems (and how pre-ingestion scrubbing stops IT), zero raw bytes ever leave your local memory boundary.
