Sanitize Financial Models & Client Portfolios Before AI Analysis
AI Summary / Key Takeaways
"PrivacyScrubber eliminates the barrier between utilizing powerful AI and strict corporate data bans. By sanitizing PANs, routing numbers, and balances locally in browser RAM, it keeps your external AI integrations out of the scope of rigid PCI-DSS and SOC 2 audits, protecting both your career and corporate reputation."
How to sanitize financial ledgers, IBANs, and credit card numbers for AI financial analysis?
Sanitize financial data by masking Primary Account Numbers (PAN), IBANs, and ledger details into deterministic tokens directly in volatile memory. Operating in full compliance with PCI DSS v4.0 Requirement 3.4 and GLBA, PrivacyScrubber ensures no unencrypted cardholder data or corporate balances ever enter AI training pipelines.
Interactive PII Detection & Sanitization Sandbox
Test real-time client-side RAM tokenization. Choose a specialized preset or paste your own raw prompt to test instant reversible redaction.
Sanitized locally in volatile RAM. Pre-prompt compliance maintained under Finance & Banking standards (GDPR, HIPAA, SOC 2).
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
Verified by the Enterprise Board
Our 10-persona AI team ensures Finance compliance at every layer.
"PrivacyScrubber eliminates Shadow AI risk by intercepting PII at the edge. We've mapped this hub to SOC 2 Type II and ISO 27001 masking controls."
"Under GDPR Article 32 and HIPAA Safe Harbor, local anonymization removes the AI provider from the 'Data Processor' chain, negating complex DPA liabilities."
"A single GLBA or PCI-DSS violation costs 100x more than a site-wide license. We provide verifiable ROI through data loss prevention at the prompt level."
The Finance AI Privacy Gap
M&A Disclosure
Feeding un-masked term sheets into ChatGPT exposes proprietary M&A secrets.
Audit Log Leak
Sharing raw financial transaction logs violates SOC 2 and SOX data constraints.
SEC Violation
Failing to protect MNPI during AI analysis.
Raw Input: Acct: 4421-992, Balance: $1,240,000...
Sanitized: Acct: [ID_1], Balance: [MONEY_1]...
Secure Finance AI Workflow
Enable high-performance AI without client data leaving your machine
Import Files
Upload documents locally into the PrivacyScrubber sandbox.
Batch ProcessCredit Card Masking for AI
Tokenize credit cards, PANs, and bank transactions in RAM before AI analysis.
PCI DSS MaskingAnalyze with AI
Submit sanitized prompts to ChatGPT or Claude for processing.
Reverse Scrub
Restore original values into the AI response locally for the final draft.
Reverse RevealProtocol: The 5-Step Airplane Mode Audit
Don't trust us. Trust the laws of physics. Follow this audit procedure to verify zero-server PII sanitization for Finance workflows.
Load the tool: Open PrivacyScrubber.com in your browser.
Go Offline: Disconnect your WiFi or enable Airplane Mode. The site remains fully functional.
Process Data: Paste a sensitive finance document and click "Sanitize PII".
Inspect Network: Open Developer Tools (F12) and check the 'Network' tab. Verify 0 requests were made.
Verify Local RAM: All finance identifiers stay in your transient browser memory—never stored, never logged.
Finance & Banking Profile: Detection Coverage
GLBA and SOC 2 aligned detection ruleset for financial institutions, wealth advisors, and banking ops. Neutralizes IBANs, PAN cards, and balances locally.
Top 6 Finance & Banking Sensitive Entity Types Detected & Scrubbed
International Bank Accounts
Primary Account Numbers (PAN)
Internal Bank Accounts
Routing & SWIFT Codes
EIN & Tax Identifiers
Monetary Net Worth Values
Continuous Detection Engine Expansion & Custom Regex Sovereignty
The 6 entity types above represent the core detection baseline for Finance & Banking. Our zero-trust engine detects hundreds of additional data classes and is continuously updated with new heuristic patterns, shadow AI leak vectors, and custom regulatory rulesets. Need proprietary database IDs or internal project codenames masked? PRO and TEAMS users can define unlimited custom regular expressions running 100% locally in browser RAM.
How the PrivacyScrubber Engine Solves This
Interactive Tool Controls for Finance & Banking. Hover for specs.
In-DOM Payment Card & IBAN Shield
The Browser Extension detects and masks credit cards, IBANs, routing numbers, and SSNs in browser RAM before network send.
- Engine WASM-Accelerated
- Privacy 100% Local RAM
- Security Zero-Server Leak
Offline Spreadsheet & CSV Scrub
Process entire customer transaction ledgers and payroll spreadsheets locally via the Wasm Table Sanitizer.
- Engine WASM-Accelerated
- Privacy 100% Local RAM
- Security Zero-Server Leak
Encrypted Teams Financial Handoff
Share tokenized bank reports with colleagues using XChaCha20-Poly1305 session links without cloud storage.
- Engine WASM-Accelerated
- Privacy 100% Local RAM
- Security Zero-Server Leak
Finance Technical Compliance Library
Deep architectural mapping of Zero-Trust Data Sanitization (ZTDS) controls to industry-specific regulatory standards.
Zero-Trust Verification Signature
The above technical controls are enforced deterministically by the PrivacyScrubber Local Engine. All redaction cycles generate zero server-side telemetry, satisfying global data residency requirements for Finance institutions.
Hardened Audit Standards
Enforcing audit-grade data controls across financial workflows.
No data persistence on untrusted infrastructure.
Privacy by design at the engineering layer.
Data masking as a core organisational control.
Cardholder data masked before AI processing.
Federal PII minimisation and transparency controls.
Finance & Banking Compliance Library
Step-by-step redaction workflows for Finance & Banking environments.
Prevent IBAN, Bank Account & Financial Statement Network Leakage
Prevent IBAN, bank account numbers, and balances from leaking to external cloud networks. 100% in-RAM zero-server data sanitization for finance teams.
Prevent Payroll & Salary Spreadsheet Leakage to External Clouds
Prevent employee salaries, SSNs, and direct deposit routing numbers from leaking to external networks. 100% offline in-RAM payroll data protection.
Prevent Pitch Deck, Cap Table & Startup Financials Cloud Egress
Prevent cap tables, unreleased ARR metrics, and investor lists from leaking to external networks. 100% in-RAM trade secret protection for founders and VCs.
Prevent Loan Applications & Borrower SSN Network Leakage
Prevent borrower SSNs, tax returns, and loan applications from leaking to external clouds. 100% in-RAM sanitization under GLBA and Fair Housing Act.
Prevent Wire Transfer, SWIFT & IBAN Leakage to Cloud Networks
Prevent SWIFT MT103, IBAN, and Fedwire details from leaking to external cloud networks. 100% in-memory data sanitization under UCC 4A & FinCEN.
Prevent Financial Audit Logs & ERP Transaction Network Leakage
Prevent PANs, IBANs, and ERP journal audit trails from leaking to external clouds. 100% in-RAM sanitization under SOC 2 CC6.1 & CC6.7 controls.
AI Privacy for Financial Advisors
Financial advisors can use AI safely by protecting client names, account numbers, and balances first. Flat-rate TEAMS pricing available.
How to Sanitize Bank Statements for LLMs (100% Local)
Protect account numbers, balances, and names from bank statements fully offline before AI budgeting. Zero server storage. Zero-server architecture.
Secure AI Tax Document Analysis
Analyze tax documents with AI without exposing SSNs, addresses, or financial data to external servers. Flat-rate TEAMS pricing available.
Insurance Claims AI
Remove policyholder names and claim details from insurance documents before AI review or analysis. Local browser processing ensures financial PII stays on-device.
Mortgage AI Safety
Mortgage AI tools must not receive raw borrower PII. Protect applications before AI underwriting. Local browser processing ensures financial PII stays on-device.
Crypto AI Privacy
Blockchain and crypto teams using AI for KYC must protect wallet holder identities. PrivacyScrubber keeps customer PII on-device with zero server uploads.
Trading Algorithm Data Privacy
Quantitative trading algorithms trained on client order data carry PII risk. Protect identifiers before model development. Zero-server architecture.
Sanitize Scanned Tax Returns for AI Financial Analysis
Accounting firms want to use AI to summarize complex tax documents, but they only have flattened scans that contain high-risk PII.
Financial Data Protection for Banking & FinTech AI
Financial data protection for secure LLM usage in banking. Protect wealth management PII locally. Local browser processing ensures financial PII stays on-device.
Credit Card Masking for AI Analysis — PCI DSS 4.0 Compliant
Mask card and account numbers locally before AI analysis while keeping amounts readable. Supports PCI DSS programs. Free to try, TEAMS flat rate.
IBAN Redaction for Safe European Financial AI
Redact IBANs and bank details locally before querying ChatGPT. Ensure GDPR compliance for European financial AI workflows with zero data sent to external servers.
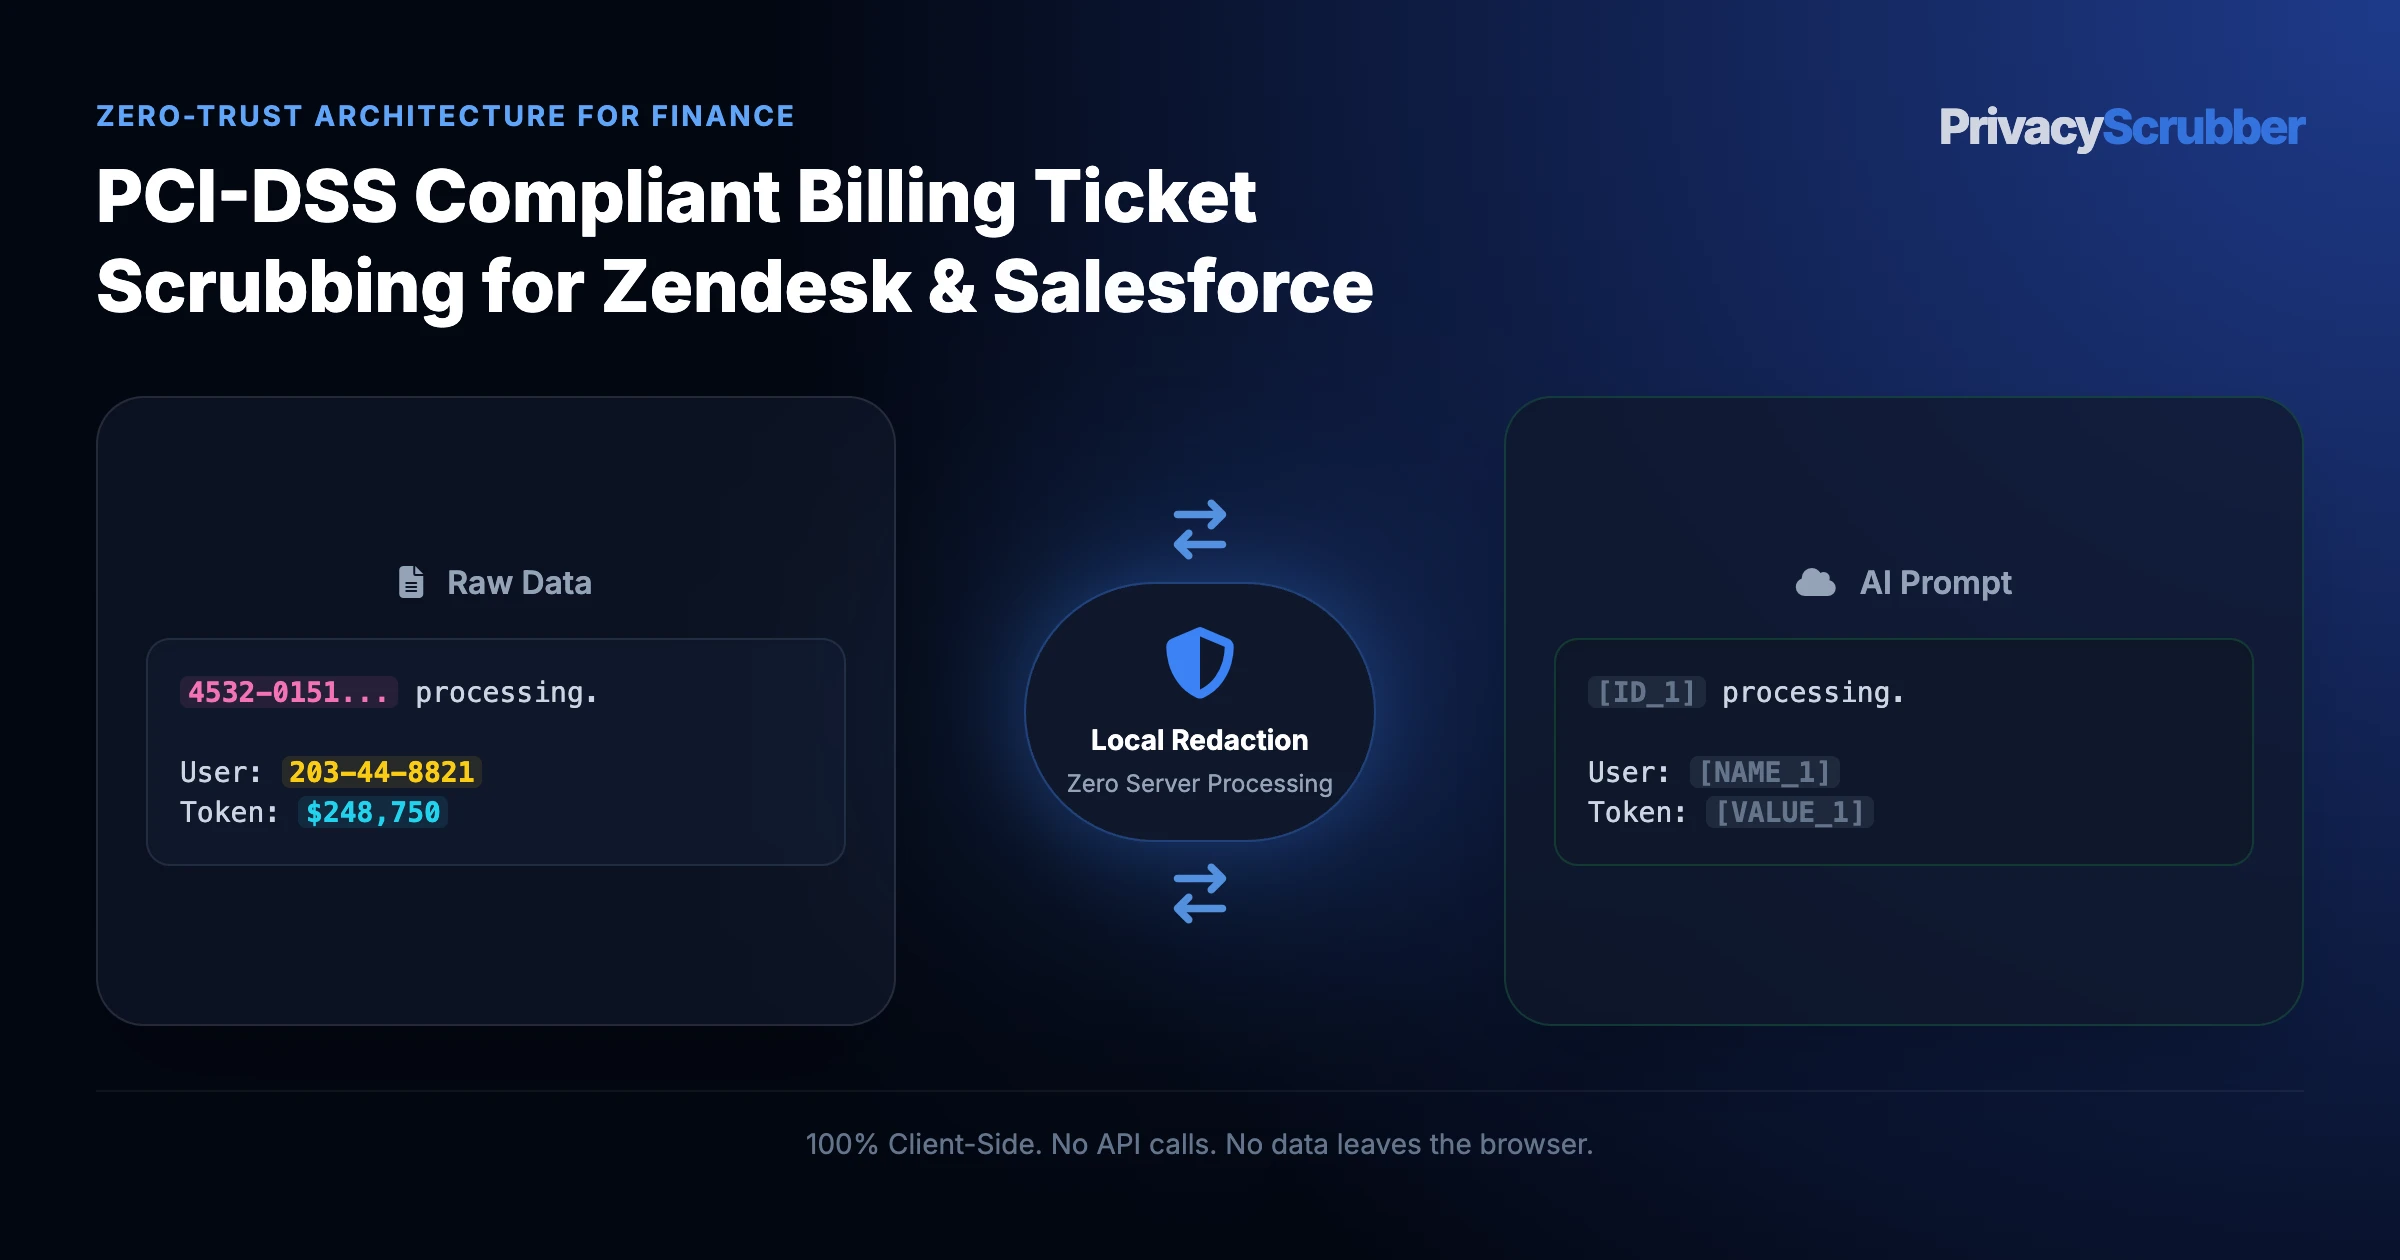
PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce
Enforce automated consumer payment rights at the support boundary. Pre-emptively sanitize credit card numbers, CVVs, and buyer identities in Zendesk, Freshdesk, and Salesforce Service Cloud locally before AI routing—achieving zero data loss and eliminating third-party PCI DSS 4.0 audit scope expansion.
Sanitize W-2 Forms & Paystubs for AI Mortgage Underwriting
Mask borrower SSN, EIN and account numbers in local RAM before AI loan underwriting while keeping wages readable. Supports GLBA Safeguards Rule programs.
Commercial Lending & SBA 7(a) Loan Privacy
Sanitize SBA 7(a) and 504 loan packages, UCC-1 filing numbers, personal financial statements (PFS), and borrower tax records locally before using AI to write commercial credit memos.
Mortgage Underwriting AI Privacy
Zero-trust local redaction for mortgage loan origination systems (LOS) — Form 1003 URLA, MISMO XML bundles, TRID disclosures, appraisal reports, and credit packages — under GLBA Safeguards Rule and FCRA.
Sanitize FinCEN SAR & KYC Narratives for AI
Zero-trust local PII sanitization for FinCEN SAR Form 111 and KYC risk narratives. Comply with BSA anti-tipping-off rules and 31 CFR § 1020.320 while leveraging AI for AML transaction monitoring.
Sanitize ISO 20022 XML & SWIFT MT103 Messages for AI Financial Analysis
Local client-side PII sanitization for ISO 20022 XML (pacs.008, pacs.002) and SWIFT MT103 payment payloads. Redact debtor/creditor IBANs and personal identifiers while keeping XML schema and settlement amounts intact.
FINRA Regulatory Notice 24-09 & SEC Rule 17a-4
Comply with FINRA Notice 24-09 & SEC Rule 17a-4 when using ChatGPT. Redact MNPI, account numbers, and CUSIPs locally in browser RAM with zero cloud egress.
Compare Edition Features
From individual use to corporate rollout, choose the level of control your organization requires.
| Core Capabilities |
Free
Web Only
|
PRO
$15/mo or $110 Lifetime
|
TEAMS
$99/mo
|
ENTERPRISE
Custom Tier
|
|---|---|---|---|---|
| 100% Local Processing (Airplane Mode) | ||||
| Text Paste & Single File Docs | 15k General / 5k Verticals | UNLIMITED | UNLIMITED | UNLIMITED |
| Batch Processing & Background OCR | — | |||
| Custom Regex & Specific Redaction Rules | — | |||
| Chrome Extension Native App | — | |||
| Silent Corporate Deployment (MDM) | — | — | ||
| Policy Control Center & Enforcement | — | — | ||
| IDE MCP Server & Headless Node.js SDK | MCP Free | MCP Unlimited | MCP + Team Sync | SDK ($299/mo) & Air-Gap |
| On-Premise Source Code License | — | — | — | |
| 100% Air-Gapped Operation | — | — | — | |
| Dedicated GRC Support | — | — | — | |
| Try Free | Details | Deploy TEAMS | Enterprise Hub |
Complementary AI Privacy Hubs & Frameworks
Cross-framework zero-trust sanitization workflows and enterprise compliance architectures.
Frequently Asked Questions
Common questions about deploying zero-trust AI for Finance & Banking Teams.
Is this compliant with GLBA and SOC 2?
Does this store any data on your servers?
How does the 'Airplane Mode' verification work?
Can I use this with custom internal identifiers?
Zero-Trust Sanitization Verified
Technical safeguards supporting GDPR Art. 32, HIPAA & CCPA. All PII processing occurs locally in browser RAM.
