Technical Security & Architecture
PrivacyScrubber enforces data confidentiality not through legal policy or backend promises, but through mathematical impossibility and local execution boundaries. All string scanning, deterministic ZTDS™ detection pattern matching, and cryptographic tokenization occur strictly inside endpoint RAM.
ZTDS-CERT-2026-PRIVACYSCRUBBER-WEB-D02DC6Cryptographically signed Ed25519 conformance seal • IETF Internet-Draft draft-sibiryakov-ztds-protocol-01
Zero-Trust Data Sanitization (ZTDS) Lifecycle
How data flows exclusively within the local host security perimeter.
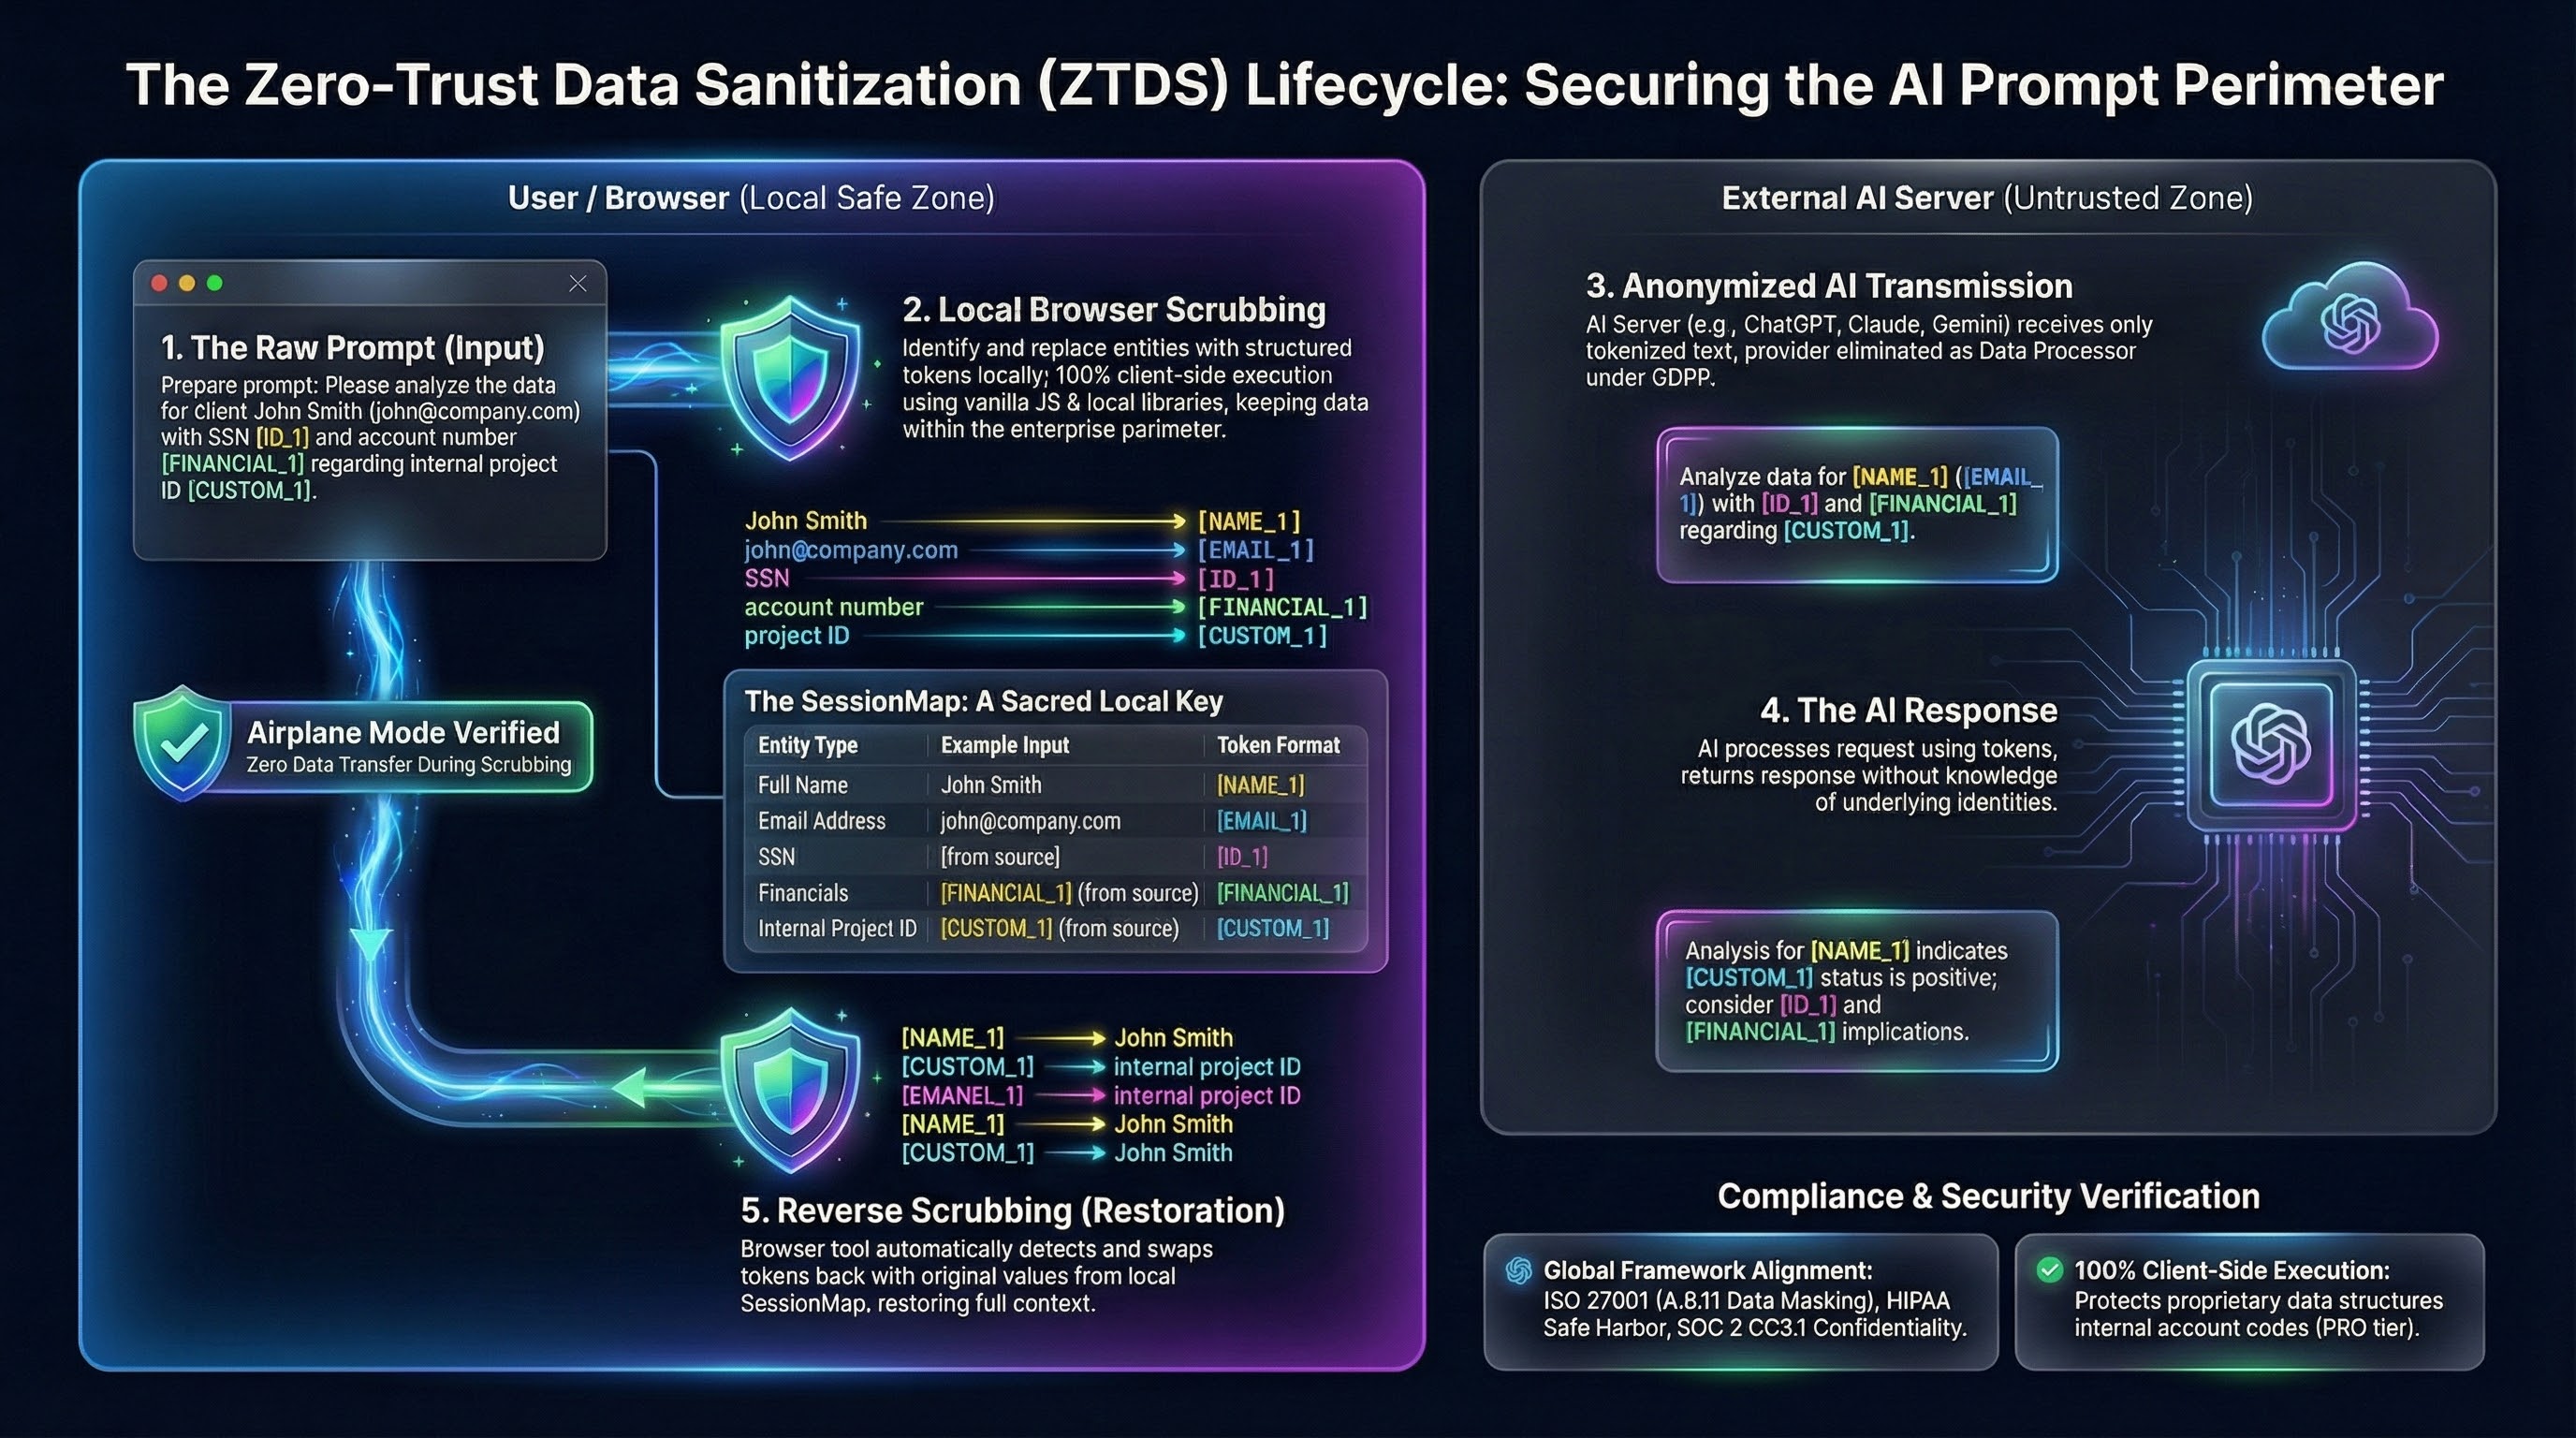
Raw inputs are evaluated locally in memory through our Contextual Entity Disambiguation Engine across 30 specialized industry compliance profiles.
Surrogate tokens (e.g. [NAME_1]) are deterministically assigned while preserving strict code, JSON, and table formatting integrity.
When the AI responds with sanitized tokens, 1-Click Reveal restores original values in sub-millisecond RAM execution, with zero disk trace.
Zero-Database Credential Architecture — Why No Trial or Login Exists
Because PrivacyScrubber has zero central backend servers, there is physically no user database, no credential store, and no authentication API. We do not require users to create accounts, set passwords, or provide corporate emails. There is no expiring trial mechanism — the Community Tier is 100% free forever for all users directly in local browser RAM without gatekeeping. For enterprise evaluations requiring 30 specialized industry profiles, batch processing, or team governance, corporate pilots operate on strict 7-day RS256 JWT cryptographically signed tokens with automated fail-closed expiration.
Execution Isolation Across All 4 Surfaces
Detailed technical runtime boundaries for every deployment modality.
Web Workspace (In-Browser SPA)
Web Worker Sandbox Executes via an isolated HTML5 Web Worker thread detached from the main UI thread. Employs the ZTDS™ offline OCR and local PDF engine for local OCR. Network activity during scrubbing is physically blocked by Content Security Policy directives (connect-src 'none' for worker endpoints).
Chrome Extension (Manifest V3)
Target Tab Isolated WorldInjected strictly into active target tabs (ChatGPT, Claude, Gemini) within an Isolated World context. The in-page shield HUD (Alt+Shift+X) intercepts the text area DOM node locally. Zero background page syncing or remote logging is executed.
PII MCP Server (@privacyscrubber/mcp-server)
Local Stdio / IPC Stream Compliant with Model Context Protocol (Anthropic/Cursor). Communicates over local standard input/output (stdio) or loopback interface (127.0.0.1). Does not initialize HTTP listener ports, external sockets, or telemetry beacons.
Developer SDK (@privacyscrubber/sdk)
Deterministic Node/WASMIsomorphic npm package with zero runtime telemetry dependencies. Functions execute synchronously on input strings. License validation is achieved via offline asymmetric cryptographic signature checks (Ed25519) without phone-home verification.
RAM Lifecycle & Dual-Plane Cryptographic Primitives
Zero-persistence memory destruction and Protocol V5 authenticated session handoff.
Volatile RAM Token Dictionary Lifecycle
The mapping dictionary ([NAME_1] → "John Doe") is instantiated as a tab-isolated in-memory JavaScript Map object (with ephemeral tab-scoped backup for soft-reload resilience). It is strictly never committed to:
- Persistent browser storage or disk files
- Plaintext
local encrypted browser storageorWebSQL - HTTP Cookies, Service Worker caches, or remote APIs
Upon tab closing or clicking "Reset Session", all references and tab-scoped memory allocations are immediately severed and zeroed.
Protocol V5 Dual-Plane Session Handoff
When TEAMS Session Handoff exports an encrypted dictionary via RFC 3986 URL #fragment (< 1,850 chars, 0 HTTP egress) or .pssession container, Protocol V5 (0x05 framing) enforces:
- Payload Compression: In-memory binary stream compression prior to AEAD sealing.
- Symmetric AEAD Cipher:XChaCha20-Poly1305 (256-bit key, 192-bit nonce, 128-bit MAC tag).
- Memory-Hard KDF:Argon2id (64MB RAM, 3 iterations, 4 lanes; WebCrypto PBKDF2-SHA256 fallback).
- Recipient Licensing: External recipients (outside counsel, clients, auditors) decrypt locally in 0.4s for free.
Cryptographic Taxonomy: Client-Side ZTDS™ vs. Homomorphic Encryption (FHE) & Legacy PGP
Why lattice-based encrypted compute (FHE) and PGP fail on commercial Frontier Cloud LLMs — and how Dual-Plane ZTDS solves it in < 1ms.
Why Homomorphic Encryption (FHE) Cannot Power Frontier LLMs
Fully Homomorphic Encryption (FHE — e.g., lattice-based encrypted compute platforms) allows mathematical evaluation over ciphertexts, but incurs a 10,000× to 1,000,000× computational overhead (10s–120s+ per query) and requires custom homomorphic circuits on the server. Commercial frontier LLMs (OpenAI GPT-4o/o3, Anthropic Claude 3.7, Google Gemini) execute standard floating-point Transformer weights and do not accept FHE ciphertexts.
Why Legacy PGP & E2EE Break AI Reasoning
End-to-end encryption (OpenPGP, S/MIME, Signal) collapses the entire document into a single opaque ASCII-armored ciphertext block (-----BEGIN PGP MESSAGE-----). If pasted into ChatGPT or Claude, the LLM is completely blind to syntax, legal clauses, clinical timelines, and code structure, rendering AI reasoning impossible until decrypted.
Sub-Millisecond Client RAM · Zero Server Cooperation
ZTDS™ requires zero cryptographic cooperation from OpenAI, Anthropic, or Google. By splitting the Sanitized AI Context Plane ([NAME_1], [IBAN_1]) from the Local RAM Dictionary Plane, standard uncooperative Cloud LLMs reason at 100% native token speeds while direct PII never leaves client RAM (< 1ms execution).
| Architectural Dimension | Client-Side ZTDS™ (PrivacyScrubber) | Homomorphic Encryption (FHE) | Confidential Computing (Server TEEs) | Legacy PGP / E2EE | Cloud DLP / Token Vaults |
|---|---|---|---|---|---|
| Works with Commercial Cloud LLMs (ChatGPT, Claude, Gemini) | Yes (100% Native Reasoning) | No (Requires Custom FHE Server Circuits) | Only Self-Hosted Enclave Models | No (Opaque Ciphertext Blinds AI) | Yes (Via Cloud Proxy MITM) |
| End-to-End Processing Latency | < 1 ms (Local CPU RAM) | 10,000 ms – 120,000+ ms (10⁴×–10⁶× Penalty) | 150 ms – 800 ms (Remote Enclave RTT) | 5 ms (Manual CLI / Keyring) | 600 ms – 2,500 ms (Cloud API RTT) |
| Raw PII Network Egress | 0 Bytes (Stays in Device RAM) | Encrypted Lattice Ciphertext Egress | Full Raw PII Egress to Cloud Enclave | Armored Ciphertext Egress | Full Raw PII Egress to DLP Vendor |
| Collaborative Team Handoff | Protocol V5 #hash SafeLink (Recipients Decrypt Free in 0.4s) | Requires Shared FHE Evaluation Keys | Server IAM Session Access | Manual Public Keyring & Re-Typing | Paid Per-Seat Cloud DB Lookup |
| Statutory Compliance Posture | GDPR Art. 32, HIPAA & SOC 2 Safe Harbor (Zero DPA) | Cryptographic Research / Niche Compute | Requires Cloud Processor BAA / DPA | Storage/Transit Only (No AI Use) | Sub-Processor DPA & Breach Liability |
The 3-Step "Airplane Mode" Verification Playbook
Independent technical audit protocol for security engineers and SOC analysts.
Navigate to PrivacyScrubber in Chrome, Firefox, or Safari.
Toggle your device to Airplane Mode or physically disconnect your Ethernet cable.
Paste confidential text. Notice immediate sanitization with DevTools Network panel recording 0 requests.
Automated QA Suite & Empirical Security Benchmarks
Continuous Integration (CI) test assertions executed on every software build.
| Automated CI Test Suite | Target Threat Vector | Verified Security Assertion | CI Status |
|---|---|---|---|
| E2E UI & XSS Guard | DOM-based XSS & Reverse Scrub Payload Injection | HTML tags sanitized to textContent; zero JavaScript execution. | 100% Passed |
| Extension Shadow DOM Isolation | Host-Page DOM Traversal & Script Hijacking | Closed Shadow Root (mode: "closed"); host scripts cannot access extension UI. | 100% Passed |
| Tab Isolation & Memory Lifetime | Cross-Tab Data Contamination & Storage Persistence | 0 token leakage between parallel tabs; 100% memory zeroed on reload. | 100% Passed |
| Extension Weak Vectors Guard | Prototype Pollution & Cross-Frame Message Spoofing | Rejects e.source !== window; postMessage prototype pollution mitigated. | 100% Passed |
| Cross-Platform Crypto Handoff | Cryptographic Desynchronization | 100% AES-GCM / Argon2id bit-level interop across Web, Extension & MCP. | 100% Passed |
| MCP Stdio JSON-RPC 2.0 Protocol | Network Port Exposure in AI IDEs (Cursor/Claude) | Air-gapped stdio transport only; zero listening network ports opened. | 100% Passed |
Independent CLI & Socket Verification
Reproduce zero-egress cryptographic proof on your own air-gapped infrastructure.
Monkey-patches node:net, node:tls, and node:http. Simulates 30 specialized profiles across 12,000+ characters to mathematically assert 0 socket openings and 0 bytes egress.
npm run verify:zero-egressRun the zero-trust sanitization engine directly in any terminal via npx. Verifies local string tokenization and sub-millisecond execution latency.
npx @privacyscrubber/sdk demoAcademic Attestations & Protocol Standards
Formal mathematical publications, preprint archives, and IETF protocol drafts.
Formal IETF specification for zero-trust client-side data sanitization and air-gapped agent boundaries.
Open data preprint on client-side ephemeral RAM tokenization and empirical benchmarks.
Comparative analysis of cloud DLP proxies vs. deterministic client-side tokenizers.
European open-archive research paper on GDPR Article 25/32 zero-egress compliance.
Empirical evaluation of client-side regex vs transformer models for real-time redaction.
Statutory framework mapping ZTDS to HIPAA Safe Harbor and EU AI Act obligations.
Deploy Zero-Trust Sanitization in Your Stack
Integrate in-process Node.js/WASM sanitization into your backend ETL and RAG pipelines, or deploy company-wide via Chrome Extension and Teams workspace governance.
Technical Security & Cryptographic FAQs
Direct architectural answers for CISOs, cryptographers, and DPOs.
How does Client-Side ZTDS™ compare to Fully Homomorphic Encryption (FHE) for generative AI?
[NAME_1]) so frontier LLMs reason at native token speeds. Why does legacy PGP or end-to-end encryption fail for collaborative AI workflows?
-----BEGIN PGP MESSAGE-----). If pasted into ChatGPT or Claude, the LLM cannot parse syntax, legal clauses, or clinical logic. ZTDS Dual-Plane Session Handoff separates the Sanitized AI Context Plane from the Key Dictionary Plane (sealed via Protocol V5 Argon2id + XChaCha20-Poly1305 inside an RFC 3986 URL #fragment), allowing full AI reasoning and 0.4-second free recipient restoration. 