
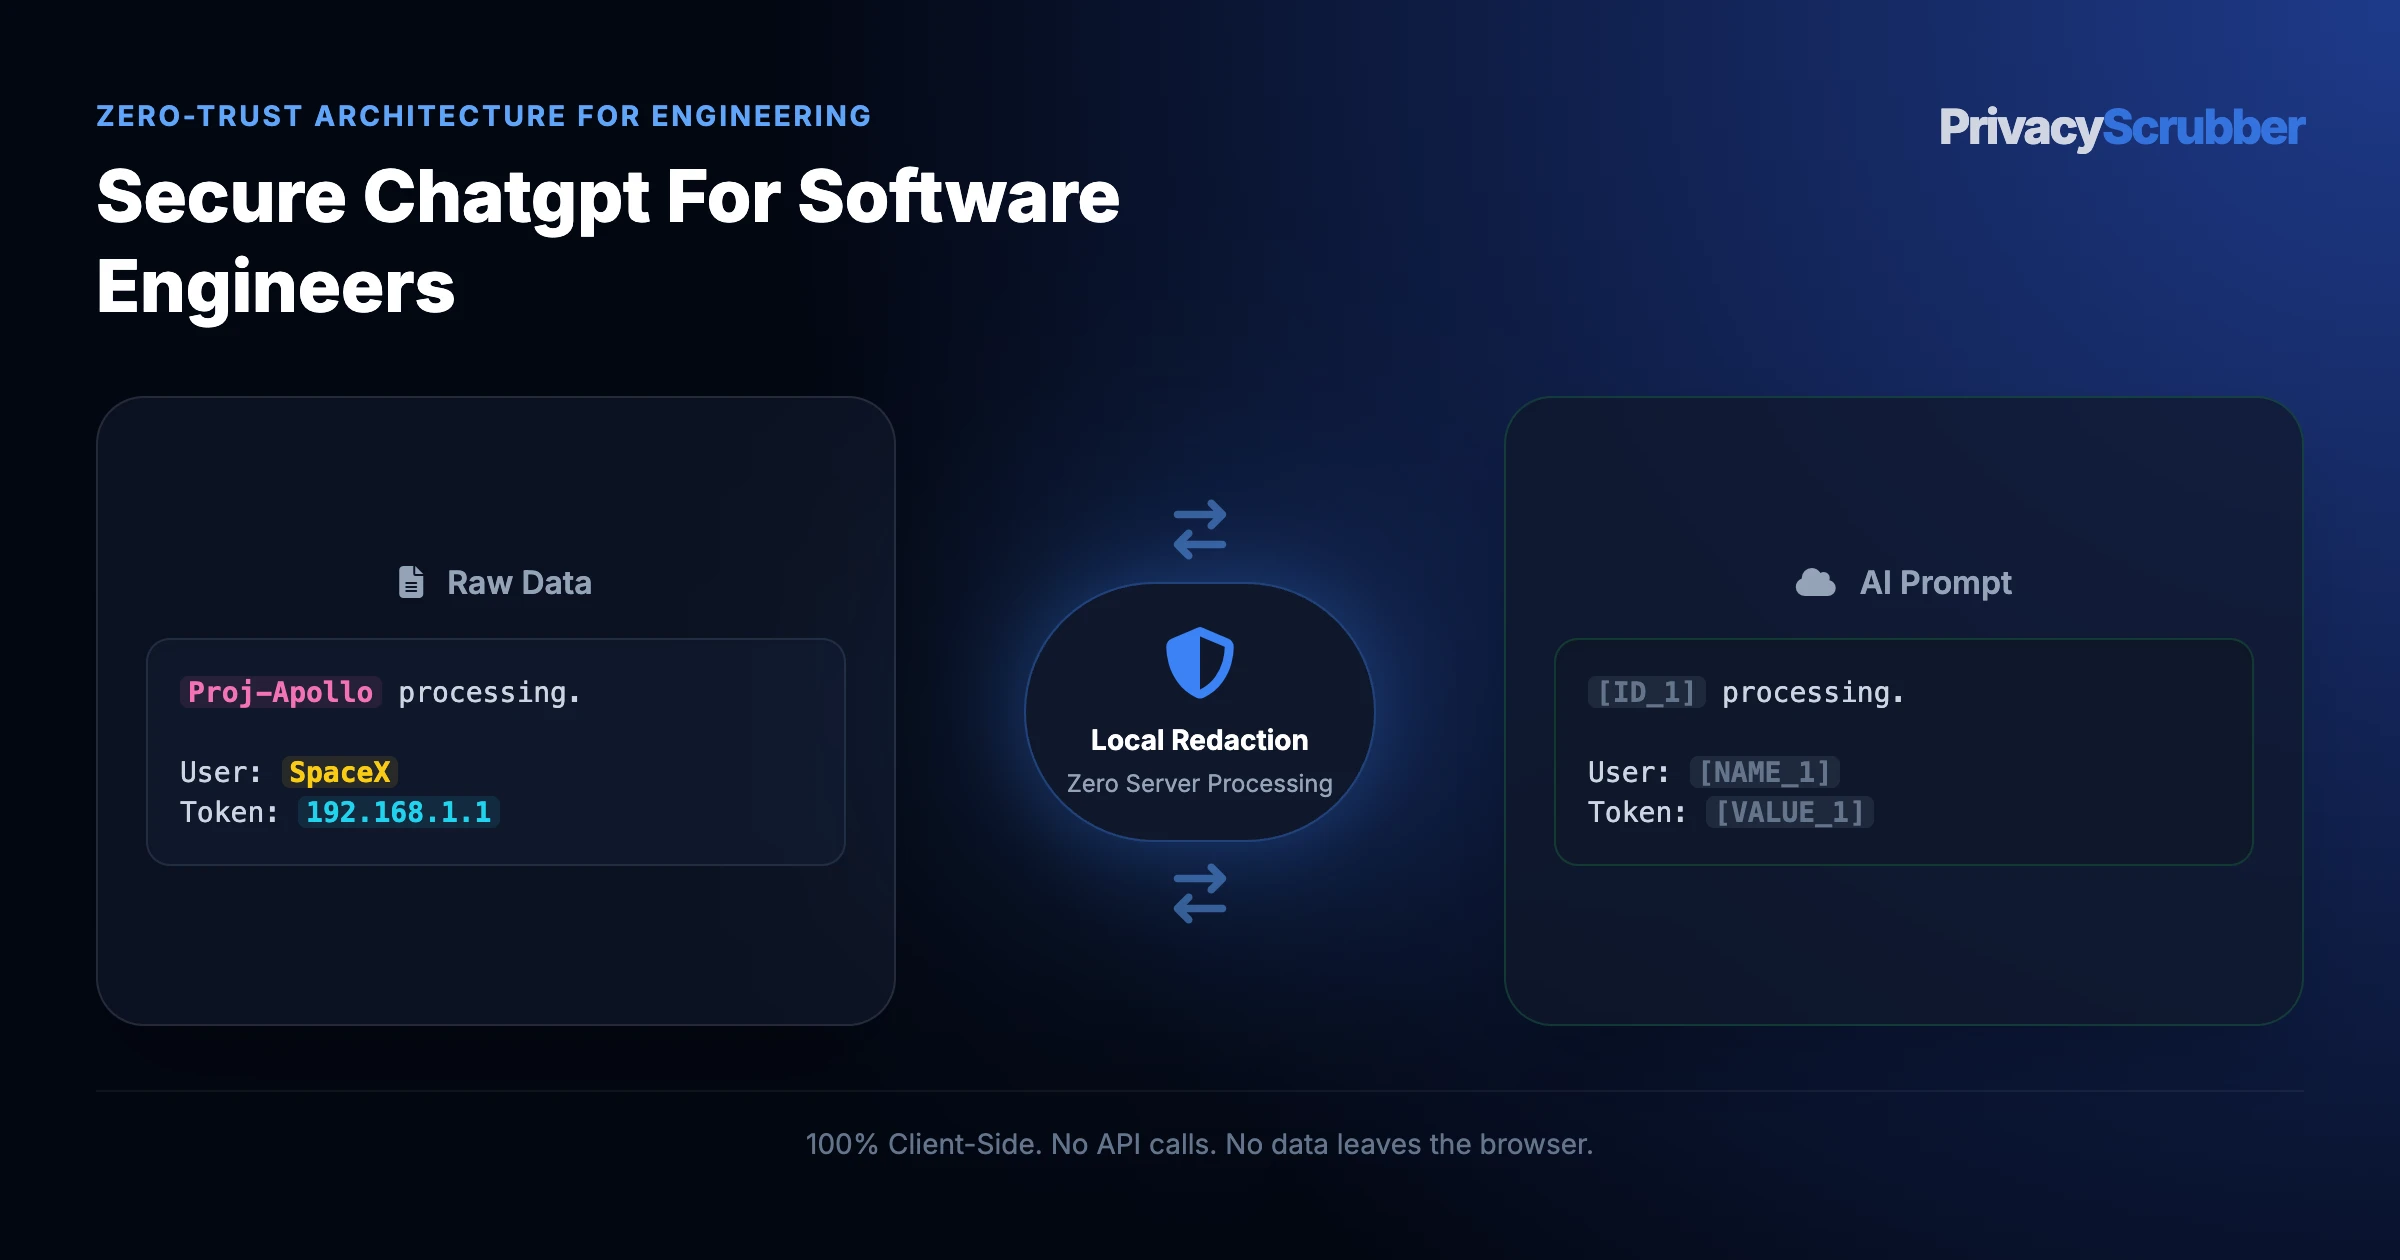
Architecting Secure ChatGPT for Software Engineers for high-compliance Software Engineering & DevOps environments requires eliminating unmasked production stack traces and CI/CD logs leaking into third-party LLM telemetry. Through @privacyscrubber/sdk & <60MB Alpine Docker Sidecar, PrivacyScrubber performs deterministic in-memory tokenization ([API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1]) for secure chatgpt for software engineers and source code pii scrubber, guaranteeing that third-party AI models only ever process anonymized logic.
Secure ChatGPT for Software Engineers: What Software and DevOps Engineers Expose to Cloud AI
Every unmasked prompt in Secure ChatGPT for Software Engineers exposes secure chatgpt for software engineers and developer prompt secret redaction to third-party sub-processors across GitHub Copilot, ChatGPT, and local IDE agent integrations. To prevent pasting active AWS keys, database passwords, or Kubeconfig IPs into AI debugging sessions and eliminate unmasked production stack traces and CI/CD logs leaking into third-party LLM telemetry, our Software Engineering & DevOps AI privacy guides map out client-side ZTDS™ tokenization ([API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1]) tailored for Software Engineering & DevOps workflows.
Why do conventional security gateways fail on Secure ChatGPT for Software Engineers? Secure ChatGPT for software engineers by masking credentials and secrets entirely offline. 100% client-side in browser RAM with zero cloud egress. When software engineers, devops, and system administrators handle secure chatgpt for software engineers and source code pii scrubber, unmasked production stack traces and CI/CD logs leaking into third-party LLM telemetry leaves sensitive context vulnerable to pasting active AWS keys, database passwords, or Kubeconfig IPs into AI debugging sessions.
Client-Boundary Sanitization for secure chatgpt for software engineers
Why do legacy DLP tools struggle with Secure ChatGPT for Software Engineers? Because unmasked production stack traces and CI/CD logs leaking into third-party LLM telemetry. When teams process secure chatgpt for software engineers and developer prompt secret redaction, routing cleartext to an external inspection server still constitutes an outbound disclosure under OWASP and ISO 27001 Secure Engineering principles.
By running @privacyscrubber/sdk & <60MB Alpine Docker Sidecar directly inside client or application memory, PrivacyScrubber replaces sensitive records with [API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1] before a single byte touches the network stack—delivering verifiable Airplane Mode isolation for source code pii scrubber.
Pre-Inference Redaction Matrix: Secure ChatGPT for Software Engineers
Under OWASP and ISO 27001 Secure Engineering principles, software engineers, DevOps, and system administrators enforce this selective masking rule on Secure ChatGPT for Software Engineers:
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Secondary Regulated Attributes (local mcp secret guard) | REDACT | [HOST_1] | Satisfies OWASP and ISO 27001 Secure Engineering principles data minimization by replacing sensitive Software Engineering & DevOps strings in local RAM. |
| Contact & Routing Endpoints (source code pii scrubber) | REDACT | [INTERNAL_IP_1] | Eliminates cross-record linkage and unauthorized sub-processor indexing during Secure ChatGPT for Software Engineers. |
| Authentication, Account & Reference Keys (developer prompt secret redaction) | REDACT | [JWT_1] | Blocks credential, account, or case-number exfiltration across Software Engineering & DevOps telemetry and vendor logs. |
| Regulatory Clause Citations & Policy Taxonomy (OWASP and ISO 27001 Secure Engineering principles) | PRESERVE | Cleartext Citations | Allows the AI model to map Secure ChatGPT for Software Engineers findings against statutory controls and audit frameworks. |
| Relative Timelines, Status Codes & Error Severities | PRESERVE | Cleartext (ISO Sequence) | Maintains chronological ordering and root-cause diagnostics across developer prompt secret redaction workflows. |
| Quantitative Metrics, Ratios & Aggregated Totals | PRESERVE | Cleartext ($ / % / Deltas) | Enables accurate mathematical reasoning and variance analysis for Secure ChatGPT for Software Engineers without identity exposure. |
Ready-to-Use Sanitized Prompt: Secure ChatGPT for Software Engineers
Submit this prompt wrapper with your masked Secure ChatGPT for Software Engineers input so the AI reasons over symbolic tokens without altering placeholder tags:
Objective: Process Secure ChatGPT for Software Engineers (secure chatgpt for software engineers) with zero cloud data leakage.
All personal and corporate identifiers are represented by bijective tokens ([API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1]).

Steps:
1. Audit the quantitative and logical parameters of the Secure ChatGPT for Software Engineers record.
2. Produce a concise executive summary tailored for software engineers, devops, and system administrators.
3. Maintain all [API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1] markers in-place for deterministic local RAM reveal.

[PASTE SANITIZED PAYLOAD HERE]
Objective: Process Secure ChatGPT for Software Engineers (secure chatgpt for software engineers) with zero cloud data leakage.
All personal and corporate identifiers are represented by bijective tokens ([API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1]).

Steps:
1. Audit the quantitative and logical parameters of the Secure ChatGPT for Software Engineers record.
2. Produce a concise executive summary tailored for software engineers, devops, and system administrators.
3. Maintain all [API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1] markers in-place for deterministic local RAM reveal.

[PASTE SANITIZED PAYLOAD HERE]
OWASP and ISO 27001 Secure Engineering principles Audit & Compliance Risks for Secure ChatGPT for Software Engineers
Under OWASP and ISO 27001 Secure Engineering principles (OWASP and ISO 27001 Secure Engineering principles), unstructured secure chatgpt for software engineers prompts are subject to the same strict custody rules as structured databases. Integrating the safeguards from masking kubernetes kubeconfig ips for ChatGPT into Secure ChatGPT for Software Engineers ensures all [API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1] mappings remain 100% local.
3-Step Local RAM Redaction for Secure ChatGPT for Software Engineers Workflows
With @privacyscrubber/sdk & <60MB Alpine Docker Sidecar, Secure ChatGPT for Software Engineers inputs are sanitized at the source: secure chatgpt for software engineers and developer prompt secret redaction values are mapped to [API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1] in <1ms of local RAM. This implements the exact technical safeguards described in Salesforce agentforce compliance with 0.00 bytes of server egress.
To prove 0-byte network leakage for Secure ChatGPT for Software Engineers, run @privacyscrubber/sdk & <60MB Alpine Docker Sidecar with Airplane Mode active. All secure chatgpt for software engineers and developer prompt secret redaction identifiers convert to [API_KEY_1], [JWT_1], [INTERNAL_IP_1], [HOST_1] in local RAM, meeting the technical verification criteria of enterprise security questionnaire guide.
