Anthropic MCP Design Vulnerability: Systemic RCE & AI Supply Chain Threat
Anthropic MCP Design Vulnerability: Critical architectural flaws in Anthropic's Model Context Protocol (MCP) enable remote code execution and systemic data exposure across enterprise AI integrations, halted only by local client-side sanitization.
Published: · Updated: · 3 min read
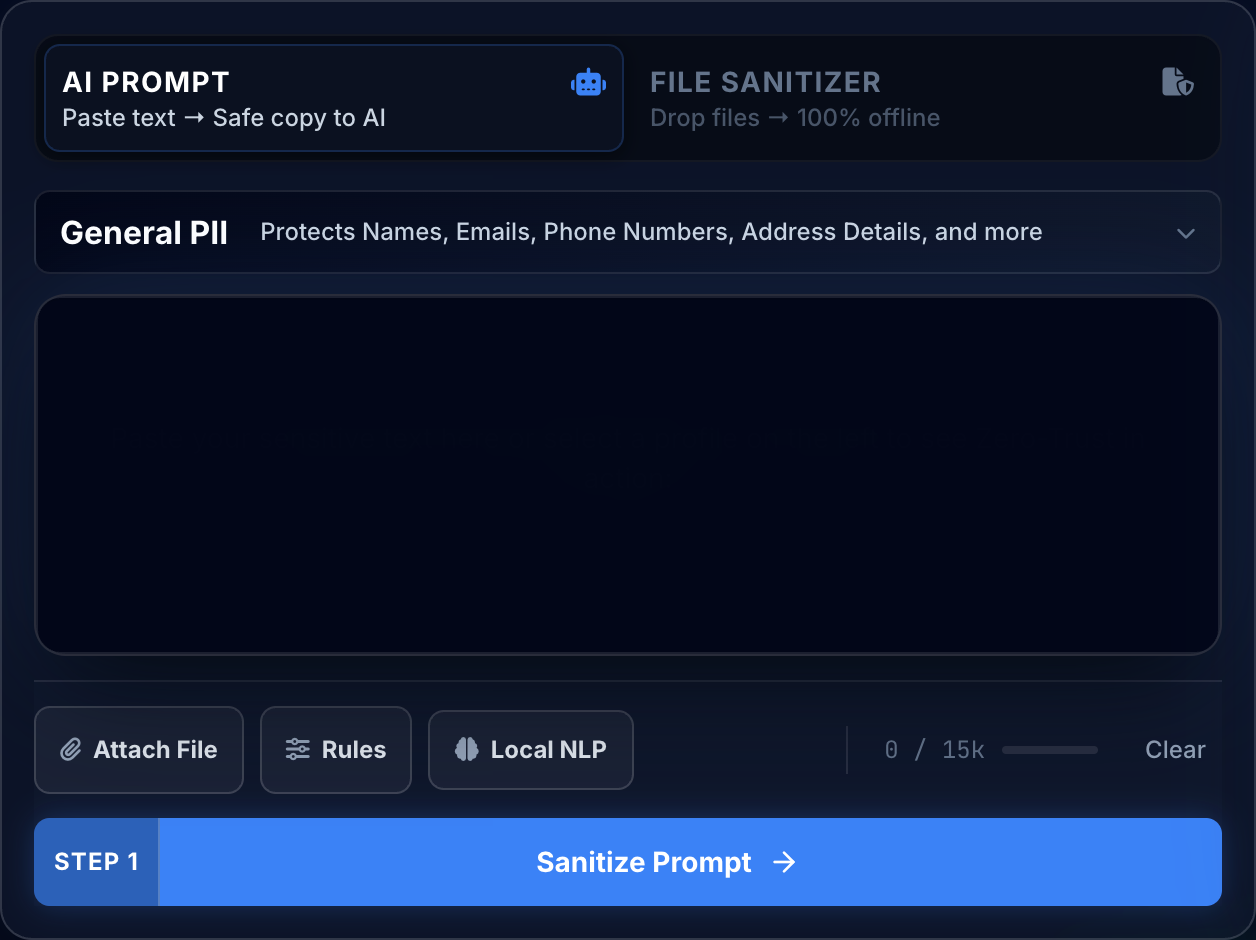
Interactive PII Detection & Sanitization Sandbox
Test real-time client-side RAM tokenization. Choose a specialized preset or paste your own raw prompt to test instant reversible redaction.
Technical Incident Analysis
Recent security disclosures have revealed a systemic design flaw in Anthropic's Model Context Protocol (MCP), exposing thousands of enterprise applications to remote code execution (RCE) and automated prompt injection attacks. Because MCP servers automatically execute contextual tool calls, attackers can weaponize inputs to exfiltrate database connections, source code, and internal telemetry. Similar to previous OpenAI Hardware Security Risks, unchecked telemetry channels present critical exposure. Explore our AI Security Architecture to understand how modern protocols are being hardened.
Enterprise Blast Radius & Compliance Risks
When autonomous agents use compromised MCP servers, regulatory perimeters under GDPR & CCPA Compliance are immediately breached. Exposing Personally Identifiable Information (PII) and corporate secrets to third-party endpoints through automated tool chaining creates severe compliance penalties and litigation exposure.
Client-Side Mitigation via Zero-Trust Data Sanitization
Organizations can completely neutralize this supply chain risk by adopting browser-based PII filtering. By executing tokenization in WASM browser RAM with zero network latency prior to prompt transmission, sensitive payloads are replaced with secure placeholders before ever reaching vulnerable model contexts. Learn more about our Model Context Protocol (MCP) Sanitizer and sessionMap ephemeral isolation protocols.
Step-by-Step Integration Guide: Anthropic MCP Design Vulnerability
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use Developer AI & IDE Agent Pipelines:
1 Method A: Instant Clipboard & Web Workspace
Fastest for ad-hoc debugging, server crash logs, or DB dumps:
- Paste the raw database dump, stack trace, or config payload into PrivacyScrubber.
- Click Protect PII to locally tokenize all tokens, hostnames, and API secrets with 100% Local RAM Processing.
- Copy the sanitized code and safely query ChatGPT, Claude, or Copilot.
- Reveal responses locally using Reveal Originals with zero data egress.
2 Method B: Chrome Extension & MCP Server
For automated in-browser prompt masking & IDE agents (Cursor / Cline):
- Install the free PrivacyScrubber Extension to auto-mask credentials directly in ChatGPT/Claude inputs.
- Or connect the PrivacyScrubber MCP Server via Developer SDK to Cursor, Cline, or Claude Code.
- Session token maps remain 100% in volatile RAM with zero telemetry.
- Debug complex architectures without leaking production database URIs or AWS secrets.
Local Redaction & Risk Matrix for Security
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| User / Server IP Addresses | [IP_ADDRESS] | High (DLP / Location footprinting) | IPv4 / IPv6 format strip |
| AWS_KEY Details | [AWS_KEY] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_HOSTNAME Details | [INTERNAL_HOSTNAME] | Medium (PII Exposure) | Deterministic local swap |
| MAC_ADDRESS Details | [MAC_ADDRESS] | Medium (PII Exposure) | Deterministic local swap |
| VULN_ID Details | [VULN_ID] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Lead DevSecOps Engineer / Cloud Security Architect · Target: Developer AI & IDE Agent PipelinesAct as a principal cloud systems architect. Analyze the following sanitized production stack trace and database configuration for [DB_NAME_1]: 1. Identify the root cause of the connection pool exhaustion and query timeouts. 2. Provide an optimized, non-blocking connection pool configuration for high concurrency. 3. Draft a step-by-step remediation patch. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Retain all cryptographic token identifiers ([DB_NAME_1], [INTERNAL_IP_1], [SECRET_1], [JWT_TOKEN_1]) strictly unchanged in your configuration suggestions for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Enterprise Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Risk & Audit LeadCOMPLIANCE AUDIT
Data Protection OfficerGDPR COMPLIANCE
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII masking — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Sensitive Data compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any sensitive data text, click Protect PII. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.