
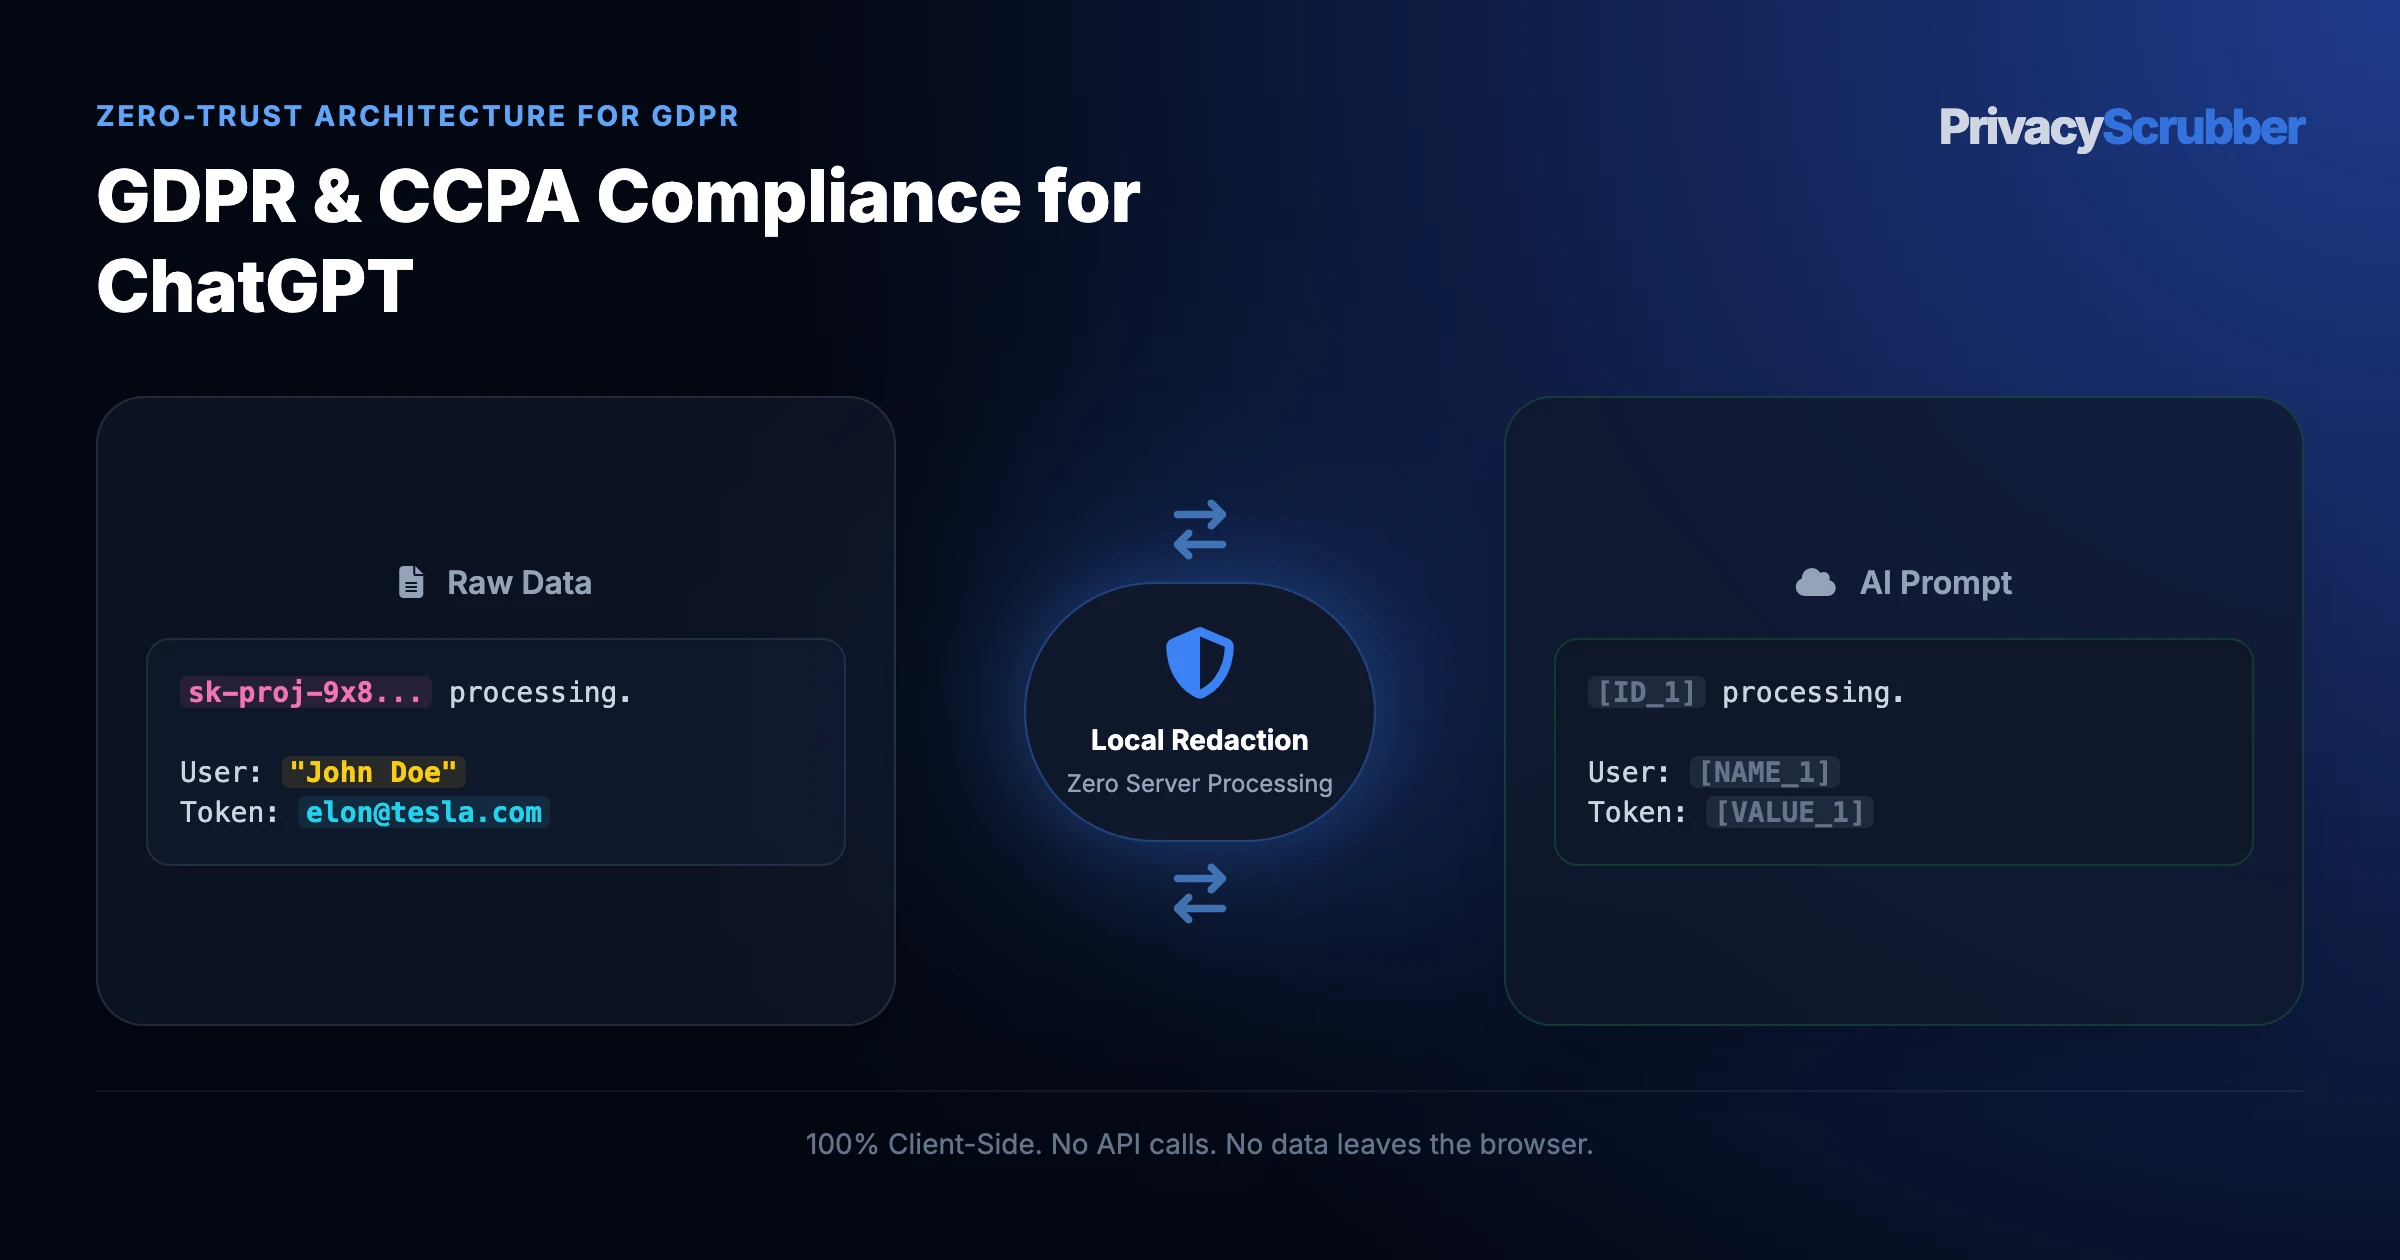
Cloud filters see GDPR AI compliance only after network transit. For GDPR & CCPA AI Compliance, offline endpoint scrubber masks records into [NAME_1] and [IBAN_1] inside DPOs RAM beforehand.
Remove consumer PII before the prompt leaves the device
Regulators look at what is sent to the vendor. Direct identifiers are replaced with tokens in local memory, so the model receives no names, emails or ID numbers. This is risk minimization (GDPR Art. 32), not a legal exemption.
Choose a profile in the sandbox above, paste the customer text, review the tokens, then copy the masked prompt.
Open workspaceThe extension masks consumer PII inside the ChatGPT or Claude input box and restores it in the reply.
Add Chrome shieldConfigure stdio masking for GDPR & CCPA AI Compliance directly on your machine (free tier compatible).
{
  "mcpServers": {
    "privacyscrubber": {
      "command": "npx",
      "args": ["-y", "@privacyscrubber/mcp-server"]
    }
  }
}npm install @privacyscrubber/sdk
import { sanitize, restore } from '@privacyscrubber/sdk';

// Pseudonymize consumer data before it reaches an LLM, log or vector store
const { scrubbedText, tokenMap } = sanitize(customerRecord);
const aiAnswer = await callYourModel(scrubbedText);   // only tokens leave your process
const { restoredText } = restore(aiAnswer, tokenMap); // originals restored in local RAMGDPR & CCPA AI Compliance: What Privacy and DPO Teams Expose to Cloud AI
High-compliance GDPR teams prevent Art. 44 transfer & training exposure on GDPR & CCPA AI Compliance using client-side offline endpoint scrubber; GDPR AI privacy guides cover GDPR AI compliance isolation into [NAME_1].
Meet GDPR Art. 28/32 and CCPA/CPRA AI rules in 2026: tokenize consumer PII in local browser RAM before ChatGPT or Claude prompts with 0 cloud egress. External models retain GDPR AI compliance inputs longer than DPOs realize; substituting [IBAN_1] locally closes the leak inside ChatGPT.
Playbook: GDPR Compliance for unstructured AI Prompts
The Vulnerability
Employee prompts containing customer records, email logs, or database exports are stored by cloud AI providers. If this data belongs to EU or California citizens, it constitutes an unauthorized data transfer under GDPR Article 46 and CCPA. Standard cloud filters are too late — once the prompt leaves the browser, the compliance breach is already recorded.
The ZTDS Reputation Shield
By shifting the security boundary directly to the employee's browser, PrivacyScrubber prevents compliance anxiety. If OpenAI or Anthropic never receives the PII, your organization is designed to be protected from data leakage fines and reputational audits. It is the ultimate insurance policy for modern, AI-driven workforces.
Install the Chrome Extension for Zero-Risk Clipboard Actions
Instantly sanitizes clipboard copies and text entries before they hit the cloud, protecting employees from accidental leaks during daily brainstorming.
Use the Secure Workspace for Bulk Compliance Logs (PRO/TEAMS)
Process entire datasets or customer lists offline. The browser sandbox executes local de-identification with zero server telemetry.
Use the Reveal Gateway Locally
After the AI outputs its results, decrypt and restore original identities strictly on your device. The external AI model only sees tokenized logic.
Cryptographic Handoff
Share Magic Links to transmit clean, tokenized session prompts to co-workers, while keeping the client's actual identity out of transit.
Deterministic Token Mapping for GDPR & CCPA AI Compliance
Use the classification table below to separate high-liability GDPR & CCPA AI Compliance attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Subject Identifiers (GDPR AI compliance) | REDACT | [NAME_1] | GDPR (Article 32 guard prevents ChatGPT from retaining personal GDPR & CCPA AI Compliance records. |
| Regulated Strings (CCPA AI privacy) | REDACT | [EMAIL_1] | Applies GDPR (Article 32 minimization locally before GDPR & CCPA AI Compliance leaves RAM. |
| Tax, Token & Session Strings (gdpr ai) | REDACT | [IBAN_1] | Zero-egress tokenization keeps GDPR & CCPA AI Compliance identifiers off vendor storage. |
| Schema & Formatting (GDPR & CCPA AI Compliance) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for ChatGPT on GDPR AI compliance. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for GDPR & CCPA AI Compliance while shielding real names. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets ChatGPT trace root causes cleanly inside sanitized gdpr ai logs. |
Bijective Prompt Blueprint for GDPR & CCPA AI Compliance
Submit this prompt wrapper with your masked GDPR & CCPA AI Compliance input so the AI reasons over symbolic tokens without altering placeholder tags:
Task for ChatGPT: Review masked GDPR & CCPA AI Compliance input (GDPR AI compliance).
1. Summarize findings around [NAME_1] and [IBAN_1].
2. Highlight next actions for DPOs.
3. Preserve bracketed placeholders verbatim.

[INSERT TOKENIZED INPUT]
Task for ChatGPT: Review masked GDPR & CCPA AI Compliance input (GDPR AI compliance).
1. Summarize findings around [NAME_1] and [IBAN_1].
2. Highlight next actions for DPOs.
3. Preserve bracketed placeholders verbatim.

[INSERT TOKENIZED INPUT]
Minimizing GDPR (Article 32 Exposure in GDPR & CCPA AI Compliance
Rather than halting AI, AI recruitment & GDPR gives GDPR & CCPA AI Compliance teams a GDPR (Article 32 safe harbor via sub-millisecond GDPR AI compliance masking.
3-Step Local RAM Redaction for GDPR & CCPA AI Compliance Workflows
Through offline endpoint scrubber, GDPR & CCPA AI Compliance swaps GDPR AI compliance into [NAME_1] in <1ms RAM before ChatGPT, pairing with ChatGPT agent mode privacy risks for 1-click Reveal.
Testing GDPR & CCPA AI Compliance offline lets DPOs prove gdpr ai masking lives solely in RAM, reinforcing prevent salesbleed.
