
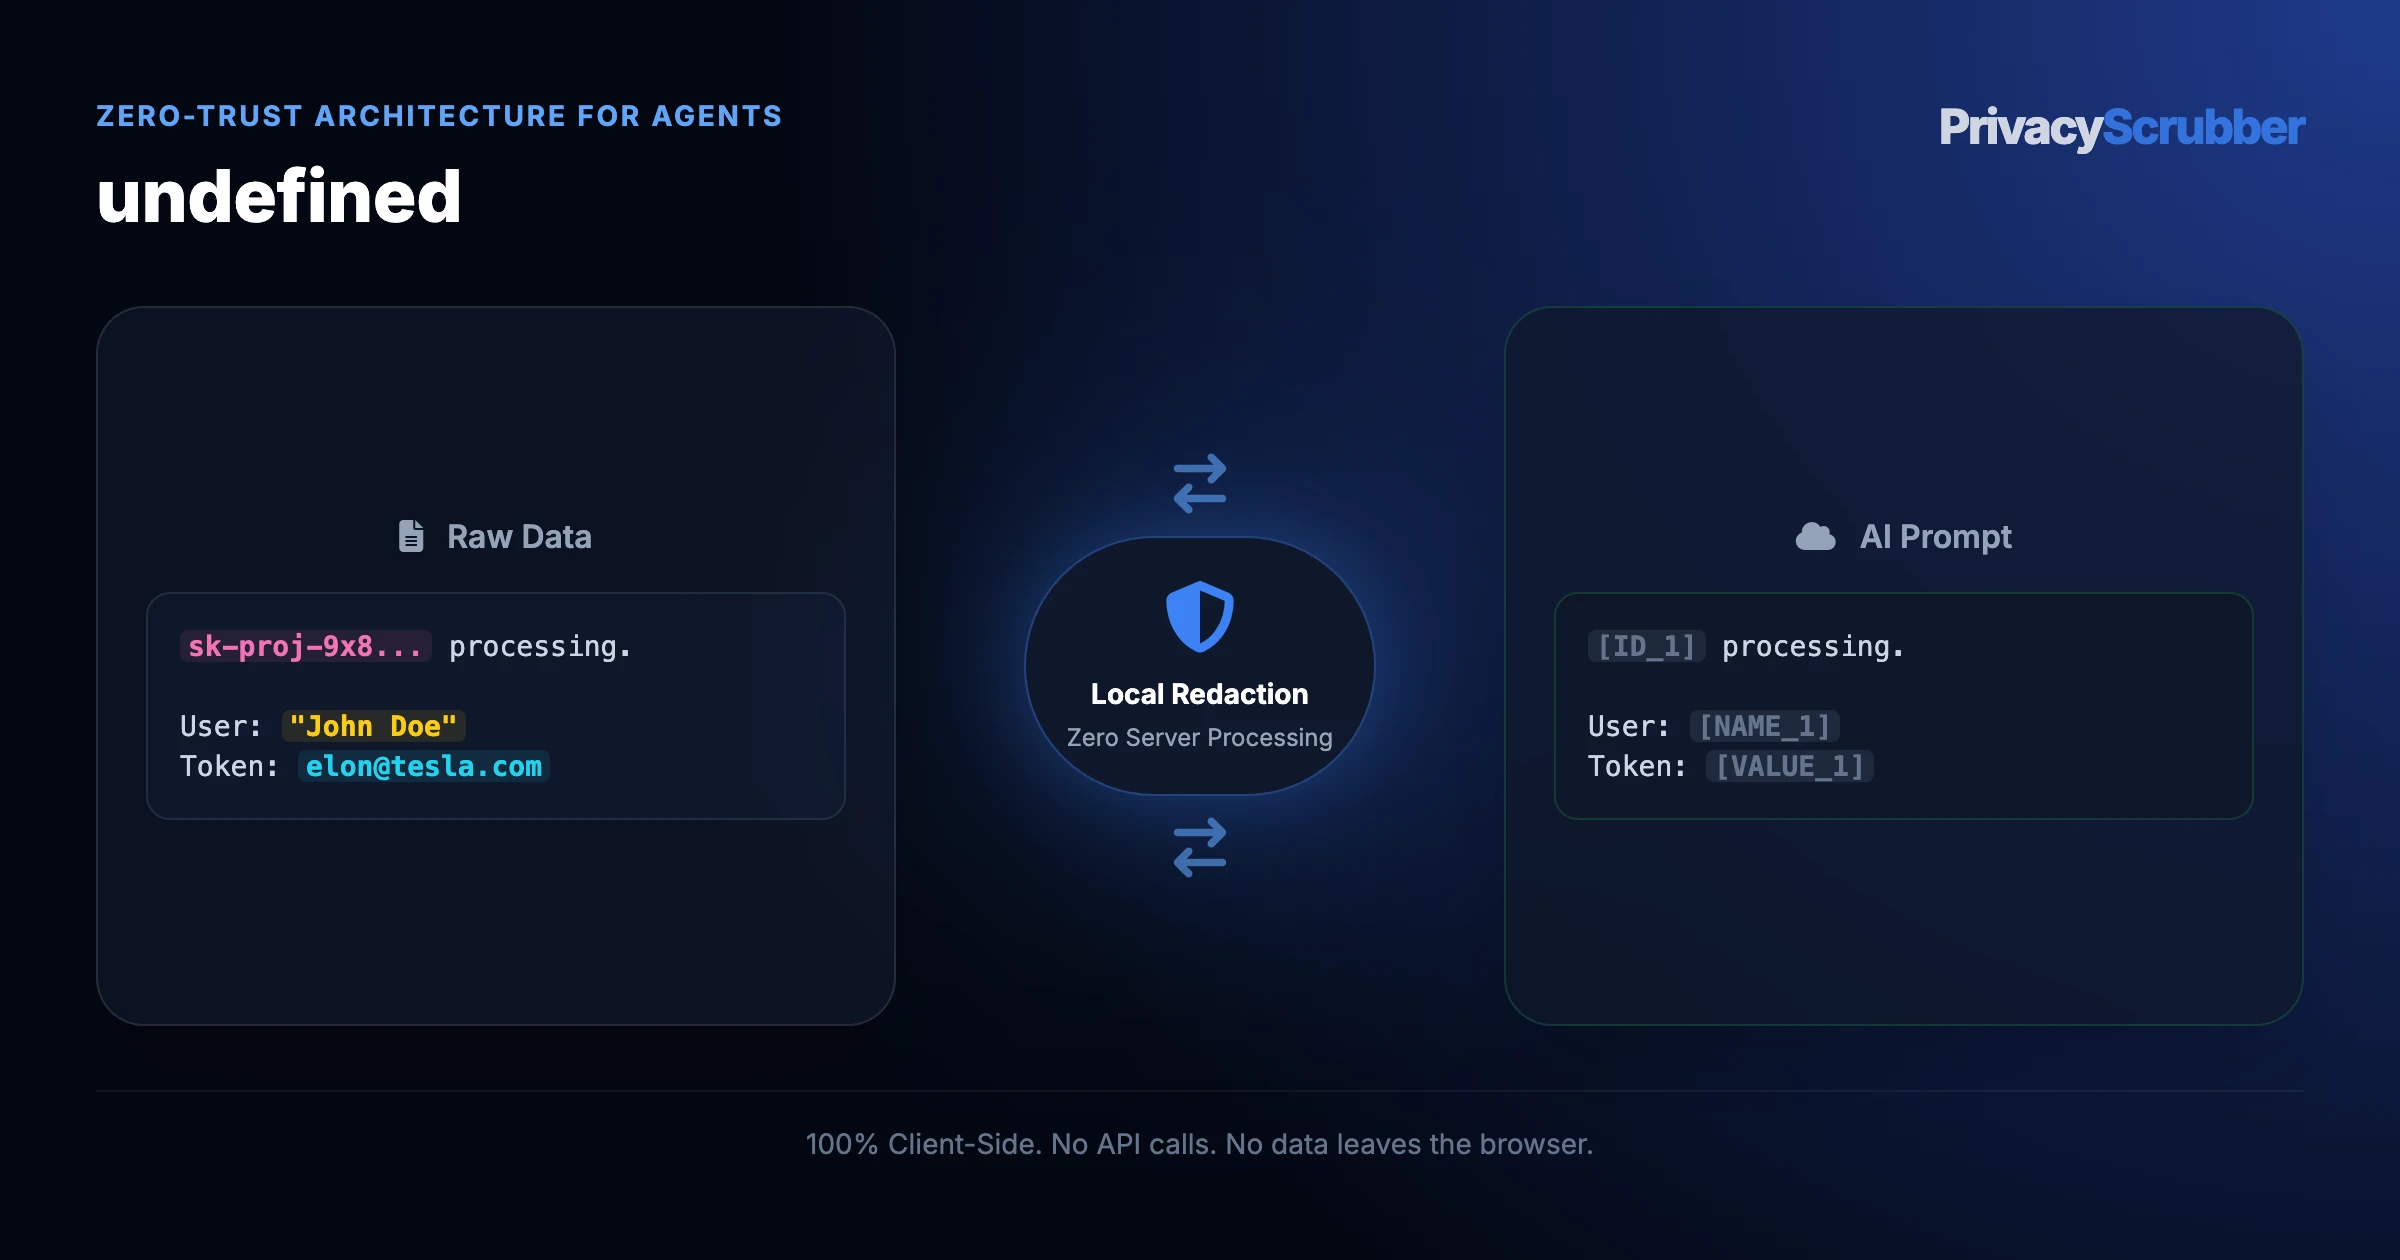
Claude Desktop's Model Context Protocol (MCP) architecture enables the LLM to read local directories, query internal SQL databases, and inspect git repositories directly on the user's workstation. Without a local stdio sanitization layer, every file chunk retrieved by an MCP server is transmitted in cleartext to Anthropic's cloud API. Deploying @privacyscrubber/mcp-server intercepts and tokenizes PII and secrets in local RAM before egress.
What AI Engineers and Agent Builders Send to AI During Claude Desktop Local PII Sanitization
Operationalizing Claude Desktop Local PII Sanitization under and emerging agentic AI governance guidance demands blocking and emerging agentic AI governance guidance egress gaps before AutoGPT sees claude desktop local sanitization. Read AI Agents & RAG AI privacy guides for deterministic [SECRET_1] masking.
Every unmasked claude desktop local sanitization query sent outside creates persistent exposure on AutoGPT. Sanitize prompts, local files, and database queries in Claude Desktop using our local stdio MCP server. 100% local browser RAM processing with zero egress. Without local volatile memory engine, enterprise AI architects face and emerging agentic AI governance guidance egress gaps.
The Hidden Egress Risk of Claude Desktop & Local MCP Connectors
Anthropic's Claude Desktop application paired with the Model Context Protocol (MCP) has transformed how executives, legal teams, and software engineers interact with local data. By linking Claude Desktop to local folders, internal databases, and CRM exports, autonomous AI agents can synthesize complex reports across dozens of documents in seconds.
However, traditional network DLP and cloud CASB gateways are blind to local desktop agent workflows or block Claude Desktop entirely. When an MCP connector reads a local spreadsheet, legal contract, or log file, the raw contents are packaged into an HTTPS payload and dispatched to Anthropic's inference cluster. Under GDPR Article 32 and SOC 2 CC6.1, organizations require a deterministic pre-transmission boundary on the workstation itself.
Production Configuration: claude_desktop_config.json
100% Local stdio · 0ms Network OverheadAdd the following block to ~/Library/Application Support/Claude/claude_desktop_config.json (macOS) or %APPDATA%Claudeclaude_desktop_config.json (Windows):
{
  "mcpServers": {
    "privacyscrubber": {
      "command": "npx",
      "args": ["-y", "@privacyscrubber/mcp-server"]
    }
  }
}
Supports session isolation via session_id across all 7 tools: sanitize_text, reveal_text, sanitize_file, guard_git_diff, guard_rag_chunk, audit_compliance, and reset_session.
Unprotected Claude Desktop Risks
- Silent Filesystem Ingestion: Local filesystem MCP tools sweep entire project directories—including unmasked client contracts and .env files—into cloud context windows.
- Database Query Egress: SQL MCP servers return raw customer rows (emails, SSNs, IBANs) directly into Anthropic's cloud prompt history.
- Zero Audit Visibility: Security teams lack cryptographic proof of whether sensitive identifiers were stripped prior to desktop AI ingestion.
PrivacyScrubber Local MCP Shield
- 30 Specialized Industry Profiles: Enforce HIPAA Safe Harbor, PCI-DSS, Legal Privilege, or DevSecOps secret rules locally in V8 memory.
- Cryptographic Compliance Receipts: Generate SHA-256 verification receipts via
audit_compliancefor CISO and DPO governance logs. - Multi-Agent Session Isolation: Concurrent agent workflows maintain isolated surrogate maps with FIFO memory bounds.
Explore Connected AI Agent & MCP Security Guides
Review our comprehensive AI Agents & Autonomous Workflow Privacy Hub, including our architecture deep-dive on MCP Data Sanitization and Cursor AI Source Code Privacy. For multi-agent orchestration frameworks, inspect CrewAI & AutoGen Agentic Memory PII Redaction.
Balancing AI Context & Privacy in Claude Desktop Local PII Sanitization
Use the classification table below to separate high-liability Claude Desktop Local PII Sanitization attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Routing Endpoints (anthropic data protection) | REDACT | [SECRET_1] | Blocks contact linkage when enterprise AI architects analyze claude desktop local sanitization batches. |
| Entity Names (AI Agents & RAG) | REDACT | [NAME_1] | Maintains multi-turn coherence on claude desktop local sanitization without exposing raw parties. |
| Subject Identifiers (claude desktop local sanitization) | REDACT | [NAME_1] | and emerging agentic AI governance guidance guard prevents AutoGPT from retaining personal Claude Desktop Local PII Sanitization records. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets AutoGPT trace root causes cleanly inside sanitized claude privacy pii logs. |
| Non-PII Workflow Constraints | PRESERVE | Cleartext Context | Preserves reasoning constraints across Claude Desktop Local PII Sanitization prompts sent offline. |
| Domain Instructions (AI Agents & RAG) | PRESERVE | Cleartext Logic | Retains workflow intent so enterprise AI architects get actionable anthropic data protection outputs. |
Copy-Paste Safe Instruction for Claude Desktop Local PII Sanitization
Copy this prompt frame when handing sanitized Claude Desktop Local PII Sanitization context to frontier LLMs under strict zero-egress rules:
Analyze Claude Desktop Local PII Sanitization (claude privacy pii) for enterprise AI architects.
Surrogate markers [NAME_1] and [EMAIL_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Analyze Claude Desktop Local PII Sanitization (claude privacy pii) for enterprise AI architects.
Surrogate markers [NAME_1] and [EMAIL_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Why AI Safety and Security Governance Teams Flag Unmasked Prompts in Claude Desktop Local PII Sanitization
Strict and emerging agentic AI governance guidance mandates leave no margin for and emerging agentic AI governance guidance egress gaps. Combining Claude Desktop Local PII Sanitization workflows with zero-trust data sanitization for model context protocol (MCP) workflows keeps anthropic data protection off LlamaIndex.
Local Tokenization Architecture: Claude Desktop Local PII Sanitization
To avoid proxy lag on Claude Desktop Local PII Sanitization, local RAM (AI Agents & RAG) tokenizes claude desktop local sanitization and claude privacy pii locally into [ID_1] following batch anonymize crm exports & lead lists for AI analysis.
Security teams verify Claude Desktop Local PII Sanitization by scrubbing anthropic data protection totally disconnected so volatile dictionaries obey redact screenshots and scanned PDFs before uploading to ChatGPT.
