
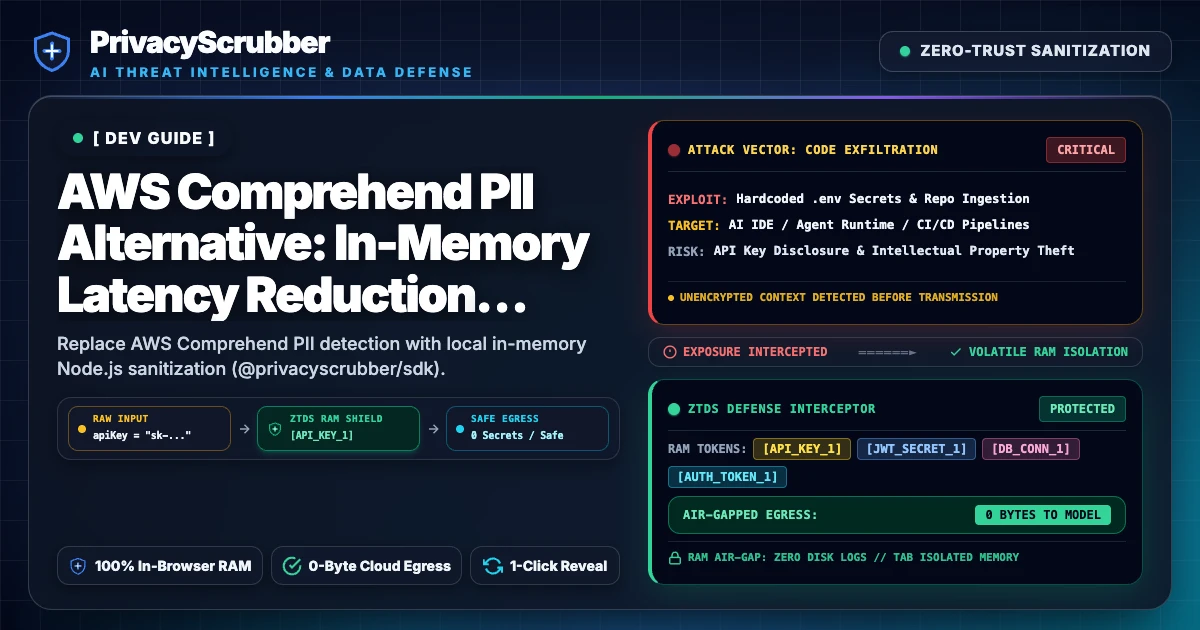
AWS Comprehend PII detection charges per 100-character unit and adds 200ms–300ms of latency per call, making real-time generative AI interactions sluggish. In addition, Comprehend does not provide built-in token restoration for AI completions. The PrivacyScrubber SDK runs locally in Node.js heap memory, providing bidirectional tokenization in <0.82ms without AWS API credentials.
Why Unmasked Prompts Break AWS Comprehend PII Alternative Security
Achieving verifiable data protection for AWS Comprehend PII Alternative is a foundational requirement when software engineers, devops teams, and security engineers integrate GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools. Because cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs, unmasked aws comprehend pii alternative payloads create immediate exposure across Software Development perimeters. Our Software Development AI privacy guides detail how to isolate comprehend pii latency reduction in local RAM before any cloud API call occurs.
The core vulnerability in AWS Comprehend PII Alternative occurs the millisecond unredacted aws comprehend pii alternative or comprehend pii latency reduction text crosses the browser or application socket. Replace AWS Comprehend PII detection with local in-memory Node.js sanitization (@privacyscrubber/sdk). 100% local browser RAM processing with zero egress. Without local RAM interception via @privacyscrubber/sdk (<0.8ms Node.js/TS RAM) & @privacyscrubber/mcp-server, software engineers, devops teams, and security engineers remain exposed to leaking API keys, database credentials, user PII from logs, and internal system architecture to AI code assistants that may log prompts.
To eliminate the 240ms latency of AWS Comprehend PII, switch to @privacyscrubber/sdk.
It runs in <0.82ms in Node.js volatile memory, eliminates AWS API costs, and includes built-in bidirectional token reversal.
npx @privacyscrubber/sdk demoComplete Implementation: AWS Comprehend Replacement
npm install @privacyscrubber/sdk openaiimport OpenAI from 'openai';
import { sanitize, restore } from '@privacyscrubber/sdk';
const openai = new OpenAI({ apiKey: process.env.OPENAI_API_KEY });
// Replace heavy @aws-sdk/client-comprehend with 1 in-memory call
const rawPrompt = 'Customer Rebecca Vance (Phone: 415-555-0144, SSN: 901-22-3344) requested balance confirmation.';
// 1. Sanitize in local RAM in <0.82ms (Zero IAM roles, zero AWS network calls)
const { scrubbedText, tokenMap } = sanitize(rawPrompt, {
profile: 'General',
detectSecrets: true
});
console.log('Sanitized output:', scrubbedText);
// "Customer [NAME_1] (Phone: [PHONE_1], SSN: [SSN_1]) requested balance confirmation."
// 2. Invoke AI model with sanitized prompt (0 PII egress):
const completion = await openai.chat.completions.create({
model: 'gpt-4o',
messages: [{ role: 'user', content: scrubbedText }]
});
const llmResponse = completion.choices[0].message.content || '';
// 3. Restore authentic values in local RAM:
const cleartextResponse = restore(llmResponse, tokenMap).restoredText;
console.log(cleartextResponse);Need security, compliance, or CISO sign-off before deploying to production? Copy our pre-filled vendor-risk evaluation memo covering GDPR Art. 25/28, zero-subprocessor architecture, and air-gapped memory isolation.
# Vendor Architecture & Security Evaluation: @privacyscrubber/sdk **Project**: Enterprise AI / LLM Integration (AWS Comprehend PII Alternative: In-Memory Latency Reduction (<1ms)) **Target Tier**: Developer SDK ($299/mo or $2,990/yr flat) **Vendor**: PrivacyScrubber (ZTDS - Zero-Trust Data Sanitization) **Technical Classification**: In-process ZTDS™ PII Redaction Library ## 1. Compliance & Data Protection Rationale - **GDPR Art. 25 & 28**: Prompt payloads are sanitized directly in local V8 heap memory (<1ms) before transmitting to model APIs. No external subprocessors or third-party DLP cloud vendors are introduced. - **HIPAA Safe Harbor & SOC 2 Type II**: Replaces cleartext identifiers (names, emails, SSNs, financial IDs, tokens) with deterministic category tokens ([NAME_1], [EMAIL_1]), mathematically preventing sensitive data leakage into model training or provider logging. - **Zero Data Retention**: The session token mapping is volatile, held strictly in-memory (RAM-only), tab/thread-isolated, and immediately wiped upon completion. ## 2. Infrastructure & Latency Benchmark - **Execution Overhead**: < 0.85 ms per 10KB payload (vs. 40ms+ for Presidio Docker, 200ms+ for Cloud DLP APIs). - **Network Egress**: 0 Bytes. Functions completely in air-gapped / Airplane Mode environments. - **DevOps Footprint**: ~180 KB native Node.js/WASM package. 0 external daemon, 0 Redis requirement, 0 Python container maintenance. ## 3. Commercials & Procurement - **License**: $299/month flat (or $2,990/year) covering unlimited internal nodes, microservices, and RAG pipelines. - **Vendor Risk & DPA**: Zero-DPA posture (software runs entirely inside our tenant boundary; zero data egresses to vendor servers). - **Payment Method**: Corporate Net 30 Invoicing or Credit Card via Merchant of Record (Paddle).Compliance Verification
By running on-premise without cloud calls, applications satisfy SOC 2 Type II Confidentiality controls. See our Google Cloud DLP Alternative Guide for multi-cloud comparisons.
ZTDS™ Field Governance for AWS Comprehend PII Alternative Workflows
Effective sanitization of AWS Comprehend PII Alternative requires stripping direct identifiers while keeping structural and quantitative context intact for model reasoning:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Embedded Secrets, Tax IDs & Session Identifiers in AWS Comprehend PII Alternative | REDACT | [SECRET_1], [API_KEY_1] | Intercepts high-liability literals before cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs. |
| Secondary Regulated Attributes (local comprehend replacement javascript) | REDACT | [EMAIL_1] | Satisfies OWASP guidelines on secrets management data minimization by replacing sensitive Software Development strings in local RAM. |
| Contact & Routing Endpoints (aws dlp alternative nodejs) | REDACT | [DB_URI_1] | Eliminates cross-record linkage and unauthorized sub-processor indexing during AWS Comprehend PII Alternative. |
| Non-Identifying Domain Logic & Operational Instructions | PRESERVE | Cleartext Narrative | Preserves 100% of analytical instructions for aws dlp alternative nodejs so local detokenization yields production-ready output. |
| Regulatory Clause Citations & Policy Taxonomy (OWASP guidelines on secrets management) | PRESERVE | Cleartext Citations | Allows the AI model to map AWS Comprehend PII Alternative findings against statutory controls and audit frameworks. |
| Relative Timelines, Status Codes & Error Severities | PRESERVE | Cleartext (ISO Sequence) | Maintains chronological ordering and root-cause diagnostics across comprehend pii latency reduction workflows. |
Safe LLM Prompt Template for AWS Comprehend PII Alternative
Designed for software engineers, DevOps teams, and security engineers: copy this prompt to process tokenized AWS Comprehend PII Alternative records with zero cloud PII exposure:
System Role: Software Development Compliance & Technical Analyst for AWS Comprehend PII Alternative.
Input State: Pre-sanitized in volatile memory under OWASP guidelines on secrets management safeguards ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]).

Deliverables:
1. Analyze relationships between [SECRET_1] and [API_KEY_1] within the aws comprehend pii alternative workflow.
2. Highlight any policy, schema, or execution gaps related to aws dlp alternative nodejs.
3. Preserve every [SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1] tag intact in your output for 1-click local re-hydration.

[PASTE SANITIZED PAYLOAD HERE]
System Role: Software Development Compliance & Technical Analyst for AWS Comprehend PII Alternative.
Input State: Pre-sanitized in volatile memory under OWASP guidelines on secrets management safeguards ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]).

Deliverables:
1. Analyze relationships between [SECRET_1] and [API_KEY_1] within the aws comprehend pii alternative workflow.
2. Highlight any policy, schema, or execution gaps related to aws dlp alternative nodejs.
3. Preserve every [SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1] tag intact in your output for 1-click local re-hydration.

[PASTE SANITIZED PAYLOAD HERE]
Why DevSecOps and Security Engineering Teams Flag Unmasked Prompts in AWS Comprehend PII Alternative
Compliance frameworks for Software Development (OWASP guidelines on secrets management, SOC 2 Type II trust service criteria, and GDPR Article 25 (data protection by design)) require proactive data minimization at the ingestion boundary. When implementing AWS Comprehend PII Alternative, teams reference microsoft presidio docker vs in-memory ZTDS™ to neutralize cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs and keep aws comprehend pii alternative mappings strictly inside volatile RAM.
Zero-Trust Code and Engineering Tokenization for AWS Comprehend PII Alternative
By deploying @privacyscrubber/sdk (<0.8ms Node.js/TS RAM) & @privacyscrubber/mcp-server, PrivacyScrubber intercepts AWS Comprehend PII Alternative payloads at the local boundary and converts aws comprehend pii alternative into deterministic placeholders ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]). Mirroring the architecture in enterprise PII masking workspace, external AI models only process sanitized logic while the volatile token map stays isolated in your browser or process memory.
This zero-egress architecture for AWS Comprehend PII Alternative is independently verifiable via the Airplane Mode Standard: disconnect your network, sanitize a sample aws comprehend pii alternative payload into [SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1], and confirm 0 outbound packets in DevTools. This satisfies best ChatGPT privacy extensions compared (2026) and generates a cryptographic SHA-256 compliance receipt for OWASP guidelines on secrets management audits.
