
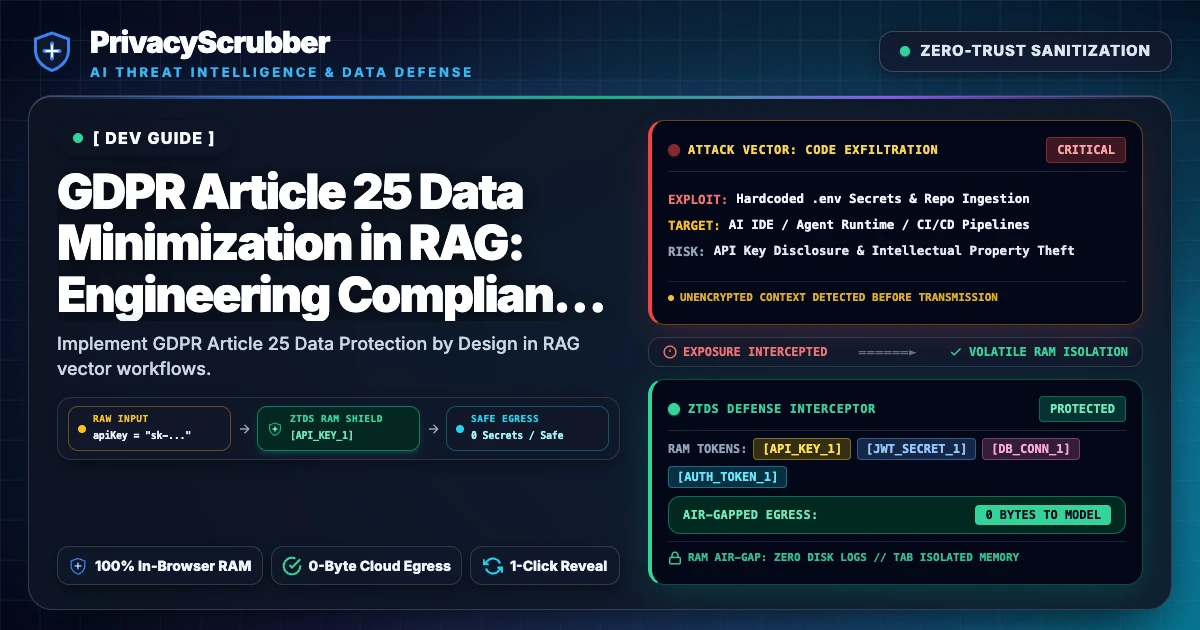
Article 25 of the GDPR legally mandates that data controllers implement appropriate technical measures—such as pseudonymization—both at the time of the determination of the means for processing and at the time of the processing itself. In RAG pipelines, ingesting unredacted customer data violates Article 25 by default. @privacyscrubber/sdk provides the architectural drop-in for programmatic data minimization.
Data Leakage Risks in GDPR Article 25 Data Minimization in RAG for Software Developers
To operationalize GDPR Article 25 Data Minimization in RAG without violating OWASP guidelines on secrets management, enterprises must eliminate cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs. When software engineers, devops teams, and security engineers prompt GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools with unredacted gdpr article 25 rag data minimization context, sensitive identifiers enter external telemetry queues. Our Software Development AI privacy guides establish deterministic local sanitization ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) prior to network serialization.
When software engineers, devops teams, and security engineers paste or stream raw GDPR Article 25 Data Minimization in RAG payloads into GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools, sensitive identifiers ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) are exposed at the moment of TLS serialization. Implement GDPR Article 25 Data Protection by Design in RAG vector workflows. Redact customer PII in local browser RAM with zero cloud egress or leaks. Legacy cloud filters cannot prevent leaking API keys, database credentials, user PII from logs, and internal system architecture to AI code assistants that may log prompts once cleartext leaves the device.
To satisfy GDPR Article 25 (Data Protection by Design) in RAG pipelines, sanitize customer inputs at the application boundary with @privacyscrubber/sdk.
It enforces sub-millisecond in-process pseudonymization (<0.8ms), ensuring downstream LLMs and vector stores never receive cleartext personal data.
npx @privacyscrubber/sdk demoComplete Implementation: GDPR Article 25 RAG Boundary
npm install @privacyscrubber/sdk openaiimport OpenAI from 'openai';
import { sanitize, restore } from '@privacyscrubber/sdk';
const openai = new OpenAI({ apiKey: process.env.OPENAI_API_KEY });
// Ingestion Pipeline: Customer Support Ticket
const rawCustomerTicket = 'User Claire Dubois (claire.dubois@paris-tech.fr, +33 1 42 68 55 00) reports invoice discrepancy #INV-9921.';
// 1. Enforce Data Minimization in local memory before RAG processing (<0.8ms)
const { scrubbedText, tokenMap } = sanitize(rawCustomerTicket, {
profile: 'General'
});
// 2. Vectorize and process ONLY the pseudonymized payload (Zero PII egress)
console.log('Sanitized Payload for Vector Embeddings & LLM:');
console.log(scrubbedText);
// 3. Safely summarize ticket via LLM:
const completion = await openai.chat.completions.create({
model: 'gpt-4o',
messages: [{ role: 'user', content: `Summarize support ticket:\n\n${scrubbedText}` }]
});
const rawSummary = completion.choices[0].message.content || '';
// 4. Reverse only when serving verified data subjects in authorized sessions:
const authorizedOutput = restore(rawSummary, tokenMap).restoredText;
console.log('\nAuthorized Output for Support Agent:');
console.log(authorizedOutput);Need security, compliance, or CISO sign-off before deploying to production? Copy our pre-filled vendor-risk evaluation memo covering GDPR Art. 25/28, zero-subprocessor architecture, and air-gapped memory isolation.
# Vendor Architecture & Security Evaluation: @privacyscrubber/sdk **Project**: Enterprise AI / LLM Integration (GDPR Article 25 Data Minimization in RAG: Engineering Compliance Guide) **Target Tier**: Developer SDK ($299/mo or $2,990/yr flat) **Vendor**: PrivacyScrubber (ZTDS - Zero-Trust Data Sanitization) **Technical Classification**: In-process ZTDS™ PII Redaction Library ## 1. Compliance & Data Protection Rationale - **GDPR Art. 25 & 28**: Prompt payloads are sanitized directly in local V8 heap memory (<1ms) before transmitting to model APIs. No external subprocessors or third-party DLP cloud vendors are introduced. - **HIPAA Safe Harbor & SOC 2 Type II**: Replaces cleartext identifiers (names, emails, SSNs, financial IDs, tokens) with deterministic category tokens ([NAME_1], [EMAIL_1]), mathematically preventing sensitive data leakage into model training or provider logging. - **Zero Data Retention**: The session token mapping is volatile, held strictly in-memory (RAM-only), tab/thread-isolated, and immediately wiped upon completion. ## 2. Infrastructure & Latency Benchmark - **Execution Overhead**: < 0.85 ms per 10KB payload (vs. 40ms+ for Presidio Docker, 200ms+ for Cloud DLP APIs). - **Network Egress**: 0 Bytes. Functions completely in air-gapped / Airplane Mode environments. - **DevOps Footprint**: ~180 KB native Node.js/WASM package. 0 external daemon, 0 Redis requirement, 0 Python container maintenance. ## 3. Commercials & Procurement - **License**: $299/month flat (or $2,990/year) covering unlimited internal nodes, microservices, and RAG pipelines. - **Vendor Risk & DPA**: Zero-DPA posture (software runs entirely inside our tenant boundary; zero data egresses to vendor servers). - **Payment Method**: Corporate Net 30 Invoicing or Credit Card via Merchant of Record (Paddle).Compliance Verification
Enforcing data minimization at the application boundary aligns with GDPR Article 25 Technical Controls. Check our Pinecone Vector Upsert Guide for vector storage.
Entity Handling Standard for GDPR Article 25 Data Minimization in RAG
Effective sanitization of GDPR Article 25 Data Minimization in RAG requires stripping direct identifiers while keeping structural and quantitative context intact for model reasoning:
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Contact & Routing Endpoints (gdpr compliance rag architecture) | REDACT | [DB_URI_1] | Eliminates cross-record linkage and unauthorized sub-processor indexing during GDPR Article 25 Data Minimization in RAG. |
| Authentication, Account & Reference Keys (data protection by design ai) | REDACT | [API_KEY_1] | Blocks credential, account, or case-number exfiltration across Software Development telemetry and vendor logs. |
| Primary Identity & Subject Records (gdpr article 25 rag data minimization) | REDACT | [SECRET_1] | OWASP guidelines on secrets management direct identifier guard: prevents cloud LLMs from associating GDPR Article 25 Data Minimization in RAG prompts with real individuals. |
| Relative Timelines, Status Codes & Error Severities | PRESERVE | Cleartext (ISO Sequence) | Maintains chronological ordering and root-cause diagnostics across data protection by design ai workflows. |
| Quantitative Metrics, Ratios & Aggregated Totals | PRESERVE | Cleartext ($ / % / Deltas) | Enables accurate mathematical reasoning and variance analysis for GDPR Article 25 Data Minimization in RAG without identity exposure. |
| Structural Schema, Keys & GDPR Article 25 Data Minimization in RAG Syntax | PRESERVE | Cleartext Structure | Required so the LLM can parse gdpr article 25 rag data minimization hierarchy, JSON/SQL grammar, and document formatting. |
Bijective Prompt Blueprint for GDPR Article 25 Data Minimization in RAG
Designed for software engineers, DevOps teams, and security engineers: copy this prompt to process tokenized GDPR Article 25 Data Minimization in RAG records with zero cloud PII exposure:
You are an enterprise Software Development specialist reviewing a sanitized GDPR Article 25 Data Minimization in RAG payload.
All regulated identifiers for gdpr article 25 rag data minimization and data protection by design ai have been replaced in local RAM with deterministic ZTDS™ tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]).

Tasks:
1. Evaluate the structural logic, anomalies, and operational metrics in the GDPR Article 25 Data Minimization in RAG input.
2. Formulate actionable recommendations aligned with OWASP guidelines on secrets management.
3. Keep all bracketed tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) verbatim so local reverse detokenization restores exact values.

[PASTE SANITIZED GDPR ARTICLE 25 DATA MINIMIZATION IN RAG PAYLOAD HERE]
You are an enterprise Software Development specialist reviewing a sanitized GDPR Article 25 Data Minimization in RAG payload.
All regulated identifiers for gdpr article 25 rag data minimization and data protection by design ai have been replaced in local RAM with deterministic ZTDS™ tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]).

Tasks:
1. Evaluate the structural logic, anomalies, and operational metrics in the GDPR Article 25 Data Minimization in RAG input.
2. Formulate actionable recommendations aligned with OWASP guidelines on secrets management.
3. Keep all bracketed tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) verbatim so local reverse detokenization restores exact values.

[PASTE SANITIZED GDPR ARTICLE 25 DATA MINIMIZATION IN RAG PAYLOAD HERE]
How DevSecOps and Security Engineering Teams Enforce Zero-Egress on GDPR Article 25 Data Minimization in RAG
Because OWASP guidelines on secrets management, SOC 2 Type II trust service criteria, and GDPR Article 25 (data protection by design), security and DPO leads cannot approve GDPR Article 25 Data Minimization in RAG workflows that suffer from cloud DLP proxy round-trips (150ms–400ms WAN latency) and cleartext inspection logs. Adopting the local sanitization methodology in stripe & PCI dss 4.0 credit card PAN scrubber in node.js (<1ms) converts gdpr article 25 rag data minimization into [SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1] before any external API interaction.
Running AI on GDPR Article 25 Data Minimization in RAG Without Sending Real Identifiers
PrivacyScrubber enforces Zero-Trust Data Sanitization (ZTDS™) for GDPR Article 25 Data Minimization in RAG via @privacyscrubber/sdk (<0.8ms Node.js/TS RAM) & @privacyscrubber/mcp-server. Sensitive gdpr article 25 rag data minimization and data protection by design ai fields are replaced in <1ms of local RAM with bijective tokens ([SECRET_1], [API_KEY_1], [DB_URI_1], [EMAIL_1]) prior to prompting GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools. This aligns with seed-stage compliance, allowing software engineers, devops teams, and security engineers to restore authentic values locally in 1 click once the model responds.
By validating GDPR Article 25 Data Minimization in RAG under the Airplane Mode Standard, software engineers, devops teams, and security engineers confirm that gdpr article 25 rag data minimization and data protection by design ai redaction executes 100% in local RAM—Directly supporting the technical standards in complete PDF text sanitization for enterprise AI workflows.
