
How to Use AI on Real Code and Engineering Data — Without Sending a Single Real Name
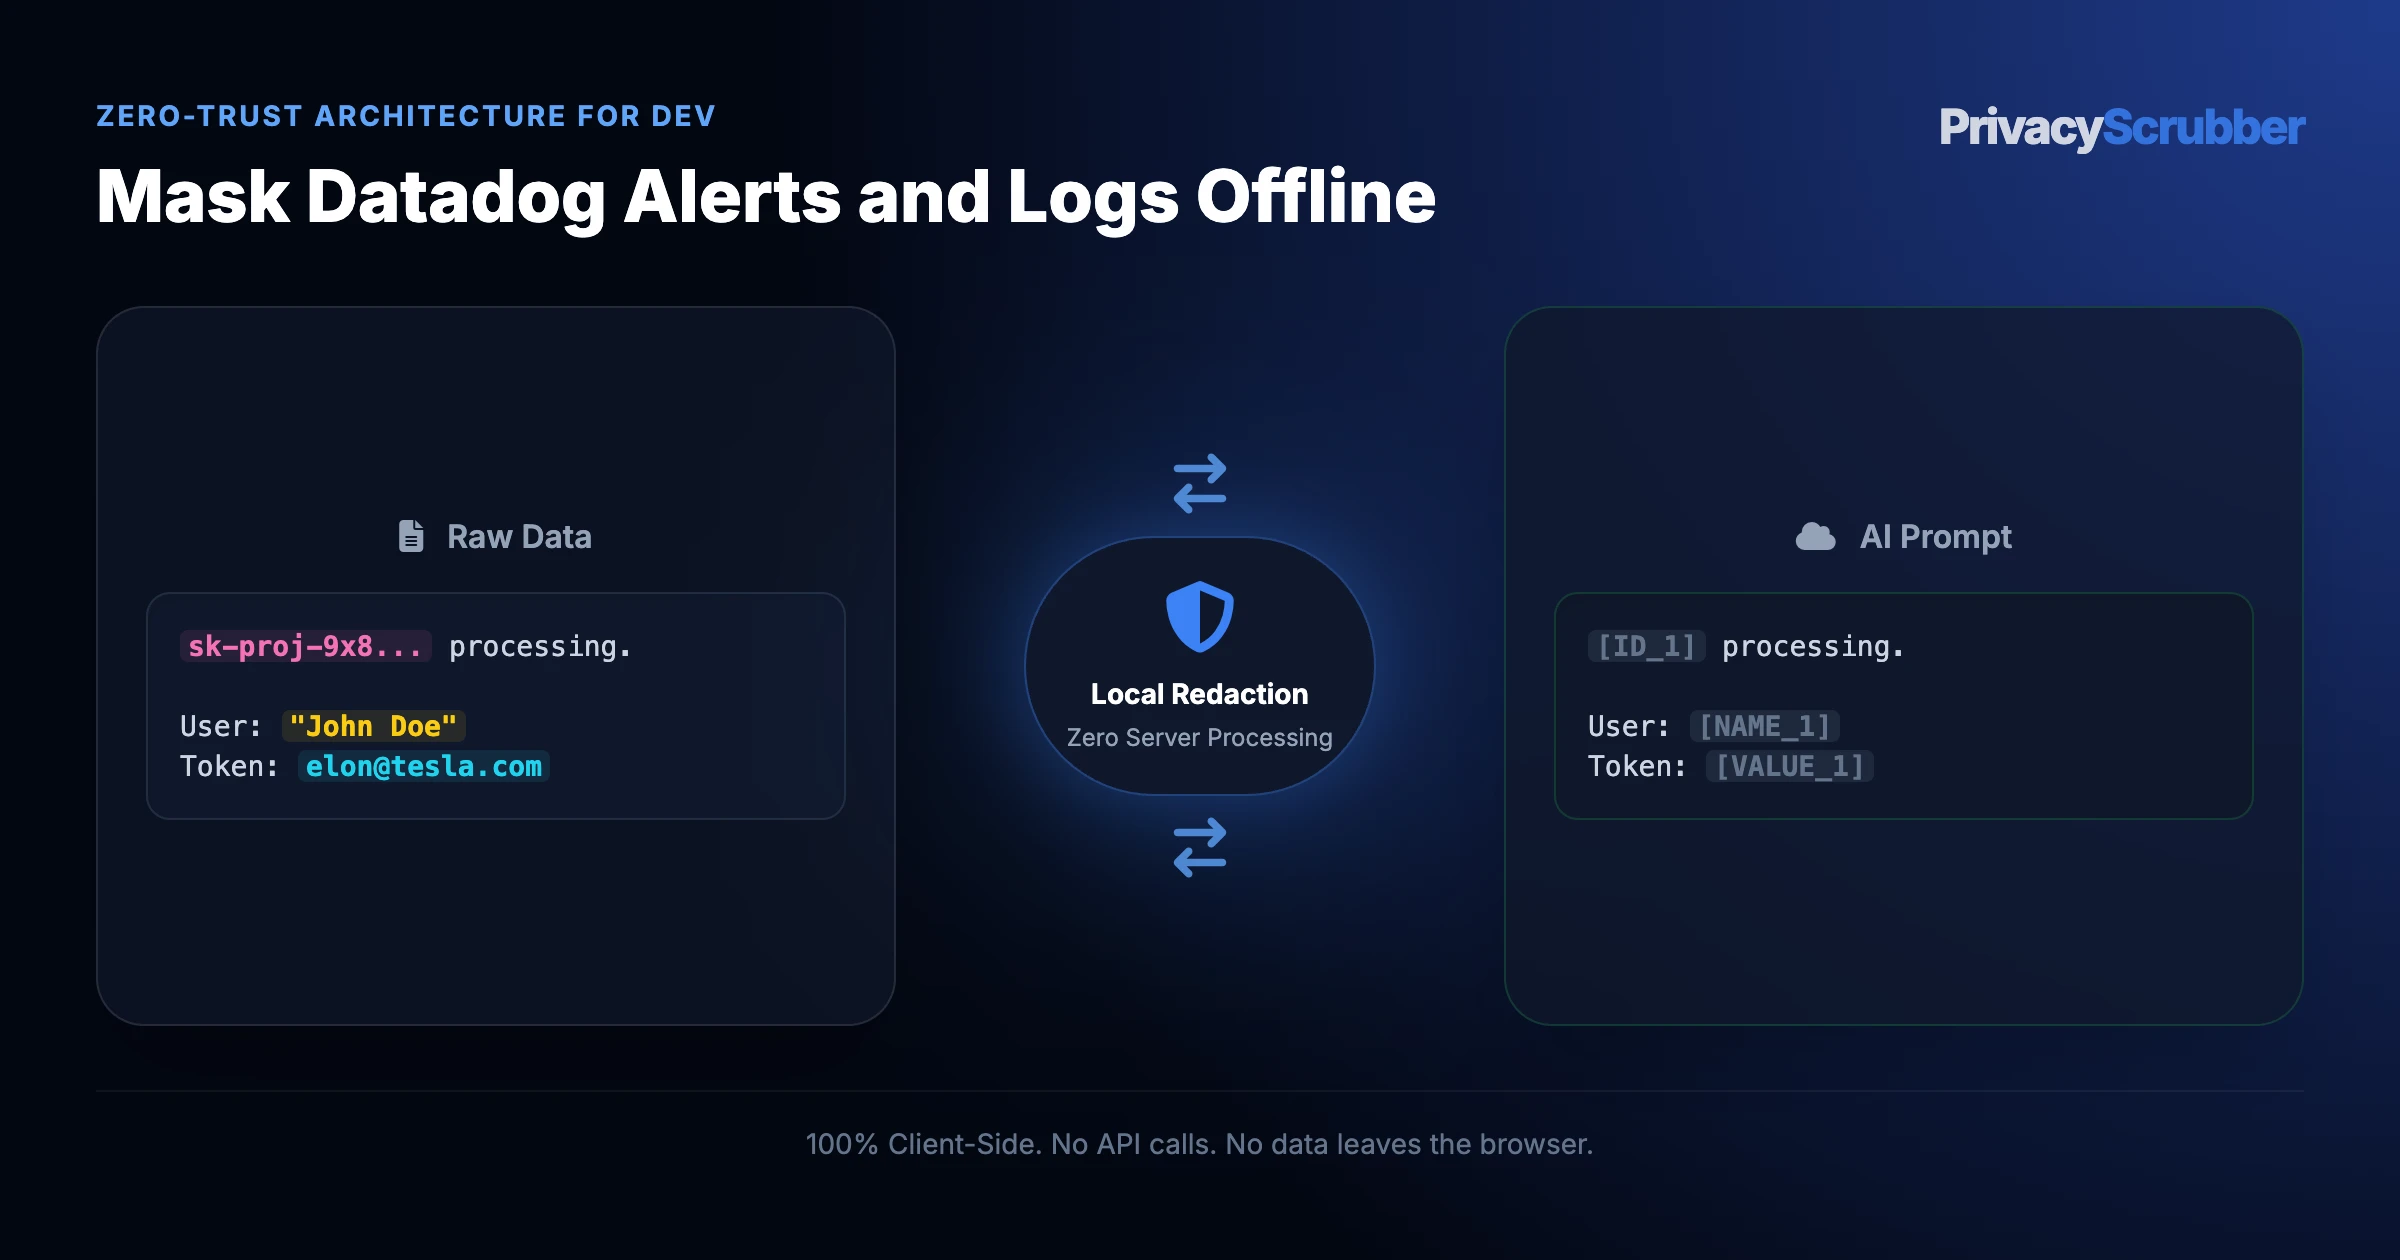
PrivacyScrubber implements Zero-Trust Data Sanitization (ZTDS) at the browser intake layer, giving teams the choice of a manual copy-paste dashboard or an automated workflow via the PrivacyScrubber Chrome Extension. Our engine performs local deterministic ZTDS™ detection matching to replace sensitive identifiers with deterministic tokens (e.g., [NAME_1], [ID_2]) before transmission. This architectural pattern mirrors industry standards for secure license distribution — ensuring that only sanitized, non-identifiable logic is processed by the AI. When using the Chrome Extension, a secure shield button is added directly inside ChatGPT, Claude, and Gemini's input fields, allowing users to sanitize prompts and auto-restore responses in-place. Processing data through browser-based deterministic ZTDS™ in-memory tokenization allows safe integration of GitHub Copilot, ChatGPT, Cursor AI, and AI-assisted debugging tools for complex tasks while preserving client privacy.
This zero-transmission architecture is independently auditable via our Airplane Mode Standard. By disconnecting your network and running a full scrub-and-restore cycle, you verify that no outbound packets are transmitted. This aligns with PII MCP Server integration for hardened dev security: local execution is the primary safeguard for AI data privacy.
