
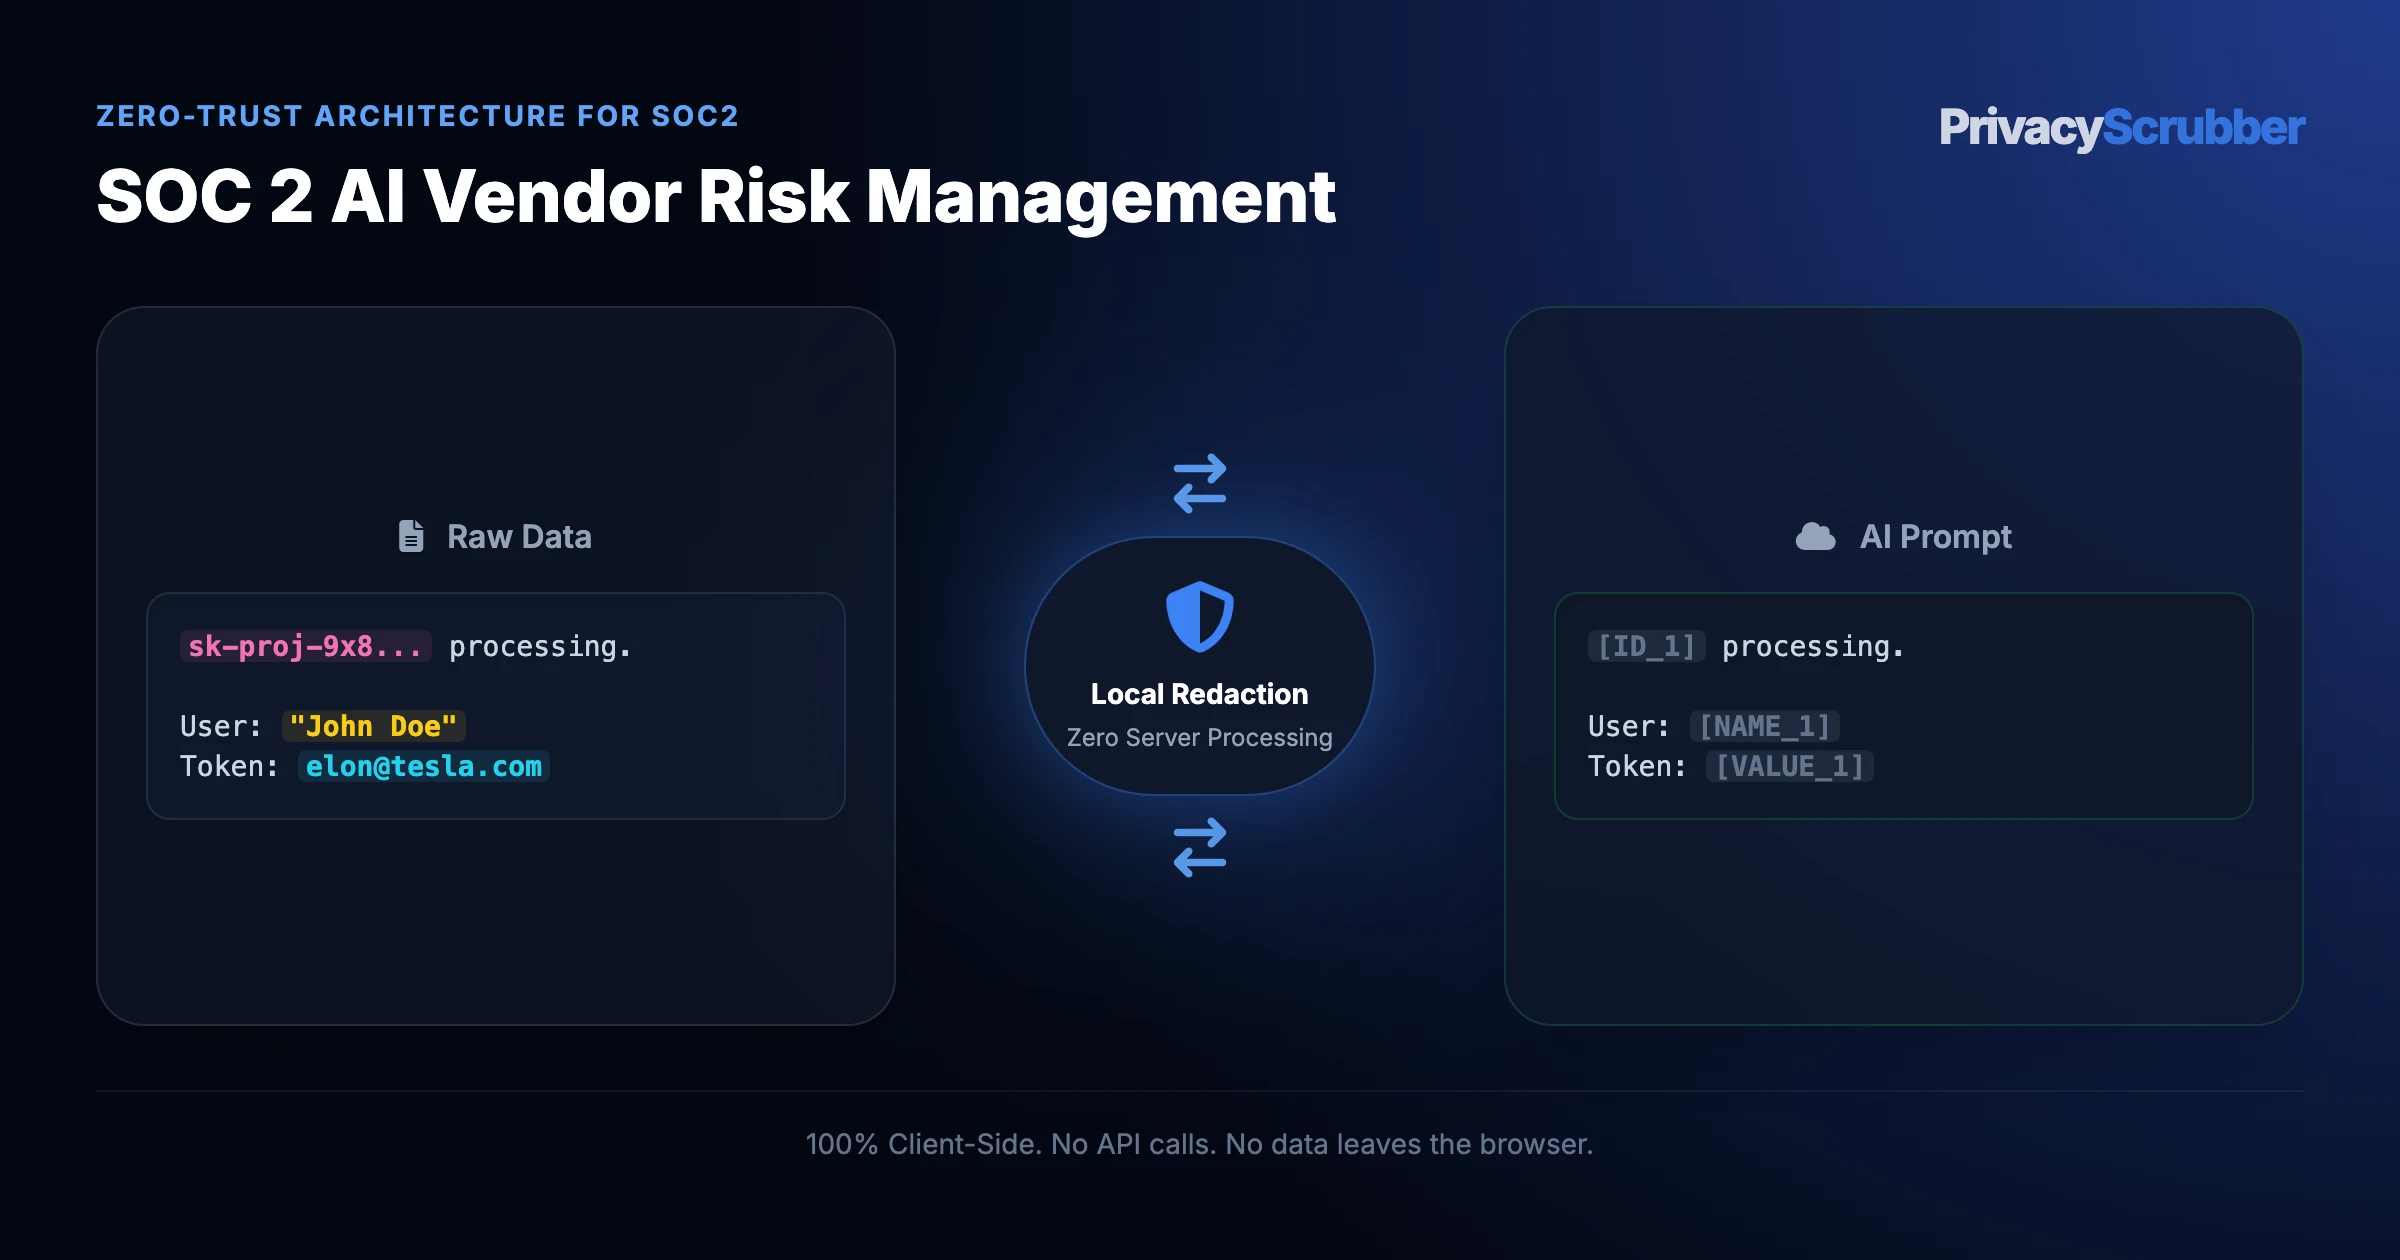
SOC 2 CC9.1 requires controls over data transmitted to third-party vendors. PrivacyScrubber provides an immediate technical control that satisfies CC9.1 from day one under our SOC 2 Type II Hub.
SOC 2 AI Vendor Risk Management Exposure Surface for Infosec and Audit Teams
For CISOs working on SOC 2 AI Vendor Risk Management, TEAMS & CISO SHA-256 receipts prevents CC6.1/CC6.7 cleartext egress gaps on SOC 2 AI vendor risk and CC9.1 third-party AI controls. Review SOC 2 AI privacy guides for sub-millisecond client safeguards.
Sending raw SOC 2 AI vendor risk strings into Vanta bypasses endpoint controls for CISOs. Manage SOC 2 vendor risk when using AI tools. Redact sensitive PII in local browser RAM with zero server egress or cloud leaks. Swapping entities to [SECRET_1] locally removes unmasked SOC 2 AI vendor risk exposure.
Local RAM Isolation for SOC 2 AI Vendor Risk Management
Cloud opt-out switches fail to prevent unmasked SOC 2 AI vendor risk exposure across distributed SOC 2 AI Vendor Risk Management tasks. Running SOC 2 AI vendor risk through TEAMS & CISO SHA-256 receipts turns risky literals into reversible [CUSTOMER_1] tokens offline.
Because [CUSTOMER_1] placeholders remain strictly ephemeral, CISOs can safely evaluate SOC 2 ChatGPT vendor assessment inside Drata and wipe all state instantly upon completion.
ZTDS™ Field Governance for SOC 2 AI Vendor Risk Management Workflows
Use the classification table below to separate high-liability SOC 2 AI Vendor Risk Management attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Internal IDs inside SOC 2 AI Vendor Risk Management | REDACT | [USER_1] / [SECRET_1] | Prevents CC6.1/CC6.7 cleartext egress gaps via pre-send TEAMS & CISO SHA-256 receipts substitution. |
| Private Records in SOC 2 AI Vendor Risk Management | REDACT | [CUSTOMER_1] | Replaces direct PII with [CUSTOMER_1] inside volatile client memory. |
| Routing Endpoints (SOC 2 ChatGPT vendor assessment) | REDACT | [CUSTOMER_1] | Blocks contact linkage when CISOs analyze SOC 2 AI vendor risk batches. |
| Domain Instructions (SOC 2) | PRESERVE | Cleartext Logic | Retains workflow intent so CISOs get actionable SOC 2 ChatGPT vendor assessment outputs. |
| Numeric Totals & Ratios (CC9.1 third-party AI controls) | PRESERVE | Cleartext ($ / %) | Enables accurate calculations across SOC 2 AI Vendor Risk Management without revealing identities. |
| Aggregation Counts & Deltas | PRESERVE | Cleartext Metrics | Supports statistical analysis of SOC 2 AI vendor risk without linking individuals. |
Bijective Prompt Blueprint for SOC 2 AI Vendor Risk Management
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Task for Vanta: Review masked SOC 2 AI Vendor Risk Management input (SOC 2 AI vendor risk).
1. Summarize findings around [USER_1] and [SECRET_1].
2. Highlight next actions for CISOs.
3. Preserve bracketed placeholders verbatim.

[INSERT TOKENIZED INPUT]
Task for Vanta: Review masked SOC 2 AI Vendor Risk Management input (SOC 2 AI vendor risk).
1. Summarize findings around [USER_1] and [SECRET_1].
2. Highlight next actions for CISOs.
3. Preserve bracketed placeholders verbatim.

[INSERT TOKENIZED INPUT]
SOC 2 Type II Trust Service Criteria (Privacy and Security) Mandate Checkpoints: SOC 2 AI Vendor Risk Management
Enforcing SOC 2 Type II Trust Service Criteria (Privacy and Security) on SOC 2 AI Vendor Risk Management connects directly with passing SOC 2 type ii with shadow AI risks—ensuring SOC 2 AI vendor risk becomes [USER_1] before cloud transit.
Safe LLM Workflows for SOC 2 AI Vendor Risk Management Teams
Zero-Trust rules for SOC 2 AI vendor risk execute natively inside TEAMS & CISO SHA-256 receipts, preserving [USER_1] co-references across Vanta while matching secure ChatGPT for cpa firms.
Disconnect Ethernet mid-session to confirm SOC 2 AI Vendor Risk Management converts SOC 2 AI vendor risk to [USER_1] cleanly as required by FDA AI software and PHI.
