
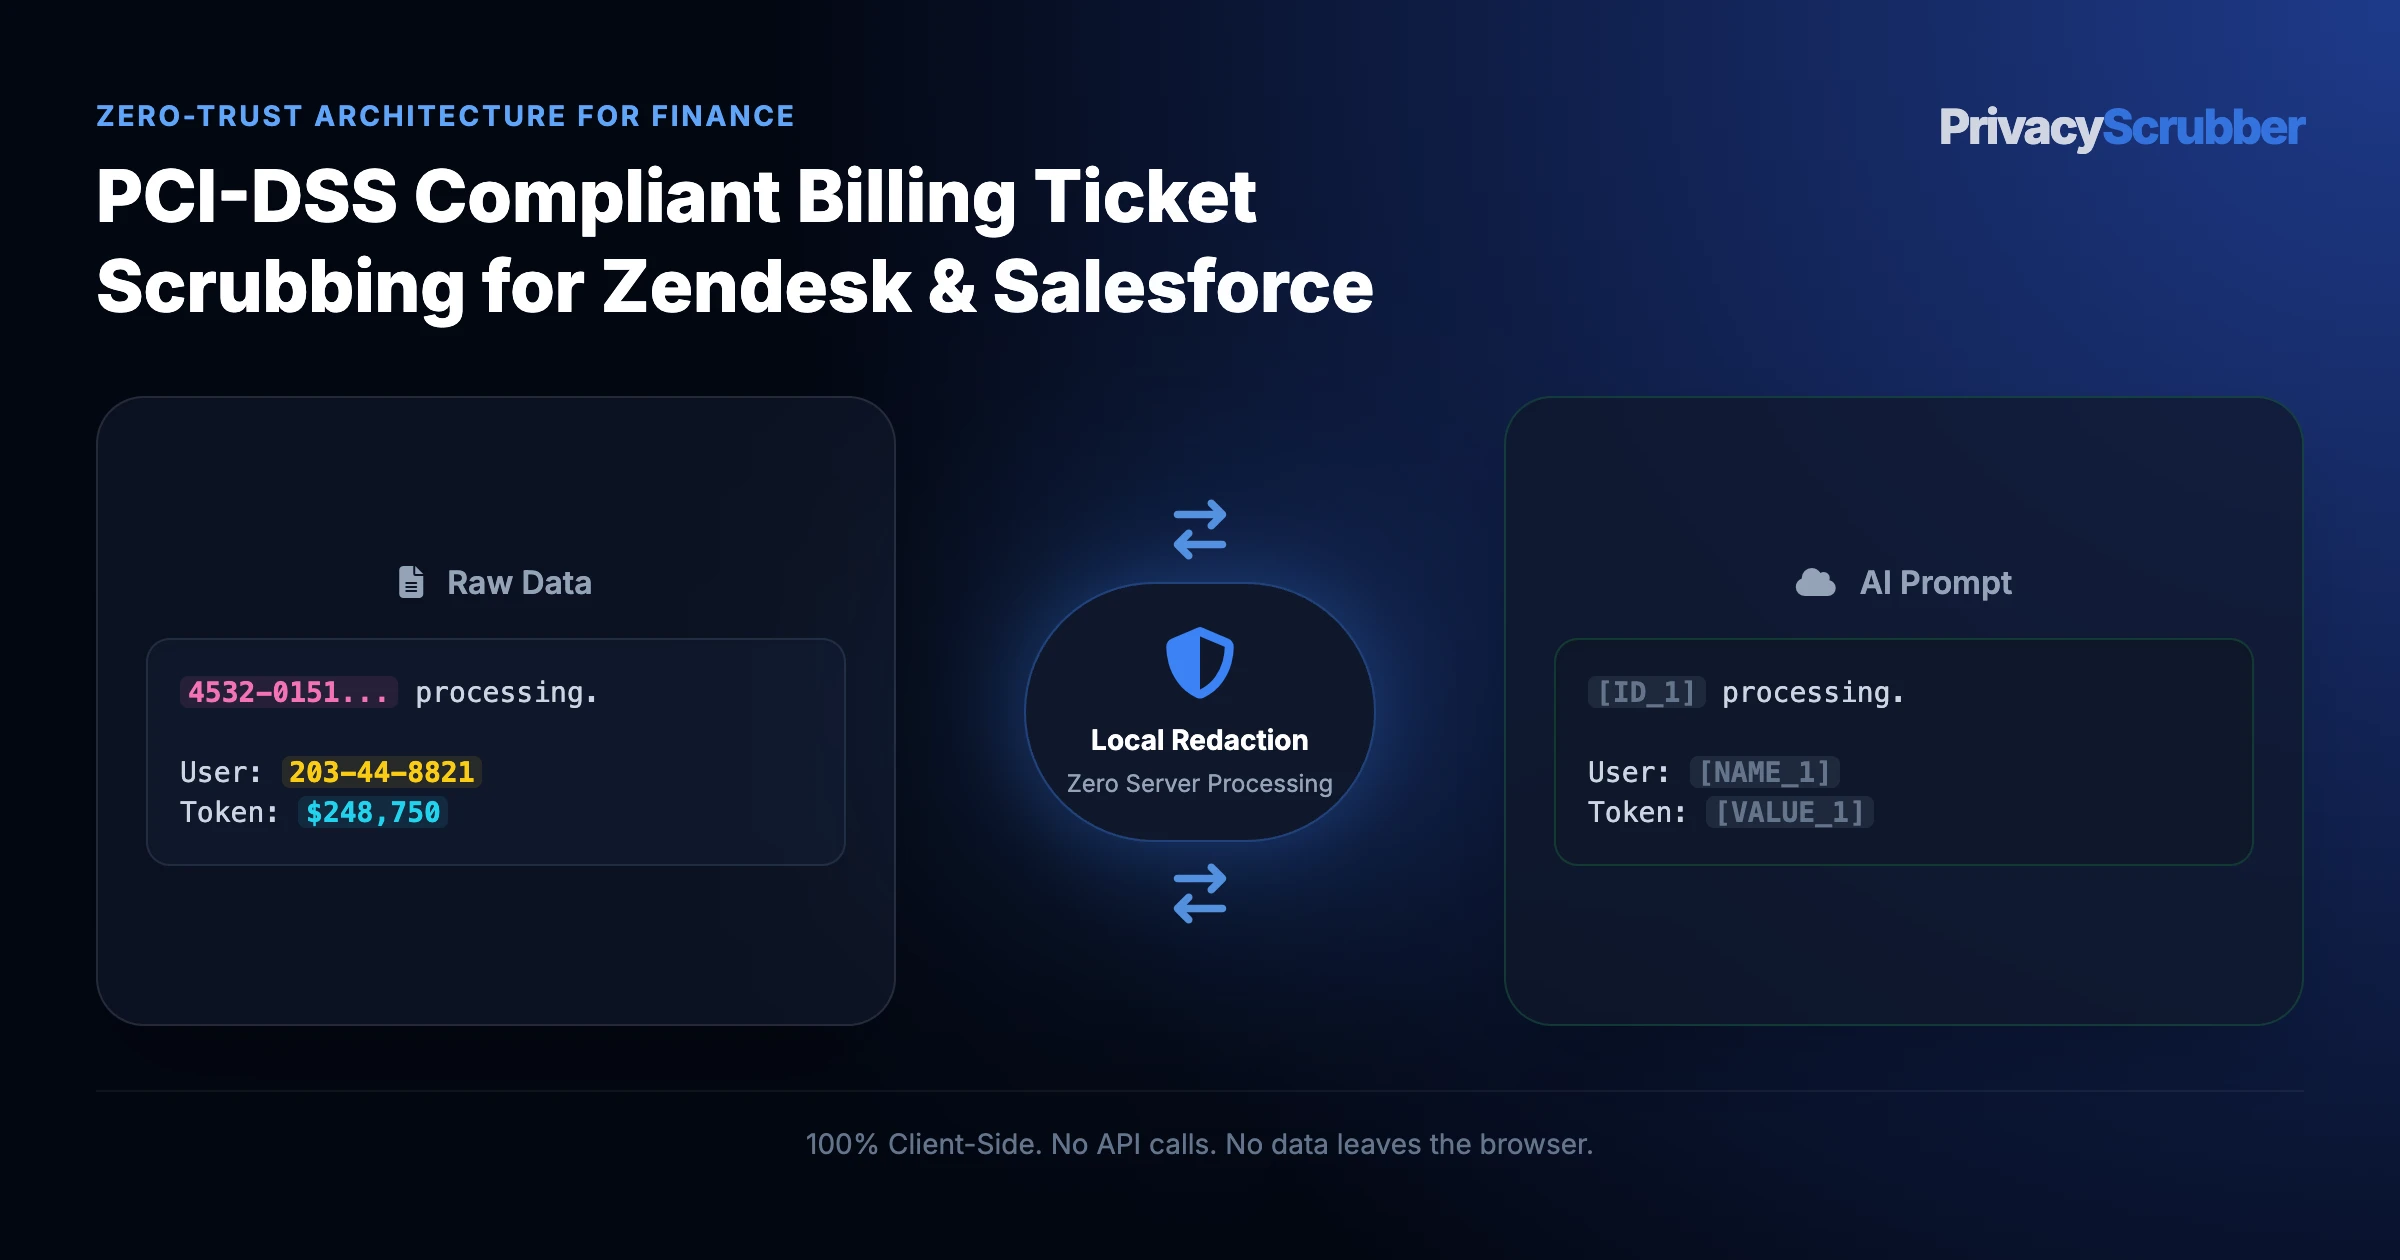
In production Financial Services workflows, pci dss ticket scrubbing and zendesk billing protection often fail because leaking GLBA Non-Public Personal Information (NPI), wire routing numbers, and account ledgers to cloud LLMs. PrivacyScrubber eliminates this egress vector by intercepting payloads inside volatile endpoint memory (PrivacyScrubber Finance Profile (Browser RAM & @privacyscrubber/sdk)), replacing regulated entities with bijective tokens ([ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1]) while keeping 0.00 bytes on external servers.
What Finance and Accounting Teams Send to AI During PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce
For financial advisors, accountants, loan officers, and fintech teams, PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce represents a high-leverage AI use case that is frequently blocked by sending client account numbers, portfolio balances, SSNs, and transaction histories to AI providers who may store or train on the data. By pairing ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools with PrivacyScrubber Finance Profile (Browser RAM & @privacyscrubber/sdk)—covered in our Financial Services AI privacy guides—organizations tokenize pci dss ticket scrubbing into [ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1] locally under SEC Regulation S-P.
In PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce, the gap between employee productivity and SEC Regulation S-P enforcement is driven by leaking GLBA Non-Public Personal Information (NPI), wire routing numbers, and account ledgers to cloud LLMs. Enforce automated consumer payment rights at the support boundary. Redact sensitive PII in local browser RAM with zero server egress or cloud leaks. Only local RAM sanitization of pci dss ticket scrubbing and zendesk billing protection eliminates sending client account numbers, portfolio balances, SSNs, and transaction histories to AI providers who may store or train on the data at the source.
How ZTDS™ Secures PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce Without Cloud Latency
Auditing PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce under SEC Regulation S-P requires provable technical controls rather than administrative policy memos alone. Because leaking GLBA Non-Public Personal Information (NPI), wire routing numbers, and account ledgers to cloud LLMs, unmasked pci dss ticket scrubbing inputs create immediate sub-processor exposure.
PrivacyScrubber deploys PrivacyScrubber Finance Profile (Browser RAM & @privacyscrubber/sdk) to tokenize zendesk billing protection and Salesforce Service Cloud PII into [ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1] locally in RAM. Each sanitization pass can be verified offline in Airplane Mode and documented with a tamper-evident SHA-256 compliance receipt.
What to Redact vs. Preserve in PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce
Under SEC Regulation S-P, financial advisors, accountants, loan officers, and fintech teams enforce this selective masking rule on PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce:
| Payload Element | Policy | ZTDS™ Token | Compliance & Reasoning Impact |
|---|---|---|---|
| Multi-Line Counterparty & Organization Names (Financial Services) | REDACT | [ACCOUNT_1] | Preserves co-reference continuity across multi-paragraph PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce prompts without leaking names. |
| Embedded Secrets, Tax IDs & Session Identifiers in PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce | REDACT | [ACCOUNT_1], [IBAN_1] | Intercepts high-liability literals before leaking GLBA Non-Public Personal Information (NPI), wire routing numbers, and account ledgers to cloud LLMs. |
| Secondary Regulated Attributes (billing ticket redaction) | REDACT | [TAX_ID_1] | Satisfies SEC Regulation S-P data minimization by replacing sensitive Financial Services strings in local RAM. |
| Anonymized Category Labels & Department Roles | PRESERVE | Cleartext (Financial Services Role) | Retains organizational context for PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce while keeping personal identities inside local RAM. |
| Non-Identifying Domain Logic & Operational Instructions | PRESERVE | Cleartext Narrative | Preserves 100% of analytical instructions for Salesforce Service Cloud PII so local detokenization yields production-ready output. |
| Regulatory Clause Citations & Policy Taxonomy (SEC Regulation S-P) | PRESERVE | Cleartext Citations | Allows the AI model to map PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce findings against statutory controls and audit frameworks. |
Copy-Paste Safe Instruction for PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce
Submit this prompt wrapper with your masked PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce input so the AI reasons over symbolic tokens without altering placeholder tags:
Objective: Process PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce (pci dss ticket scrubbing) with zero cloud data leakage.
All personal and corporate identifiers are represented by bijective tokens ([ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1]).

Steps:
1. Audit the quantitative and logical parameters of the PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce record.
2. Produce a concise executive summary tailored for financial advisors, accountants, loan officers, and fintech teams.
3. Maintain all [ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1] markers in-place for deterministic local RAM reveal.

[PASTE SANITIZED PAYLOAD HERE]
Objective: Process PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce (pci dss ticket scrubbing) with zero cloud data leakage.
All personal and corporate identifiers are represented by bijective tokens ([ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1]).

Steps:
1. Audit the quantitative and logical parameters of the PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce record.
2. Produce a concise executive summary tailored for financial advisors, accountants, loan officers, and fintech teams.
3. Maintain all [ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1] markers in-place for deterministic local RAM reveal.

[PASTE SANITIZED PAYLOAD HERE]
Statutory Liability for Finance and Accounting Teams: PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce
Meeting SEC Regulation S-P obligations (SEC Regulation S-P, FINRA Rule 4370, PCI-DSS, and banking secrecy laws) during PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce requires proving that raw pci dss ticket scrubbing and zendesk billing protection data never crosses into unauthorized cloud jurisdictions. Aligning with sanitize w-2 forms & paystubs for AI mortgage underwriting establishes a defensible zero-egress posture via PrivacyScrubber Finance Profile (Browser RAM & @privacyscrubber/sdk).
How to Sanitize PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce in Local RAM (Zero Cloud Egress)
Through PrivacyScrubber Finance Profile (Browser RAM & @privacyscrubber/sdk), PrivacyScrubber provides a zero-egress firewall for PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce. Before any pci dss ticket scrubbing or zendesk billing protection text reaches ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools, deterministic tokenization substitutes sensitive strings with [ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1] in volatile memory, fulfilling mask PII in clinical trial datasets with zero external server dependencies.
Our Airplane Mode Standard gives CISOs and DPOs deterministic proof for PCI-DSS Compliant Billing Ticket Scrubbing for Zendesk & Salesforce: sever network access, tokenize pci dss ticket scrubbing into [ACCOUNT_1], [IBAN_1], [CARD_1], [TAX_ID_1] in <1ms, and confirm zero outbound traffic in accordance with redact PII before using ChatGPT.
