FINRA Regulatory Notice 24-09 & SEC Rule 17a-4: Generative AI Compliance for Broker-Dealers
TEAMS EDITION
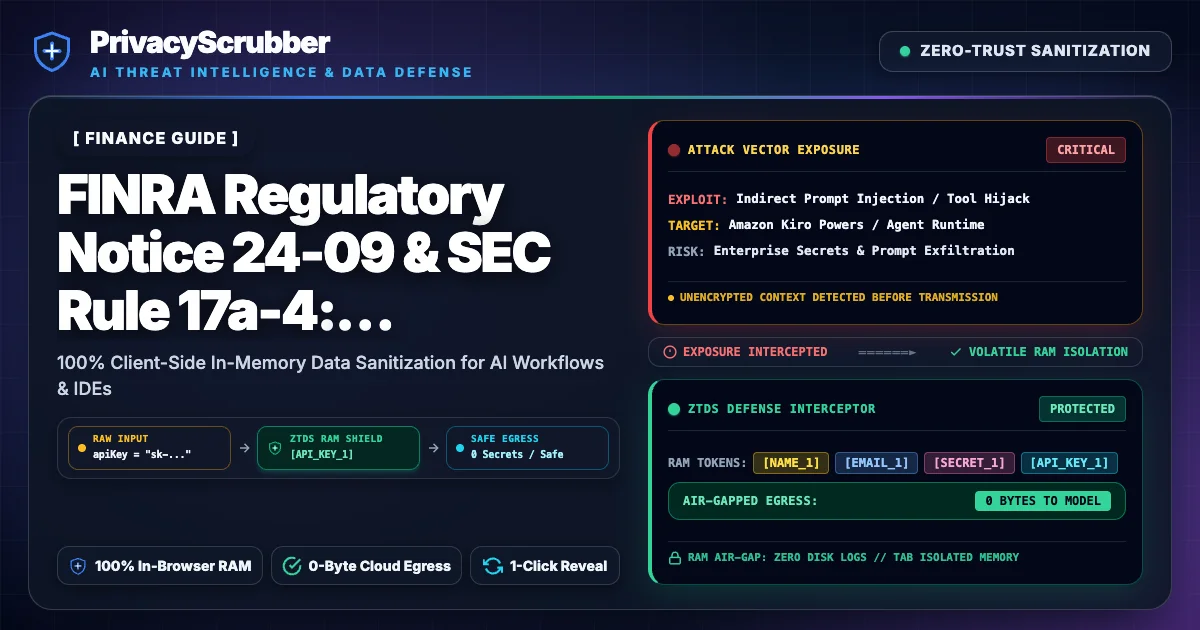
FINRA Regulatory Notice 24-09 & SEC Rule 17a-4: Comply with FINRA Notice 24-09 & SEC Rule 17a-4 when using ChatGPT. Redact MNPI, account numbers, and CUSIPs locally in browser RAM with zero cloud egress.
To comply with FINRA Regulatory Notice 24-09 and SEC Rule 17a-4 without triggering off-channel communication penalties or MNPI leaks, broker-dealers must tokenize customer account numbers, beneficial owner identities, specific CUSIP identifiers, and pending block order quantities in client-side RAM before submitting financial workpapers to ChatGPT or Claude. Macro market logic, asset allocation formulas, and security taxonomy remain in cleartext with zero network egress.
AI Summary / Key Takeaways
Verified Zero-Trust Logic
"PrivacyScrubber provides the essential de-identification layer for Finance professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Finance data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
FINRA Regulatory Notice 24-09 reminds member firms of their supervisory obligations when deploying Generative AI and Large Language Models. Under FINRA Rule 3110 (Supervision), broker-dealers must establish and maintain written supervisory procedures (WSPs) governing all AI tools utilized by associated persons. Concurrently, SEC Exchange Act Rules 17a-3 and 17a-4 mandate strict electronic books-and-records retention—enforced by over $2.8 billion in regulatory penalties for unapproved 'off-channel communications'. Submitting client account numbers, trading orders, or Material Non-Public Information (MNPI) into public or enterprise cloud LLMs breaches WORM recordkeeping mandates and triggers investigations under Section 15(g) of the Exchange Act. PrivacyScrubber's Zero-Trust Data Sanitization (ZTDS) operates 100% locally within workstation browser RAM, stripping customer NPI, brokerage account numbers, and restricted CUSIPs prior to prompting, guaranteeing that zero client or transaction data is leaked to external cloud AI infrastructure.
Zero-Trust Data Protection: Failing to mask client financial data before sending it to ChatGPT can trigger severe GLBA and SEC penalties. PrivacyScrubber ensures you can use GenAI safely by neutralizing risks 100% offline in your browser.
What Finance and Accounting Teams Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
Aligning corporate data policy with FINRA Regulatory Notice 24-09 & SEC Rule 17a-4 requires strict input validation. As enterprises deploy platforms like ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools, preventing unmanaged information egress to public model training queues becomes a top priority. Our finance AI privacy guides maps out a clear path to maintain the finance safety envelope. The primary concern is preventing sending client account numbers, portfolio balances, SSNs, and transaction histories to AI providers who may store or train on the data across all endpoints.
Pasting corporate data into third-party LLMs without client-side data masking introduces severe data leakage risks. Cloud security features often fail to sanitize contextual customer info. For financial advisors, accountants, loan officers, and fintech teams, the core exposure occurs at the prompt entry point. Comply with FINRA Notice 24-09 & SEC Rule 17a-4 when using ChatGPT. Redact MNPI, account numbers, and CUSIPs locally in browser RAM with zero cloud egress.
Privacy Insight: FINRA Regulatory Notice 24-09 reminds member firms of their supervisory obligations when deploying Generative AI and Large Language Models. Under FINRA Rule 3110 (Supervision), broker-dealers must establish and maintain written supervisory procedures (WSPs) governing all AI tools utilized by associated persons. Concurrently, SEC Exchange Act Rules 17a-3 and 17a-4 mandate strict electronic books-and-records retention—enforced by over $2.8 billion in regulatory penalties for unapproved 'off-channel communications'. Submitting client account numbers, trading orders, or Material Non-Public Information (MNPI) into public or enterprise cloud LLMs breaches WORM recordkeeping mandates and triggers investigations under Section 15(g) of the Exchange Act. PrivacyScrubber's Zero-Trust Data Sanitization (ZTDS) operates 100% locally within workstation browser RAM, stripping customer NPI, brokerage account numbers, and restricted CUSIPs prior to prompting, guaranteeing that zero client or transaction data is leaked to external cloud AI infrastructure.
Enterprise Finance Data Redaction
Auditing transaction ledgers or sanitizing bank records? Avoid the predatory 'per-seat' pricing models of legacy DLP systems. PrivacyScrubber TEAMS costs a flat $99/month for unlimited employees, supporting offline OCR document scrubbing and local re-hydration of tokenized bank statements.
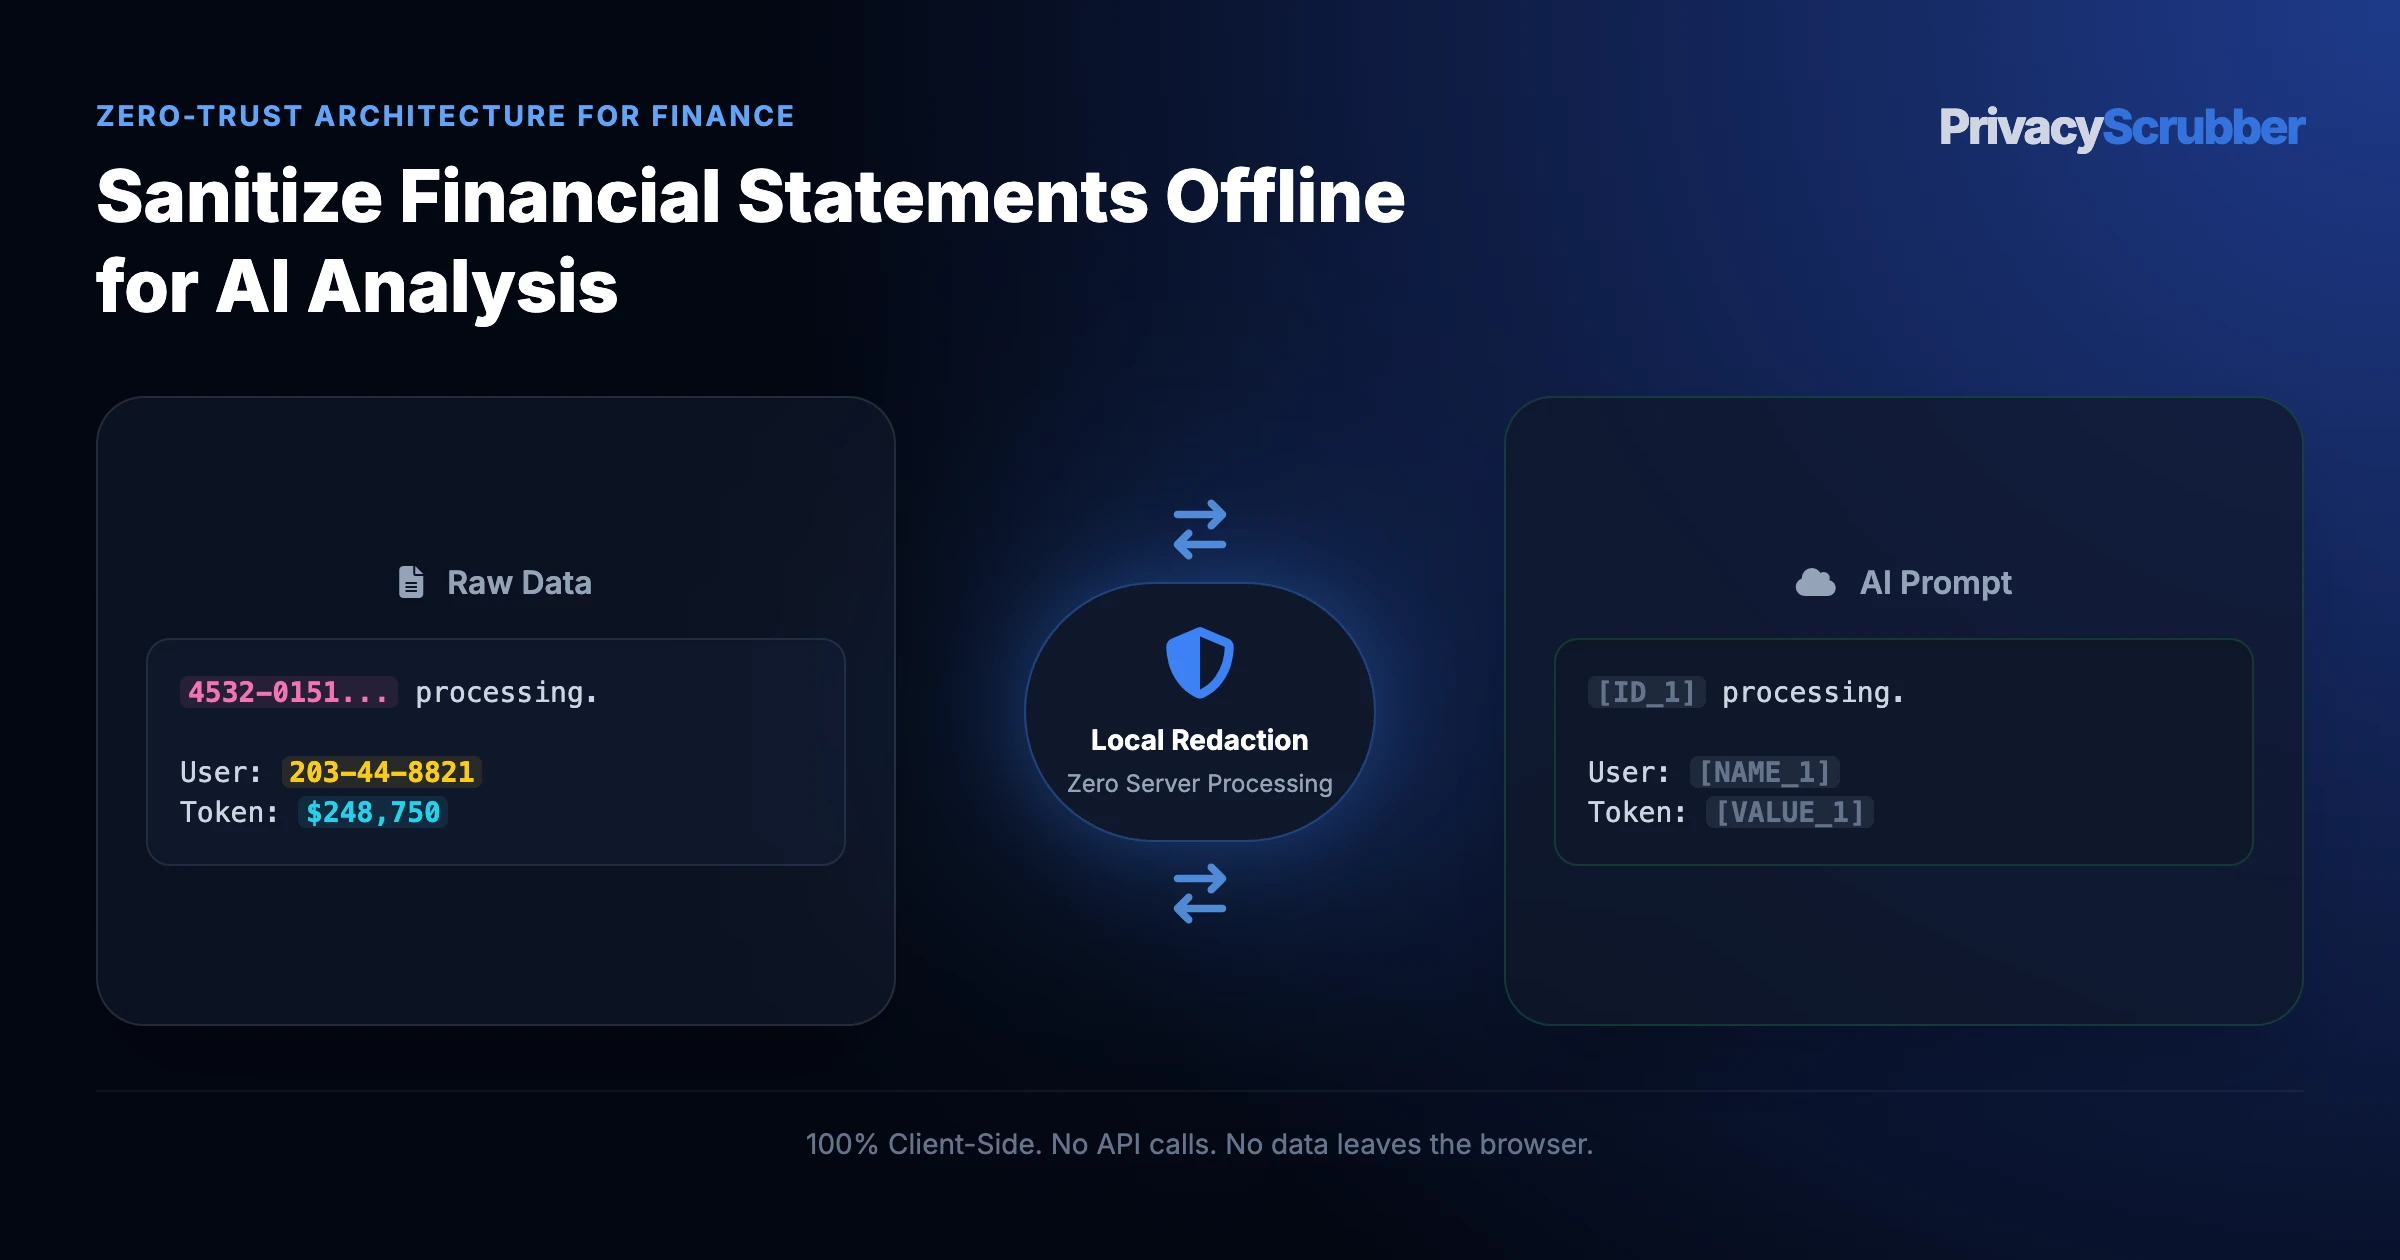
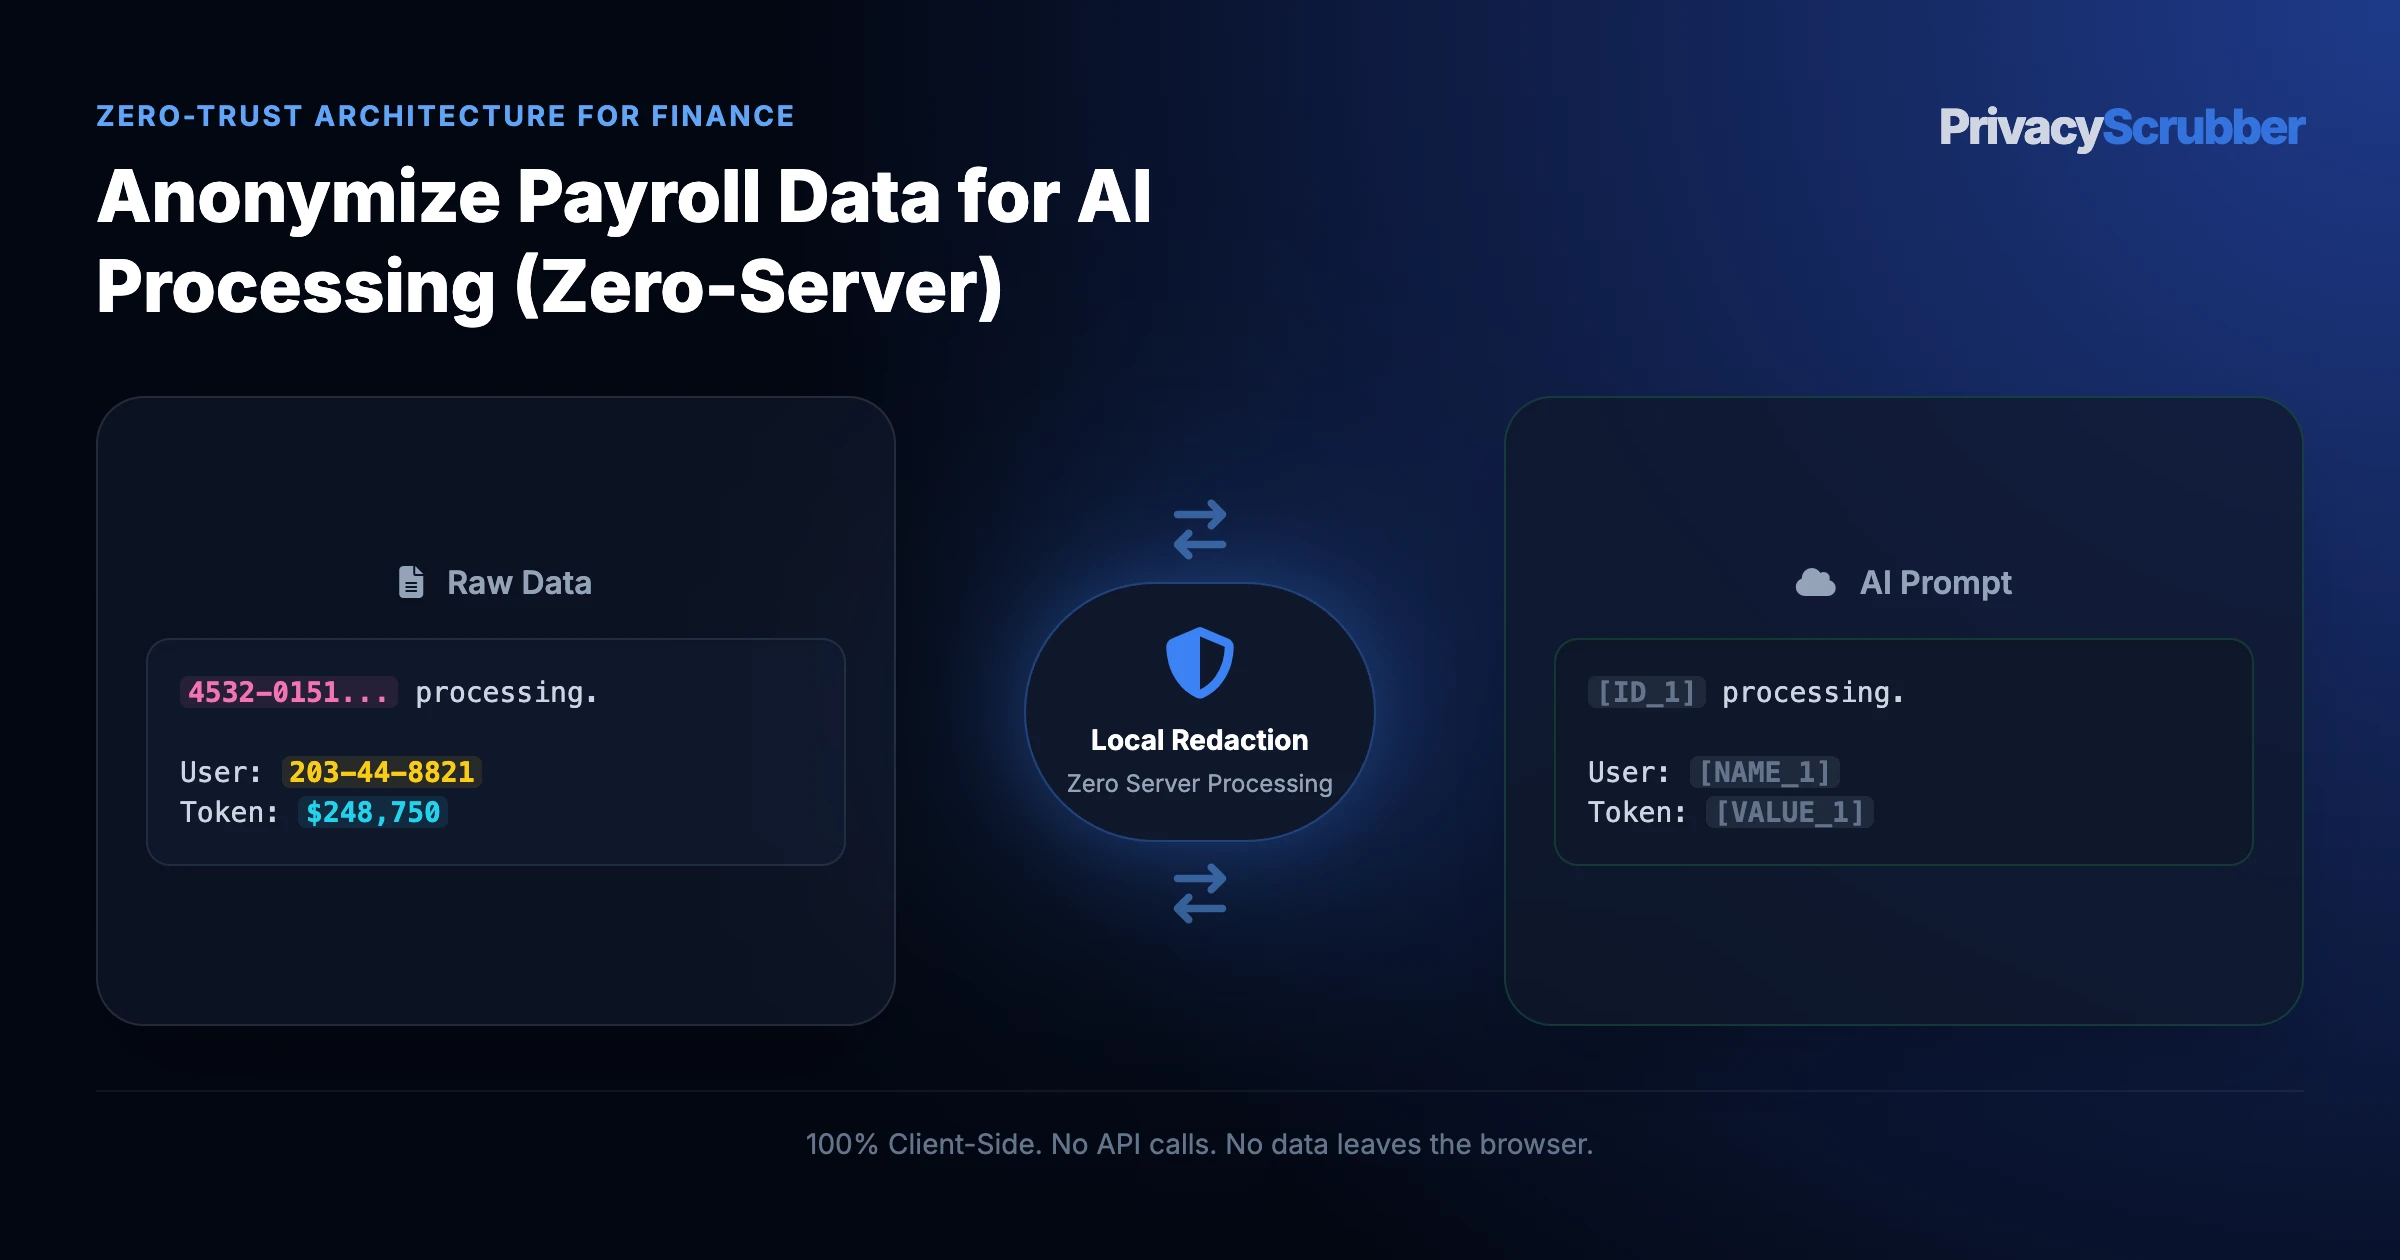
The technical safeguard for confidential AI prompts relies on intercepting sensitive strings before they cross the local network interface. By replacing actual values with deterministic placeholders (e.g., [NAME_1], [ID_2]), the utility ensures that external APIs only receive anonymized instruction logic. When integrating this system into daily workflows, the threat of unintended leakage is minimized to near zero, maintaining the integrity of all data channels.
Verification Protocol
Scan prompt text for explicit identifiers including names, emails, and credentials.
Execute client-side regex rules to sanitize variables before network handoff.
Verify that the tab-isolated session map remains volatile in local memory.
Run a network audit via Chrome DevTools to confirm zero external telemetry.
FINRA Notice 24-09 & SEC Books and Records Mandates
Financial Industry Regulatory Authority (FINRA) Regulatory Notice 24-09 establishes that member firms cannot bypass core regulatory duties when deploying Generative AI and Large Language Models. Broker-dealers and registered representatives face strict supervision obligations under FINRA Rule 3110, public communications standards under Rule 2210, and mandatory electronic recordkeeping under SEC Exchange Act Rule 17a-4 and FINRA Rule 4511. Entering confidential client trade flows, account numbers, or Material Non-Public Information (MNPI) into public or multi-tenant cloud AI systems exposes broker-dealers to massive regulatory enforcement actions, disgorgement orders, and individual supervisory sanctions.
The matrix below highlights how PrivacyScrubber protects institutional research workpapers through our Financial Services AI Scrubber engine:
Broker-Dealer Field
Raw Trading Desk & Workpaper Entry
PrivacyScrubber Local Token
Supervisory & AI Utility
Customer Brokerage Account Number
Pershing Clearing Acct #849-291048-01
Pershing Clearing Acct #[ACCT_1]
Eliminates SEC Reg S-P customer NPI breach
Material Non-Public Information (MNPI)
Pending Block Order: 45,000 Convertible Notes
Pending Block Order: [BLOCK_ORDER_1] Notes
Prevents front-running & Section 15(g) leaks
Restricted Private Debt Placement CUSIP
Private Issuer CUSIP: 65342T-AA-9
Private Issuer CUSIP: [CUSIP_1]
Shields confidential syndication identifiers
Registered Principal & Rep Registration
Principal CRD #4928104 | Rep CRD #6184902
Principal CRD #[CRD_1] | Rep CRD #[CRD_2]
Protects associated person professional identities
Public Market Tickers & Conversion Terms
Conversion Price: $18.50/share (42.5% Premium)
Conversion Price: $18.50/share (42.5% Premium)
Preserved 100% Cleartext for Valuation Modeling
Supervisory Rules & Statutory Citations
FINRA Rule 3110, Rule 2210, SEC Rule 17a-4
FINRA Rule 3110, Rule 2210, SEC Rule 17a-4
Preserved 100% Cleartext for Compliance Memos
Institutional Research Pipeline with @privacyscrubber/sdk
Capital markets desks, quantitative trading teams, and institutional broker-dealers embed zero-egress sanitization into algorithmic research pipelines and client portals:
Node.js: Institutional Trade Workpaper Sanitizernpm i @privacyscrubber/sdk
import { PrivacyScrubberEngine } from '@privacyscrubber/sdk';

const engine = new PrivacyScrubberEngine({
  profile: 'Finance & Banking',
  detectSecrets: true
});

const institutionalWorkpaper = `CONFIDENTIAL SYNDICATE TRADE ALLOCATION:
Broker-Dealer: Apex Horizon Capital Markets (CRD #184912 / SEC #8-69104).
Client: Sovereign Meridian Global Macro Fund (DTC #0248, Acct #849-291048-01).
Restricted Note CUSIP: 65342T-AA-9 (Pre-IPO Convertible Senior Notes).
Pending Allocation: 45,000 Notes @ $1,000 Par Value ($45,000,000 Total Allocation).
Supervising Principal: Marcus Vance, Series 24 (CRD #4928104).`;

const { sanitizedText, tokenMap } = engine.sanitize(institutionalWorkpaper);
console.log('Sanitized Trade Payload for AI Covenant Review:\n', sanitizedText);

// Rehydrate generated Series 24 supervisory memo in client RAM
const rawAiReview = 'Supervisory memo: [ORG_1] allocation of [BLOCK_ORDER_1] Notes for [ORG_2] complies with FINRA Rule 3110.';
const finalSupervisoryMemo = engine.restore(rawAiReview, tokenMap);
Cross-Regulatory Governance & Off-Channel Communication Defense
Broker-dealer compliance directors coordinate local sanitization in conjunction with FinCEN SAR & KYC Narrative AI Redaction to protect anti-money laundering workflows. Financial institutions managing tax-sensitive trading accounts integrate IRC § 7216 Tax Preparer AI Compliance. Multi-branch brokerages enforce enterprise-wide WSPs and team-based zero-trust handoffs through Centralized AI Governance dashboards, ensuring complete immunity against SEC off-channel communication violations.
Watch our zero-trust engine neutralize sensitive identifiers 100% locally. No data ever leaves your device.
Local processing 0 Server logs
ZTDS_ENGINE_V1.5.0
PROMPT INPUT > Draft a reply for customer inquiry. Sender is Alice Johnson, email: alice.j@organization.org, mobile: 555-0177.
PROMPT INPUT > Draft a reply for customer inquiry. Sender is [NAME_1], email: [EMAIL_1], mobile: [PHONE_1].
Finance Detection Profile
Our zero-trust engine is pre-hardened for Finance workflows, automatically identifying and tokenizing the following parameters 100% locally.
BORROWER_NAME
Active Protection
SSN
Active Protection
EMPLOYER_NAME
Active Protection
FEIN
Active Protection
ACCOUNT_NUMBER
Active Protection
ROUTING_NUMBER
Active Protection
ADDRESS
Active Protection
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with financial SOC 2 compliance.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
Compliance Decision Matrix
Field-by-Field Sanitization Rule for Broker-Dealer Trade Allocation Sheet & Supervisory Research Workpaper (FINRA Notice 24-09 / SEC 17a-4)
To maintain LLM analytical context while avoiding cloud data breaches, follow this deterministic mapping before submitting prompts to third-party AI models:
Substantive quantitative metrics necessary for portfolio rebalancing without revealing customer identity
1-Click Persona Prompt
Safe LLM Prompt Template for Broker-Dealer Trade Allocation Sheet & Supervisory Research Workpaper (FINRA Notice 24-09 / SEC 17a-4)
Copy and paste this structured prompt into ChatGPT, Claude, or Gemini alongside your tokenized text to prevent LLM rejection:
You are a Senior Broker-Dealer Compliance Principal and Chief Regulatory Officer specializing in FINRA Rule 3110 supervision and SEC Rule 17a-4 recordkeeping. Review this sanitized institutional allocation memorandum where firm names, registered representative CRDs, clearing account numbers, beneficial owner identities, and specific private debt CUSIPs are tokenized ([ORG_1], [NAME_1], [CRD_1], [ACCT_1], [CUSIP_1]).

Tasks:
1. Evaluate the supervisory review controls required under FINRA Regulatory Notice 24-09 for Generative AI ingestion of trade documentation.
2. Outline the mandatory WORM-compliant archiving protocol under SEC Exchange Act Rule 17a-4(f) for AI-generated supervisory research memos.
3. Formulate written supervisory procedures (WSPs) to prevent the transmission of Material Non-Public Information (MNPI) to cloud model providers under Exchange Act Section 15(g).

[PASTE SANITIZED TEXT HERE]
Why Financial Controllers and Audit Leads Flag Unmasked AI Prompts
The security standards are clear: SEC Regulation S-P, FINRA Rule 4370, PCI-DSS, and banking secrecy laws. Yet, daily employee workflows demand high-speed summarization. Addressing this gap requires checking the patterns in prevent iban, bank account & financial statement network leakage to understand how unredacted logs translate into liability. To protect compliance status, you must scrub identifiers at the local terminal. Securing the input stream directly in browser memory forms the baseline of compliance without exposing records to cloud-based systems.
Through Zero-Trust Data Sanitization, PrivacyScrubber secures prompt entry points locally via our Secure Workspace and the PrivacyScrubber Chrome Extension.
How to Use AI on Real Finance Data — Without Sending a Single Real Name
Through Zero-Trust Data Sanitization, PrivacyScrubber secures prompt entry points locally via our Secure Workspace and the PrivacyScrubber Chrome Extension. The system tokenizes customer and business identifiers (such as [ID_1]) before exfiltration, aligning with standard procedures for centralized AI governance. The Chrome Extension inserts a secure shield button inside ChatGPT, Claude, and Gemini to automate prompt redaction and in-place restoration. By executing deterministic AST lookaround parsing entirely in local memory, PrivacyScrubber preserves the usefulness of ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools for production workflows without introducing external risk.
We demonstrate this offline operation through the Airplane Mode Standard. Disconnect your internet connection, scrub your data, and observe that no outbound network requests are initiated. This meets the conditions of financial SOC 2 compliance, validating that all client information remains on your local terminal.
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT (OpenAI):
Underwriting & Loan Income Analysis (Wage-Preserving DTI Calculation)PrivacyScrubber ZTDS Protocol
Act as a senior mortgage underwriter and compliance officer. Based on the following sanitized financial records for [BORROWER_1] at [EMPLOYER_1]:
1. Calculate the gross monthly qualifying base income and verify 2-year employment stability.
2. Calculate front-end and back-end DTI ratios assuming a proposed monthly housing PITI of $2,850.00.
3. Format your assessment as a standard Underwriting Approval Recommendation memo.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Maintain all cryptographic token placeholders ([BORROWER_1], [EMPLOYER_1], [FEIN_1], [SSN_1], [ACCOUNT_1]) strictly unchanged in your final response for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT (OpenAI) outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: Gramm-Leach-Bliley Act (GLBA Safeguards Rule 16 CFR Part 314) & CFPBNon-Public Personal Information (NPI) is tokenized in volatile browser RAM. Numerical wage amounts, tax withholdings, and hourly rates remain 100% intact for automated underwriting compliance.
Finance Adoption Use Cases
Chief Risk OfficerGLBA & FINRA
Zero-Trust Verified
Masks account numbers, SSNs, and credit reports locally, ensuring financial analysts stay fully compliant with SEC and FINRA AI governance mandates.
Head of Private Wealth OperationsWEALTH MANAGEMENT
Zero-Trust Verified
Enables wealth managers to draft personalized portfolio reports without exposing High-Net-Worth client balances or tax IDs to cloud AI.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Finance compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any finance text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Finance Teams.
What supervisory controls does FINRA Regulatory Notice 24-09 require for Generative AI?
Notice 24-09 emphasizes that member firms cannot delegate supervisory responsibilities to AI algorithms. Under FINRA Rule 3110 and Rule 2210, broker-dealers must verify the accuracy of AI outputs, prevent hallucinated financial advice, implement technical controls blocking the input of confidential customer information, and ensure all AI-assisted communications with the public are reviewed and approved by a registered principal (Series 24).
How does pasting trade data into ChatGPT violate SEC Rule 17a-4 books-and-records rules?
SEC Rule 17a-4 requires broker-dealers to preserve all business communications in an easily accessible place for at least three years, the first two years in an easily accessible place, with write-once-read-many (WORM) compliant audit trails. Commercial cloud LLM chat interfaces (ChatGPT, Claude, Gemini) store ephemeral, unarchived chat transcripts on third-party vendor servers outside the firm's approved compliance archive, creating an unmonitored 'off-channel communication' channel subject to severe SEC enforcement action.
What constitutes Material Non-Public Information (MNPI) in AI financial modeling?
Under Section 15(g) of the Securities Exchange Act of 1934, broker-dealers must maintain written policies reasonably designed to prevent the misuse of MNPI. Inputting pending institutional block order sizes, confidential M&A restructuring terms, pre-IPO private debt covenants, or advance earnings metrics into cloud AI platforms constitutes an unlawful transmission of non-public market-moving information to third-party infrastructure.
How does PrivacyScrubber enable broker-dealers to use LLMs safely without violating SEC or FINRA rules?
PrivacyScrubber executes entirely in local device RAM with zero network egress (Airplane Mode verified). Customer identities, DTC participant IDs, brokerage account numbers, and restricted security CUSIPs are converted into abstract cryptographic surrogates (e.g., [NAME_1], [ACCT_1], [CUSIP_1]) on the analyst's machine. The LLM processes the sanitized financial logic and bond covenants without ever seeing sensitive data. The analyst rehydrates the original terms locally, keeping the firm 100% compliant with SEC 17a-4 and FINRA 24-09.
Does protecting data with PrivacyScrubber before AI processing satisfy SEC Regulation S-P?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with SEC Regulation S-P because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for finance workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match finance-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask finance data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your finance data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Scrub in RAM" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard deterministic AST lookaround engine to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
How can banks safely use Generative AI?
Banks must prevent NPI (Non-Public Personal Information) from reaching external LLMs. Client-side scrubbing tools intercept account numbers, SSNs, and financial data at the cursor level. Ensure firm-wide compliance with our $99/mo TEAMS plan.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
Why Financial Controllers and Audit Leads Flag Unmasked AI Prompts
The security standards are clear: SEC Regulation S-P, FINRA Rule 4370, PCI-DSS, and banking secrecy laws. Yet, daily employee workflows demand high-speed summarization. Addressing this gap requires checking the patterns in prevent iban, bank account & financial statement network leakage to understand how unredacted logs translate into liability. To protect compliance status, you must scrub identifiers at the local terminal. Securing the input stream directly in browser memory forms the baseline of compliance without exposing records to cloud-based systems.
How to Use AI on Real Finance Data — Without Sending a Single Real Name
Through Zero-Trust Data Sanitization, PrivacyScrubber secures prompt entry points locally via our Secure Workspace and the PrivacyScrubber Chrome Extension. The system tokenizes customer and business identifiers (such as [ID_1]) before exfiltration, aligning with standard procedures for centralized AI governance. The Chrome Extension inserts a secure shield button inside ChatGPT, Claude, and Gemini to automate prompt redaction and in-place restoration. By executing deterministic AST lookaround parsing entirely in local memory, PrivacyScrubber preserves the usefulness of ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools for production workflows without introducing external risk.
Is PrivacyScrubber safe for finra notice 24-09 chatgpt, sec rule 17a-4 generative ai, broker dealer ai compliance, redact mnpi chatgpt, finra rule 3110 ai supervision, sec off channel communications ai?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with finra notice 24-09 chatgpt, sec rule 17a-4 generative ai, broker dealer ai compliance, redact mnpi chatgpt, finra rule 3110 ai supervision, sec off channel communications ai, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for finance?
Our engine includes 30 specialized industry profiles optimized for finance data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.
Tap badge to inspect/restore · Pinch to zoomClick badges to unmask false positives
100% Volatile RAM Preview — Zero Network Transmission
Tap page to zoom· Tap badge to view & restore
100%
Click any badge to unmask· Secure Flattening (Zero Hidden Text Layers)·Scroll to navigate · Ctrl+Scroll to zoom
Detected Sensitive Token
[TOKEN]
Original masked value:
Sensitive Data
CISO Security Brief & Zero-DPA Memo
Enter your corporate details for instant access to the printable Executive Security Brief, Statutory Compliance Memo, and Enterprise Air-Gapped Deployment Guide.
Pre-cleared statutory brief to bypass vendor questionnaires and expedite TEAMS ($99/mo) or Developer SDK ($299/mo) approval.
Select Procurement Track:
ZTDS™ VERIFIED0-Byte Egress · No DPA · Patent Pending (IL 331905 · WIPO: B17B) · 2-Page Audit Brief
Manual Activation
Unlock your features
Invalid or expired license key
License Activated
Your features are unlocked.
Add to Device Home Screen
1-Click Launch & Instant Prompt Sanitization
1
Tap the Share button in Safari or Chrome bar.
2
Scroll down and select Add to Home Screen.
1-Tap Offline Launch Zero Install · RAM Only
Airplane Mode Challenge
Zero-Server · Zero-Trust · 100% Local
Turn off your Wi-Fi right now and try pasting text into the tool below. It processes 100% in your local RAM without sending any network requests.
Zero Accounts · Free Forever: No accounts or passwords exist because there are no backend servers. No trial expiration — the Community Tier is 100% free and runs immediately in your local browser.