
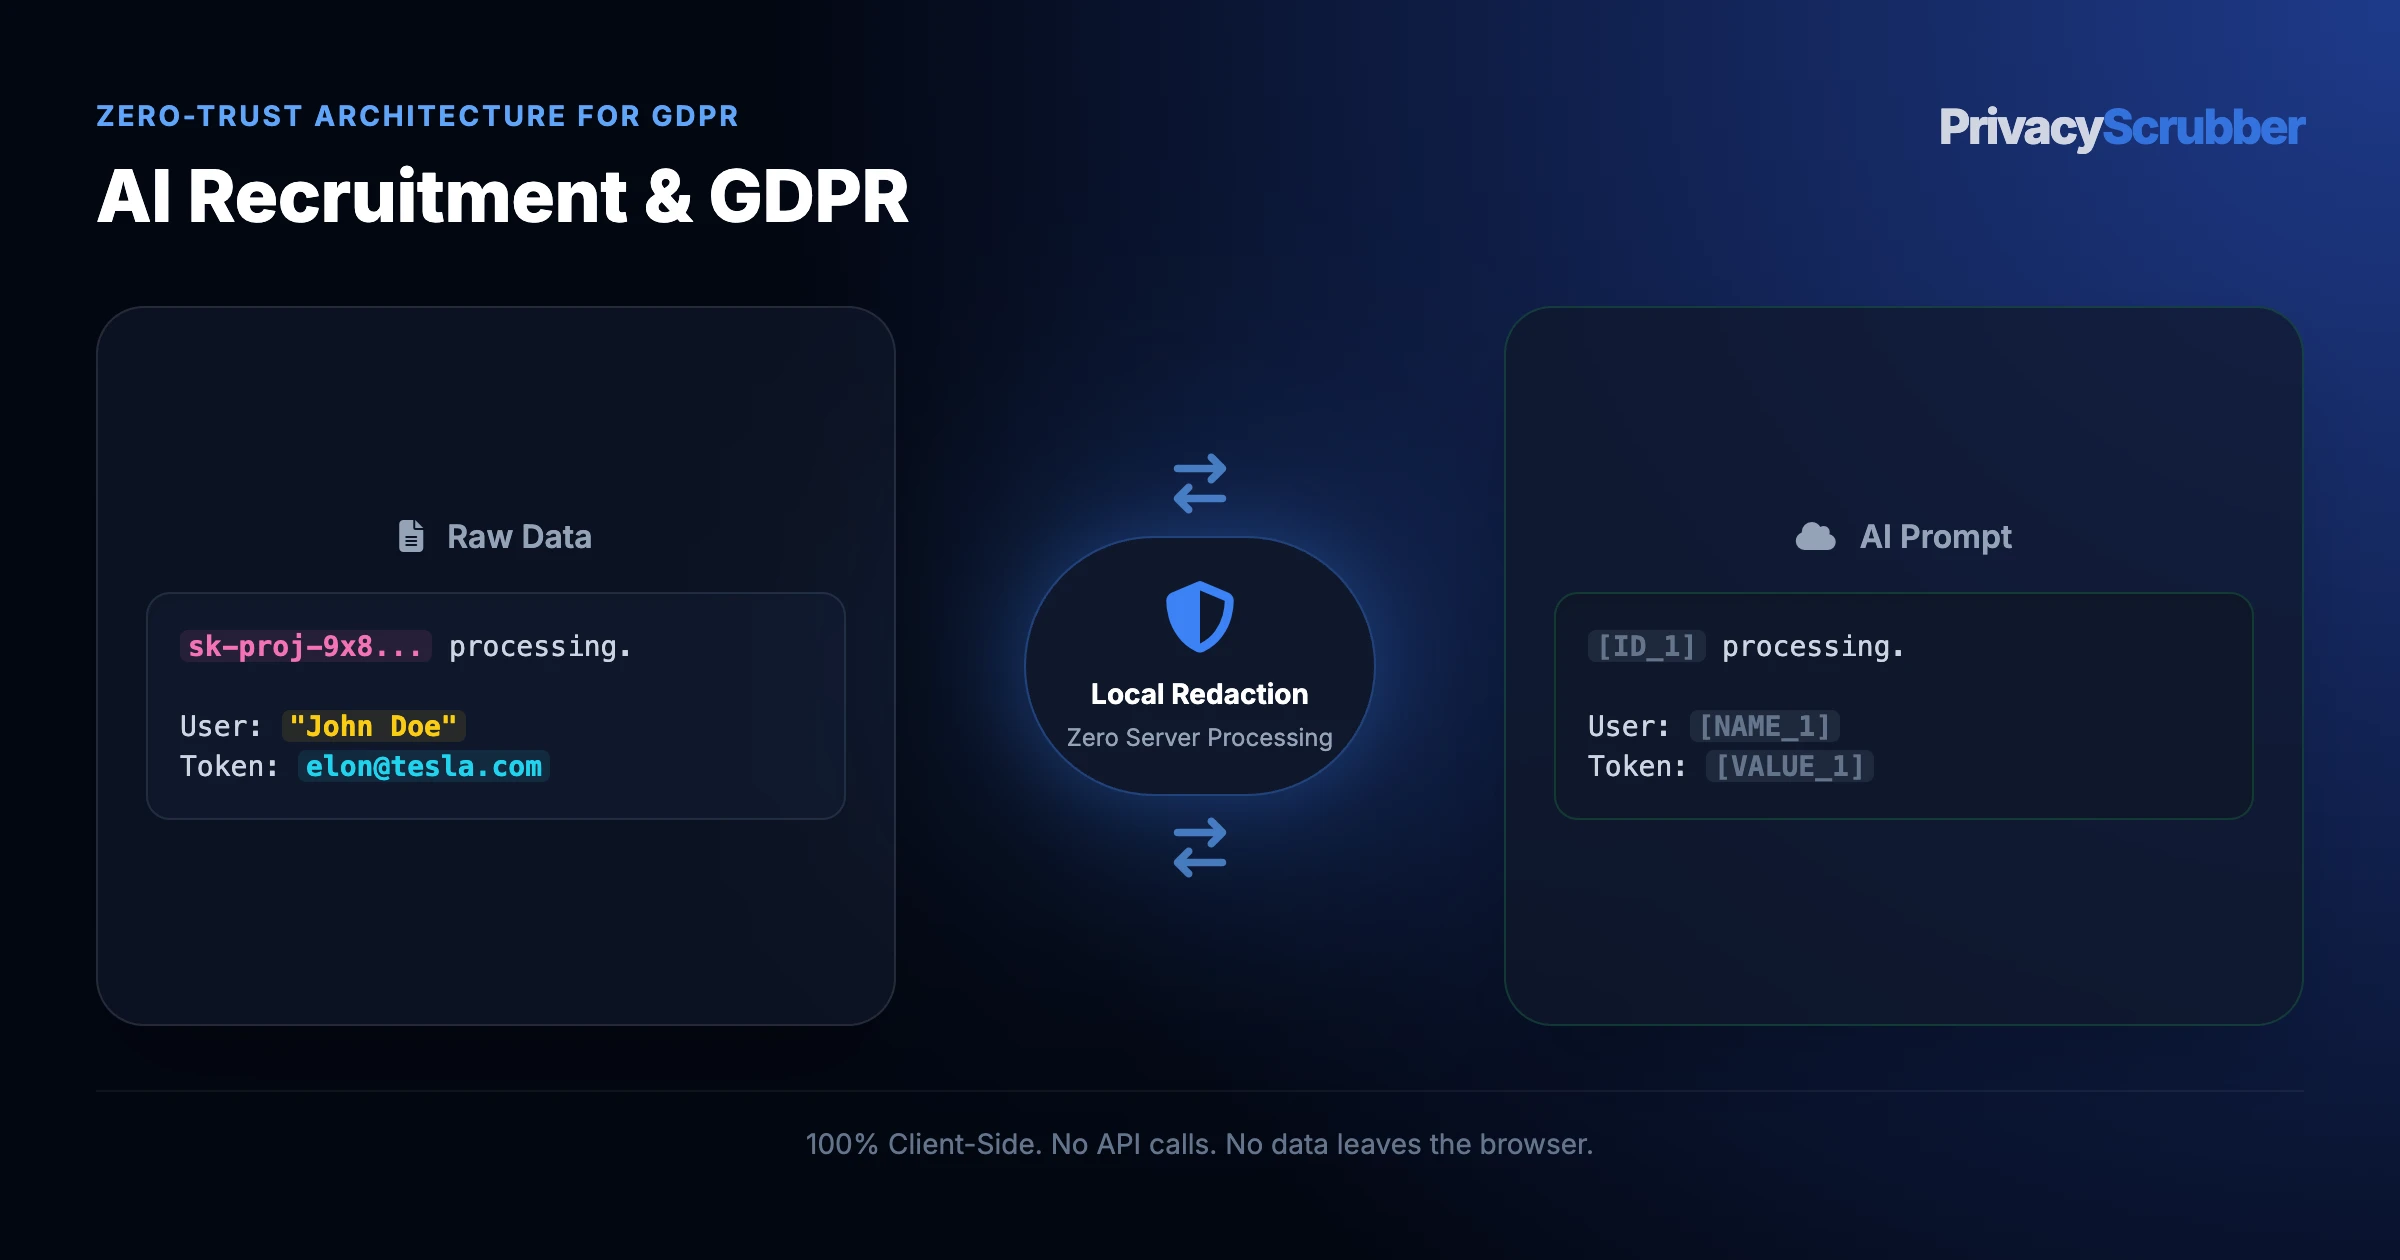
Every raw AI Recruitment & GDPR query into ChatGPT expands 5(1)(c)) audit exposure. Tokenizing GDPR AI recruitment and hiring privacy compliance via offline endpoint scrubber isolates identifiers as [NAME_1].
Remove candidate identity before AI screening
Hiring is a high-risk use of AI under the EU AI Act (Annex III) and handles personal data under GDPR. Replace names, contact details and ID numbers with tokens locally before screening, and restore them only on your side.
Paste a CV in the sandbox above and copy the masked version.
Launch local scrubberRecruiters mask inside ChatGPT or Claude with one click.
Install free extensionRun local MCP sanitization on AI Recruitment & GDPR payloads without API keys.
{
  "mcpServers": {
    "privacyscrubber": {
      "command": "npx",
      "args": ["-y", "@privacyscrubber/mcp-server"]
    }
  }
}npm install @privacyscrubber/sdk
import { sanitize, restore } from '@privacyscrubber/sdk';

// Anonymize CVs before a screening model
const { scrubbedText, tokenMap } = sanitize(resumeText);
const aiAnswer = await callYourModel(scrubbedText);   // only tokens leave your process
const { restoredText } = restore(aiAnswer, tokenMap); // originals restored in local RAMAI Recruitment & GDPR: What Privacy and DPO Teams Expose to Cloud AI
Intercepting GDPR AI recruitment inside AI Recruitment & GDPR protects European business owners from unmasked GDPR AI recruitment exposure. Across GDPR AI privacy guides, offline endpoint scrubber confines hiring privacy compliance strictly to volatile RAM.
Why do network gateways miss AI Recruitment & GDPR? Hiring AI is high-risk under the EU AI Act and handles personal data under GDPR. Mask candidate identity locally before screening. TEAMS flat rate. Encrypted browser prompts carrying GDPR AI recruitment trigger Art. 44 transfer & training exposure beyond proxy inspection.
Why European business owners Isolate AI Recruitment & GDPR Locally
Hiring AI is high-risk under the EU AI Act and handles personal data under GDPR. Mask candidate identity locally before screening. TEAMS flat rate. Without local pre-scrubbing via offline endpoint scrubber, European business owners handle GDPR AI recruitment payloads that leak straight into ChatGPT queues.
Because [NATIONAL_ID_1] placeholders remain strictly ephemeral, European business owners can safely evaluate candidate data protection inside ChatGPT and wipe all state instantly upon completion.
Field-by-Field Sanitization Rule for AI Recruitment & GDPR
Follow this bijective sanitization schedule for AI Recruitment & GDPR so downstream AI completions can be detokenized locally in one click:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Subject Identifiers (GDPR AI recruitment) | REDACT | [NAME_1] | 5(1)(c)) guard prevents ChatGPT from retaining personal AI Recruitment & GDPR records. |
| Regulated Strings (zero-egress AI) | REDACT | [EMAIL_1] | Applies 5(1)(c)) minimization locally before AI Recruitment & GDPR leaves RAM. |
| Tax, Token & Session Strings (hiring privacy compliance) | REDACT | [IBAN_1] | Zero-egress tokenization keeps AI Recruitment & GDPR identifiers off vendor storage. |
| Schema & Formatting (AI Recruitment & GDPR) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for ChatGPT on GDPR AI recruitment. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for AI Recruitment & GDPR while shielding real names. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets ChatGPT trace root causes cleanly inside sanitized hiring privacy compliance logs. |
Bijective Prompt Blueprint for AI Recruitment & GDPR
Attach this guardrail prompt to any redacted AI Recruitment & GDPR session so downstream models keep symbolic tags intact for instant restoration:
Task for ChatGPT: Review masked AI Recruitment & GDPR input (GDPR AI recruitment).
1. Summarize findings around [NAME_1] and [IBAN_1].
2. Highlight next actions for European business owners.
3. Preserve bracketed placeholders verbatim.

[INSERT TOKENIZED INPUT]
Task for ChatGPT: Review masked AI Recruitment & GDPR input (GDPR AI recruitment).
1. Summarize findings around [NAME_1] and [IBAN_1].
2. Highlight next actions for European business owners.
3. Preserve bracketed placeholders verbatim.

[INSERT TOKENIZED INPUT]
How Data Protection Officers (DPOs) Enforce Zero-Egress on AI Recruitment & GDPR
Bridging 5(1)(c)) compliance and fast AI Recruitment & GDPR iteration relies on OpenAI dpa compliance pseudonymization over raw candidate data protection entries.
Local Tokenization Architecture: AI Recruitment & GDPR
Replacing destructive blanks, ZTDS™ turns GDPR AI recruitment in AI Recruitment & GDPR into reversible [IBAN_1] tokens via offline endpoint scrubber, honoring safely paste work emails into ChatGPT without leaking data.
Non-PII SHA-256 receipts accompany AI Recruitment & GDPR offline runs on hiring privacy compliance, eliminating Art. 44 transfer & training exposure alongside reverse unscrubbing.
