
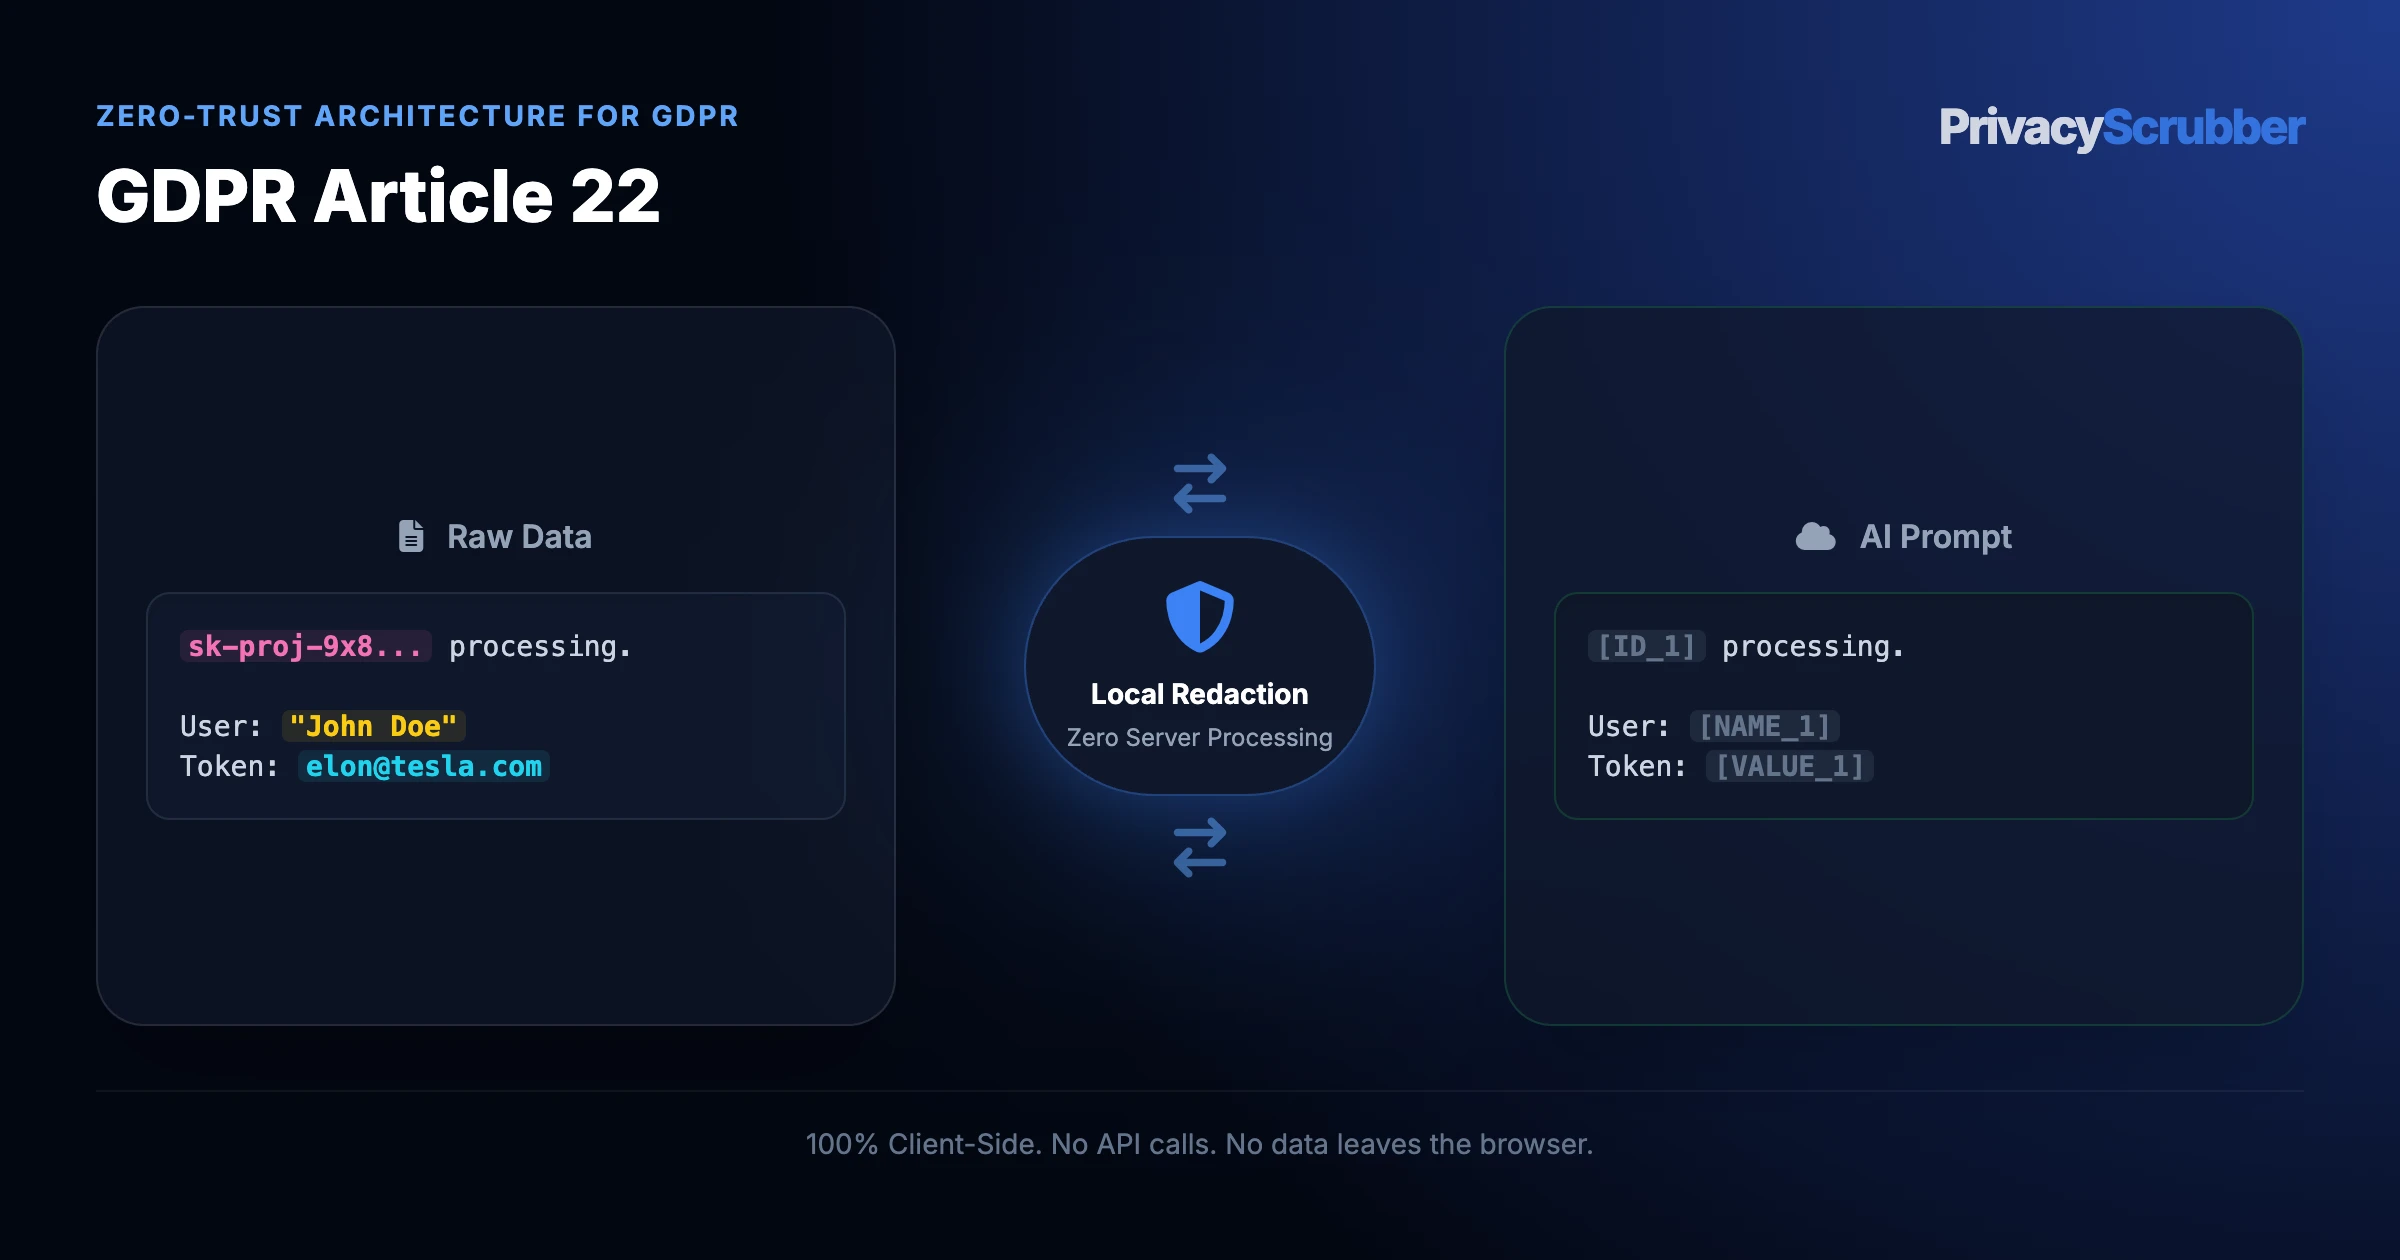
Sub-millisecond local RAM (GDPR) lets DPOs analyze GDPR Article 22 in ChatGPT without unmasked gdpr article 22 ai exposure. Sensitive gdpr article 22 ai literals swap to [NATIONAL_ID_1] before dispatch.
Data Leakage Risks in GDPR Article 22 for Privacy and DPO Teams
Unredacted prompts in GDPR Article 22 send gdpr article 22 ai straight to Mistral. Using GDPR AI privacy guides, teams deploy offline endpoint scrubber and map inputs to [IBAN_1].
Comply with GDPR Automated Decision-Making rules. Prevent algorithmic bias in HR and Finance by scrubbing demographic PII from AI prompts. Daily GDPR prompts pack nested preventing ai bias ztds context that turns routine GDPR Article 22 tasks into GDPR (Article 32 incidents.
Why DPOs Isolate GDPR Article 22 Locally
Comply with GDPR Automated Decision-Making rules. Prevent algorithmic bias in HR and Finance by scrubbing demographic PII from AI prompts. Without local pre-scrubbing via local RAM (GDPR), DPOs handle gdpr article 22 ai payloads that leak straight into Mistral queues.
Encrypted browser vaults keep custom gdpr article 22 ai rules on device so DPOs scale GDPR safety across ChatGPT with zero vendor sub-processors.
Deterministic Token Mapping for GDPR Article 22
Use the classification table below to separate high-liability GDPR Article 22 attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Keys & Account Codes (preventing ai bias ztds) | REDACT | [IBAN_1] | Stops preventing ai bias ztds credentials from entering cloud telemetry on GDPR Article 22. |
| Internal IDs inside GDPR Article 22 | REDACT | [NAME_1] / [IBAN_1] | Prevents unmasked gdpr article 22 ai exposure via pre-send local RAM (GDPR) substitution. |
| Private Records in GDPR Article 22 | REDACT | [NATIONAL_ID_1] | Replaces direct PII with [NATIONAL_ID_1] inside volatile client memory. |
| Numeric Totals & Ratios (preventing ai bias ztds) | PRESERVE | Cleartext ($ / %) | Enables accurate calculations across GDPR Article 22 without revealing identities. |
| Aggregation Counts & Deltas | PRESERVE | Cleartext Metrics | Supports statistical analysis of gdpr article 22 ai without linking individuals. |
| GDPR (Article 32 Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map GDPR Article 22 findings directly against policy clauses. |
Safe LLM Prompt Template for GDPR Article 22
Attach this guardrail prompt to any redacted GDPR Article 22 session so downstream models keep symbolic tags intact for instant restoration:
Role: GDPR advisor evaluating GDPR Article 22.
Sanitized tokens ([NAME_1], [IBAN_1]) mask all gdpr article 22 ai identifiers.
1. Flag operational gaps in preventing ai bias ztds.
2. Recommend GDPR (Article 32 fixes.
3. Keep [NAME_1] unchanged.

[PASTE GDPR ARTICLE 22 TEXT]
Role: GDPR advisor evaluating GDPR Article 22.
Sanitized tokens ([NAME_1], [IBAN_1]) mask all gdpr article 22 ai identifiers.
1. Flag operational gaps in preventing ai bias ztds.
2. Recommend GDPR (Article 32 fixes.
3. Keep [NAME_1] unchanged.

[PASTE GDPR ARTICLE 22 TEXT]
Audit Readiness Across GDPR Article 22 Workstations
Proving pre-transmission sanitization on preventing ai bias ztds fulfills GDPR (Article 32 reviews of GDPR Article 22, echoing principles across bypassing schrems ii.
3-Step Local RAM Redaction for GDPR Article 22 Workflows
Local RAM re-hydration restores authentic gdpr article 22 ai values inside GDPR Article 22 replies after local RAM (GDPR) completes docker local PII sanitization sidecar masking.
Testing GDPR Article 22 offline lets DPOs prove preventing ai bias ztds masking lives solely in RAM, reinforcing Claude 3.7 extended thinking.
