
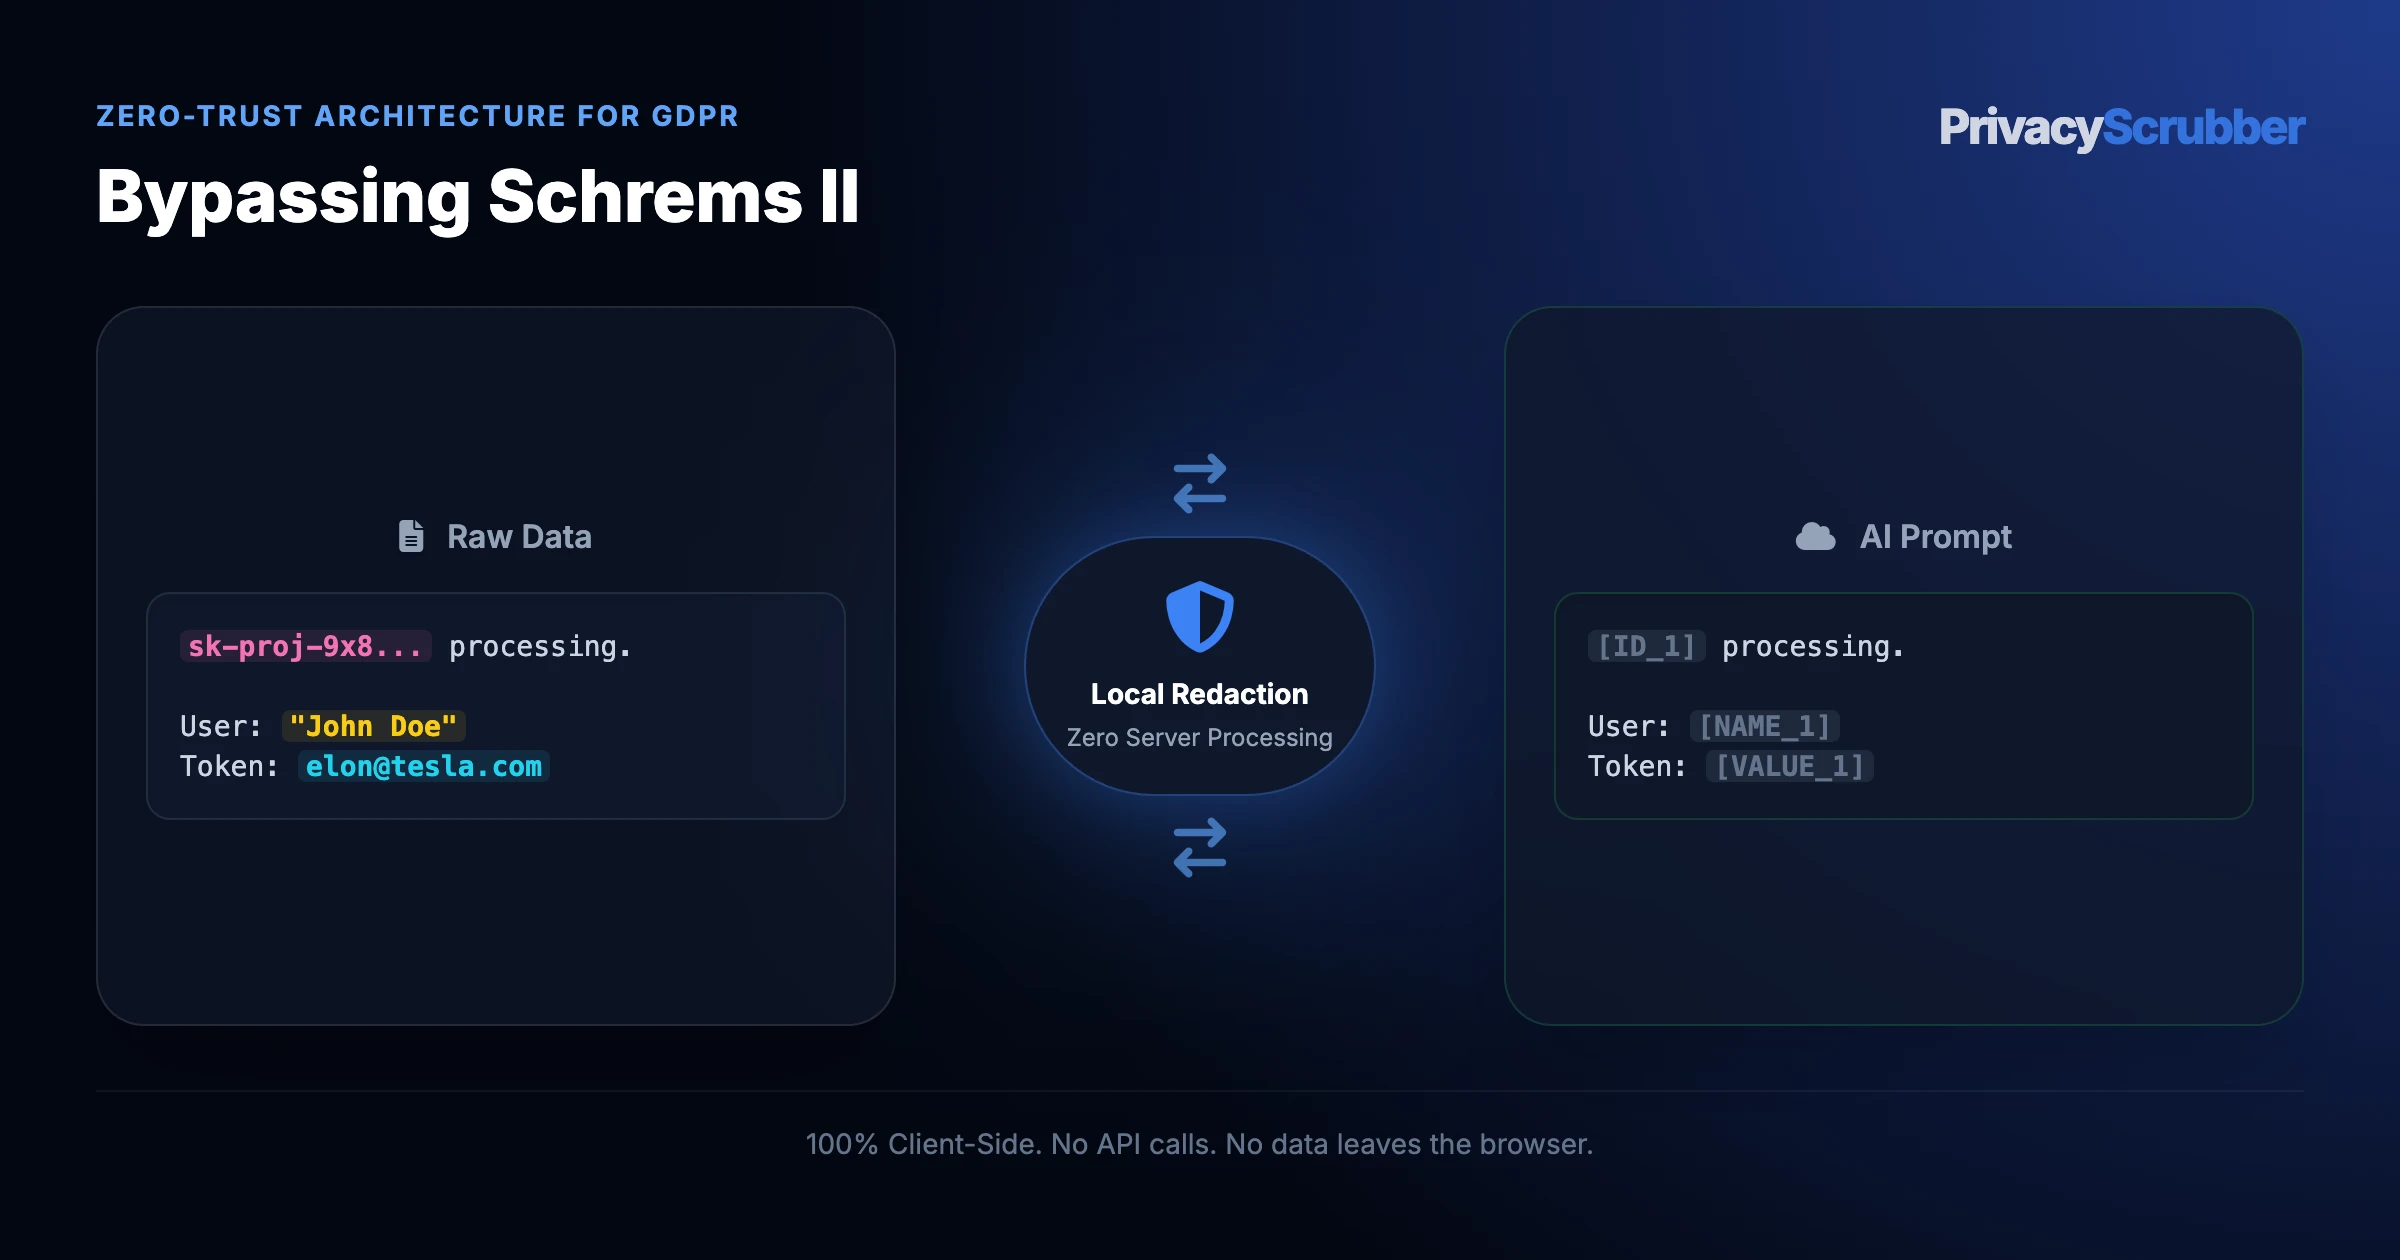
DPOs running Bypassing Schrems II via ChatGPT risk Art. 44 transfer & training exposure. Using volatile memory engine converts cross border data transfer ai into [NAME_1] locally in sub-millisecond RAM under GDPR (Article 32.
Bypassing Schrems II Exposure Surface for Privacy and DPO Teams
Scaling Bypassing Schrems II across GDPR units fails whenever Art. 44 transfer & training exposure exposes cross border data transfer ai. Turn to GDPR AI privacy guides to isolate schrems ii chatgpt in local heap RAM.
In Bypassing Schrems II, productivity clashes with GDPR (Article 32 due to Art. 44 transfer & training exposure. Comply with GDPR Chapter V cross-border rules for AI without US transfer risks. Redact EU personal data locally in browser RAM before prompt submission. Endpoint scrubbing converts schrems ii chatgpt to [NAME_1] first.
Stopping cross border data transfer ai Leaks in ChatGPT
Traditional gateways inspect cross border data transfer ai only after transit begins, creating GDPR (Article 32 gaps for DPOs. Using volatile memory engine isolates Bypassing Schrems II into [IBAN_1] right inside volatile memory.
Across browser extensions, IDE stdio tools, and Node.js pipelines, local RAM (GDPR) guarantees uniform schrems ii chatgpt protection on every Bypassing Schrems II request.
Deterministic Token Mapping for Bypassing Schrems II
This field-level specification ensures Bypassing Schrems II prompts retain 100% mathematical and semantic accuracy with zero cleartext PII egress:
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Internal IDs inside Bypassing Schrems II | REDACT | [NAME_1] / [IBAN_1] | Prevents Art. 44 transfer & training exposure via pre-send volatile memory engine substitution. |
| Private Records in Bypassing Schrems II | REDACT | [NATIONAL_ID_1] | Replaces direct PII with [NATIONAL_ID_1] inside volatile client memory. |
| Routing Endpoints (eu us data privacy framework ai) | REDACT | [NATIONAL_ID_1] | Blocks contact linkage when DPOs analyze cross border data transfer ai batches. |
| Domain Instructions (GDPR) | PRESERVE | Cleartext Logic | Retains workflow intent so DPOs get actionable eu us data privacy framework ai outputs. |
| Numeric Totals & Ratios (schrems ii chatgpt) | PRESERVE | Cleartext ($ / %) | Enables accurate calculations across Bypassing Schrems II without revealing identities. |
| Aggregation Counts & Deltas | PRESERVE | Cleartext Metrics | Supports statistical analysis of cross border data transfer ai without linking individuals. |
Token-Preserving AI Prompt for Bypassing Schrems II
Pair this structured instruction with your tokenized Bypassing Schrems II payload so ChatGPT, Claude, or Gemini preserves all bracketed surrogates for local RAM restoration:
Context: Local RAM scrubbing converted cross border data transfer ai to [NAME_1] / [NATIONAL_ID_1] for Bypassing Schrems II.
1. Audit logic and risks.
2. Keep output aligned with GDPR (Article 32.
3. Retain all tokens untouched.

[PASTE CLEAN PAYLOAD]
Context: Local RAM scrubbing converted cross border data transfer ai to [NAME_1] / [NATIONAL_ID_1] for Bypassing Schrems II.
1. Audit logic and risks.
2. Keep output aligned with GDPR (Article 32.
3. Retain all tokens untouched.

[PASTE CLEAN PAYLOAD]
How Data Protection Officers (DPOs) Enforce Zero-Egress on Bypassing Schrems II
Enforcing GDPR (Article 32 on Bypassing Schrems II connects directly with dsar nightmare in RAG systems (and how pre-ingestion scrubbing stops IT)—ensuring cross border data transfer ai becomes [NAME_1] before cloud transit.
Zero-Trust European Consumer Tokenization for Bypassing Schrems II
Deploying local RAM (GDPR) traps Bypassing Schrems II inputs locally, mapping schrems ii chatgpt to [IBAN_1]; aligned with go (golang) LLM PII masking, ChatGPT never touches cleartext.
Transparent DevTools inspection proves Bypassing Schrems II sends zero cross border data transfer ai packets externally, backing secure AI agent memory and GDPR (Article 32.
