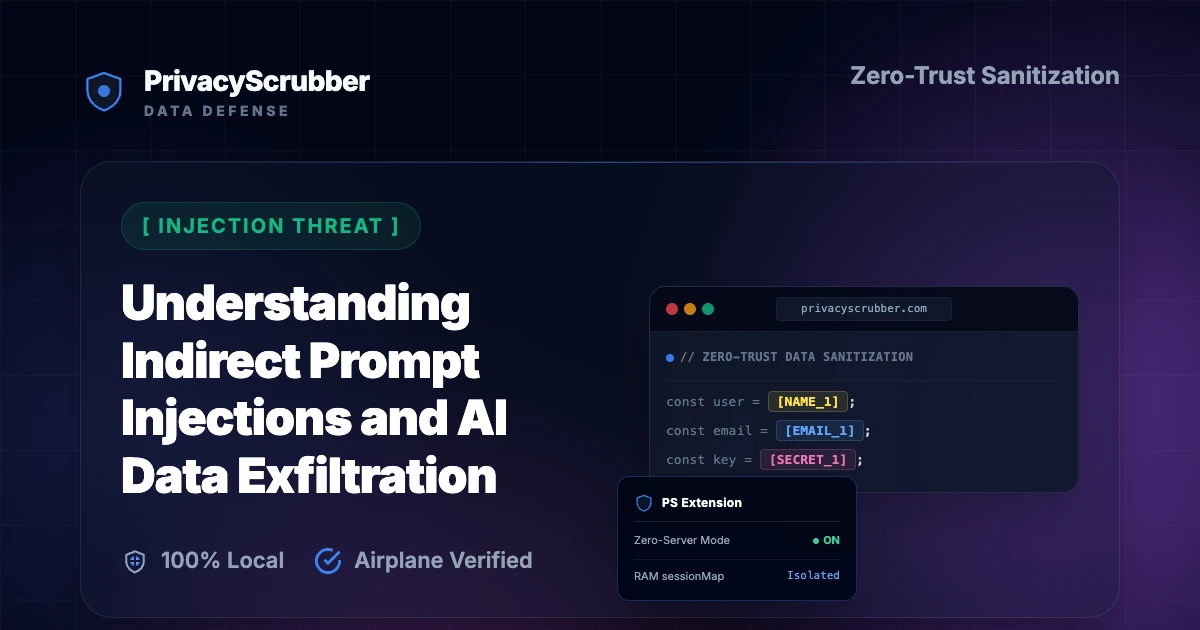
Understanding Indirect Prompt Injections and AI Data Exfiltration
Understanding Indirect Prompt Injections and AI Data Exfiltration: A look at how indirect prompt injections trick LLMs like Google Gemini into exfiltrating user data, and how local clipboard sanitization guards your inputs.
The Stealthy Rise of Indirect Injections
Prompt injections are no longer limited to users trying to make ChatGPT write jokes. A much more dangerous threat has emerged: Indirect Prompt Injection. Security experts advise implementing a local AI Security Perimeter to isolate client prompts before they enter the model context.
In this scenario, an attacker places hidden instructions inside a website, PDF, or email. When you use Google Gemini or Claude to summarize that document, the AI reads the hidden instructions and acts on them. The threat is closely linked to the AWS logging leaks highlighted in the Claude for Work 30-Day Log Exposure, showing how vulnerable cached prompts are to remote exfiltration.
Why Firewalls and VPNs Can't Stop This
Traditional corporate security focuses on blocking unauthorized network requests. But when you use an AI tool, you authorize the connection. The indirect injection executes inside the LLM's context window. Because the channel is legitimate, firewalls and VPNs see it as normal traffic. This makes it incredibly difficult to satisfy compliance requirements under SOC 2 Confidentiality Audits without active client-side redaction.
Protect the Prompt, Neutralize the Injection
Since the AI model can be tricked into leaking its context, you must ensure its context contains nothing of value to an attacker. Organizations can completely eliminate this vulnerability by deploying Zero-Trust Data Sanitization on all employee workstations.
By running prompts through PrivacyScrubber first, original values are held securely in the browser RAM's sessionMap. The text sent to Gemini or Claude contains only anonymous tokens (like [NAME_1]). If the model is hit by an injection, the attacker only exfiltrates useless tags. Once the reply returns, PrivacyScrubber restores original details locally on your screen with 0ms latency, ensuring secure and private AI operations.
Step-by-Step Integration Guide: Understanding Indirect Prompt Injections and AI Data Exfiltration
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use Claude (Anthropic):
1 Method A: Instant Clipboard & Web Workspace
Fastest for ad-hoc debugging, server crash logs, or DB dumps:
- Paste the raw database dump, stack trace, or config payload into PrivacyScrubber.
- Click Sanitize Prompt to locally tokenize all tokens, hostnames, and API secrets with 100% Local RAM Processing.
- Copy the sanitized code and safely query ChatGPT, Claude, or Copilot.
- Reveal responses locally using Reveal Originals with zero data egress.
2 Method B: Chrome Extension & MCP Server
For automated in-browser prompt masking & IDE agents (Cursor / Cline):
- Install the free PrivacyScrubber Extension to auto-mask credentials directly in ChatGPT/Claude inputs.
- Or connect the PrivacyScrubber MCP Server via Developer SDK to Cursor, Cline, or Claude Code.
- Session token maps remain 100% in volatile RAM with zero telemetry.
- Debug complex architectures without leaking production database URIs or AWS secrets.
Local Redaction & Risk Matrix for Security
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| User / Server IP Addresses | [IP_ADDRESS] | High (DLP / Location footprinting) | IPv4 / IPv6 format strip |
| AWS_KEY Details | [AWS_KEY] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_HOSTNAME Details | [INTERNAL_HOSTNAME] | Medium (PII Exposure) | Deterministic local swap |
| MAC_ADDRESS Details | [MAC_ADDRESS] | Medium (PII Exposure) | Deterministic local swap |
| VULN_ID Details | [VULN_ID] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Lead DevSecOps Engineer / Cloud Security Architect · Target: Claude (Anthropic)Act as a principal cloud systems architect. Analyze the following sanitized production stack trace and database configuration for [DB_NAME_1]: 1. Identify the root cause of the connection pool exhaustion and query timeouts. 2. Provide an optimized, non-blocking connection pool configuration for high concurrency. 3. Draft a step-by-step remediation patch. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Retain all cryptographic token identifiers ([DB_NAME_1], [INTERNAL_IP_1], [SECRET_1], [JWT_TOKEN_1]) strictly unchanged in your configuration suggestions for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Enterprise Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Sensitive Data compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any sensitive data text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.