
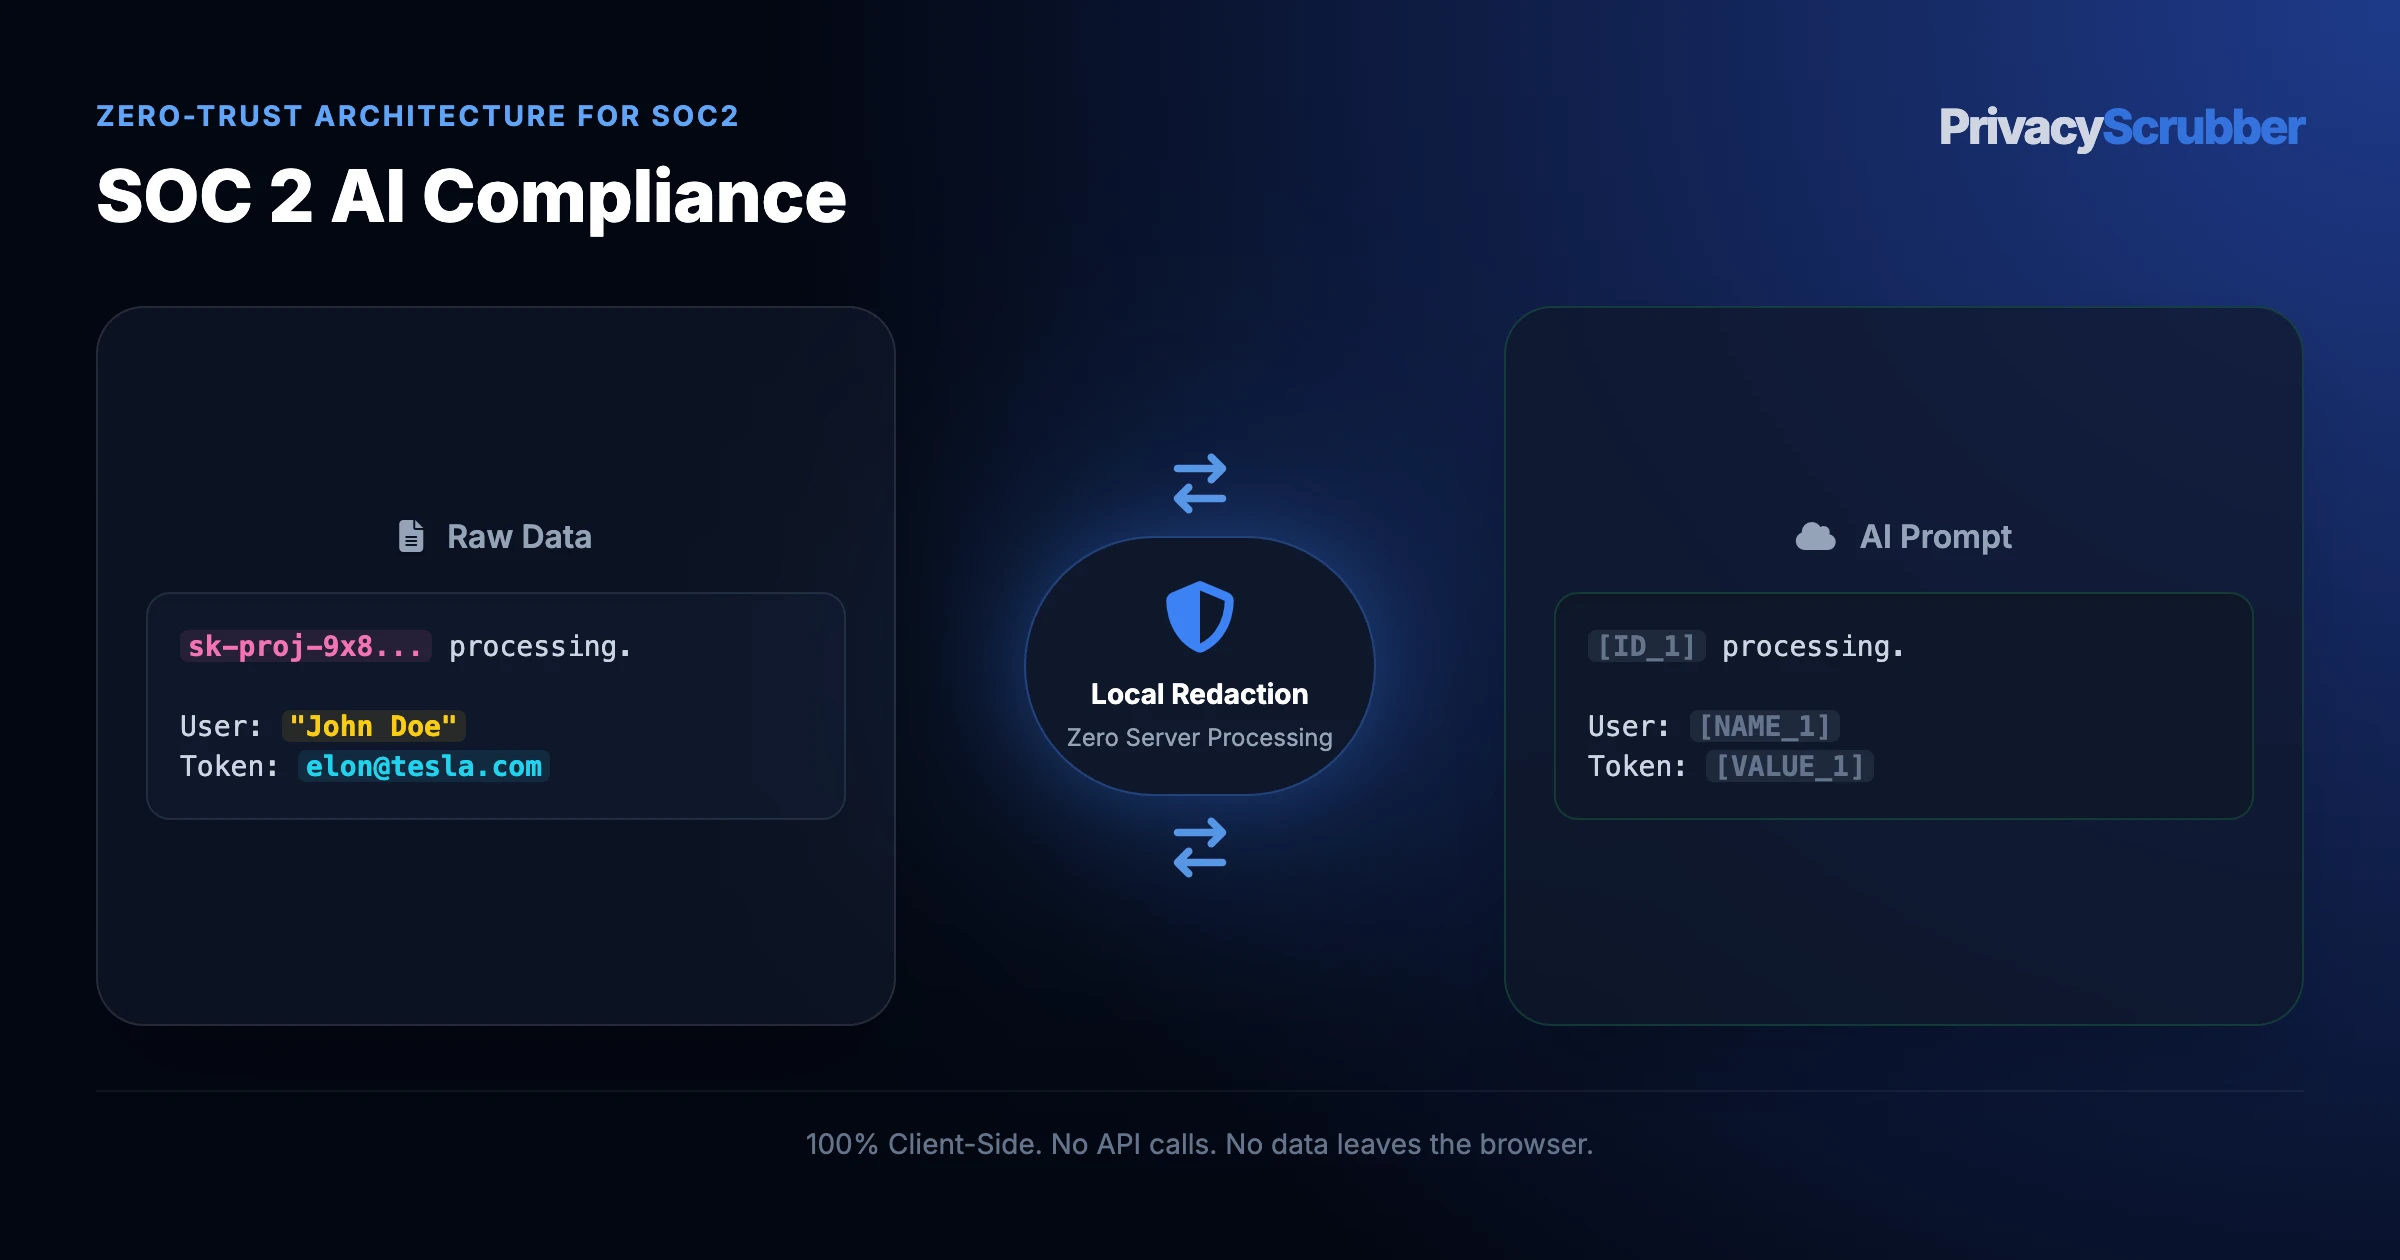
For SOC 2 governance over SOC 2 AI Compliance, SOC 2 Type II Trust Service Criteria (Privacy and Security) audits inspect egress points. Tokenizing SOC 2 AI compliance via TEAMS & CISO SHA-256 receipts yields verifiable [USER_1] isolation.
Why Unmasked Prompts Break SOC 2 AI Compliance Security
Before prompting Vanta about SOC 2 AI Compliance, CISOs strip SOC 2 AI compliance and client-side tokenization SOC 2 into [USER_1] tokens following SOC 2 AI privacy guides.
Satisfy SOC 2 CC9.1 confidentiality with AI. De-identify customer PII locally in browser memory before cloud transmission to avoid compliance breaches. Across SOC 2 apps, SOC 2 AI Compliance embeds regulated SOC 2 AI compliance attributes vulnerable to raw SOC 2 CC9.1 AI privacy retention under SOC 2 Type II Trust Service Criteria (Privacy and Security).
Pre-Prompt Sanitization for SOC 2 AI Compliance
Unfiltered prompts in SOC 2 AI Compliance replicate confidential SOC 2 CC9.1 AI privacy across Vanta logs. Deploying browser ZTDS shield replaces personal identifiers with [ID_1] in sub-millisecond RAM.
Instead of destroying prompt context on SOC 2 CC9.1 AI privacy, reversible [USER_1] surrogates keep multi-turn logic coherent across Vanta until local Reveal completes.
Balancing AI Context & Privacy in SOC 2 AI Compliance
Use the classification table below to separate high-liability SOC 2 AI Compliance attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Regulated Strings (SOC 2 data de-identification) | REDACT | [ID_1] | Applies SOC 2 Type II Trust Service Criteria (Privacy and Security) minimization locally before SOC 2 AI Compliance leaves RAM. |
| Tax, Token & Session Strings (SOC 2 CC9.1 AI privacy) | REDACT | [SECRET_1] | Zero-egress tokenization keeps SOC 2 AI Compliance identifiers off vendor storage. |
| Keys & Account Codes (SOC 2 CC9.1 AI privacy) | REDACT | [SECRET_1] | Stops SOC 2 CC9.1 AI privacy credentials from entering cloud telemetry on SOC 2 AI Compliance. |
| SOC 2 Type II Trust Service Criteria (Privacy and Security) Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map SOC 2 AI Compliance findings directly against policy clauses. |
| Schema & Formatting (SOC 2 AI Compliance) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for Vanta on SOC 2 AI compliance. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for SOC 2 AI Compliance while shielding real names. |
Zero-Trust System Prompt: SOC 2 AI Compliance
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Review SOC 2 AI compliance workflow for SOC 2 AI Compliance under SOC 2 Type II Trust Service Criteria (Privacy and Security).
1. Inspect interactions between [USER_1] and [CUSTOMER_1].
2. Deliver concise steps preserving every bracketed token.

[INSERT SCRUBBED TEXT]
Review SOC 2 AI compliance workflow for SOC 2 AI Compliance under SOC 2 Type II Trust Service Criteria (Privacy and Security).
1. Inspect interactions between [USER_1] and [CUSTOMER_1].
2. Deliver concise steps preserving every bracketed token.

[INSERT SCRUBBED TEXT]
Governance Requirements Governing SOC 2 AI Compliance
Eliminating third-party processor exposure on SOC 2 AI Compliance matches prevent SOC 2 audit trail & evidence log leakage to cloud safeguards and keeps SOC 2 CC9.1 AI privacy compliant with SOC 2 Type II Trust Service Criteria (Privacy and Security).
Isolating Sensitive Fields Inside SOC 2 AI Compliance Prompts
A local firewall via TEAMS & CISO SHA-256 receipts shields SOC 2 AI Compliance: SOC 2 AI compliance becomes [SECRET_1] on-device before Drata, delivering ChatGPT team workspace suspensions parity.
Enable Airplane Mode and mask SOC 2 AI compliance inside SOC 2 AI Compliance; all [USER_1] swaps finish in RAM per nestjs PII sanitization interceptor.
