
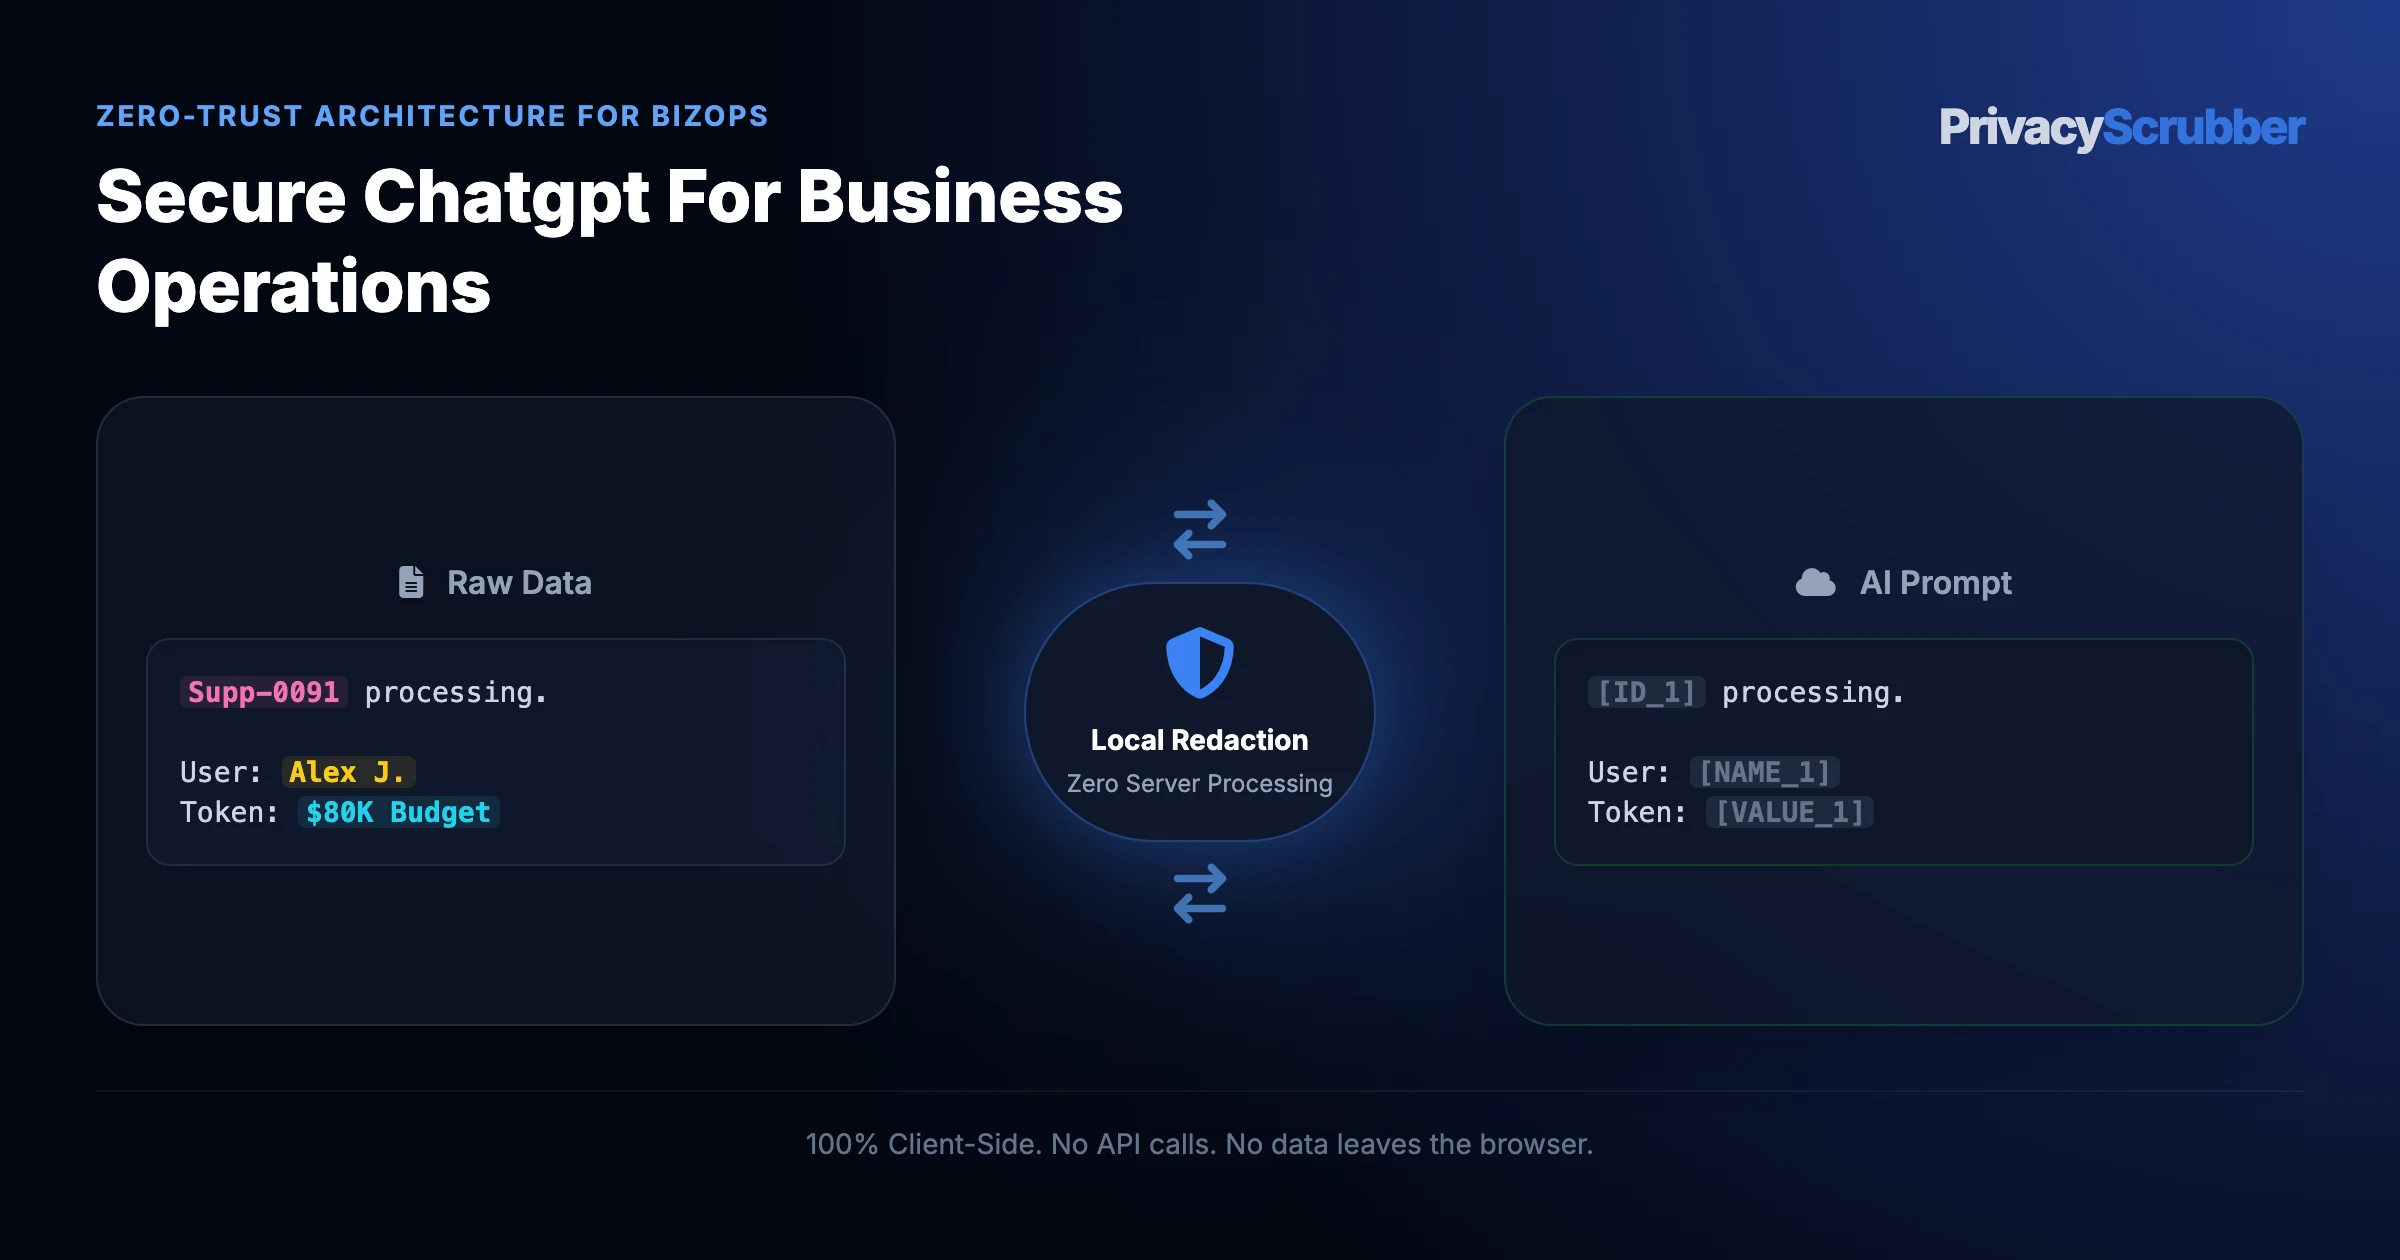
Operationalizing secure chatgpt for business operations and business operations ai data governance for Secure ChatGPT for Business Operations demands an air-gapped client boundary. PrivacyScrubber's PrivacyScrubber BizOps & Procurement Profile replaces regulated identifiers with reversible tokens ([VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1]) locally, eliminating exposing supplier pricing schedules, SLA penalties, and vendor banking details during AI contract analysis and establishing Corporate NDAs and Trade Secret frameworks technical safe harbor.
Data Leakage Risks in Secure ChatGPT for Business Operations for Corporate Strategy and BizOps Teams
Achieving verifiable data protection for Secure ChatGPT for Business Operations is a foundational requirement when fp&a analysts, business operations managers, and corporate development teams integrate Virtual Deal Rooms, ChatGPT, and FP&A forecasting AI. Because exposing supplier pricing schedules, SLA penalties, and vendor banking details during AI contract analysis, unmasked secure chatgpt for business operations payloads create immediate exposure across Business Operations perimeters. Our Business Operations AI privacy guides detail how to isolate bizops ai data governance in local RAM before any cloud API call occurs.
For fp&a analysts, business operations managers, and corporate development teams, Secure ChatGPT for Business Operations workflows involve high-sensitivity secure chatgpt for business operations and bizops ai data governance attributes that cannot be shared with cloud sub-processors. Scale business operations with secure ChatGPT workflows using local data sanitization. 100% client-side in browser RAM with zero cloud egress. Standard administrative policies alone cannot stop breaching M&A confidentiality and exposing proprietary EBITDA KPIs to competitors via AI memory.
Enforcing Corporate NDAs and Trade Secret frameworks Technical Safeguards on Secure ChatGPT for Business Operations
Scale business operations with secure ChatGPT workflows using local data sanitization. 100% client-side in browser RAM with zero cloud egress. Standard perimeter firewalls cannot parse unstructured secure chatgpt for business operations text pasted into browser chat boxes or serialized into agent tool calls, leading to exposing supplier pricing schedules, SLA penalties, and vendor banking details during AI contract analysis. PrivacyScrubber resolves this at the source with PrivacyScrubber BizOps & Procurement Profile.
Every sensitive attribute across business operations ai data governance and corporate operations pii masking is substituted with format-preserving tokens ([VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1]) in volatile RAM (~0.4ms). Upstream LLMs reason over clean symbolic structures, and authentic identifiers are re-hydrated locally on response under Corporate NDAs and Trade Secret frameworks.
Field-by-Field Sanitization Rule for Secure ChatGPT for Business Operations
To maintain LLM analytical context while avoiding cloud data breaches, apply this deterministic field mapping in local RAM before submitting Secure ChatGPT for Business Operations prompts:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Contact & Routing Endpoints (corporate operations pii masking) | REDACT | [CONTACT_1] | Eliminates cross-record linkage and unauthorized sub-processor indexing during Secure ChatGPT for Business Operations. |
| Authentication, Account & Reference Keys (business operations ai data governance) | REDACT | [CONTRACT_1] | Blocks credential, account, or case-number exfiltration across Business Operations telemetry and vendor logs. |
| Primary Identity & Subject Records (secure chatgpt for business operations) | REDACT | [VENDOR_1] | Corporate NDAs and Trade Secret frameworks direct identifier guard: prevents cloud LLMs from associating Secure ChatGPT for Business Operations prompts with real individuals. |
| Relative Timelines, Status Codes & Error Severities | PRESERVE | Cleartext (ISO Sequence) | Maintains chronological ordering and root-cause diagnostics across business operations ai data governance workflows. |
| Quantitative Metrics, Ratios & Aggregated Totals | PRESERVE | Cleartext ($ / % / Deltas) | Enables accurate mathematical reasoning and variance analysis for Secure ChatGPT for Business Operations without identity exposure. |
| Structural Schema, Keys & Secure ChatGPT for Business Operations Syntax | PRESERVE | Cleartext Structure | Required so the LLM can parse secure chatgpt for business operations hierarchy, JSON/SQL grammar, and document formatting. |
Token-Preserving AI Prompt for Secure ChatGPT for Business Operations
Pair this structured instruction with your tokenized Secure ChatGPT for Business Operations payload so ChatGPT, Claude, or Gemini preserves all bracketed surrogates for local RAM restoration:
System Role: Business Operations Compliance & Technical Analyst for Secure ChatGPT for Business Operations.
Input State: Pre-sanitized in volatile memory under Corporate NDAs and Trade Secret frameworks safeguards ([VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1]).

Deliverables:
1. Analyze relationships between [VENDOR_1] and [CONTRACT_1] within the secure chatgpt for business operations workflow.
2. Highlight any policy, schema, or execution gaps related to corporate operations pii masking.
3. Preserve every [VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1] tag intact in your output for 1-click local re-hydration.

[PASTE SANITIZED PAYLOAD HERE]
System Role: Business Operations Compliance & Technical Analyst for Secure ChatGPT for Business Operations.
Input State: Pre-sanitized in volatile memory under Corporate NDAs and Trade Secret frameworks safeguards ([VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1]).

Deliverables:
1. Analyze relationships between [VENDOR_1] and [CONTRACT_1] within the secure chatgpt for business operations workflow.
2. Highlight any policy, schema, or execution gaps related to corporate operations pii masking.
3. Preserve every [VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1] tag intact in your output for 1-click local re-hydration.

[PASTE SANITIZED PAYLOAD HERE]
How M&A Legal and Corporate Risk Committees Enforce Zero-Egress on Secure ChatGPT for Business Operations
Regulatory expectations for Business Operations are explicit: Corporate NDAs and Trade Secret frameworks. Navigating the compliance boundary for Secure ChatGPT for Business Operations directly intersects with PII scrubber for corporate deal rooms—preventing secure chatgpt for business operations from becoming a permanent liability in external systems. Enforcing Statutory Risk Minimization requires stripping identifiers into [VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1] before cloud transit.
Running AI on Secure ChatGPT for Business Operations Without Sending Real Identifiers
PrivacyScrubber enforces Zero-Trust Data Sanitization (ZTDS™) for Secure ChatGPT for Business Operations via PrivacyScrubber BizOps & Procurement Profile. Sensitive secure chatgpt for business operations and bizops ai data governance fields are replaced in <1ms of local RAM with bijective tokens ([VENDOR_1], [CONTRACT_1], [CONTACT_1], [TAX_ID_1]) prior to prompting Virtual Deal Rooms, ChatGPT, and FP&A forecasting AI. This aligns with desktop AI agents privacy, allowing fp&a analysts, business operations managers, and corporate development teams to restore authentic values locally in 1 click once the model responds.
Compliance teams verify Secure ChatGPT for Business Operations by testing secure chatgpt for business operations and corporate operations pii masking redaction completely offline under the Airplane Mode Standard. Combined with use ChatGPT safely, this guarantees that volatile session maps never touch external storage.
