Sanitize ISO 20022 XML & SWIFT MT103 Messages for AI Financial Analysis
TEAMS EDITION
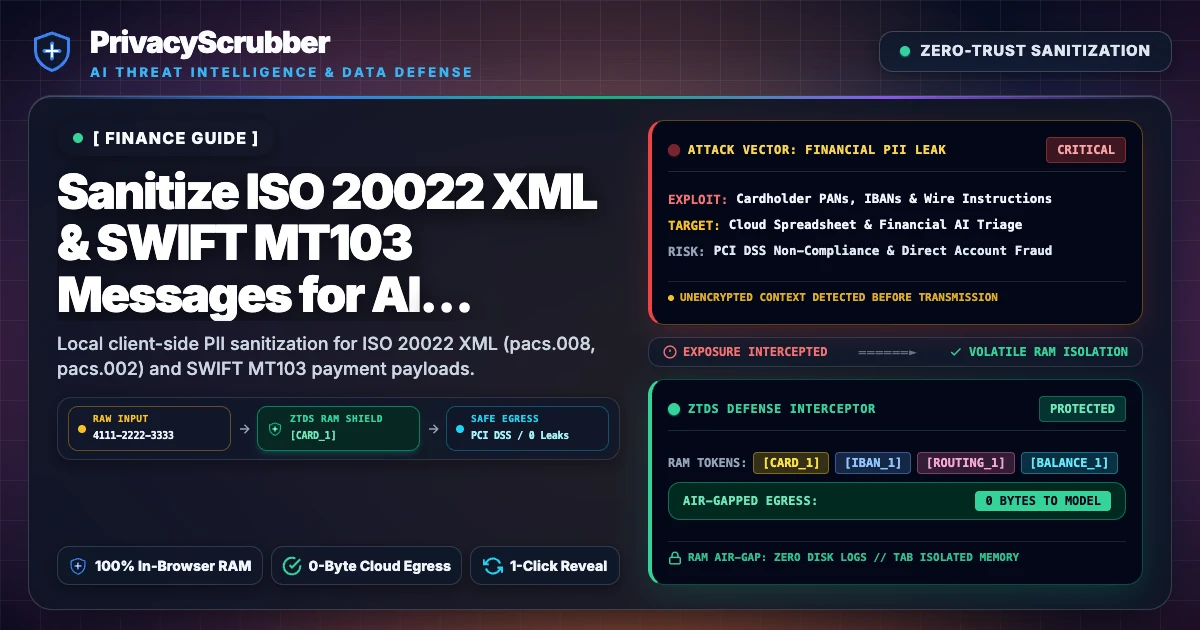
Sanitize ISO 20022 XML & SWIFT MT103 Messages for AI Financial Analysis: Local client-side PII sanitization for ISO 20022 XML (pacs.008, pacs.002) and SWIFT MT103 payment payloads. Redact debtor/creditor IBANs and personal identifiers while keeping XML schema and settlement amounts intact.
Ilya SibiryakovPrivacy Architect••3 min read
100% Local Airplane Mode
ISO 20022 XML & SWIFT MT103 / pacs.008 Payment Payloads Payment Systems Architects, Core Banking Engineers & FinTech Operations Analysts Gramm-Leach-Bliley Act (GLBA Safeguards Rule 16 CFR Part 314), PCI DSS 4.0 & EPC SEPA Rules
Direct Technical Standard (Zero-Trust Rule)
Sanitizing ISO 20022 XML (pacs.008, pacs.002) and SWIFT MT103 payment payloads for AI analysis requires removing debtor and creditor personal names, account IBANs/BBANs, postal addresses, and unmasked remittance notes while strictly keeping XML schema tags, interbank settlement amounts, currency codes, BICs, and settlement dates intact. This allows LLMs to debug payment routing failures without leaking customer financial identifiers.
AI Summary / Key Takeaways
Verified Zero-Trust Logic
"PrivacyScrubber provides the essential de-identification layer for Finance professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Finance data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
Zero-Trust Data Protection: Failing to mask client financial data before sending it to ChatGPT can trigger severe GLBA and SEC penalties. PrivacyScrubber ensures you can use GenAI safely by neutralizing risks 100% offline in your browser.
What Finance and Accounting Teams Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
To implement Sanitize ISO 20022 XML & SWIFT MT103 Messages for AI Financial Analysis safely across team workflows, companies must address the risk of data exfiltration. Using tools like ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools without local redaction leaves finance frameworks highly vulnerable. Our finance AI privacy guides details how to build a resilient finance security model that neutralizes sending client account numbers, portfolio balances, SSNs, and transaction histories to AI providers who may store or train on the data before any cloud API is called.
Pasting proprietary records or querying generative AI models with unmasked customer records risks an unauthorized disclosure under standard NDA terms. Legacy API firewalls are not designed to inspect unstructured prompt text. For financial advisors, accountants, loan officers, and fintech teams, preventing exfiltration requires local verification at the endpoint. Local client-side PII sanitization for ISO 20022 XML (pacs.008, pacs.002) and SWIFT MT103 payment payloads. Redact debtor/creditor IBANs and personal identifiers while keeping XML schema and settlement amounts intact.
Privacy Insight: Payment operations teams, core banking integration engineers, and FinTech developers use generative AI to debug rejected payment rails, validate XML schema parsing errors (pacs.008, pacs.002, camt.053), and simulate FedNow or SEPA routing hops. However, raw financial payment messages embed nonpublic personal information (NPI) — including debtor legal names, creditor IBANs, and residential addresses — regulated under the GLBA Safeguards Rule and PCI DSS 4.0. Cloud AI transmission without client-side tokenization exposes payment infrastructure to unauthorized cloud retention and multi-jurisdictional financial penalties.
Why Finance Compliance Teams Flag Unmasked AI Prompts
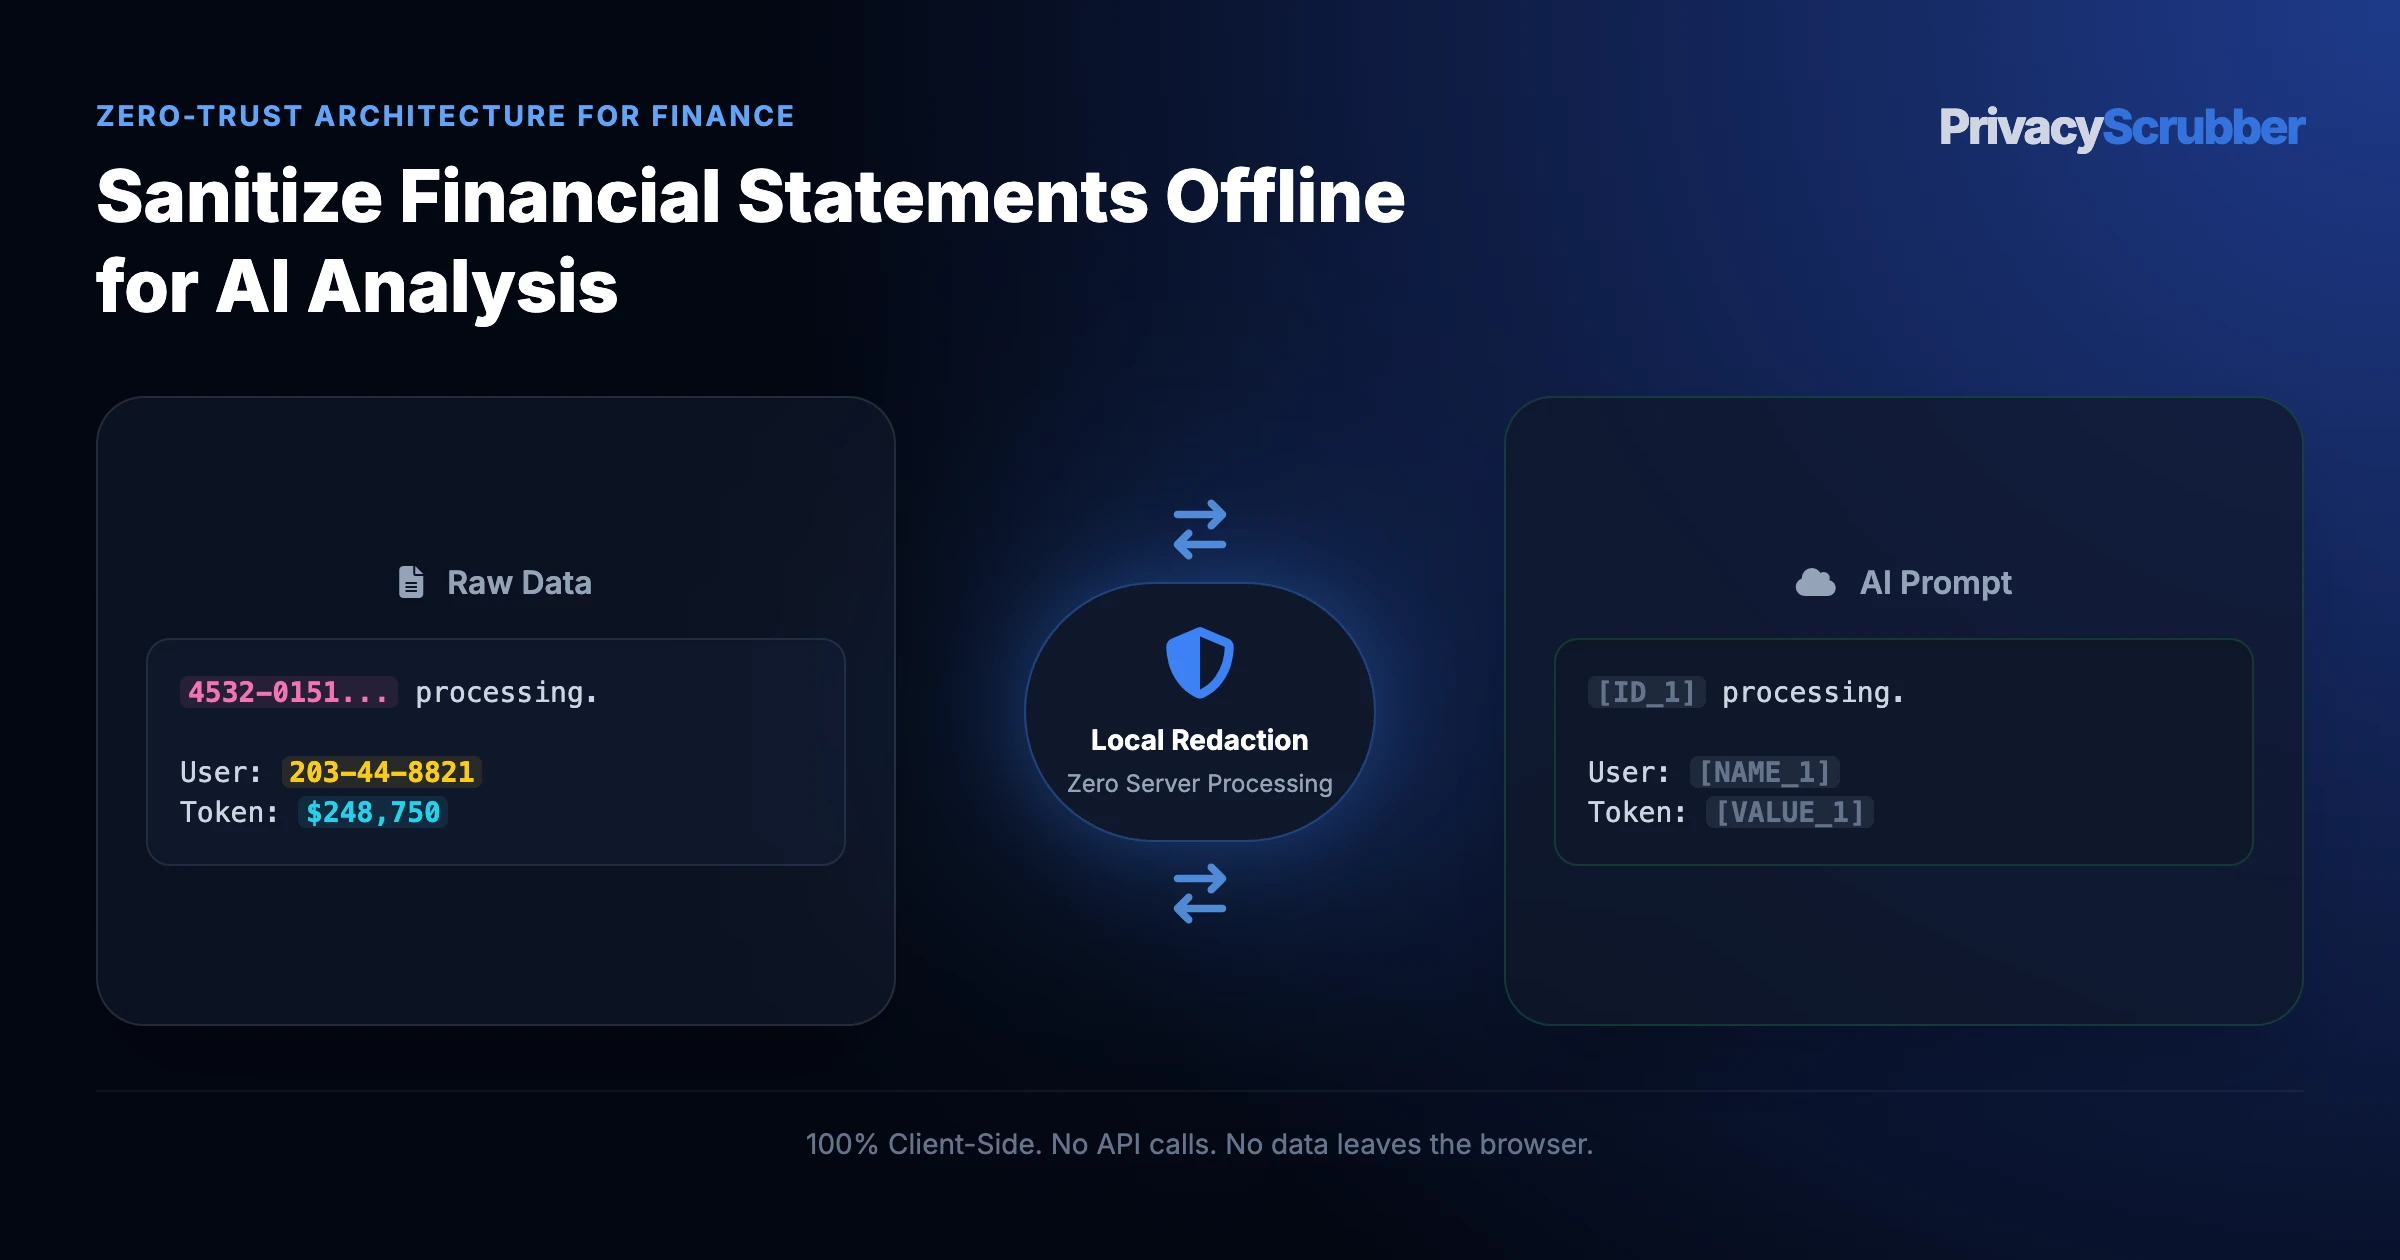
Regulatory oversight for the finance sector is explicit: SEC Regulation S-P, FINRA Rule 4370, PCI-DSS, and banking secrecy laws. However, technical compliance lags behind AI adoption curves. Navigating the data exposure surface often overlaps with sanitize financial statements offline for ai analysis — identifying how unstructured data becomes a permanent liability in model weights. To achieve verifiable security, you must eliminate the PII before it reaches the cloud. Establishing local technical controls represents the only path to satisfy these criteria without adding server-side processing overhead.
PrivacyScrubber delivers client-side protection through local Zero-Trust Data Sanitization (ZTDS), operating as a manual copy-paste board and via the PrivacyScrubber Chrome Extension.
How to Use AI on Real Finance Data — Without Sending a Single Real Name
PrivacyScrubber delivers client-side protection through local Zero-Trust Data Sanitization (ZTDS), operating as a manual copy-paste board and via the PrivacyScrubber Chrome Extension. The in-browser processor automatically maps and replaces identifying information with secure, non-associative tokens (like [NAME_1]) before cloud dispatch. This satisfies the requirements of centralized AI governance, allowing teams to utilize cloud engines without sending raw patient, customer, or employee identities. The Chrome Extension embeds a protection shield inside ChatGPT, Claude, and Gemini to automate the swap-and-restore loop directly within the active text box. Processing data through browser-based deterministic AST lookaround tokenization allows safe integration of ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools for complex tasks while preserving client privacy.
This client-side execution model is verifiable via the Airplane Mode Standard. Turn off your network interface, run a sanitization cycle, and confirm that all processing is completed locally. This aligns with financial SOC 2 compliance, proving that no database or server logs receive unmasked data.
Enterprise Finance Data Redaction
Auditing transaction ledgers or sanitizing bank records? Avoid the predatory 'per-seat' pricing models of legacy DLP systems. PrivacyScrubber TEAMS costs a flat $99/month for unlimited employees, supporting offline OCR document scrubbing and local re-hydration of tokenized bank statements.
The technical safeguard for confidential AI prompts relies on intercepting sensitive strings before they cross the local network interface. By replacing actual values with deterministic placeholders (e.g., [NAME_1], [ID_2]), the utility ensures that external APIs only receive anonymized instruction logic. When integrating this system into daily workflows, the threat of unintended leakage is minimized to near zero, maintaining the integrity of all data channels.
Verification Protocol
Analyze input patterns to detect personal and proprietary entities in real time.
Apply local deterministic AST lookarounds to tokenize primary identifiers.
Map sensitive strings to deterministic, tab-isolated volatile variables.
Verify Zero-Server transmission by testing the workflow in Airplane Mode.
The ISO 20022 Migration & AI Integration Blind Spot
As central banks and global payment rails (FedNow, SEPA, CHIPS, TARGET2) transition to ISO 20022 XML standards, the structural richness of financial messaging has increased dramatically. While this enables granular straight-through processing (STP), it also consolidates sensitive debtor and creditor nonpublic personal information (NPI) into explicit XML blocks. When core banking engineers paste failing XML envelopes into AI models to diagnose clearing rejections, they unintentionally transmit regulated customer identifiers to external servers. Using the local tokenization tools in our Financial Data Protection Hub, payment engineers sanitize payload data before diagnostic AI submission.
Protecting Customer Remittance & Wire Context
Unstructured remittance tags () represent a frequent source of accidental data exposure, often containing invoices, medical bill descriptions, or personal settlement references. Cross-referencing our Wire Transfer Redaction Protocols ensures complete elimination of customer PII while keeping interbank settlement amounts, currency codes, and routing BICs in cleartext.
PCI DSS 4.0 & Operational Log Resilience
Financial entities handling card-originated credit transfers must enforce strict boundaries under PCI DSS 4.0 Compliance Guidelines. When debugging failed payment transactions, developers must avoid leaking server hostnames and session credentials into AI prompts by deploying automated Server Log Sanitization Controls before LLM ingestion.
Instant Simulation
Sanitize ISO 20022 XML & SWIFT MT103 Messages for AI Financial Analysis Sanitizer
Watch our zero-trust engine neutralize sensitive identifiers 100% locally. No data ever leaves your device.
Local processing 0 Server logs
ZTDS_ENGINE_V1.5.0
PROMPT INPUT > Analyze the email from Bob Smith (bob.smith@corp.com, tel 555-0123) regarding project timeline.
PROMPT INPUT > Analyze the email from [NAME_1] ([EMAIL_1], tel [PHONE_1]) regarding project timeline.
Finance Detection Profile
Our zero-trust engine is pre-hardened for Finance workflows, automatically identifying and tokenizing the following parameters 100% locally.
BORROWER_NAME
Active Protection
SSN
Active Protection
EMPLOYER_NAME
Active Protection
FEIN
Active Protection
ACCOUNT_NUMBER
Active Protection
ROUTING_NUMBER
Active Protection
ADDRESS
Active Protection
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with financial SOC 2 compliance.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
Compliance Decision Matrix
Field-by-Field Sanitization Rule for ISO 20022 XML & SWIFT MT103 / pacs.008 Payment Payloads
To maintain LLM analytical context while avoiding cloud data breaches, follow this deterministic mapping before submitting prompts to third-party AI models:
Document Field / Box
Required Action
Deterministic Token
Statutory & AI Rationale
Debtor Legal Name (<Dbtr><Nm>)
REDACT
[NAME_1]
Originating sender personal identity; GLBA nonpublic personal information (NPI)
Debtor Account IBAN (<DbtrAcct><Id><IBAN>)
REDACT
[IBAN_1]
Direct bank account number; severe financial theft and account takeover risk
Debtor Postal Address (<Dbtr><PstlAdr>)
REDACT
[ADDRESS_1]
Residential address; enables geographic tracking and identity resolution
Creditor Legal Name (<Cdtr><Nm>)
REDACT
[NAME_2]
Beneficiary recipient individual identity subject to privacy regulations
Creditor Account IBAN (<CdtrAcct><Id><IBAN>)
REDACT
[IBAN_2]
Beneficiary bank account number protected under international banking rules
Unstructured Remittance Note (<RmtInf><Ustrd>)
REDACT
[REMITTANCE_1]
Free-text payment description frequently containing private invoice or medical PII
Interbank Settlement Amount (<IntrBkSttlmAmt>)
PRESERVE
Cleartext (EUR 350,000.00)
Core quantitative value required for AI liquidity validation and reconciliation
Settlement Date (<IntrBkSttlmDt>)
PRESERVE
Cleartext (2026-09-24)
Required for value date processing, interest calculation, and clearing deadlines
Bank routing identifiers; masked under specialized finance profile to prevent institutional routing enumeration
ISO 20022 XML Message Structure & Schema Tags
PRESERVE
Cleartext (<pacs.008.001.10>)
Mandatory syntactic schema required for LLM XML validation and syntax debugging
1-Click Persona Prompt
Safe LLM Prompt Template for ISO 20022 XML & SWIFT MT103 / pacs.008 Payment Payloads
Copy and paste this structured prompt into ChatGPT, Claude, or Gemini alongside your tokenized text to prevent LLM rejection:
You are a Lead Core Banking & ISO 20022 Integration Architect. Review the following sanitized pacs.008 customer credit transfer message where debtor/creditor names, IBANs, and street addresses are replaced with tokens ([NAME_1], [NAME_2], [IBAN_1], [IBAN_2], [ADDRESS_1], [ADDRESS_2]).

Tasks:
1. Validate the pacs.008.001.10 XML schema structure and check for mandatory ISO elements.
2. Confirm routing logic between initiating BIC (DEUTDEDDFXX) and instructed BIC (BNPAFRPPXXX) for SEPA clearing settlement.
3. Validate charge bearer code (SLEV) against European Payments Council standards for EUR 350,000.00 transfers.
4. Output a technical payment payload diagnostic report without attempting to discover real account holder names.

[PASTE SANITIZED TEXT HERE]
You are a Lead Core Banking & ISO 20022 Integration Architect. Review the following sanitized pacs.008 customer credit transfer message where debtor/creditor names, IBANs, and street addresses are replaced with tokens ([NAME_1], [NAME_2], [IBAN_1], [IBAN_2], [ADDRESS_1], [ADDRESS_2]).

Tasks:
1. Validate the pacs.008.001.10 XML schema structure and check for mandatory ISO elements.
2. Confirm routing logic between initiating BIC (DEUTDEDDFXX) and instructed BIC (BNPAFRPPXXX) for SEPA clearing settlement.
3. Validate charge bearer code (SLEV) against European Payments Council standards for EUR 350,000.00 transfers.
4. Output a technical payment payload diagnostic report without attempting to discover real account holder names.

[PASTE SANITIZED TEXT HERE]
LLM Code Assistants & Database Agents Integration
Step-by-Step Integration Guide: Sanitize ISO 20022 XML & SWIFT MT103 Messages for AI Financial Analysis
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use LLM Code Assistants & Database Agents:
Act as a senior database administrator. Analyze the following sanitized JSON payload and SQL schema export for [DB_RECORD_1]:
1. Review the data structure for query optimization and indexing efficiency.
2. Generate refactored SQL queries with optimized JOIN operations.
3. Ensure output adheres strictly to standard schema syntax.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Preserve all cryptographic token placeholders ([DB_RECORD_1], [API_KEY_1], [IP_ADDRESS_1]) exactly as formatted for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When LLM Code Assistants & Database Agents outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: ISO/IEC 27001:2022 Control A.8.11 (Data Masking) & GDPR Art. 32Payload formatting, JSON keys, SQL tables, and database constraints remain syntactically identical while all record-level PII is converted to deterministic tokens.
Finance Adoption Use Cases
Chief Risk OfficerGLBA & FINRA
Zero-Trust Verified
Masks account numbers, SSNs, and credit reports locally, ensuring financial analysts stay fully compliant with SEC and FINRA AI governance mandates.
Head of Private Wealth OperationsWEALTH MANAGEMENT
Zero-Trust Verified
Enables wealth managers to draft personalized portfolio reports without exposing High-Net-Worth client balances or tax IDs to cloud AI.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Finance compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any finance text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Finance Teams.
What sensitive data resides inside ISO 20022 XML payment messages?
ISO 20022 messages (such as pacs.008 customer credit transfers and pacs.002 payment status reports) contain debtor and creditor legal names (, ), bank account IBANs/BBANs (), physical street addresses (), tax identifiers, and unmasked payment remittance descriptions ().
How does client-side sanitization preserve XML schema validity for AI debugging?
PrivacyScrubber tokenizes only the leaf text nodes inside specific XML tags without altering tag names, attributes, namespaces, or hierarchy. A debtor name Maximilian Krause becomes [NAME_1], and an IBAN becomes [IBAN_1]. The resulting XML remains 100% syntactically valid against ISO 20022 XSD schemas, allowing LLMs to diagnose routing, tag formatting, and schema validation errors without data exposure.
Does PrivacyScrubber support both ISO 20022 MX and legacy SWIFT MT formats?
Yes. The sanitization engine supports both modern ISO 20022 XML payloads (pacs.008, pacs.009, camt.053, pain.001) and legacy SWIFT MT messages (MT103 Field 50a Ordering Customer, Field 59 Beneficiary, Field 70 Remittance). Both formats are processed entirely in local memory with zero external cloud API calls.
How do high-throughput payment rails integrate sanitization in automated pipelines?
FinTech and banking backend services integrate @privacyscrubber/sdk into payment exception queues and ETL pipelines. In-memory execution completes in under 1 millisecond per message, sanitizing payment payloads before sending diagnostic dumps to private AI observability models or agentic incident triage systems.
Does protecting data with PrivacyScrubber before AI processing satisfy SEC Regulation S-P?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with SEC Regulation S-P because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for finance workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match finance-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask finance data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your finance data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Sanitize Prompt" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard deterministic AST lookaround engine to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
How can banks safely use Generative AI?
Banks must prevent NPI (Non-Public Personal Information) from reaching external LLMs. Client-side scrubbing tools intercept account numbers, SSNs, and financial data at the cursor level. Ensure firm-wide compliance with our $99/mo TEAMS plan.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
Why Finance Compliance Teams Flag Unmasked AI Prompts
Regulatory oversight for the finance sector is explicit: SEC Regulation S-P, FINRA Rule 4370, PCI-DSS, and banking secrecy laws. However, technical compliance lags behind AI adoption curves. Navigating the data exposure surface often overlaps with sanitize financial statements offline for ai analysis — identifying how unstructured data becomes a permanent liability in model weights. To achieve verifiable security, you must eliminate the PII before it reaches the cloud. Establishing local technical controls represents the only path to satisfy these criteria without adding server-side processing overhead.
How to Use AI on Real Finance Data — Without Sending a Single Real Name
PrivacyScrubber delivers client-side protection through local Zero-Trust Data Sanitization (ZTDS), operating as a manual copy-paste board and via the PrivacyScrubber Chrome Extension. The in-browser processor automatically maps and replaces identifying information with secure, non-associative tokens (like [NAME_1]) before cloud dispatch. This satisfies the requirements of centralized AI governance, allowing teams to utilize cloud engines without sending raw patient, customer, or employee identities. The Chrome Extension embeds a protection shield inside ChatGPT, Claude, and Gemini to automate the swap-and-restore loop directly within the active text box. Processing data through browser-based deterministic AST lookaround tokenization allows safe integration of ChatGPT, Microsoft Copilot for Finance, and AI-powered spreadsheet tools for complex tasks while preserving client privacy.
Is PrivacyScrubber safe for iso 20022 ai sanitization, swift mt103 redaction, pacs 008 pii masking, fednow payment message privacy, sepa xml ai redaction, iban bank account redaction llm, payment routing ai analysis?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with iso 20022 ai sanitization, swift mt103 redaction, pacs 008 pii masking, fednow payment message privacy, sepa xml ai redaction, iban bank account redaction llm, payment routing ai analysis, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for finance?
Our engine includes 30 specialized industry profiles optimized for finance data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.