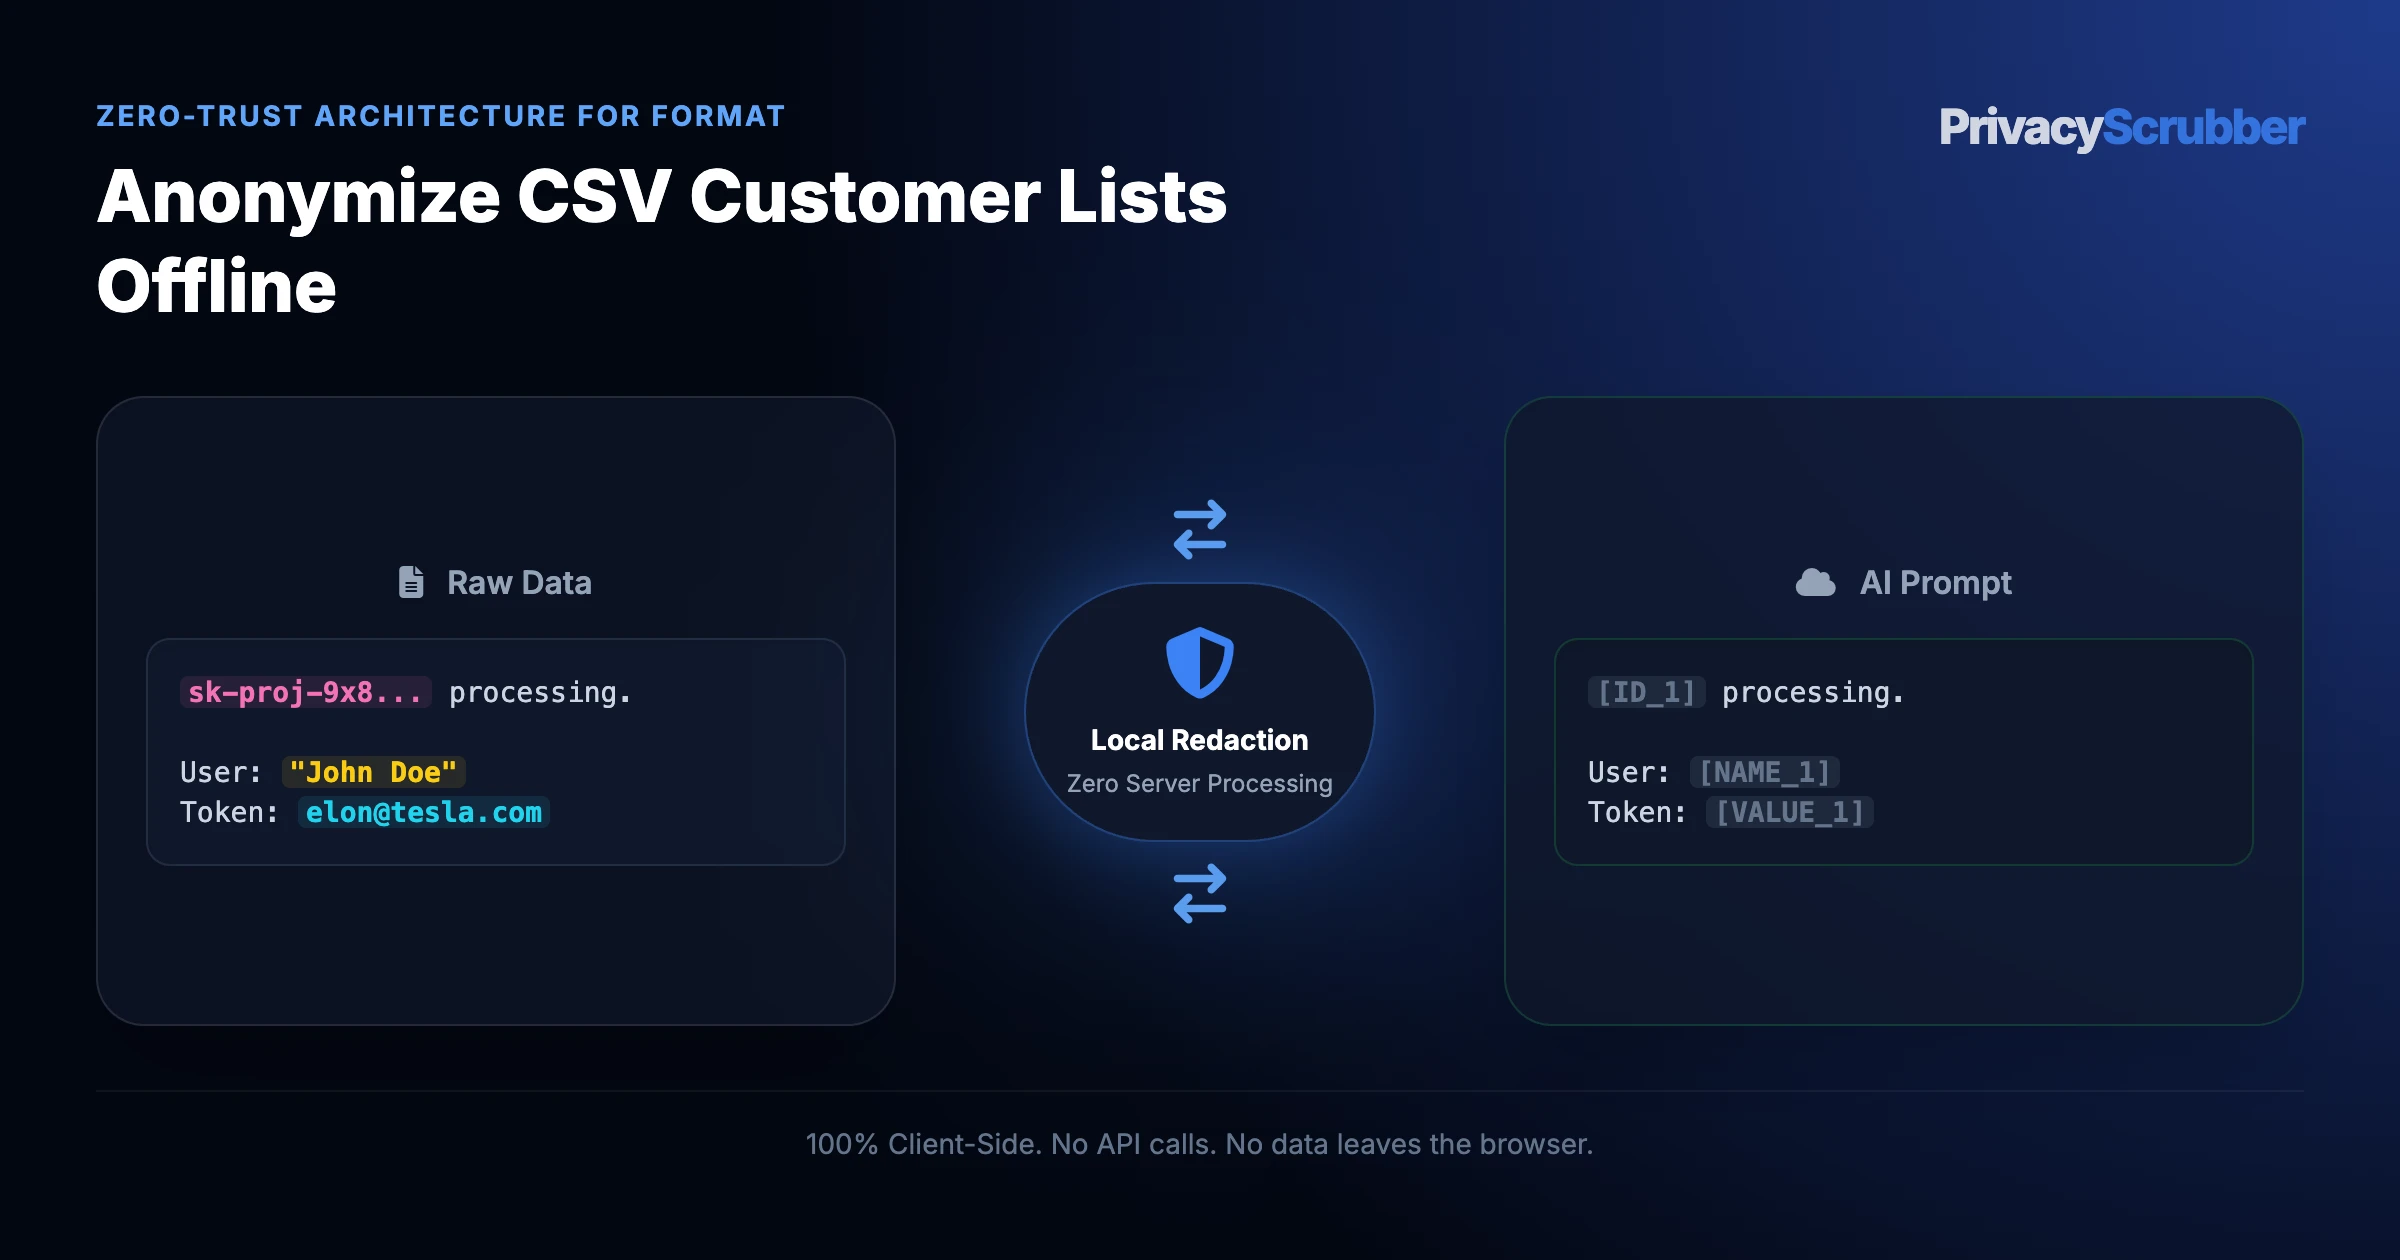
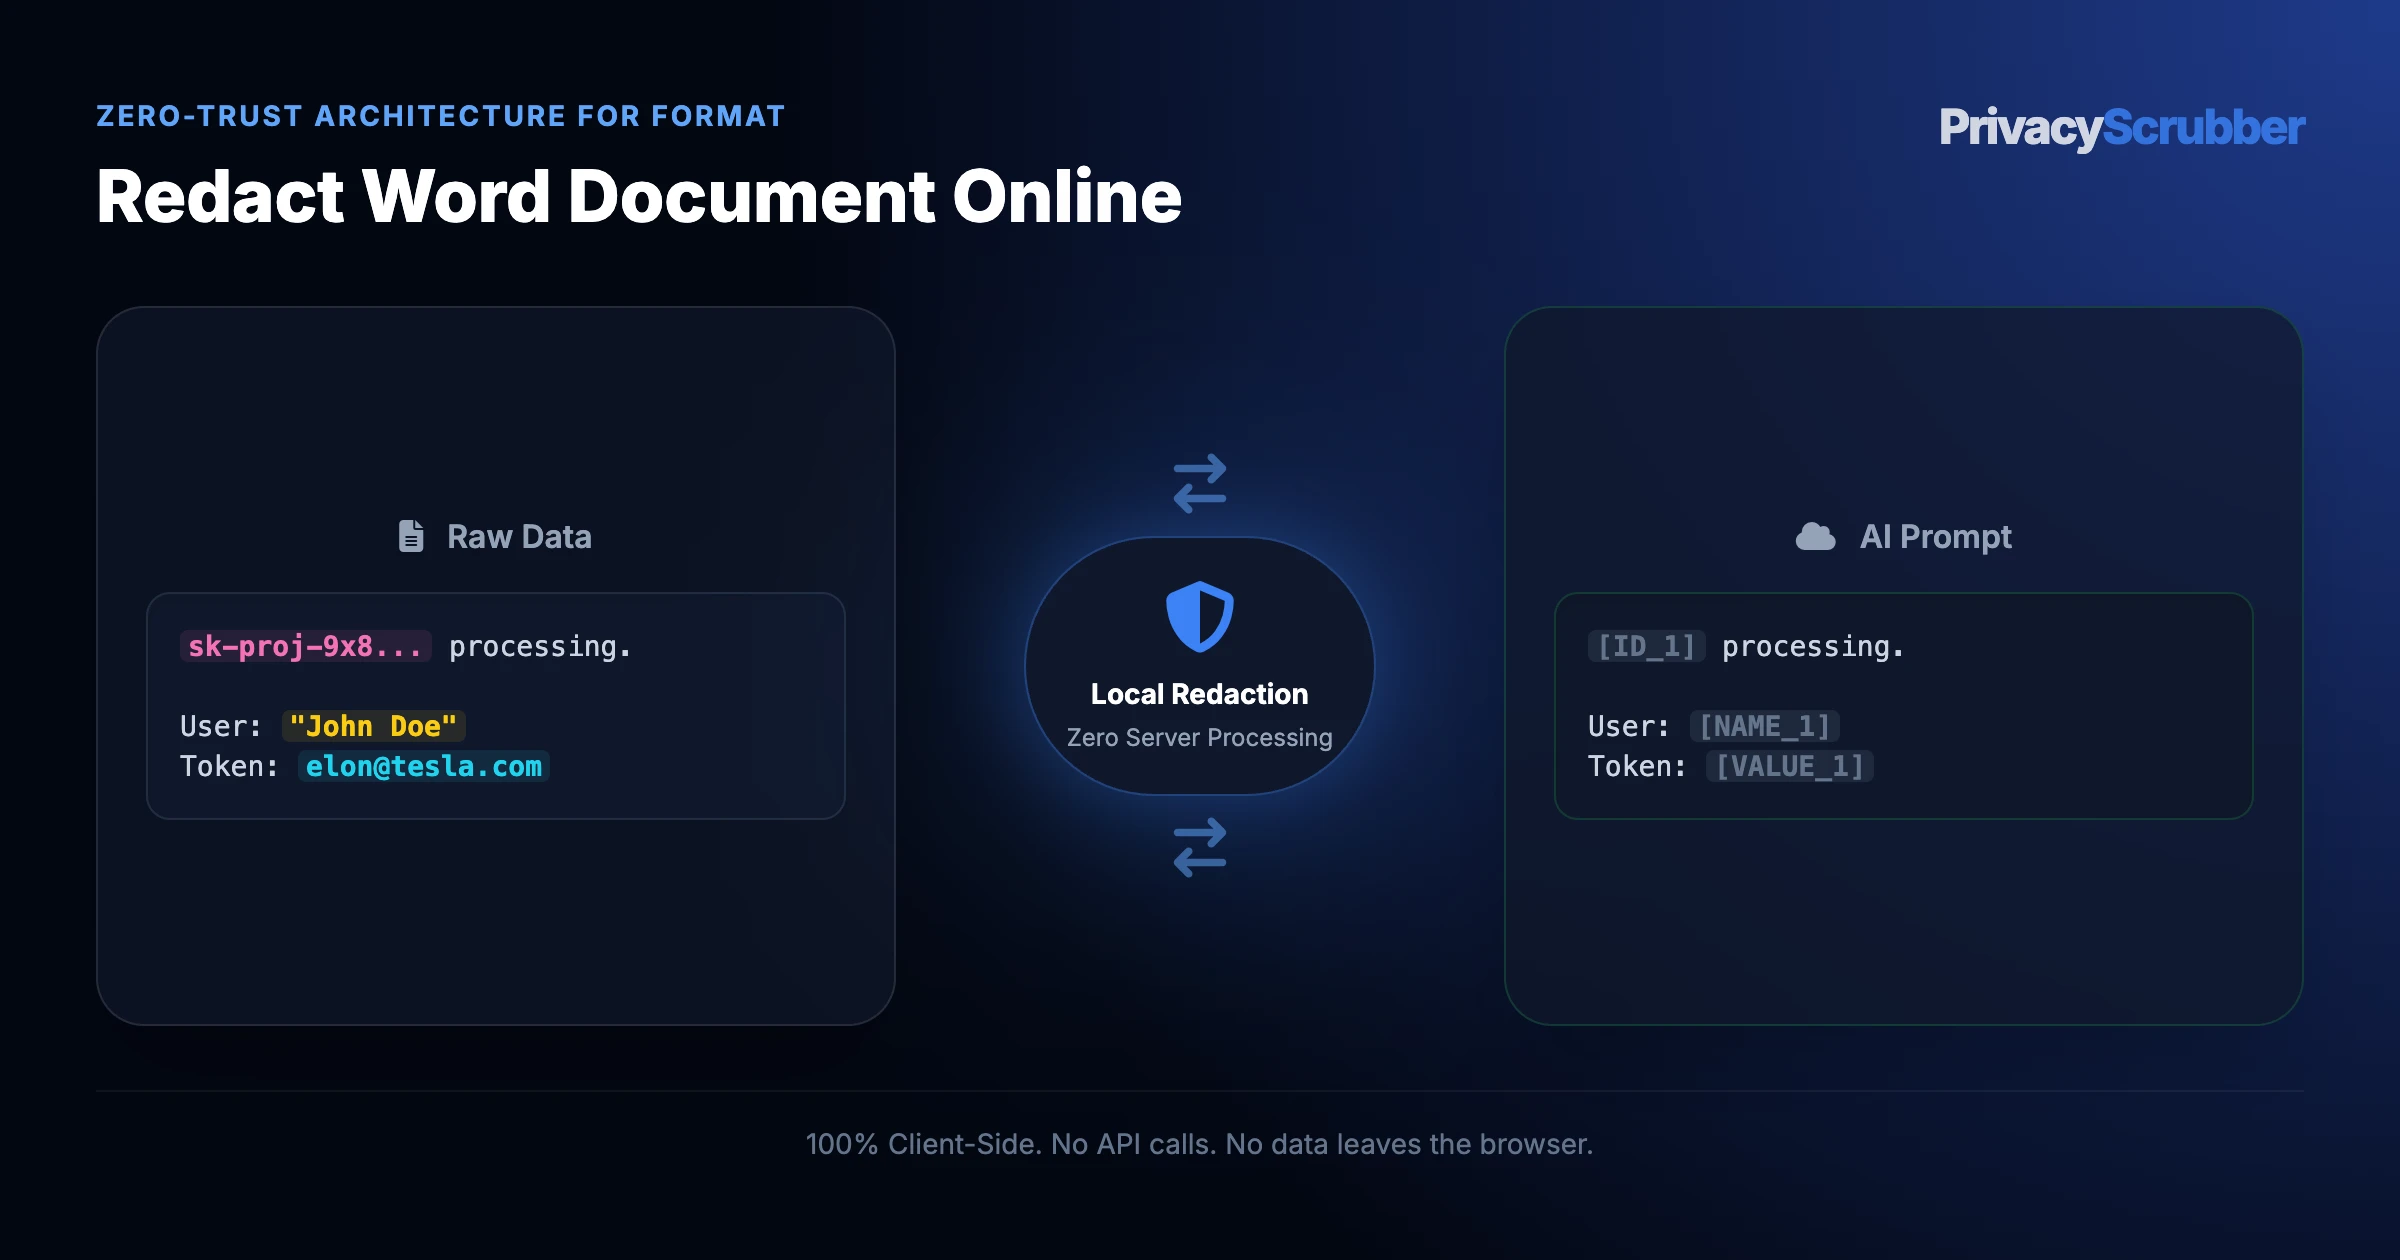
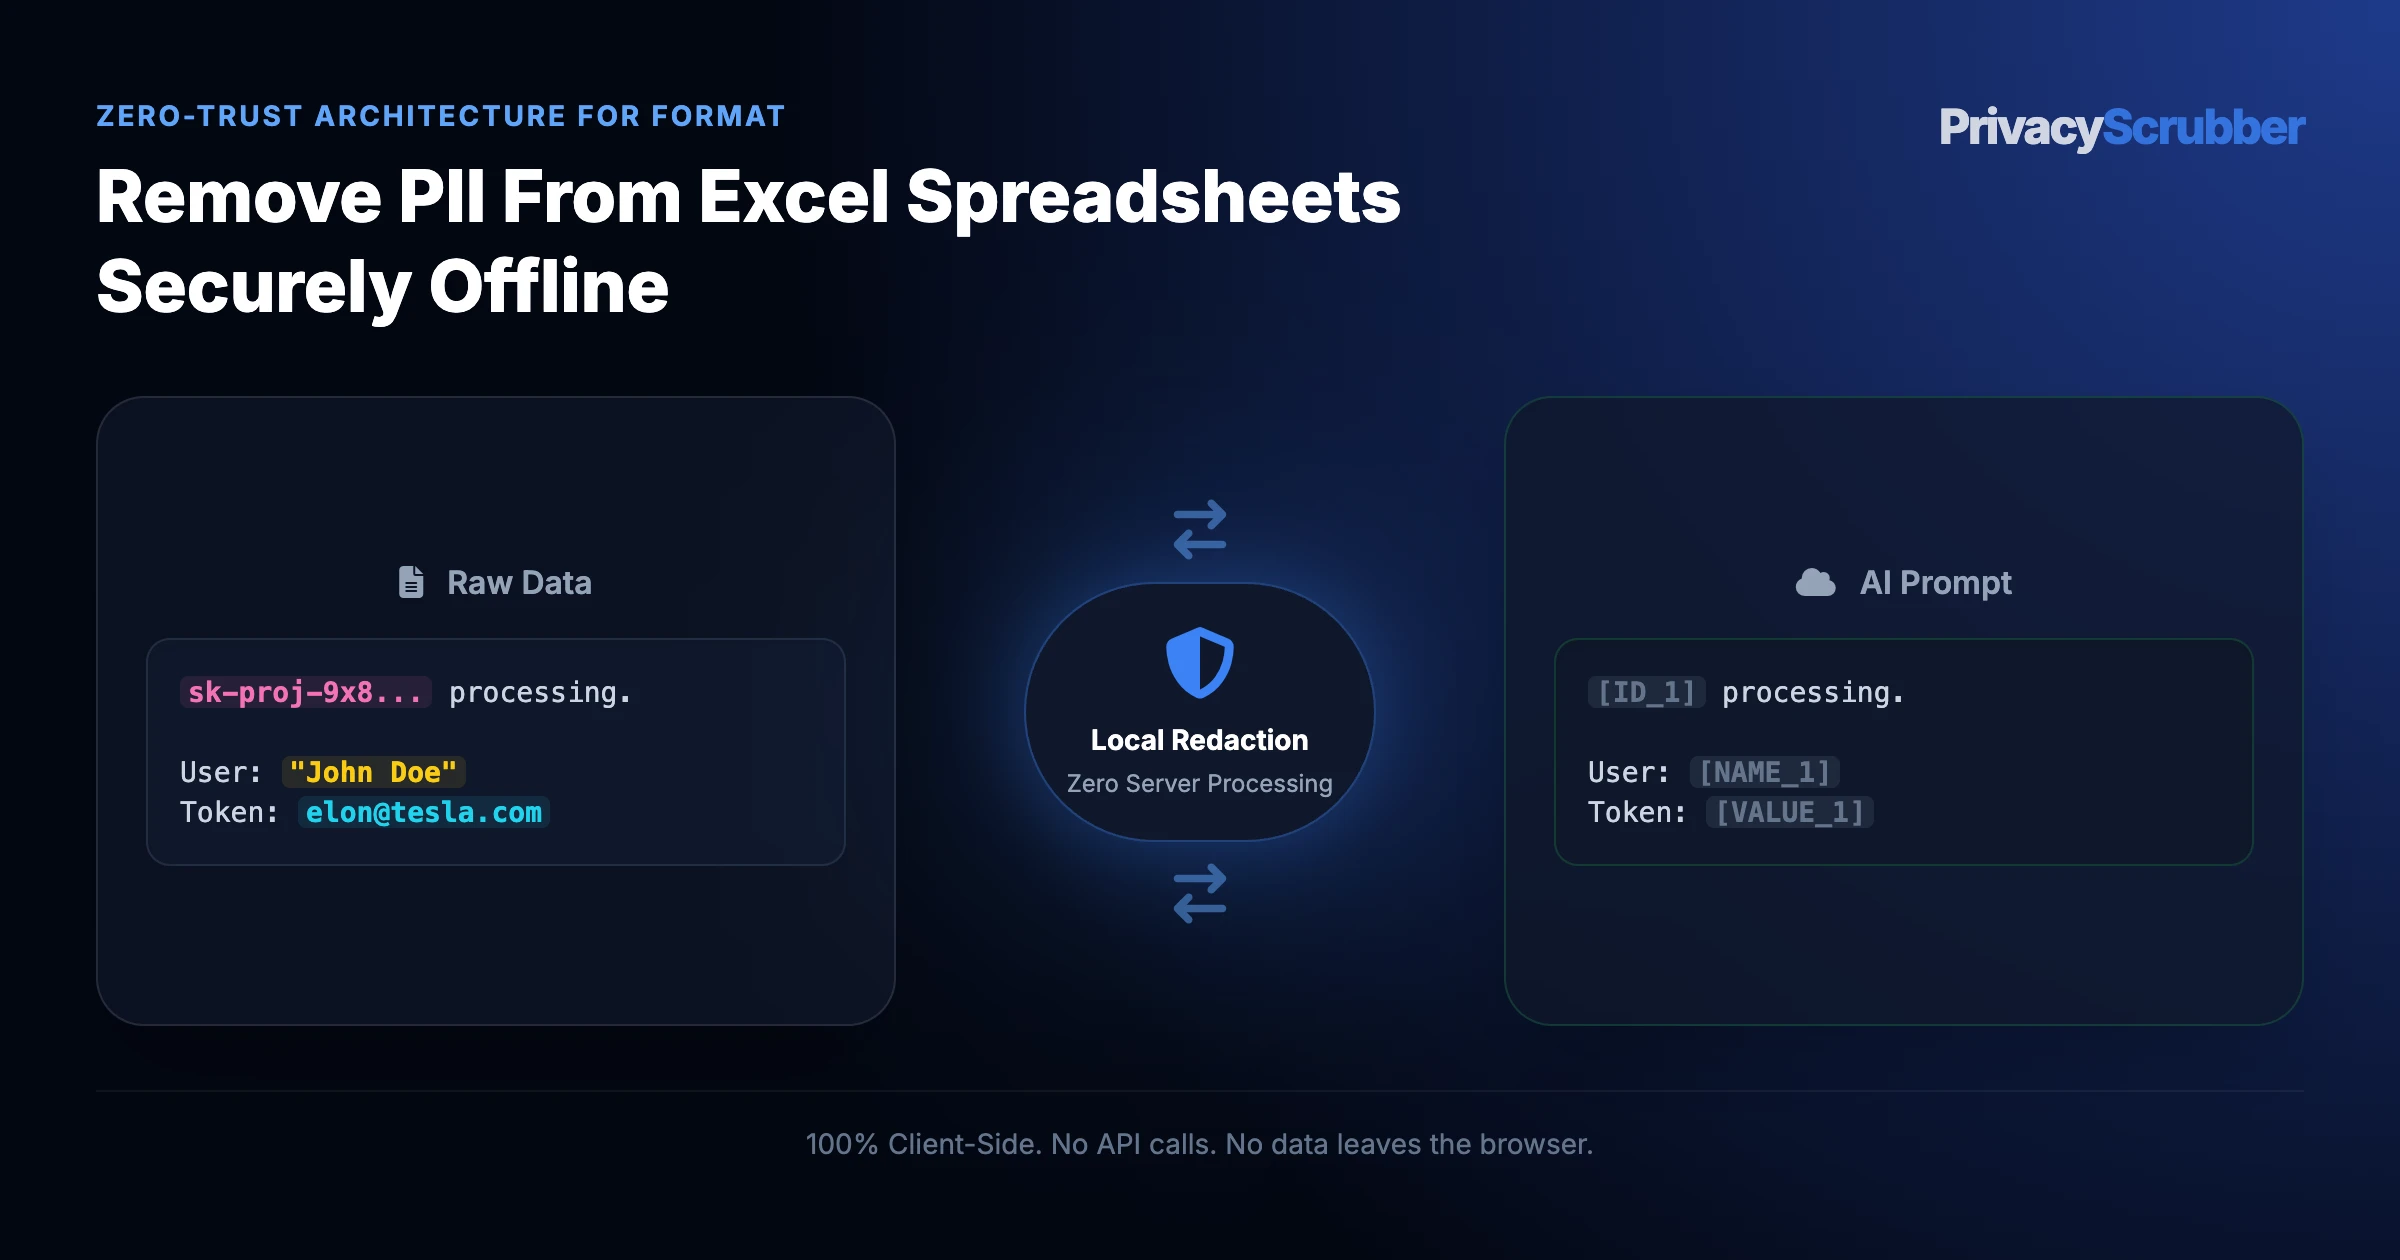
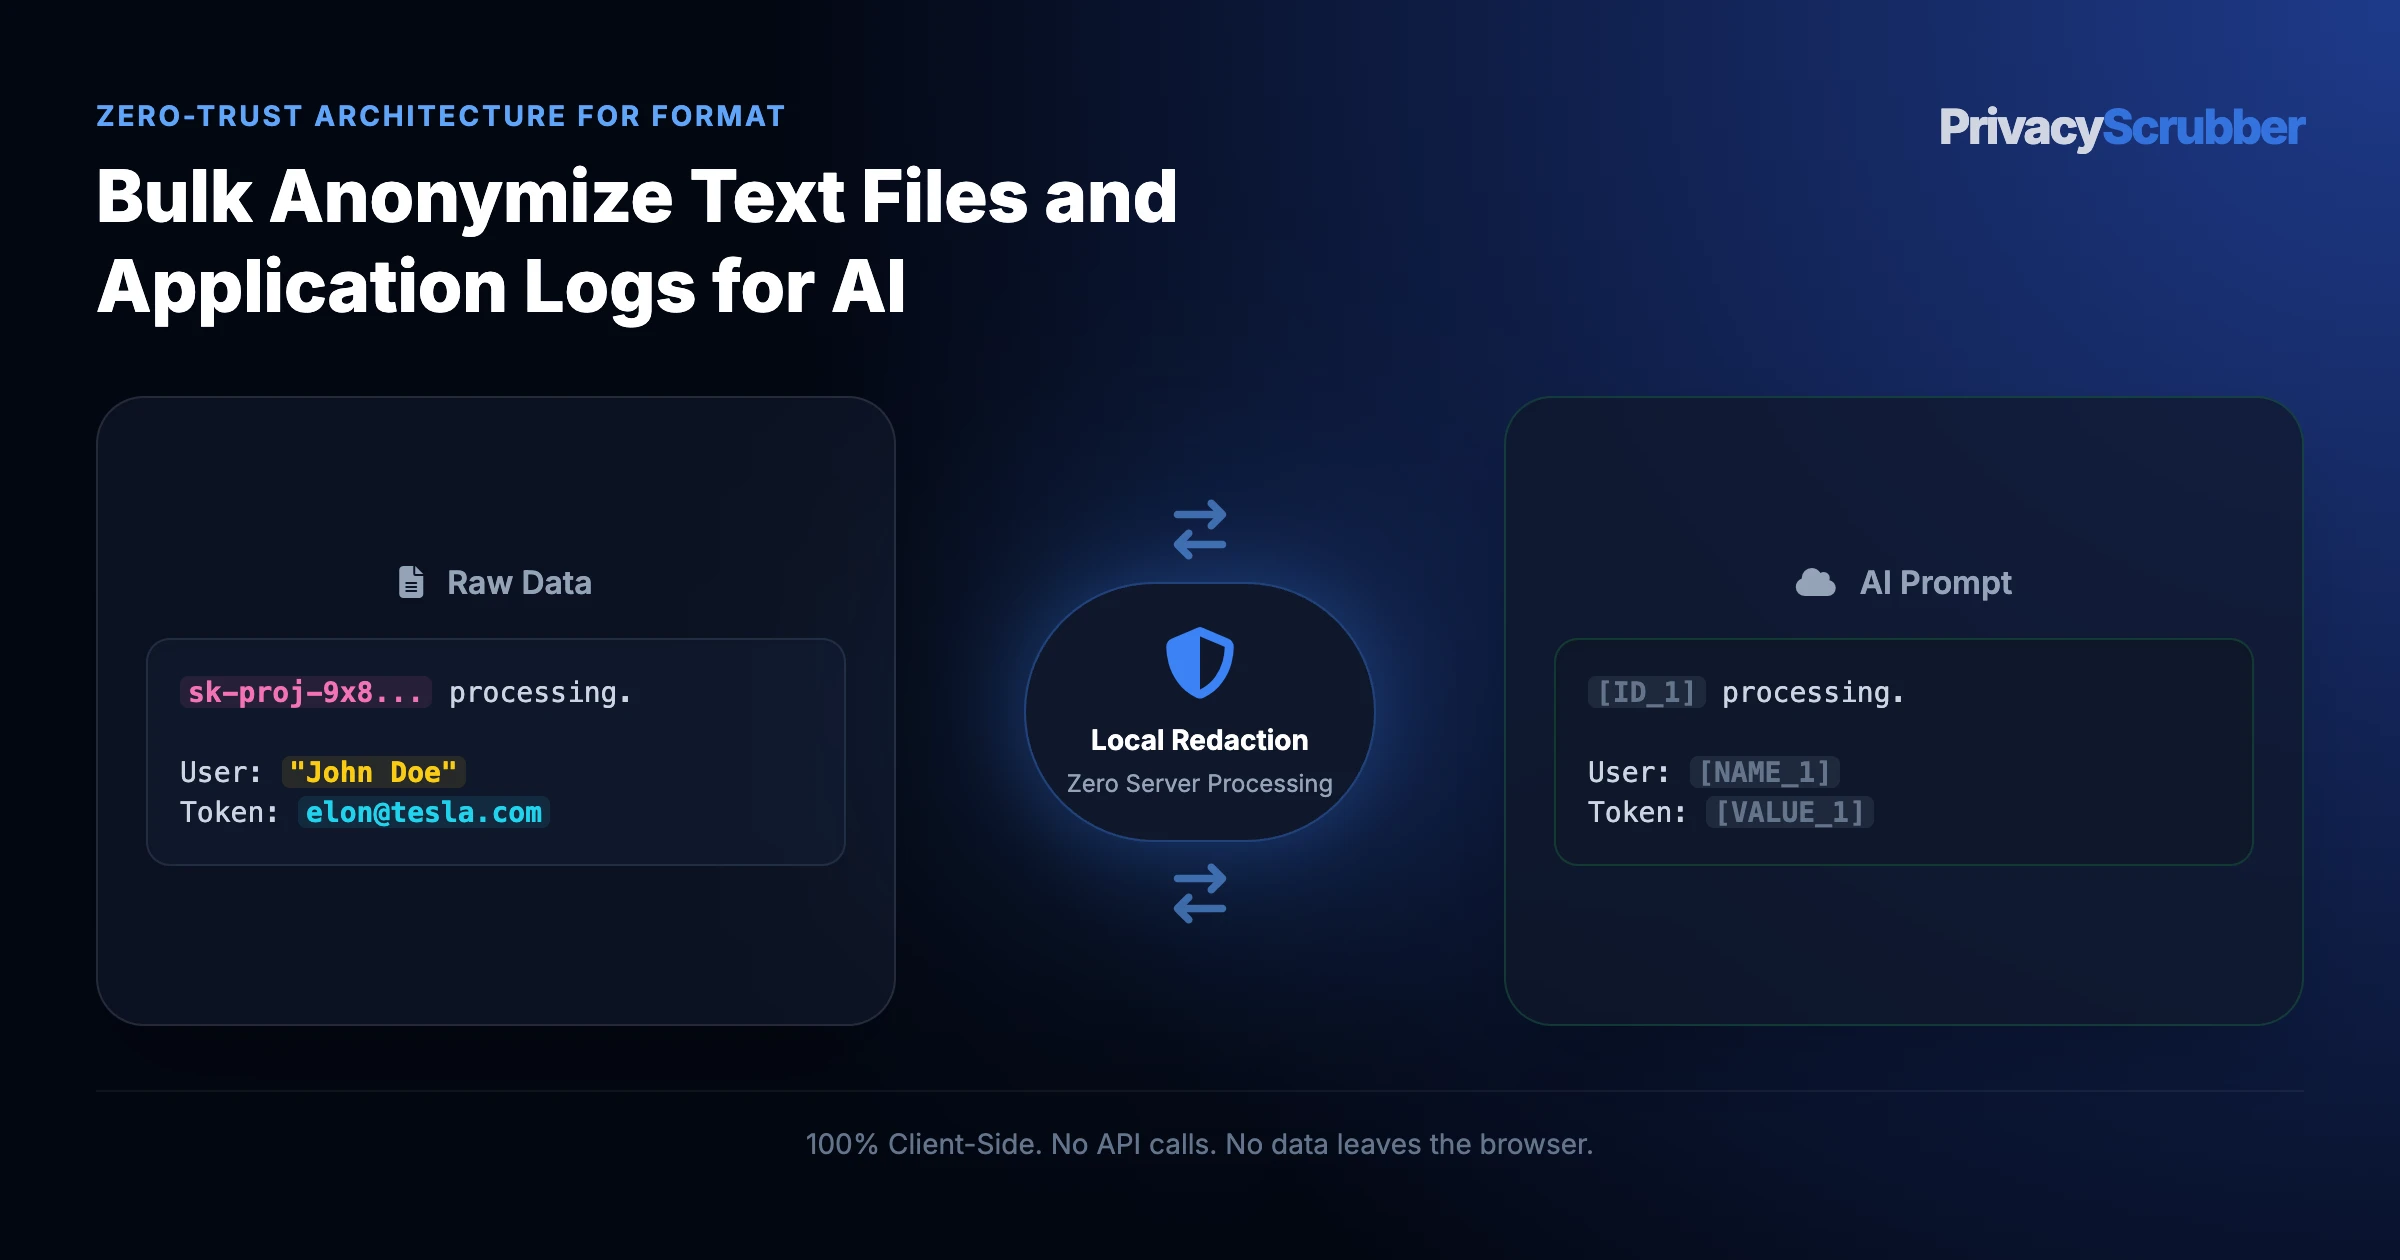
"PrivacyScrubber provides the essential de-identification layer for Format professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Format data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Scrubbing massive datasets?
Process thousands of records locally with Batch Mode.
Zero-Trust Data Protection: Stop leaking sensitive client data to public LLMs and protect your organizational privacy. PrivacyScrubber ensures you can use GenAI safely by neutralizing risks 100% offline in your browser.
What Data Analysts and Engineers Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
Achieving verifiable privacy for Anonymize CSV Customer Lists Offline prevents catastrophic dataset exfiltration when querying large language models. Integrating ChatGPT Advanced Data Analysis, Claude Projects, and programmatic ML pipelines for batch document review or tabular analysis without client-side masking leaves enterprise repositories exposed. Our format AI privacy guides details the client-side architecture required to tokenize high-risk files locally, resolving accidentally including hidden columns in Excel or nested PII in JSON payloads when uploading files directly to Advanced Data Analysis tools before any API request is formed.
When analysts upload bulk CSV customer databases or multi-page PDF records into third-party AI assistants, every unmasked row constitutes a compliance risk. Standard cloud DLP proxies often fail to parse nested document objects or require unencrypted transit to remote servers. For data analysts, data scientists, machine learning engineers, and developers, sending raw file buffers to external AI services creates an immediate compliance gap. Batch anonymize CSV customer lists in your browser. Protect client databases and customer PII before running AI-driven segmentation and marketing analytics.
Why Data Governance Teams Flag Unmasked AI Prompts
Under GDPR requirements for processing datasets, and SOC 2 criteria regarding data handling in transit, transmitting unmasked bulk records or sensitive document archives to third-party neural networks constitutes unauthorized data sharing. Resolving this liability requires adopting the local sanitization patterns in redact word document online. Verifiable compliance demands that all identifying cell values and document text be tokenized prior to API transmission. Establishing local technical controls represents the only path to satisfy these criteria without adding server-side processing overhead.
Using our client-side Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber processes files locally in your browser window with zero server transmission.
How to Use AI on Real Structured and Document Data — Without Sending a Single Real Name
Using our client-side Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber processes files locally in your browser window with zero server transmission. The WebAssembly parser extracts text from spreadsheets, PDFs (with local OCR for scanned pages), and Word documents, replacing sensitive strings with anonymous tokens before cloud transit. This aligns with enterprise bulk processing, enabling secure AI-assisted data modeling. The PrivacyScrubber Chrome Extension integrates natively into ChatGPT, Claude, and Gemini to automate the prompt-sanitization and response-restoration loop directly within the active editor. Processing data through browser-based Named Entity Recognition allows safe integration of ChatGPT Advanced Data Analysis, Claude Projects, and programmatic ML pipelines for complex tasks while preserving client privacy.
Our local processing model is independently verifiable through the Airplane Mode Standard. Disconnect from the network and sanitize complex spreadsheets or PDF files locally. The entire operation completes in RAM without dispatching outbound packets, conforming to the benchmarks in verifiable data sanitization for verifiable data sovereignty.
Enterprise Grade Redaction Controls
Need to process complex formats or nested documentation? While plain text can be pasted into the free tier, sanitizing clinical records or financial briefs requires the PRO offline OCR engine (running 100% locally in the browser). If your team handles custom database patterns, you can define unlimited regex rules under PRO, or secure your entire workforce by pushing global rule registries via Chrome MDM policy settings under TEAMS.
Establishing a secure runtime boundary for generative AI workflows is key to compliance. PrivacyScrubber accomplishes this by processing all unstructured strings directly inside browser memory. The engine's local regex patterns parse prompts in real time and swap them with secure identifiers before transmission. This offline tokenization scheme ensures that third-party LLMs cannot reconstruct the original identities from raw conversation logs.
Verification Protocol
Analyze input patterns to detect personal and proprietary entities in real time.
Apply local Named Entity Recognition to tokenize primary identifiers.
Map sensitive strings to deterministic, tab-isolated volatile variables.
Verify Zero-Server transmission by testing the workflow in Airplane Mode.
Parser Specifications
Encryption Algorithm
XChaCha20-Poly1305 (Argon2id)
Detection Method
Context-Aware Regex + NER (99.9% Accuracy)
Data Egress Rule
Zero-Server Egress (Airplane Mode Verifiable)
Classification Standard
Maximum Privacy Guard
Associated Threat Level
Low (Inference Risk)
Instant Simulation
Anonymize CSV Customer Lists Offline Sanitizer
Watch our zero-trust engine neutralize sensitive identifiers 100% locally. No data ever leaves your device.
Local processing 0 Server logs
ZTDS_ENGINE_V1.5.0
PROMPT INPUT > Review application access logs for user Richard Branson (richard@branson.co.uk), phone number: 555-0111.
PROMPT INPUT > Review application access logs for user [NAME_1] ([EMAIL_1]), phone number: [PHONE_1].
Format Detection Profile
Our zero-trust engine is pre-hardened for Format workflows, automatically identifying and tokenizing the following parameters 100% locally.
FILE_NAME
Active Protection
CELL_DATA
Active Protection
METADATA
Active Protection
COLUMN_ID
Active Protection
AUTHOR
Active Protection
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with verifiable data sanitization.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
ChatGPT Data Analysis & Claude Analytics Integration
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT Data Analysis & Claude Analytics:
Act as a senior data analyst. Analyze the following sanitized tabular dataset for [ORG_1]:
1. Calculate revenue distribution, cohort churn rates, and growth velocity metrics across segments.
2. Identify the top 3 outlier data clusters and generate formatted summary tables.
3. Provide executable Python (pandas) and SQL code for automated reporting.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Retain all column token headers ([CUSTOMER_1], [ACCOUNT_ID_1], [BALANCE_1]) exactly as provided for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT Data Analysis & Claude Analytics outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: GDPR Article 25 & 32 (Data Protection by Design & by Default)SheetJS WebAssembly parses rows and columns strictly in browser memory. Personal data columns are tokenized without distorting mathematical formulas.
Format Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
Zero-Trust Verified
Security teams deploy client-side sanitization to keep outbound AI prompts free of sensitive organizational data, avoiding complex multi-party DPA negotiations.
VP of EngineeringENGINEERING SEC
Zero-Trust Verified
Engineering managers secure developer copy-paste workflows, sanitizing cloud credentials and API keys locally before they enter public LLM histories.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Format compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any format text, click Protect PII. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in peer-reviewed repositories and persistent academic archives:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Format Teams.
Does protecting data with PrivacyScrubber before AI processing satisfy GDPR requirements for processing datasets?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with GDPR requirements for processing datasets because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for format workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match format-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask format data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your format data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Protect PII" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard Named Entity Recognition (NER) model to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
What Data Analysts and Engineers Send to AI — and What They Should Be Sending InsteadWhy Data Governance Teams Flag Unmasked AI Prompts
Under GDPR requirements for processing datasets, and SOC 2 criteria regarding data handling in transit, transmitting unmasked bulk records or sensitive document archives to third-party neural networks constitutes unauthorized data sharing. Resolving this liability requires adopting the local sanitization patterns in redact word document online. Verifiable compliance demands that all identifying cell values and document text be tokenized prior to API transmission. Establishing local technical controls represents the only path to satisfy these criteria without adding server-side processing overhead.
How to Use AI on Real Structured and Document Data — Without Sending a Single Real Name
Using our client-side Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber processes files locally in your browser window with zero server transmission. The WebAssembly parser extracts text from spreadsheets, PDFs (with local OCR for scanned pages), and Word documents, replacing sensitive strings with anonymous tokens before cloud transit. This aligns with enterprise bulk processing, enabling secure AI-assisted data modeling. The PrivacyScrubber Chrome Extension integrates natively into ChatGPT, Claude, and Gemini to automate the prompt-sanitization and response-restoration loop directly within the active editor. Processing data through browser-based Named Entity Recognition allows safe integration of ChatGPT Advanced Data Analysis, Claude Projects, and programmatic ML pipelines for complex tasks while preserving client privacy.
Is PrivacyScrubber safe for anonymize csv offline, scrub csv customer list, protect csv data ai, batch csv anonymizer, mask customer data csv?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with anonymize csv offline, scrub csv customer list, protect csv data ai, batch csv anonymizer, mask customer data csv, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for format?
Our engine includes 22+ built-in industry profiles optimized for format data. Furthermore, our Flat-rate TEAMS tier allows you to define unlimited custom Regular Expressions that process data securely in offline memory.