
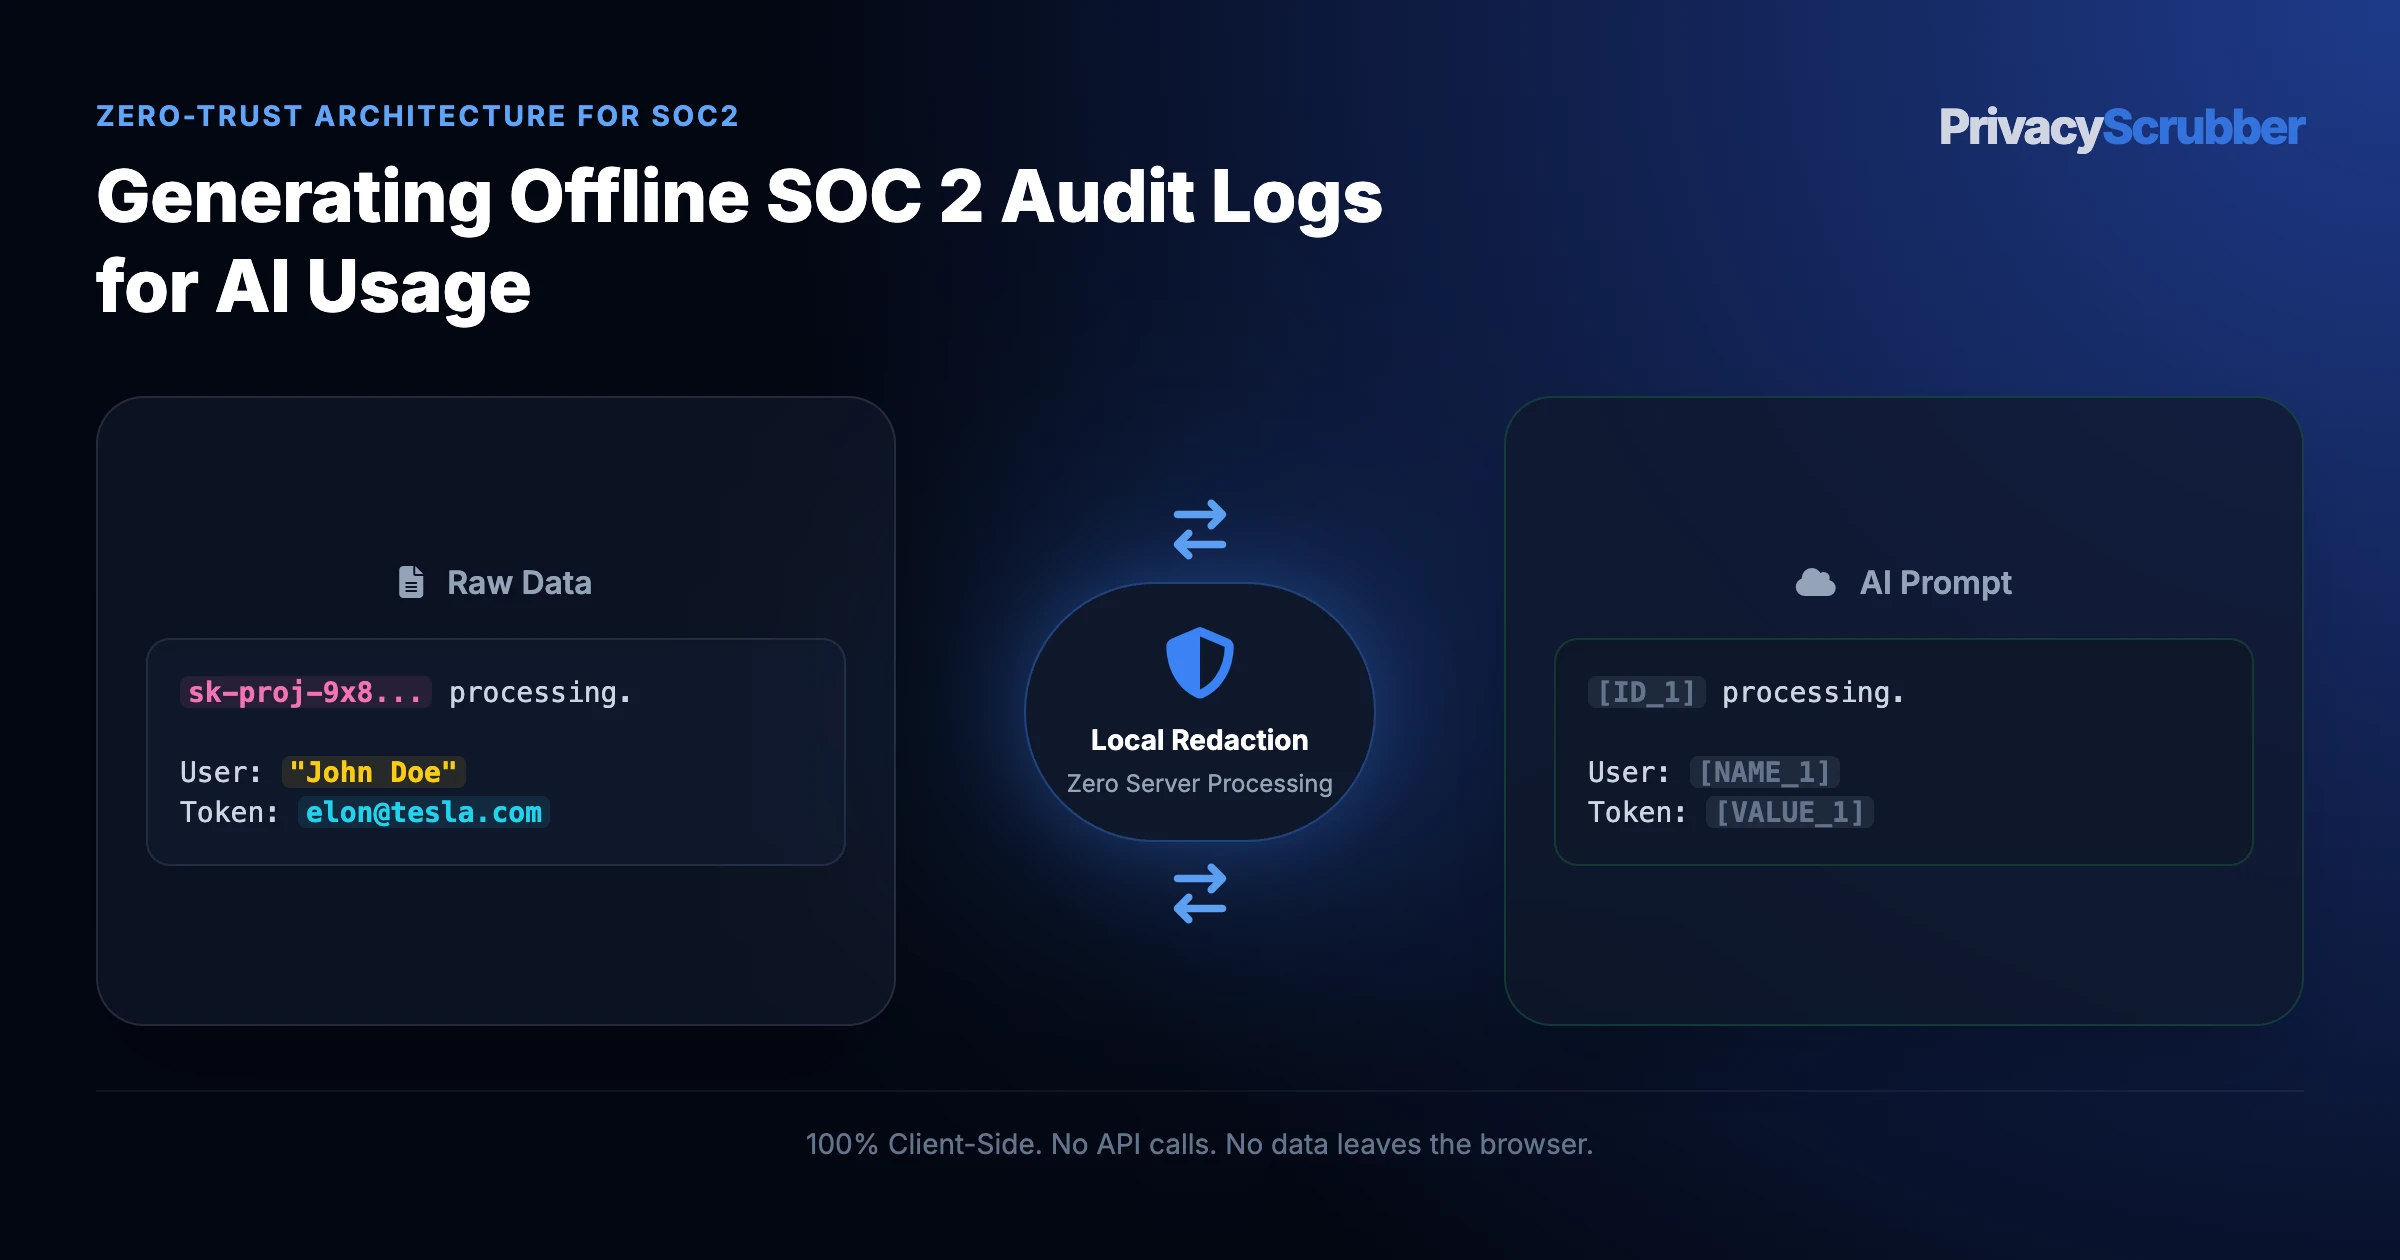
Compliance teams documenting AI governance frequently aggregate prompt telemetry, employee user IDs, and verification receipts for external SOC 2 Type II audits. Transmitting raw audit evidence to centralized SaaS tracking portals or third-party log aggregators introduces secondary data breach surfaces and expands compliance scope. Decentralized, zero-server audit logging proves technical control enforcement with zero cloud transit.
What Infosec and Audit Teams Send to AI During Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud
High-compliance SOC 2 teams prevent SOC 2 Type II Trust Service Criteria (Privacy and Security) egress gaps on Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud using client-side browser ZTDS shield; SOC 2 AI privacy guides cover prevent soc 2 log cloud leak isolation into [CUSTOMER_1].
Routing stop compliance audit network leakage payloads across Vanta exposes CTOs under SOC 2 Type II Trust Service Criteria (Privacy and Security). Prevent auditor evidence logs and compliance trails from leaking to external clouds. 100% in-RAM sanitization under SOC 2 CC6.1 & CC6.7 requirements. Converting identifiers to [CUSTOMER_1] in RAM fixes root risk.
Pre-Prompt Sanitization for Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud
Defending Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud under SOC 2 Type II Trust Service Criteria (Privacy and Security) requires eliminating SOC 2 Type II Trust Service Criteria (Privacy and Security) egress gaps at keyboard or node level. Local browser ZTDS shield tokenizes stop compliance audit network leakage to [ID_1] without touching remote clouds.
Distributed teammates can seal prevent soc 2 log cloud leak maps via XChaCha20-Poly1305 handoffs in TEAMS, letting remote CTOs unlock [CUSTOMER_1] without central storage.
Pre-Inference Redaction Matrix: SOC 2 Type II System Audit Trail, IAM Access Log & Compliance Evidence Export
Use the classification table below to separate high-liability SOC 2 Type II System Audit Trail, IAM Access Log & Compliance Evidence Export attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Auditor & Engineer Full Legal Names | REDACT | [NAME_1], [NAME_2] | Direct individual staff identities linking access actions to specific personnel |
| Corporate Work Email Addresses & IAM Usernames | REDACT | [EMAIL_1], [EMAIL_2] | Privileged internal IAM identity credentials vulnerable to targeted phishing or credential stuffing |
| Internal Corporate IPv4/IPv6 Addresses | REDACT | [IP_1], [IP_2] | Internal network topology addresses exposing corporate bastion and VPC architecture |
| Employee Personnel Badge & Directory IDs | REDACT | [ID_1], [ID_2] | HR employee IDs linking machine logs to employee HR records |
| SOC 2 Trust Services Criteria Control Identifiers | PRESERVE | Cleartext (CC6.1, CC6.6, CC6.7, CC7.2) | Standard AICPA audit control frameworks required for evidence gap mapping |
| Cloud IAM API Actions & Resource Methods | PRESERVE | Cleartext (sts:AssumeRole, s3:PutBucketPolicy, iam:CreateAccessKey) | Exact cloud operational event verbs required for privileged access analysis |
| Audit Event ISO Timestamps & Request IDs | PRESERVE | Cleartext (2026-09-30T10:14:22Z, req-984210a) | Temporal markers and request identifiers necessary for chronological audit reconciliation |
| Policy Decision Outcomes & Access Status Codes | PRESERVE | Cleartext (Success, AccessDenied, MFA_Enforced) | Security policy evaluation states required to verify control enforcement effectiveness |
Copy-Paste Safe Instruction for SOC 2 Type II System Audit Trail, IAM Access Log & Compliance Evidence Export
Submit this prompt wrapper with your masked SOC 2 Type II System Audit Trail, IAM Access Log & Compliance Evidence Export input so the AI reasons over symbolic tokens without altering placeholder tags:
You are a Principal SOC 2 Compliance Lead and Certified Information Systems Auditor (CISA). Review the following sanitized cloud audit trail export where auditor and staff identities, work emails, employee IDs, and internal IP addresses have been tokenized ([NAME_1], [NAME_2], [EMAIL_1], [EMAIL_2], [IP_1], [IP_2], [ORG_1], [ID_1], [ID_2], [ID_3], [ID_4]).

Tasks:
1. Assess compliance against SOC 2 CC6.1 (Privileged Access) for the assumed role event with MFA verification.
2. Evaluate the security posture and policy enforcement of the failed s3:PutBucketPolicy event under CC6.7.
3. Prepare a formal audit working paper summary verifying that access controls operated effectively without exposing internal corporate identities or IP layouts.

[PASTE SANITIZED TEXT HERE]
You are a Principal SOC 2 Compliance Lead and Certified Information Systems Auditor (CISA). Review the following sanitized cloud audit trail export where auditor and staff identities, work emails, employee IDs, and internal IP addresses have been tokenized ([NAME_1], [NAME_2], [EMAIL_1], [EMAIL_2], [IP_1], [IP_2], [ORG_1], [ID_1], [ID_2], [ID_3], [ID_4]).

Tasks:
1. Assess compliance against SOC 2 CC6.1 (Privileged Access) for the assumed role event with MFA verification.
2. Evaluate the security posture and policy enforcement of the failed s3:PutBucketPolicy event under CC6.7.
3. Prepare a formal audit working paper summary verifying that access controls operated effectively without exposing internal corporate identities or IP layouts.

[PASTE SANITIZED TEXT HERE]
How Infosec and SOC 2 Audit Leads Enforce Zero-Egress on Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud
Strict SOC 2 Type II Trust Service Criteria (Privacy and Security) mandates leave no margin for SOC 2 Type II Trust Service Criteria (Privacy and Security) egress gaps. Combining Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud workflows with SOC 2 AI vendor risk management keeps redact auditor evidence offline off Vanta.
Local Tokenization Architecture: Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud
Deploying volatile memory engine traps Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud inputs locally, mapping stop compliance audit network leakage to [ID_1]; aligned with Confluence & Notion AI workspace PII redaction in browser RAM, Vanta never touches cleartext.
Transparent DevTools inspection proves Prevent SOC 2 Audit Trail & Evidence Log Leakage to Cloud sends zero prevent soc 2 log cloud leak packets externally, backing secure board meeting AI and SOC 2 Type II Trust Service Criteria (Privacy and Security).
