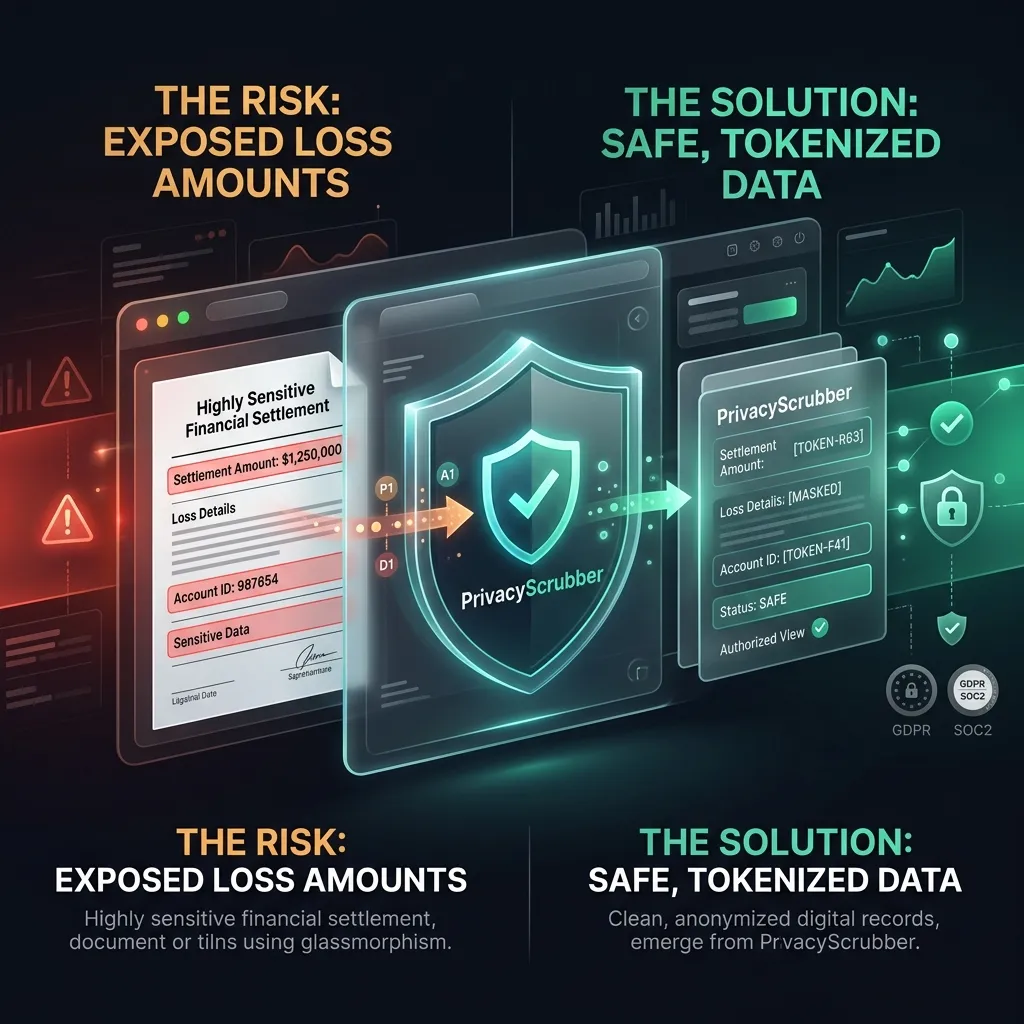
Anonymize Loss Amounts and Settlement Reserves: Anonymize loss amounts and settlement reserves to protect corporate financials in AI tools. Flat-rate TEAMS pricing available.
Ilya SibiryakovPrivacy Architect••3 min read
100% Local Airplane Mode
Actuarial Loss Run Report & Case Reserve Ledger Property & Casualty Actuaries, Reinsurance Underwriters & Risk Managers Confidentiality of Work Product, Actuarial Standards of Practice (ASOP 43) & GLBA
Direct Technical Standard (Zero-Trust Rule)
Sanitizing actuarial loss runs and settlement reserve ledgers for AI analysis requires redacting specific claimant names, attorney law firm identities, claim reference numbers, and litigation case captions, while preserving paid losses, case reserves, Incurred But Not Reported (IBNR) totals, and policy year loss ratios in cleartext. Local client-side processing prevents disclosing strategic reserve figures to opposing trial counsel.
AI Summary / Key Takeaways
Verified Zero-Trust Logic
"PrivacyScrubber provides the essential de-identification layer for Insurance professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Insurance data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
Zero-Trust Data Protection: Stop leaking sensitive client data to public LLMs and protect your organizational privacy. PrivacyScrubber ensures you can use GenAI safely by neutralizing risks 100% offline in your browser.
What Insurance Professionals Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
Understanding Anonymize Loss Amounts and Settlement Reserves is more important than ever. If you're one of the many claims adjusters, underwriters, and agency it directors utilizing AI tools like Generative AI chatbots and claims management software in your daily life, you might be sharing more than you realize. Our insurance AI privacy guides help you enjoy the benefits of AI without losing your privacy. The main concern: leaking policyholder PII and proprietary loss reserves in un-redacted AI summaries.
Pasting text into chat interfaces without local redaction creates a persistent record. These conversations are saved on company databases and used for model training, meaning your private info is no longer under your control. Anonymize loss amounts and settlement reserves to protect corporate financials in AI tools. Flat-rate TEAMS pricing available.
Why Insurance Compliance Teams Flag Unmasked AI Prompts
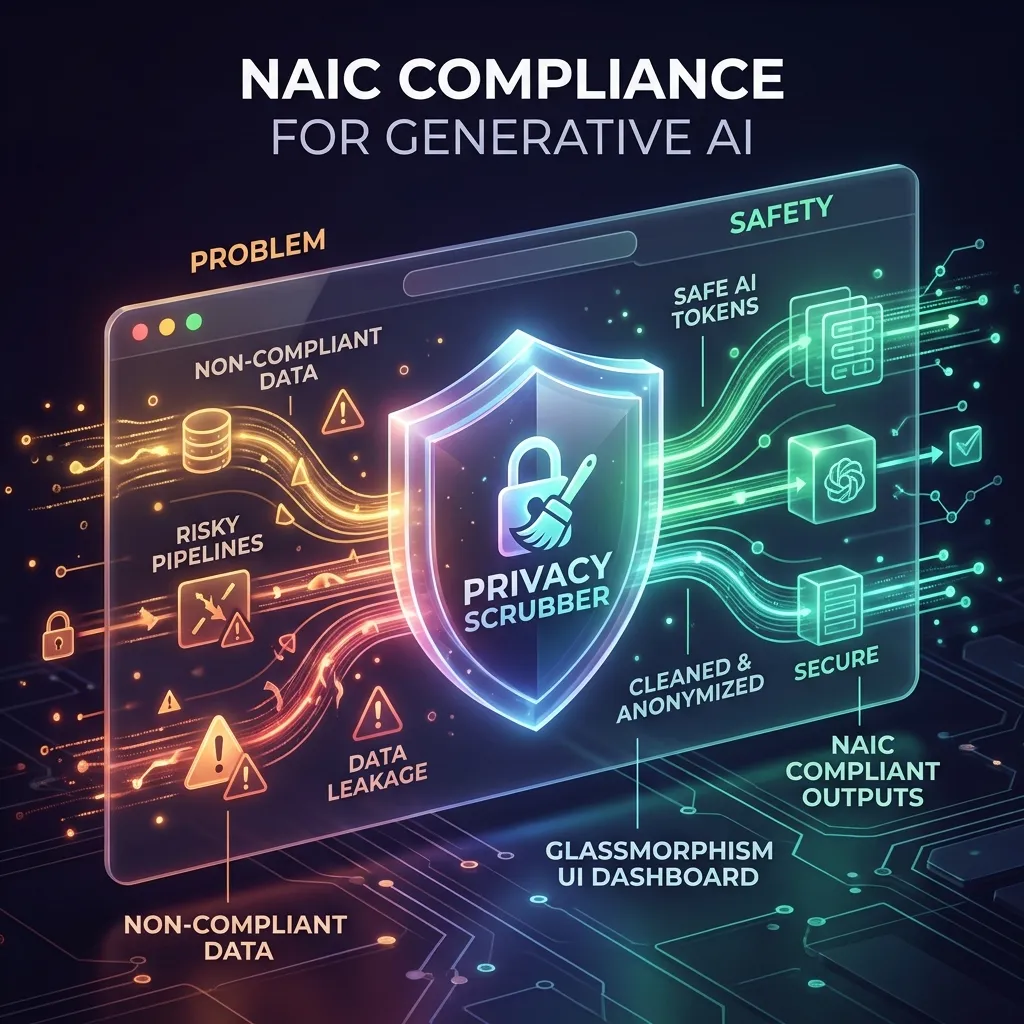
Although privacy laws like NAIC Insurance Data Security Model Law exist, they rarely prevent AI companies from keeping your chat logs. Understanding the ideas in naic compliance for generative ai usage is essential for securing your digital life. The best solution is masking your personal info before it leaves your machine. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
Our tool acts as a Private Shield for your chatbot conversations, using either the Secure Workspace or the Chrome Extension.
How to Use AI on Real Insurance Data — Without Sending a Single Real Name
Our tool acts as a Private Shield for your chatbot conversations, using either the Secure Workspace or the Chrome Extension. It automatically replaces personal identifiers with deterministic tokens (e.g., [NAME_1]) offline, ensuring the AI only processes clean context. This supports the compliance model of enterprise data governance. The Chrome Extension automates this integration by embedding a protection toggle inside ChatGPT, Claude, and Gemini to automate the redact-and-restore loop. Running Named Entity Recognition locally ensures that teams can continue using Generative AI chatbots and claims management software for daily queries without any third-party data collection.
Verify this offline capability through the Airplane Mode Verification. Disconnect from the internet and run a scrub. Since all operations run locally, this matches the standard in claims privacy standards, ensuring your personal data stays safe.
Zero-Trust Configuration & Threat Model
When users perform data analysis with AI assistants, unstructured prompts can easily leak confidential information to external servers. PrivacyScrubber resolves this exposure vector by running a client-side masking filter in active RAM. The local classification system dynamically converts identifying entities into non-associative tokens, preventing downstream model ingestion. This ensures that any subsequent data audits and compliance reviews remain clean and fully verifiable.
Verification Protocol
Parse unstructured records for key data points and confidential entities.
Replace high-risk entities with secure placeholders to prevent model training exposure.
Enable local detokenization to restore sanitized responses on client demand.
Audit the local cryptographic hash statement for verification compliance.
Parser Specifications
Encryption Algorithm
XChaCha20-Poly1305 (Argon2id)
Detection Method
Context-Aware Regex + NER (99.7% Accuracy)
Data Egress Rule
Zero-Server Egress (Airplane Mode Verifiable)
Classification Standard
High Privacy Guard
Associated Threat Level
High (Identity Exposure)
Your Private Shield
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with claims privacy standards.
Testing Your Safety
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
Compliance Decision Matrix
Field-by-Field Sanitization Rule for Actuarial Loss Run Report & Case Reserve Ledger
To maintain LLM analytical context while avoiding cloud data breaches, follow this deterministic mapping before submitting prompts to third-party AI models:
Document Field / Box
Required Action
Deterministic Token
Statutory & AI Rationale
Claimant & Injured Party Legal Names
REDACT
[NAME_1], [NAME_2]
Personal identity; subject to HIPAA and state insurance privacy safeguards
Discloses active court dockets vulnerable to public court scraping
Paid Loss & Legal Defense Incurred (ALAE)
PRESERVE
Cleartext (Paid: $125,000 / ALAE: $42,500)
Historical payout data essential for AI loss development triangle modeling
Open Case Indemnity Reserve Allocation
PRESERVE
Cleartext (Reserve: $350,000.00)
Required for actuarial ultimate loss estimation and IBNR calibration
Policy Accident Year & Valuation Date
PRESERVE
Cleartext (AY 2023, Evaluated as of 12/31/2025)
Mandatory cohort anchor required for age-to-age loss development factors
Loss Ratio & Earned Premium Baseline
PRESERVE
Cleartext (Loss Ratio: 64.2%, Earned: $2.4M)
Necessary for evaluating reinsurance treaty attachment points and pricing
1-Click Persona Prompt
Safe LLM Prompt Template for Actuarial Loss Run Report & Case Reserve Ledger
Copy and paste this structured prompt into ChatGPT, Claude, or Gemini alongside your tokenized text to prevent LLM rejection:
You are a Casualty Actuarial Pricing Analyst. Review the following sanitized loss run record where claimant identities, defense counsel firms, and court dockets are replaced with tokens ([ID_1], [ORG_1], [ORG_2], [NAME_1], [CASE_ID_1]).

Tasks:
1. Reconcile total incurred losses across paid indemnity, defense expenses, and case reserves.
2. Evaluate potential development toward the $1,000,000 excess reinsurance attachment point.
3. Recommend loss development factor (LDF) selections based on the AY 2023 maturity without seeking party identities.

[PASTE SANITIZED TEXT HERE]
You are a Casualty Actuarial Pricing Analyst. Review the following sanitized loss run record where claimant identities, defense counsel firms, and court dockets are replaced with tokens ([ID_1], [ORG_1], [ORG_2], [NAME_1], [CASE_ID_1]).

Tasks:
1. Reconcile total incurred losses across paid indemnity, defense expenses, and case reserves.
2. Evaluate potential development toward the $1,000,000 excess reinsurance attachment point.
3. Recommend loss development factor (LDF) selections based on the AY 2023 maturity without seeking party identities.

[PASTE SANITIZED TEXT HERE]
ChatGPT & Enterprise LLMs Integration
Step-by-Step Integration Guide: Anonymize Loss Amounts and Settlement Reserves
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT & Enterprise LLMs:
Zero-Trust Prompt Sanitization & AI Model InterceptionPrivacyScrubber ZTDS Protocol
Act as an executive research consultant. Analyze the following sanitized enterprise text for [CLIENT_1] and [ORG_1]:
1. Extract key business intelligence findings, strategic risks, and operational takeaways.
2. Draft 3 prioritized executive recommendations.
3. Format findings in clean, structured bullet points.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Maintain all cryptographic token placeholders ([NAME_1], [EMAIL_1], [ID_1]) exactly intact in your response for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT & Enterprise LLMs outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: Zero-Trust Data Sanitization (ZTDS) Architecture StandardRAM-only session tokenization guarantees zero data at rest and zero data in transit. Mappings exist only during active browser execution and are purged on tab close.
Insurance Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
Zero-Trust Verified
Security teams deploy client-side sanitization to keep outbound AI prompts free of sensitive organizational data, avoiding complex multi-party DPA negotiations.
VP of EngineeringENGINEERING SEC
Zero-Trust Verified
Engineering managers secure developer copy-paste workflows, sanitizing cloud credentials and API keys locally before they enter public LLM histories.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Insurance compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any insurance text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in peer-reviewed repositories and persistent academic archives:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Insurance Teams.
Does protecting data with PrivacyScrubber before AI processing satisfy NAIC Insurance Data Security Model Law?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with NAIC Insurance Data Security Model Law because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for insurance workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match insurance-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask insurance data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your insurance data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Sanitize Prompt" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard Named Entity Recognition (NER) model to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
Why Insurance Compliance Teams Flag Unmasked AI Prompts
Although privacy laws like NAIC Insurance Data Security Model Law exist, they rarely prevent AI companies from keeping your chat logs. Understanding the ideas in naic compliance for generative ai usage is essential for securing your digital life. The best solution is masking your personal info before it leaves your machine. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
How to Use AI on Real Insurance Data — Without Sending a Single Real Name
Our tool acts as a Private Shield for your chatbot conversations, using either the Secure Workspace or the Chrome Extension. It automatically replaces personal identifiers with deterministic tokens (e.g., [NAME_1]) offline, ensuring the AI only processes clean context. This supports the compliance model of enterprise data governance. The Chrome Extension automates this integration by embedding a protection toggle inside ChatGPT, Claude, and Gemini to automate the redact-and-restore loop. Running Named Entity Recognition locally ensures that teams can continue using Generative AI chatbots and claims management software for daily queries without any third-party data collection.
Is PrivacyScrubber safe for Anonymize loss amounts and settlement reserves to protect corporate financials in AI tools.?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with Anonymize loss amounts and settlement reserves to protect corporate financials in AI tools., no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for insurance?
Our engine includes 30 specialized industry profiles optimized for insurance data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.