
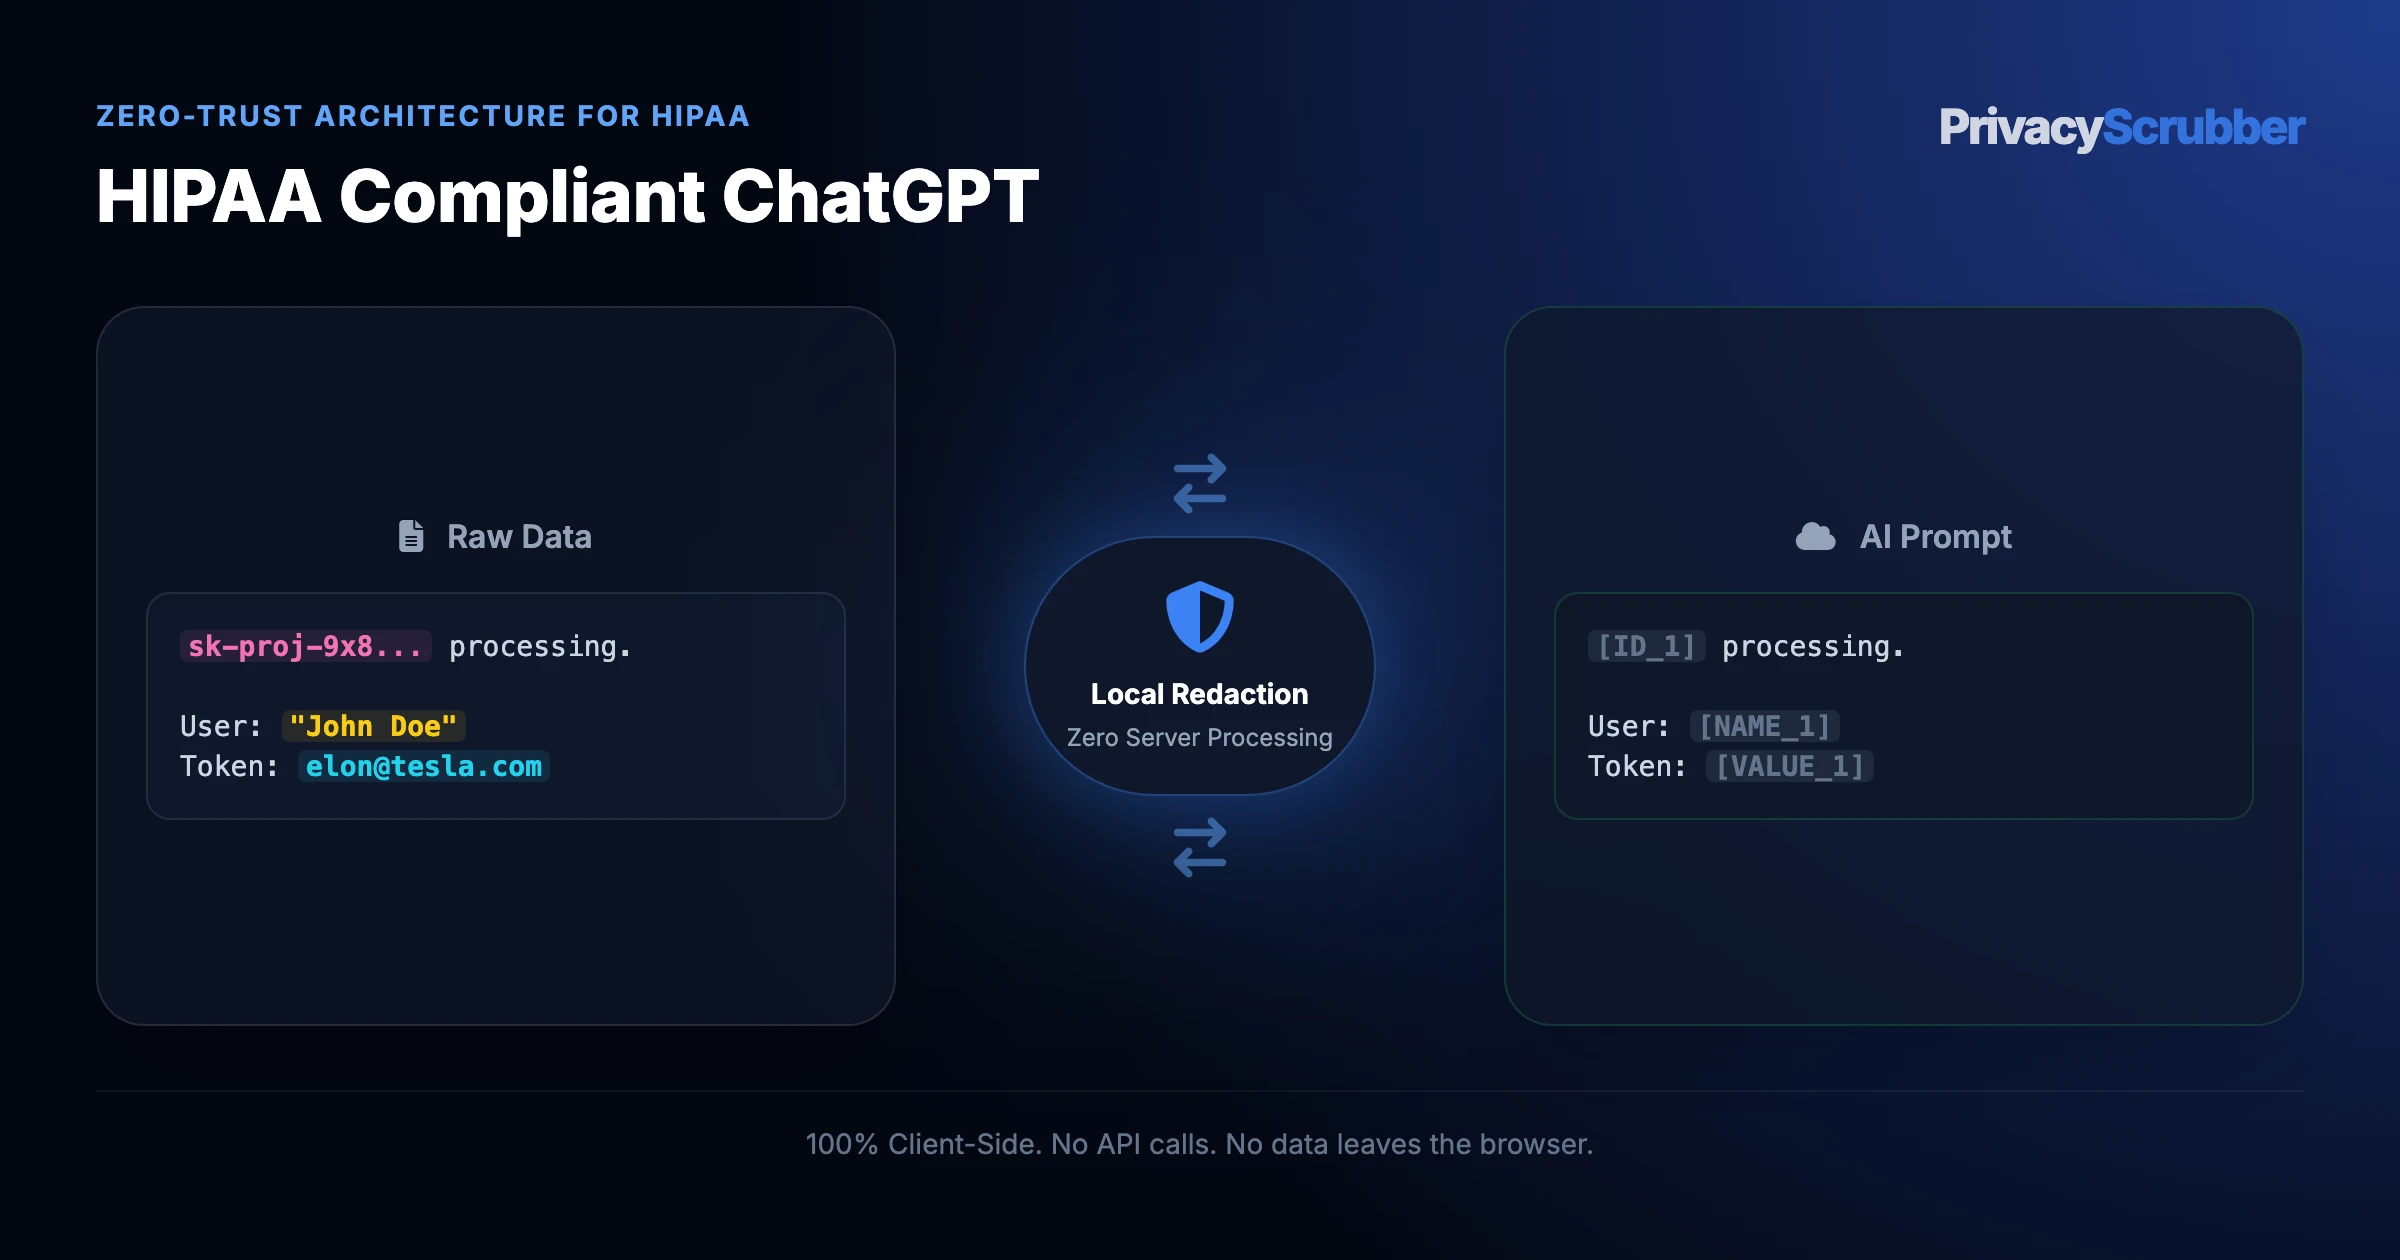
Pasting PHI directly into ChatGPT violates HIPAA. However, by redacting all 18 specific HIPAA Safe Harbor identifiers locally in your browser RAM before sending prompts, the payload is completely de-identified under 45 CFR § 164.514(b)(2). This legally strips PHI classification, allowing healthcare practitioners and researchers to use ChatGPT compliantly without paying for custom enterprise contracts.
De-identify HIPAA identifiers in the text before you prompt
Remove names, dates, MRNs, contact details and other identifiers in local memory, then prompt with the tokenized text. This follows the Safe Harbor method (45 CFR 164.514(b)(2)); free-text notes still need a human check for contextual identifiers.
Pick the Healthcare PHI preset above, paste a de-identified draft or sample note, and review every token.
Launch local scrubberClinicians and analysts get masking inside the ChatGPT box and a one-click reveal for the answer.
Install free extensionRun local MCP sanitization on HIPAA Compliant ChatGPT payloads without API keys.
{
  "mcpServers": {
    "privacyscrubber": {
      "command": "npx",
      "args": ["-y", "@privacyscrubber/mcp-server"]
    }
  }
}npm install @privacyscrubber/sdk
import { sanitize, restore } from '@privacyscrubber/sdk';

// De-identify notes before summarization or coding assistants
const { scrubbedText, tokenMap } = sanitize(clinicalNote);
const aiAnswer = await callYourModel(scrubbedText);   // only tokens leave your process
const { restoredText } = restore(aiAnswer, tokenMap); // originals restored in local RAMHIPAA Compliant ChatGPT: What Healthcare and Clinical Teams Expose to Cloud AI
For medical researchers working on HIPAA Compliant ChatGPT, volatile memory engine prevents non-BAA cloud AI ePHI exposure on hipaa compliant chatgpt and is chatgpt hipaa compliant. Review HIPAA AI privacy guides for sub-millisecond client safeguards.
Why do network gateways miss HIPAA Compliant ChatGPT? Is ChatGPT Enterprise HIPAA compliant? De-identify all 18 Safe Harbor PHI identifiers in local browser RAM before prompting without a vendor BAA. Encrypted browser prompts carrying hipaa compliant chatgpt trigger non-BAA cloud AI ePHI exposure beyond proxy inspection.
Is ChatGPT HIPAA Compliant by Default? (The BAA Dilemma)
Healthcare organizations frequently ask: is ChatGPT HIPAA compliant? The legal reality is straightforward: standard public ChatGPT (Free, Plus, and Team tiers) is not HIPAA compliant. OpenAI strictly limits Business Associate Agreements (BAAs) to costly Enterprise tier contracts (~$60/user/month with minimum annual seat commitments). Pasting unmasked clinical summaries, patient names, or lab reports into standard ChatGPT constitutes an impermissible disclosure under the HIPAA Privacy Rule (45 CFR § 164.502), exposing covered entities to Tier 1–4 civil monetary penalties from the HHS Office for Civil Rights.
How to Make ChatGPT HIPAA Compliant via Safe Harbor De-Identification
Under HIPAA statutory regulations (45 CFR § 164.514(b)(2)), medical information is legally stripped of its Protected Health Information (PHI) status once all 18 specified personal identifiers are removed. Because de-identified health data falls completely outside the statutory definition of PHI, healthcare professionals can build a HIPAA compliant ChatGPT workflow on Safe Harbor de-identification, without an expensive BAA.
Unlike cloud DLP proxies that introduce network latency and third-party data processor risks, PrivacyScrubber implements client-side Zero-Trust Data Sanitization (ZTDS). The software intercepts clinical notes directly in your browser's local RAM, substitutes patient identifiers with deterministic tokens like [PATIENT_1], and allows you to summarize charts or draft letters with zero cloud footprint.
How to Implement a HIPAA Compliant ChatGPT Architecture
By deploying client-side sanitization at the user endpoint, clinicians and administrative teams follow a simple 3-step loop:
- Strip 18 Identifiers Locally: Paste EHR text into the Secure Workspace or click the PrivacyScrubber Chrome Shield directly in the ChatGPT prompt box.
- Query ChatGPT Safely: The LLM receives pure clinical syntax and symptom patterns without patient identities, generating diagnosis summaries or billing codes safely.
- 1-Click Reveal in RAM: Paste the AI response back into PrivacyScrubber to re-hydrate original patient names locally in volatile browser memory.
| HIPAA Safe Harbor Identifier (45 CFR § 164.514) | PrivacyScrubber Local Detection | Safe Harbor Status |
|---|---|---|
| 1. Patient Names & Relatives | [NAME_N] Tokenized | 100% De-identified |
| 2. Geographic subdivisions smaller than state | [ADDRESS_N] Tokenized | 100% De-identified |
| 3. Dates directly related to individual (DOB, Admission) | [DATE_N] Tokenized | 100% De-identified |
| 4. Telephone Numbers | [PHONE_N] Tokenized | 100% De-identified |
| 5. Fax Numbers | [FAX_N] Tokenized | 100% De-identified |
| 6. Electronic Mail (Email) Addresses | [EMAIL_N] Tokenized | 100% De-identified |
| 7. Social Security Numbers (SSN) | [SSN_N] Tokenized | 100% De-identified |
| 8. Medical Record Numbers (MRN) | [MRN_N] Tokenized | 100% De-identified |
| 9. Health Plan Beneficiary Numbers | [ID_N] Tokenized | 100% De-identified |
| 10. Account Numbers (Bank/Credit) | [CARD_N] Tokenized | 100% De-identified |
| 11. Certificate / License Numbers (NPI, DEA) | [ID_N] Tokenized | 100% De-identified |
| 12. Vehicle Serial Numbers & License Plates | [VIN_N] Tokenized | 100% De-identified |
| 13. Device Identifiers & Serial Numbers | [DEVICE_N] Tokenized | 100% De-identified |
| 14. Web Universal Resource Locators (URLs) | [URL_N] Tokenized | 100% De-identified |
| 15. Internet Protocol (IP) Address Numbers | [IP_N] Tokenized | 100% De-identified |
| 16. Biometric Identifiers (Fingerprints, Voiceprints) | [BIOMETRIC_N] Tokenized | 100% De-identified |
| 17. Full-Face Photographic Images | [PHOTO_N] Tokenized | 100% De-identified |
| 18. Any other unique identifying number or code | [CUSTOM_N] Tokenized | 100% De-identified |
Verifying HIPAA Boundaries: The Airplane Mode Standard
To legally protect your clinical workflows, you must verify that no PHI is ever leaked during data preparation. PrivacyScrubber supports this through its unique client-side engine. If you disconnect your network completely (Airplane Mode) and run a patient file through the interface, the redaction operates perfectly. This demonstrates structurally that the PHI was stripped prior to any network transit, supporting a clean compliance boundary for any HIPAA compliant ChatGPT implementation.
Entity Handling Standard for HIPAA Compliant ChatGPT
Prevent over-redaction in HIPAA Compliant ChatGPT workflows by tokenizing only regulated identity fields while leaving non-identifying metrics untouched:
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Subject Identifiers (hipaa compliant chatgpt) | REDACT | [PATIENT_1] | HIPAA Privacy Rule and Safe Harbor De-identification standards guard prevents EPIC from retaining personal HIPAA Compliant ChatGPT records. |
| Regulated Strings (chatgpt hipaa compliance) | REDACT | [PLAN_ID_1] | Applies HIPAA Privacy Rule and Safe Harbor De-identification standards minimization locally before HIPAA Compliant ChatGPT leaves RAM. |
| Tax, Token & Session Strings (is chatgpt hipaa compliant) | REDACT | [MRN_1] | Zero-egress tokenization keeps HIPAA Compliant ChatGPT identifiers off vendor storage. |
| Schema & Formatting (HIPAA Compliant ChatGPT) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for EPIC on hipaa compliant chatgpt. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for HIPAA Compliant ChatGPT while shielding real names. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets EPIC trace root causes cleanly inside sanitized is chatgpt hipaa compliant logs. |
Safe LLM Prompt Template for HIPAA Compliant ChatGPT
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Analyze HIPAA Compliant ChatGPT (is chatgpt hipaa compliant) for medical researchers.
Surrogate markers [PATIENT_1] and [MRN_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Analyze HIPAA Compliant ChatGPT (is chatgpt hipaa compliant) for medical researchers.
Surrogate markers [PATIENT_1] and [MRN_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Why Healthcare Privacy and Compliance Officers Flag Unmasked Prompts in HIPAA Compliant ChatGPT
Under HIPAA Privacy Rule and Safe Harbor De-identification standards, sending raw is chatgpt hipaa compliant records to EPIC creates audit risk; FDA AI software and PHI details technical safe harbor inside local RAM.
3-Step Local RAM Redaction for HIPAA Compliant ChatGPT Workflows
Operating solely in RAM, volatile memory engine removes how to make chatgpt hipaa compliant from HIPAA Compliant ChatGPT prior to EPIC, adhering to AWS macie alternative for ChatGPT and zeroizing on close.
Sever internet access, tokenize hipaa compliant chatgpt into [PATIENT_1] for HIPAA Compliant ChatGPT, and confirm zero sockets open under vercel AI SDK stream sanitizer.
