
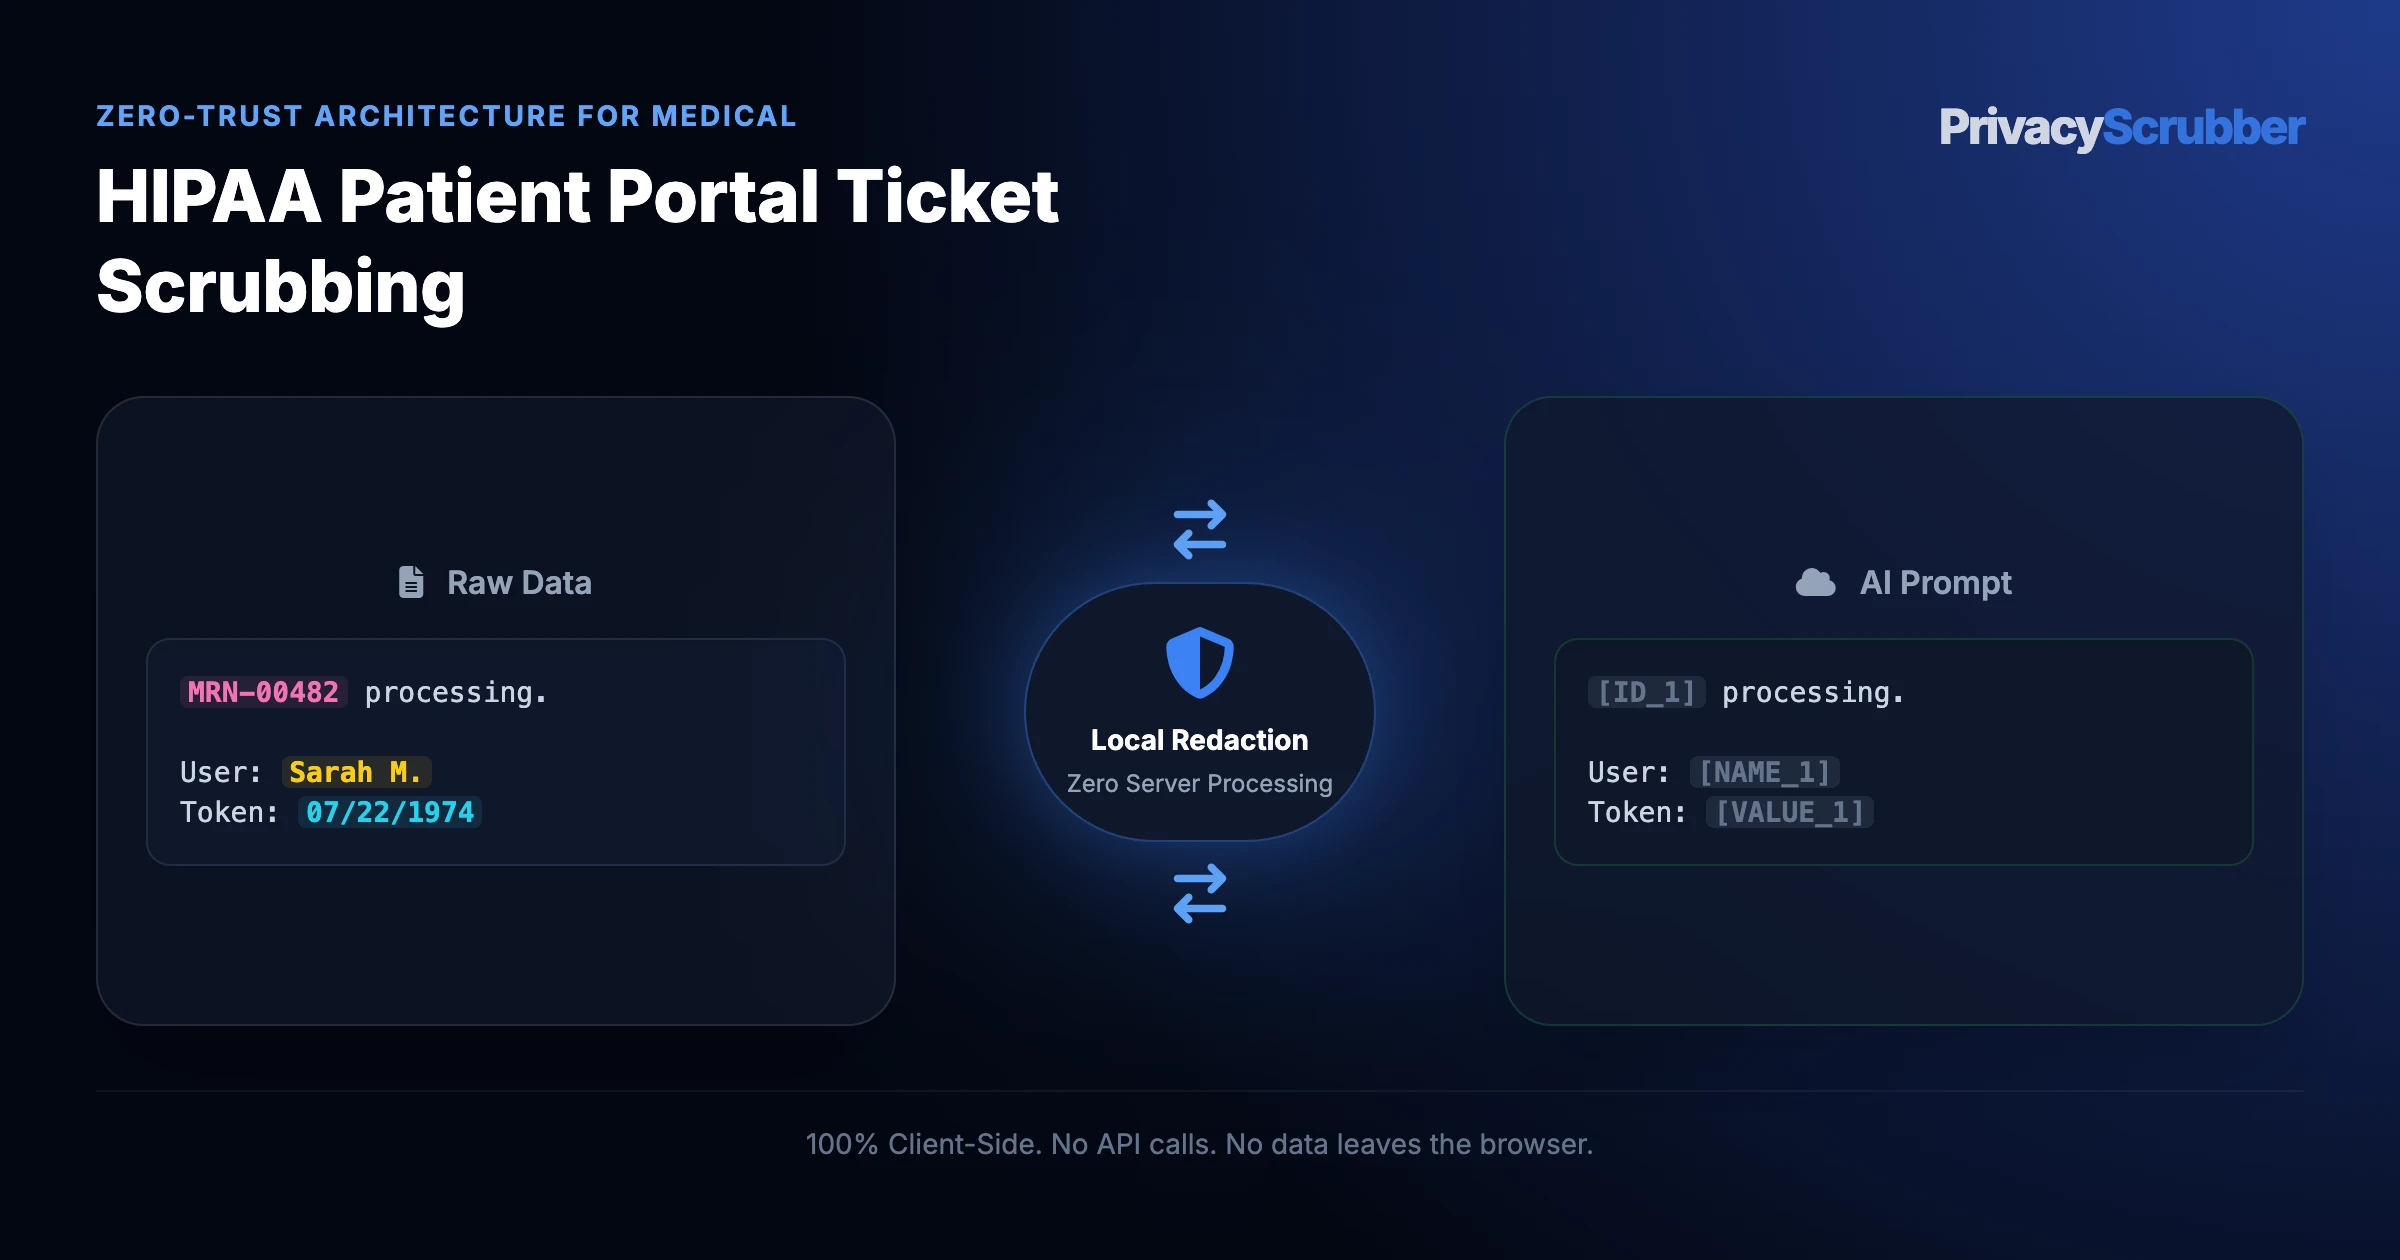
Patient portal messages from Epic MyChart, Cerner HealtheLife, and AthenaHealth contain dense Protected Health Information (PHI): patient legal names, medical record numbers (MRNs), prescription details, and sensitive clinical symptoms. Pasting raw patient messages into cloud-hosted AI tools or external SaaS web services breaches HIPAA Safe Harbor rules and creates statutory breach liabilities. Sanitizing clinical tickets in client RAM before triage processing prevents all network egress without requiring third-party Business Associate Agreements (BAAs).
Data Leakage Risks in Prevent Patient Portal Messages & Clinical PHI Cloud Leakage for Healthcare Practitioners and Staff
Achieving verifiable data protection for Prevent Patient Portal Messages & Clinical PHI Cloud Leakage is a foundational requirement when clinicians, nurses, medical researchers, and healthcare administrators integrate ChatGPT, clinical decision support AI, and AI-assisted documentation platforms. Because transmitting unmasked 18 HIPAA Safe Harbor PHI identifiers to cloud LLMs without local de-identification, unmasked prevent patient portal cloud leak payloads create immediate exposure across Healthcare & Clinical perimeters. Our Healthcare & Clinical AI privacy guides detail how to isolate stop clinical phi network leakage in local RAM before any cloud API call occurs.
Prevent Epic MyChart and patient portal messages from leaking to external clouds. 100% in-RAM HIPAA Safe Harbor de-identification for clinical triage. Across Healthcare & Clinical pipelines, Prevent Patient Portal Messages & Clinical PHI Cloud Leakage combines free-text context with regulated identifiers (prevent patient portal cloud leak, stop clinical phi network leakage). If left unredacted prior to API transit, transmitting unmasked 18 HIPAA Safe Harbor PHI identifiers to cloud LLMs without local de-identification results in immediate compliance drift under HIPAA Privacy Rule.
The Clinical Inbox Crisis: Clinician Burnout vs. HIPAA Breach Liability
Primary care physicians and clinic nurses receive an average of 50 to 100 patient portal messages daily through Epic MyChart, Cerner, or AthenaHealth. The cognitive burden of drafting personalized replies after clinic hours is the leading driver of physician burnout. AI assistants like ChatGPT can draft empathetic, context-aware responses in 10 seconds.
However, copying patient portal messages into commercial AI platforms without local de-identification exposes hospitals to statutory HIPAA Privacy and Security Rule violations. When a nurse pastes a message reading "Hi Dr. Chen, my daughter Emily (DOB: 09/12/2018, MRN #49281) has a fever of 103" into an unvetted LLM, that PHI enters third-party training logs and vendor data centers.
Patient Portal Message Anatomy: What Gets Masked vs. Preserved
PrivacyScrubber applies rigorous HIPAA Safe Harbor filtering to inbound portal inquiries:
| Message Component | Sample Raw Text | PrivacyScrubber Action | Clinical AI Utility |
|---|---|---|---|
| Patient Name | Emily Vance | Masked → [PATIENT_1] | Patient identity protected |
| Guardian / Parent | Sarah Vance (mother) | Masked → [GUARDIAN_1] | Relational context preserved |
| MRN / Account # | MRN: 94028471 | Masked → [MRN_1] | EHR identifier secured |
| Date of Birth | 09/12/2018 (6yo) | Masked → [DOB_1] (age preserved) | Pediatric dosage guidance preserved |
| Clinical Symptoms | Fever 103°F, productive cough, ear pain | PRESERVED | Acuity triage & differential diagnosis |
| Medications | Children's Tylenol 160mg/5mL | PRESERVED | Safe dosage titration advice |
Step-by-Step: AI Patient Message Triage Workflow
- 1. Copy Inbound Portal Ticket: Highlight the patient's incoming inquiry from your EHR inbox (Epic, Cerner, or AthenaHealth).
- 2. Tokenize Locally: Drop or paste the message into PrivacyScrubber under the "Medical & HIPAA" profile. Personal names, phone numbers, and MRNs are converted to tokens in active RAM.
- 3. Draft Response in AI: Ask ChatGPT to compose an initial triage assessment: "Draft a warm, professional nurse response to [GUARDIAN_1] regarding [PATIENT_1]'s fever of 103°F and ear pain. Recommend appropriate home comfort measures, safe antipyretic dosing, and clear red flags requiring urgent urgent-care evaluation."
- 4. 1-Click Reveal & Send: Paste the AI draft into PrivacyScrubber's Reveal tab. Patient and guardian names are seamlessly restored for review and delivery inside MyChart.
Verifying Zero-Server Isolation in Airplane Mode
Hospital Privacy Officers (CPOs) can verify compliance by disconnecting clinical workstations from the internet (Airplane Mode) and processing 50 sample portal messages. The tokenization runs 100% locally in browser memory with zero external network calls.
Equip Entire Clinical Departments with TEAMS
Standardize HIPAA-compliant AI triage across hospital clinics and nursing teams for a flat $99/mo rate with unlimited seats and zero cloud storage.
Balancing AI Context & Privacy in Epic MyChart Clinical Patient Portal Message & Triage Intake Ticket
Use the classification table below to separate high-liability Epic MyChart Clinical Patient Portal Message & Triage Intake Ticket attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Patient Full Legal Names & Preferred Names | REDACT | [PATIENT_1], [NAME_1] | Direct individual identifier linking medical condition to a specific human being |
| Medical Record Numbers (MRN) & Account IDs | REDACT | [MRN_1], [ACCOUNT_1] | Institutional identifier subject to HIPAA Safe Harbor mandatory de-identification |
| Patient Date of Birth & Exact Calendar Dates | REDACT | [DOB_1], [DATE_1] | Statutory HIPAA identifier exposing demographic vulnerability |
| Residential Street Addresses & Phone Numbers | REDACT | [ADDRESS_1], [PHONE_1] | Geolocation data linking medical inquiries to physical domiciles |
| Reported Clinical Symptoms & Onset Timeline | PRESERVE | Cleartext (sharp lower right quadrant pain for 36 hours) | Diagnostic medical narrative required for AI clinical triage acuity scoring |
| Prescription Medication Names & Dosages | PRESERVE | Cleartext (Amoxicillin 500mg TID, Ibuprofen 600mg) | Pharmacological context essential for drug interaction screening |
| Vital Signs, Lab Values & Pain Scales | PRESERVE | Cleartext (Temp 101.4 F, Pain Scale 7/10) | Objective physiological data needed for clinical urgency escalation |
| Clinical Department & Triage Specialty | PRESERVE | Cleartext (Pediatric Urgent Care, Family Medicine) | Operational routing parameter required for clinic workflow dispatch |
Ready-to-Use Sanitized Prompt: Epic MyChart Clinical Patient Portal Message & Triage Intake Ticket
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
You are an Emergency Medicine Triage Nurse and Clinical Decision Support Specialist. Review the following sanitized Epic MyChart message where patient names, dates of birth, MRNs, addresses, phone numbers, and physician names have been tokenized ([PATIENT_1], [DOB_1], [MRN_1], [ADDRESS_1], [PHONE_1], [NAME_1], [CLINIC_1], [ID_1]).

Tasks:
1. Assess clinical triage acuity (Emergency Severity Index - ESI score) based on reported right lower quadrant pain, fever, and nausea.
2. Evaluate potential differential diagnoses (e.g. acute appendicitis vs mesenteric adenitis) requiring urgent physical evaluation.
3. Draft a prompt, compassionate, and clear triage reply instructing the patient on immediate next steps without requesting or re-identifying any HIPAA identifiers.

[PASTE SANITIZED TEXT HERE]
You are an Emergency Medicine Triage Nurse and Clinical Decision Support Specialist. Review the following sanitized Epic MyChart message where patient names, dates of birth, MRNs, addresses, phone numbers, and physician names have been tokenized ([PATIENT_1], [DOB_1], [MRN_1], [ADDRESS_1], [PHONE_1], [NAME_1], [CLINIC_1], [ID_1]).

Tasks:
1. Assess clinical triage acuity (Emergency Severity Index - ESI score) based on reported right lower quadrant pain, fever, and nausea.
2. Evaluate potential differential diagnoses (e.g. acute appendicitis vs mesenteric adenitis) requiring urgent physical evaluation.
3. Draft a prompt, compassionate, and clear triage reply instructing the patient on immediate next steps without requesting or re-identifying any HIPAA identifiers.

[PASTE SANITIZED TEXT HERE]
How Clinical Risk and Compliance Committees Enforce Zero-Egress on Prevent Patient Portal Messages & Clinical PHI Cloud Leakage
Legal and GRC reviews of Prevent Patient Portal Messages & Clinical PHI Cloud Leakage focus on HIPAA Privacy Rule, HIPAA Security Rule, and the Common Rule (45 CFR 46) for research involving human subjects. To prevent exposing Protected Health Information (PHI) to third-party AI servers, which constitutes a HIPAA breach and carries penalties up to $1.9M per violation category while preserving AI utility for prevent patient portal cloud leak and stop clinical phi network leakage, enterprises implement the client-side redaction controls outlined in EHR & emr AI privacy.
Running AI on Prevent Patient Portal Messages & Clinical PHI Cloud Leakage Without Sending Real Identifiers
Through PrivacyScrubber Medical Profile (Chrome Extension & Offline OCR), PrivacyScrubber provides a zero-egress firewall for Prevent Patient Portal Messages & Clinical PHI Cloud Leakage. Before any prevent patient portal cloud leak or stop clinical phi network leakage text reaches ChatGPT, clinical decision support AI, and AI-assisted documentation platforms, deterministic tokenization substitutes sensitive strings with [PATIENT_1], [MRN_1], [DOB_1], [NPI_1] in volatile memory, fulfilling is notebooklm safe for confidential data with zero external server dependencies.
This zero-egress architecture for Prevent Patient Portal Messages & Clinical PHI Cloud Leakage is independently verifiable via the Airplane Mode Standard: disconnect your network, sanitize a sample prevent patient portal cloud leak payload into [PATIENT_1], [MRN_1], [DOB_1], [NPI_1], and confirm 0 outbound packets in DevTools. This satisfies batch anonymize crm exports & lead lists for AI analysis and generates a cryptographic SHA-256 compliance receipt for HIPAA Privacy Rule audits.
