"PrivacyScrubber provides the essential de-identification layer for Medical professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Medical data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
Can you send a faxed medical record to ChatGPT? Not without sanitization. Healthcare organizations still receive millions of fax documents weekly — referrals, lab results, prescriptions, prior authorization requests. These documents contain dense, unstructured PHI: patient names, DOBs, Social Security Numbers, diagnoses, NPI provider numbers, and insurance IDs. Transmitting fax content to any external AI model without HIPAA Safe Harbor de-identification constitutes a reportable breach under 45 CFR § 164.502.
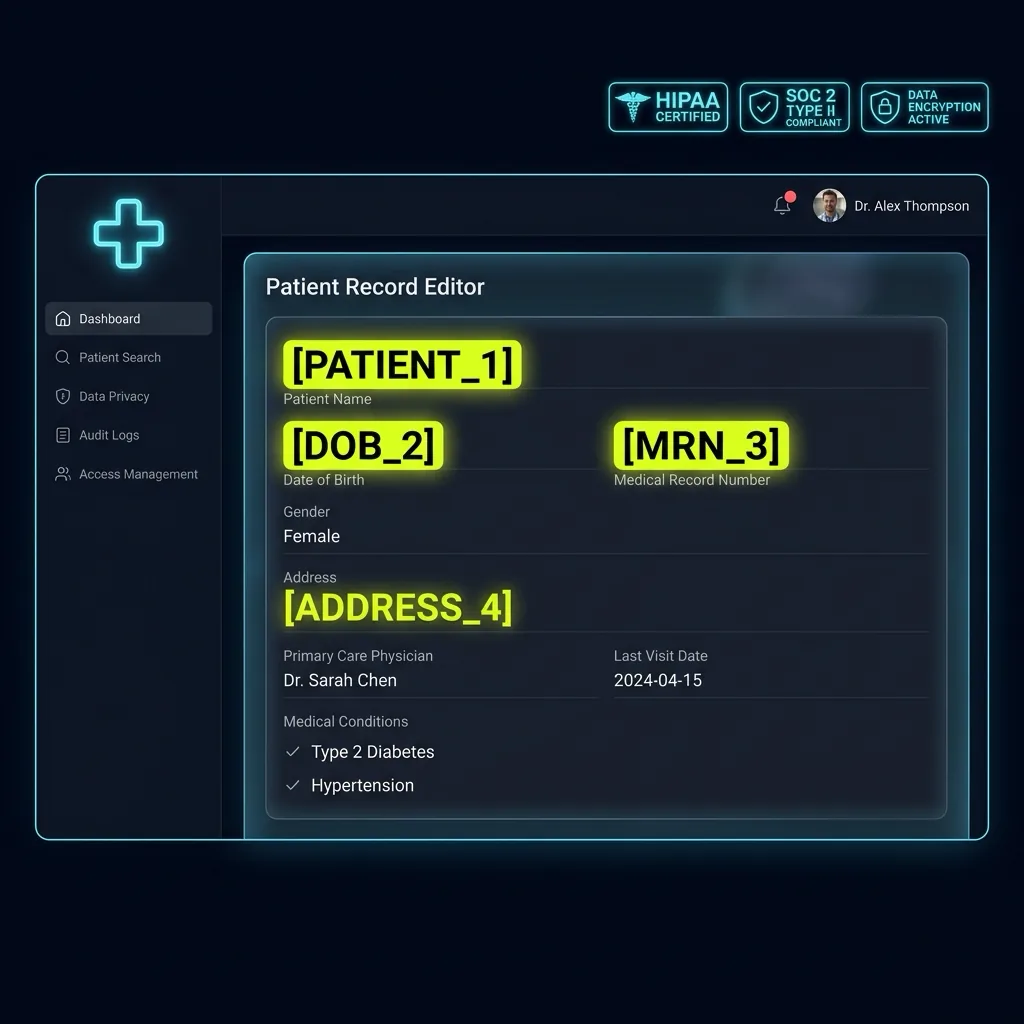
PrivacyScrubber's Medical profile detects PHI in fax document text (after OCR) and tokenizes it locally: [PATIENT_1], [MRN_1], [DX_1], [NPI_1]. The sanitized text is safe for AI-assisted triage — zero bytes of PHI reach ChatGPT or Claude.
What Healthcare Practitioners and Staff Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
Securing workflows around HIPAA Fax Document AI is an operational necessity under health privacy laws. As clinical teams adopt ChatGPT, clinical decision support AI, and AI-assisted documentation platforms for note-taking, the threat of PHI exposure to external datasets is a major security challenge. Our medical AI privacy guides outlines clinical defense standards for securing the medical perimeter. The core priority is eliminating exposing Protected Health Information (PHI) to third-party AI servers, which constitutes a HIPAA breach and carries penalties up to $1.9M per violation category.
Every clinical note or file uploaded to generative AI platforms without HIPAA-compliant redaction represents a potential violation. Standard 'do not train' flags are insufficient to protect patient data from being logged on third-party servers. For clinicians, nurses, medical researchers, and healthcare administrators, managing this input stream is critical. Healthcare fax documents contain unstructured PHI: patient names, DOBs, diagnoses, and NPI numbers. Sanitize faxed medical records locally before AI analysis — 100% HIPAA Safe Harbor compliant.
Why Medical Compliance Teams Flag Unmasked AI Prompts
Healthcare privacy laws are explicit: HIPAA Privacy Rule, HIPAA Security Rule, and the Common Rule (45 CFR 46) for research involving human subjects. However, reducing administrative overhead requires adopting AI efficiency. Adopting the guidelines in anonymize radiology reports for ai helps organizations build a secure workflow that prevents PHI from reaching model training datasets. Verifiable compliance requires stopping raw exfiltration at the browser intake interface. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
Using our Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber intercepts sensitive records at the browser level via either the web interface or our automated Chrome Extension.
How to Use AI on Real Medical Data — Without Sending a Single Real Name
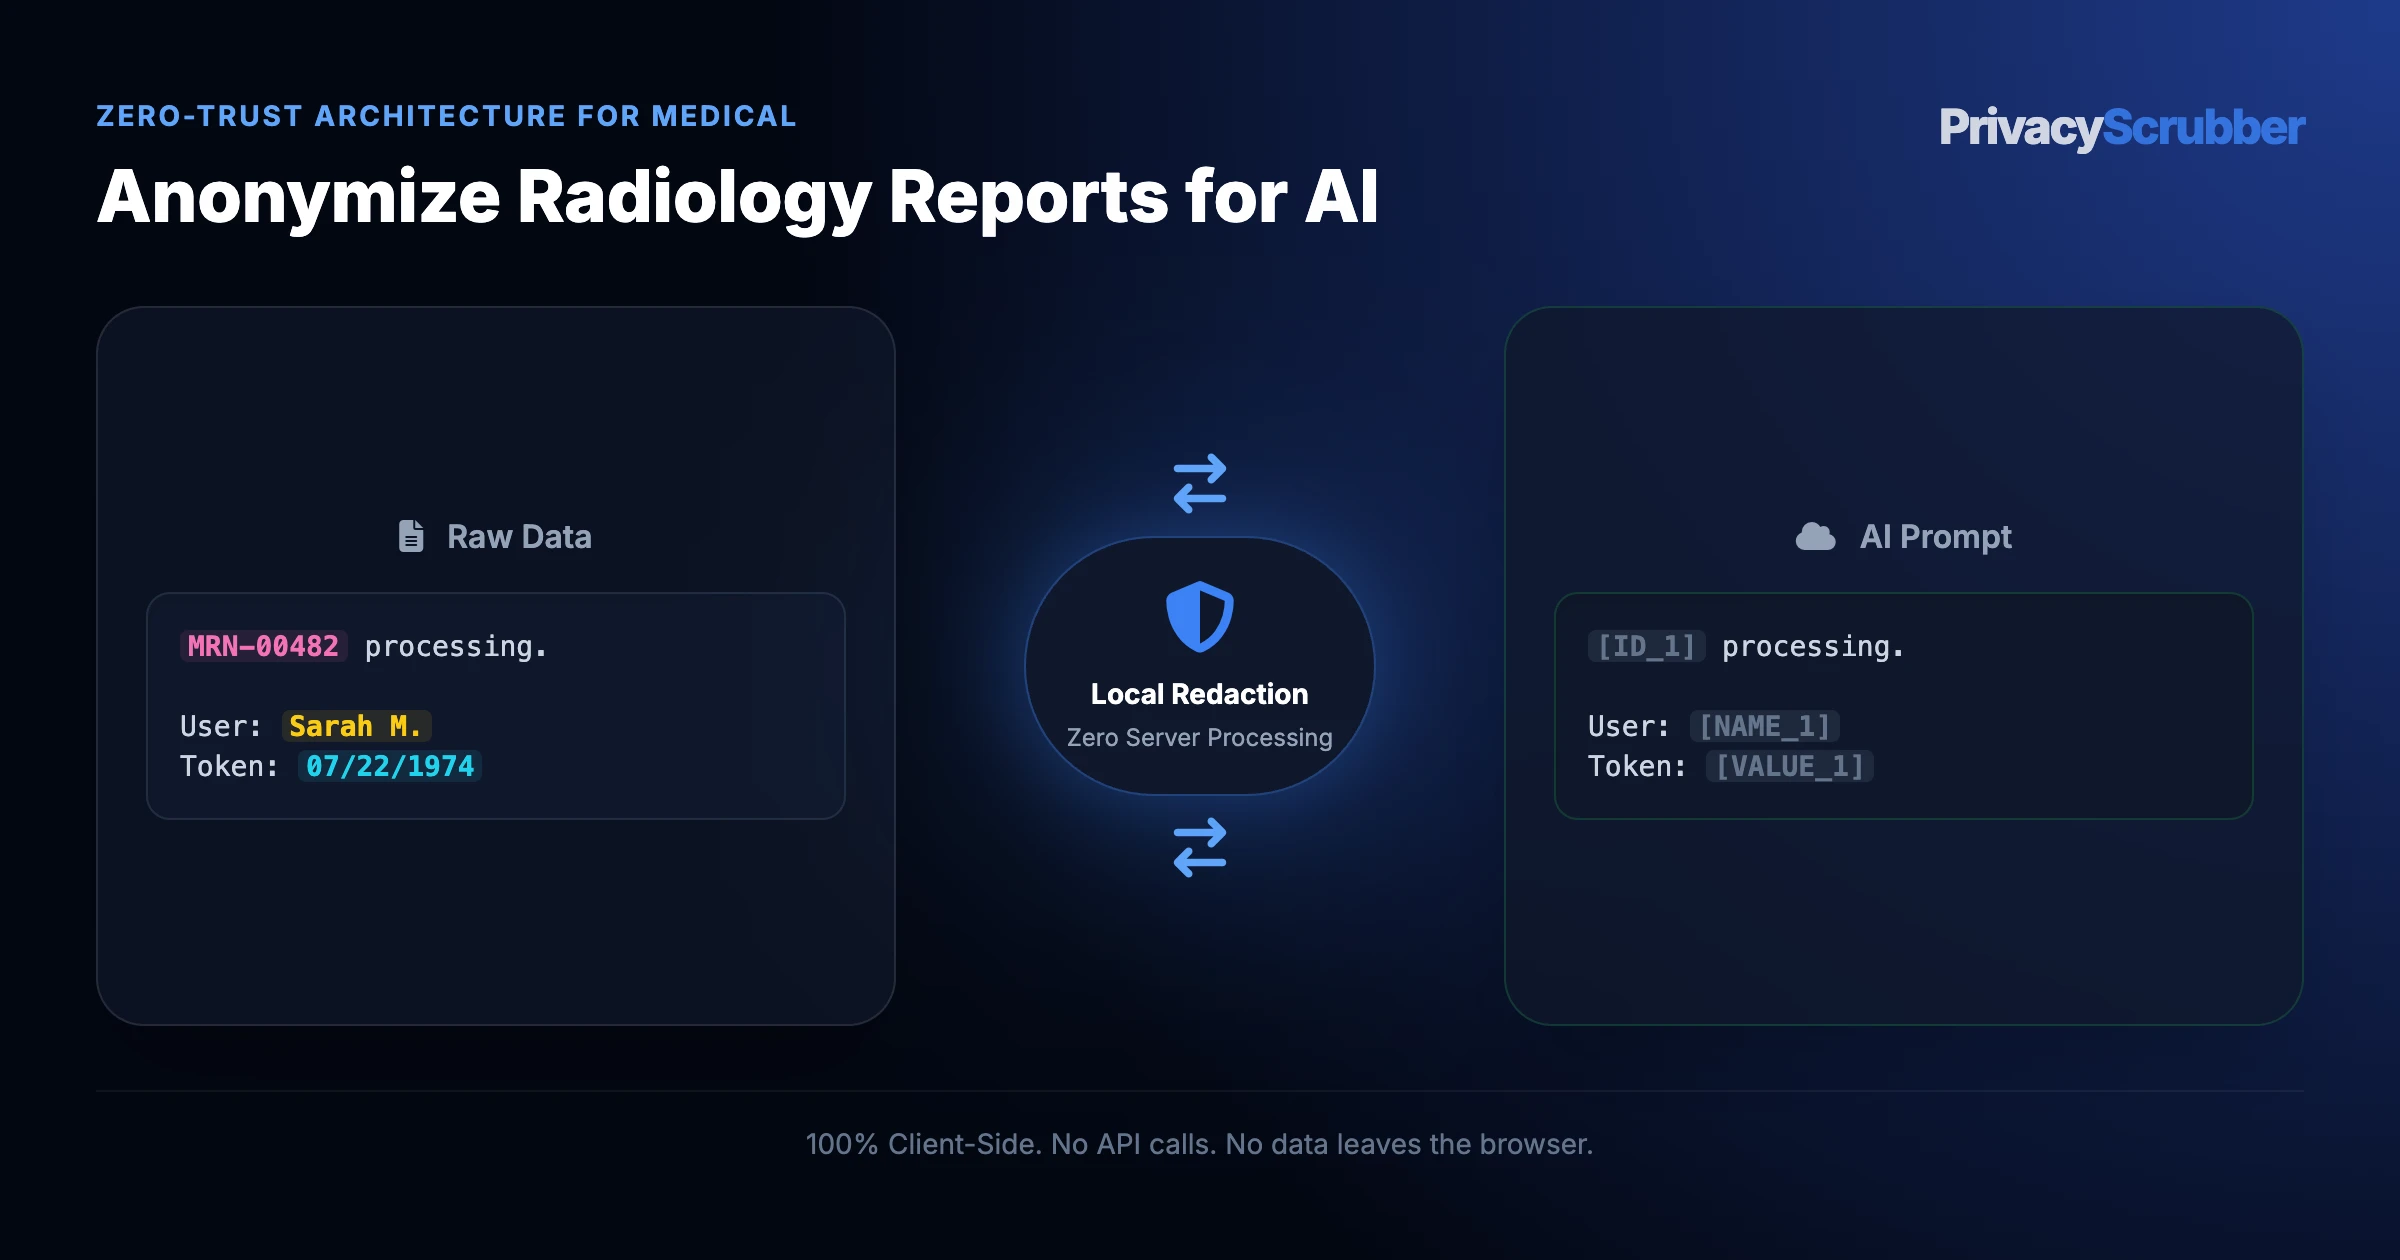
Using our Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber intercepts sensitive records at the browser level via either the web interface or our automated Chrome Extension. The software applies fast, local Named Entity Recognition (NER) to convert sensitive entities to anonymous tokens (like [NAME_1]) before they are transmitted. For compliance auditing, this mirrors the exact principles of HIPAA-compliant ChatGPT workflows, enabling organizations to use external AI capabilities without sacrificing data control. The Chrome Extension automates this integration by embedding a protection toggle directly in ChatGPT, Claude, and Gemini to automatically swap and restore text. Running Named Entity Recognition locally ensures that teams can continue using ChatGPT, clinical decision support AI, and AI-assisted documentation platforms for daily queries without any third-party data collection.
This verifiable isolation is tested via the Airplane Mode Standard. Disconnect from the internet, run a scrub, and observe the immediate redaction. Because zero data is sent externally, your compliance posture aligns with offline compliance auditing.
Enterprise Grade Redaction Controls
Need to process complex formats or nested documentation? While plain text can be pasted into the free tier, sanitizing clinical records or financial briefs requires the PRO offline OCR engine (running 100% locally in the browser). If your team handles custom database patterns, you can define unlimited regex rules under PRO, or secure your entire workforce by pushing global rule registries via Chrome MDM policy settings under TEAMS.
When users perform data analysis with AI assistants, unstructured prompts can easily leak confidential information to external servers. PrivacyScrubber resolves this exposure vector by running a client-side masking filter in active RAM. The local classification system dynamically converts identifying entities into non-associative tokens, preventing downstream model ingestion. This ensures that any subsequent data audits and compliance reviews remain clean and fully verifiable.
Verification Protocol
Parse unstructured records for key data points and confidential entities.
Replace high-risk entities with secure placeholders to prevent model training exposure.
Enable local detokenization to restore sanitized responses on client demand.
Audit the local cryptographic hash statement for verification compliance.
Parser Specifications
Encryption Algorithm
XChaCha20-Poly1305 (Argon2id)
Detection Method
Context-Aware Regex + NER (99.3% Accuracy)
Data Egress Rule
Zero-Server Egress (Airplane Mode Verifiable)
Classification Standard
High Privacy Guard
Associated Threat Level
High (Identity Exposure)
Why Fax PHI is the Highest-Risk AI Workflow in Healthcare
Despite widespread EHR adoption, fax remains the dominant interoperability protocol in US healthcare. CMS estimates that healthcare organizations send and receive 9 billion fax pages annually. These documents — referrals, discharge summaries, prior auth requests, lab results — arrive as unstructured text containing the full spectrum of PHI, making them one of the most dangerous source documents for AI ingestion.
Unlike structured EHR data with field-level access controls, fax content is free-form. A single prior authorization fax can contain patient name, SSN, diagnosis history, insurance IDs, provider NPIs, and medication lists — all in paragraph text that standard DLP pattern matching frequently misses due to formatting inconsistencies.
The risk escalates when clinical staff — seeking to accelerate medical operations — paste fax text directly into ChatGPT to draft response letters, summarize patient history, or check medication interactions. Without pre-sanitization, this workflow constitutes a HIPAA Privacy Rule violation and triggers mandatory breach notification if the AI vendor does not hold a valid BAA.
HIPAA Safe Harbor — 18 PHI Identifiers in Fax Documents
PrivacyScrubber Medical profile detects all 18 categories. Removal achieves HIPAA Safe Harbor de-identification (45 CFR § 164.514(b)).
HIPAA Compliant AI Fax Workflow
The safest architecture for fax-to-AI clinical workflows: scan fax → PrivacyScrubber offline OCR → Medical profile tokenization → HIPAA-compliant ChatGPT submission → AI response → Reverse Scrub in local RAM. The PHI never leaves the device. The AI receives a structurally complete document with zero reportable identifiers.
For medical groups processing high volumes of faxed referrals, PrivacyScrubber TEAMS provides centralized Medical profile governance. The security officer defines custom detection rules for proprietary diagnosis code formats, internal patient ID structures, and payer authorization code patterns — distributed to all staff through a single admin interface, with zero per-seat DLP licensing overhead.
Instant Simulation
HIPAA Fax Document AI Sanitizer
Watch our zero-trust engine neutralize sensitive identifiers 100% locally. No data ever leaves your device.
Local processing 0 Server logs
ZTDS_ENGINE_V1.5.0
PROMPT INPUT > Draft a reply for customer inquiry. Sender is Alice Johnson, email: alice.j@organization.org, mobile: 555-0177.
PROMPT INPUT > Draft a reply for customer inquiry. Sender is [NAME_1], email: [EMAIL_1], mobile: [PHONE_1].
Medical Detection Profile
Our zero-trust engine is pre-hardened for Medical workflows, automatically identifying and tokenizing the following parameters 100% locally.
PATIENT_NAME
Active Protection
MRN
Active Protection
DOB
Active Protection
DIAGNOSIS
Active Protection
INSURANCE_ID
Active Protection
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with offline compliance auditing.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
New Capability: Local Image OCR & Zero-Trust Sync
The PrivacyScrubber Chrome Extension now supports Local Image OCR. Paste screenshots directly into the extension popup to redact sensitive PII offline using an isolated WebAssembly worker. Combined with our new Zero-Trust Session Sync, enterprise teams can seamlessly share custom detection rules without ever transmitting data to cloud servers.
ChatGPT (OpenAI) Integration
Step-by-Step Integration Guide: HIPAA Fax Document AI
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT (OpenAI):
Act as a clinical documentation specialist. Review the following sanitized SOAP note for [PATIENT_1] under care of Dr. [PHYSICIAN_1]:
1. Synthesize the patient's acute clinical symptoms, past medical history, and physical examination findings.
2. Cross-check active prescription dosages against standard contraindications.
3. Draft a plain-English, patient-friendly after-visit discharge summary.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Do not alter any cryptographic token identifiers ([PATIENT_1], [MRN_1], [PHYSICIAN_1], [DATE_1], [POLICY_ID_1]) in your response for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT (OpenAI) outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: HIPAA Safe Harbor De-Identification (45 CFR § 164.514(b)(2))All 18 statutory personal health identifiers are stripped in local browser memory prior to prompt transmission, removing the legal requirement for a vendor Business Associate Agreement (BAA).
Medical Adoption Use Cases
Chief Medical Information OfficerHIPAA & HITECH
Zero-Trust Verified
Secures clinical notes and patient records, masking PHI locally before research staff run diagnostic queries through generative LLMs.
Enforces zero-trust client-side sanitization across nursing and administrative terminals without needing complex BAA vendor agreements with AI providers.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Medical compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any medical text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in peer-reviewed repositories and persistent academic archives:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Medical Teams.
Are faxed medical records covered under HIPAA?
Yes. Faxed medical records are Protected Health Information (PHI) under HIPAA regardless of transmission method. The paper or digital fax that arrives at a healthcare provider's fax machine contains PHI in the same way as an EHR record. HIPAA's Privacy Rule (45 CFR § 164.502) and Security Rule (45 CFR § 164.312) apply to any PHI that is digitized, including scanned fax images converted to text via OCR for AI analysis.
What PHI typically appears in healthcare fax documents?
Healthcare fax documents commonly contain: patient full name and DOB, Social Security Number (especially on insurance forms), Medical Record Number (MRN), treating provider name and NPI number, insurance member ID and group number, diagnosis codes (ICD-10), procedure codes (CPT), prescription drug names and DEA numbers, lab result values and reference ranges, and prior authorization reference numbers.
How does HIPAA Safe Harbor de-identification apply to AI workflows?
HIPAA Safe Harbor (45 CFR § 164.514(b)) requires removal of 18 specific PHI identifiers before data is considered de-identified. De-identified data is not subject to HIPAA's use and disclosure restrictions, meaning it can be submitted to ChatGPT or Claude without a Business Associate Agreement. PrivacyScrubber's Medical profile detects all 18 Safe Harbor categories and replaces them with deterministic tokens locally — achieving functional de-identification before any AI submission.
Can I use OCR to convert fax images to text and then sanitize with PrivacyScrubber?
Yes. PrivacyScrubber PRO includes local offline OCR (powered by Tesseract.js running in browser RAM). Scan or photograph the fax document, upload to PrivacyScrubber, and the OCR + Medical profile pipeline extracts text and tokenizes PHI in a single step — without any image or text leaving your device. The sanitized text output is then safe for AI analysis.
Does protecting data with PrivacyScrubber before AI processing satisfy HIPAA Privacy Rule?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with HIPAA Privacy Rule because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for medical workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match medical-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask medical data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your medical data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Sanitize Prompt" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard Named Entity Recognition (NER) model to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
Can I use AI to summarize patient records?
Only if you de-identify the records first. Uploading raw patient notes to public AI models violates HIPAA. PrivacyScrubber's local processing ensures PHI is masked before summarization. Protect your entire staff with TEAMS for $99/mo.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
What Healthcare Practitioners and Staff Send to AI — and What They Should Be Sending InsteadWhy Medical Compliance Teams Flag Unmasked AI Prompts
Healthcare privacy laws are explicit: HIPAA Privacy Rule, HIPAA Security Rule, and the Common Rule (45 CFR 46) for research involving human subjects. However, reducing administrative overhead requires adopting AI efficiency. Adopting the guidelines in anonymize radiology reports for ai helps organizations build a secure workflow that prevents PHI from reaching model training datasets. Verifiable compliance requires stopping raw exfiltration at the browser intake interface. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
How to Use AI on Real Medical Data — Without Sending a Single Real Name
Using our Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber intercepts sensitive records at the browser level via either the web interface or our automated Chrome Extension. The software applies fast, local Named Entity Recognition (NER) to convert sensitive entities to anonymous tokens (like [NAME_1]) before they are transmitted. For compliance auditing, this mirrors the exact principles of HIPAA-compliant ChatGPT workflows, enabling organizations to use external AI capabilities without sacrificing data control. The Chrome Extension automates this integration by embedding a protection toggle directly in ChatGPT, Claude, and Gemini to automatically swap and restore text. Running Named Entity Recognition locally ensures that teams can continue using ChatGPT, clinical decision support AI, and AI-assisted documentation platforms for daily queries without any third-party data collection.
Why Fax PHI is the Highest-Risk AI Workflow in Healthcare
PrivacyScrubber Medical profile detects all 18 categories. Removal achieves HIPAA Safe Harbor de-identification (45 CFR § 164.514(b)).
Is PrivacyScrubber safe for hipaa fax document ai, fax medical records chatgpt, sanitize faxed phi ai, hipaa fax machine privacy, scanned fax healthcare ai llm?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with hipaa fax document ai, fax medical records chatgpt, sanitize faxed phi ai, hipaa fax machine privacy, scanned fax healthcare ai llm, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for medical?
Our engine includes 30 specialized industry profiles optimized for medical data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.