
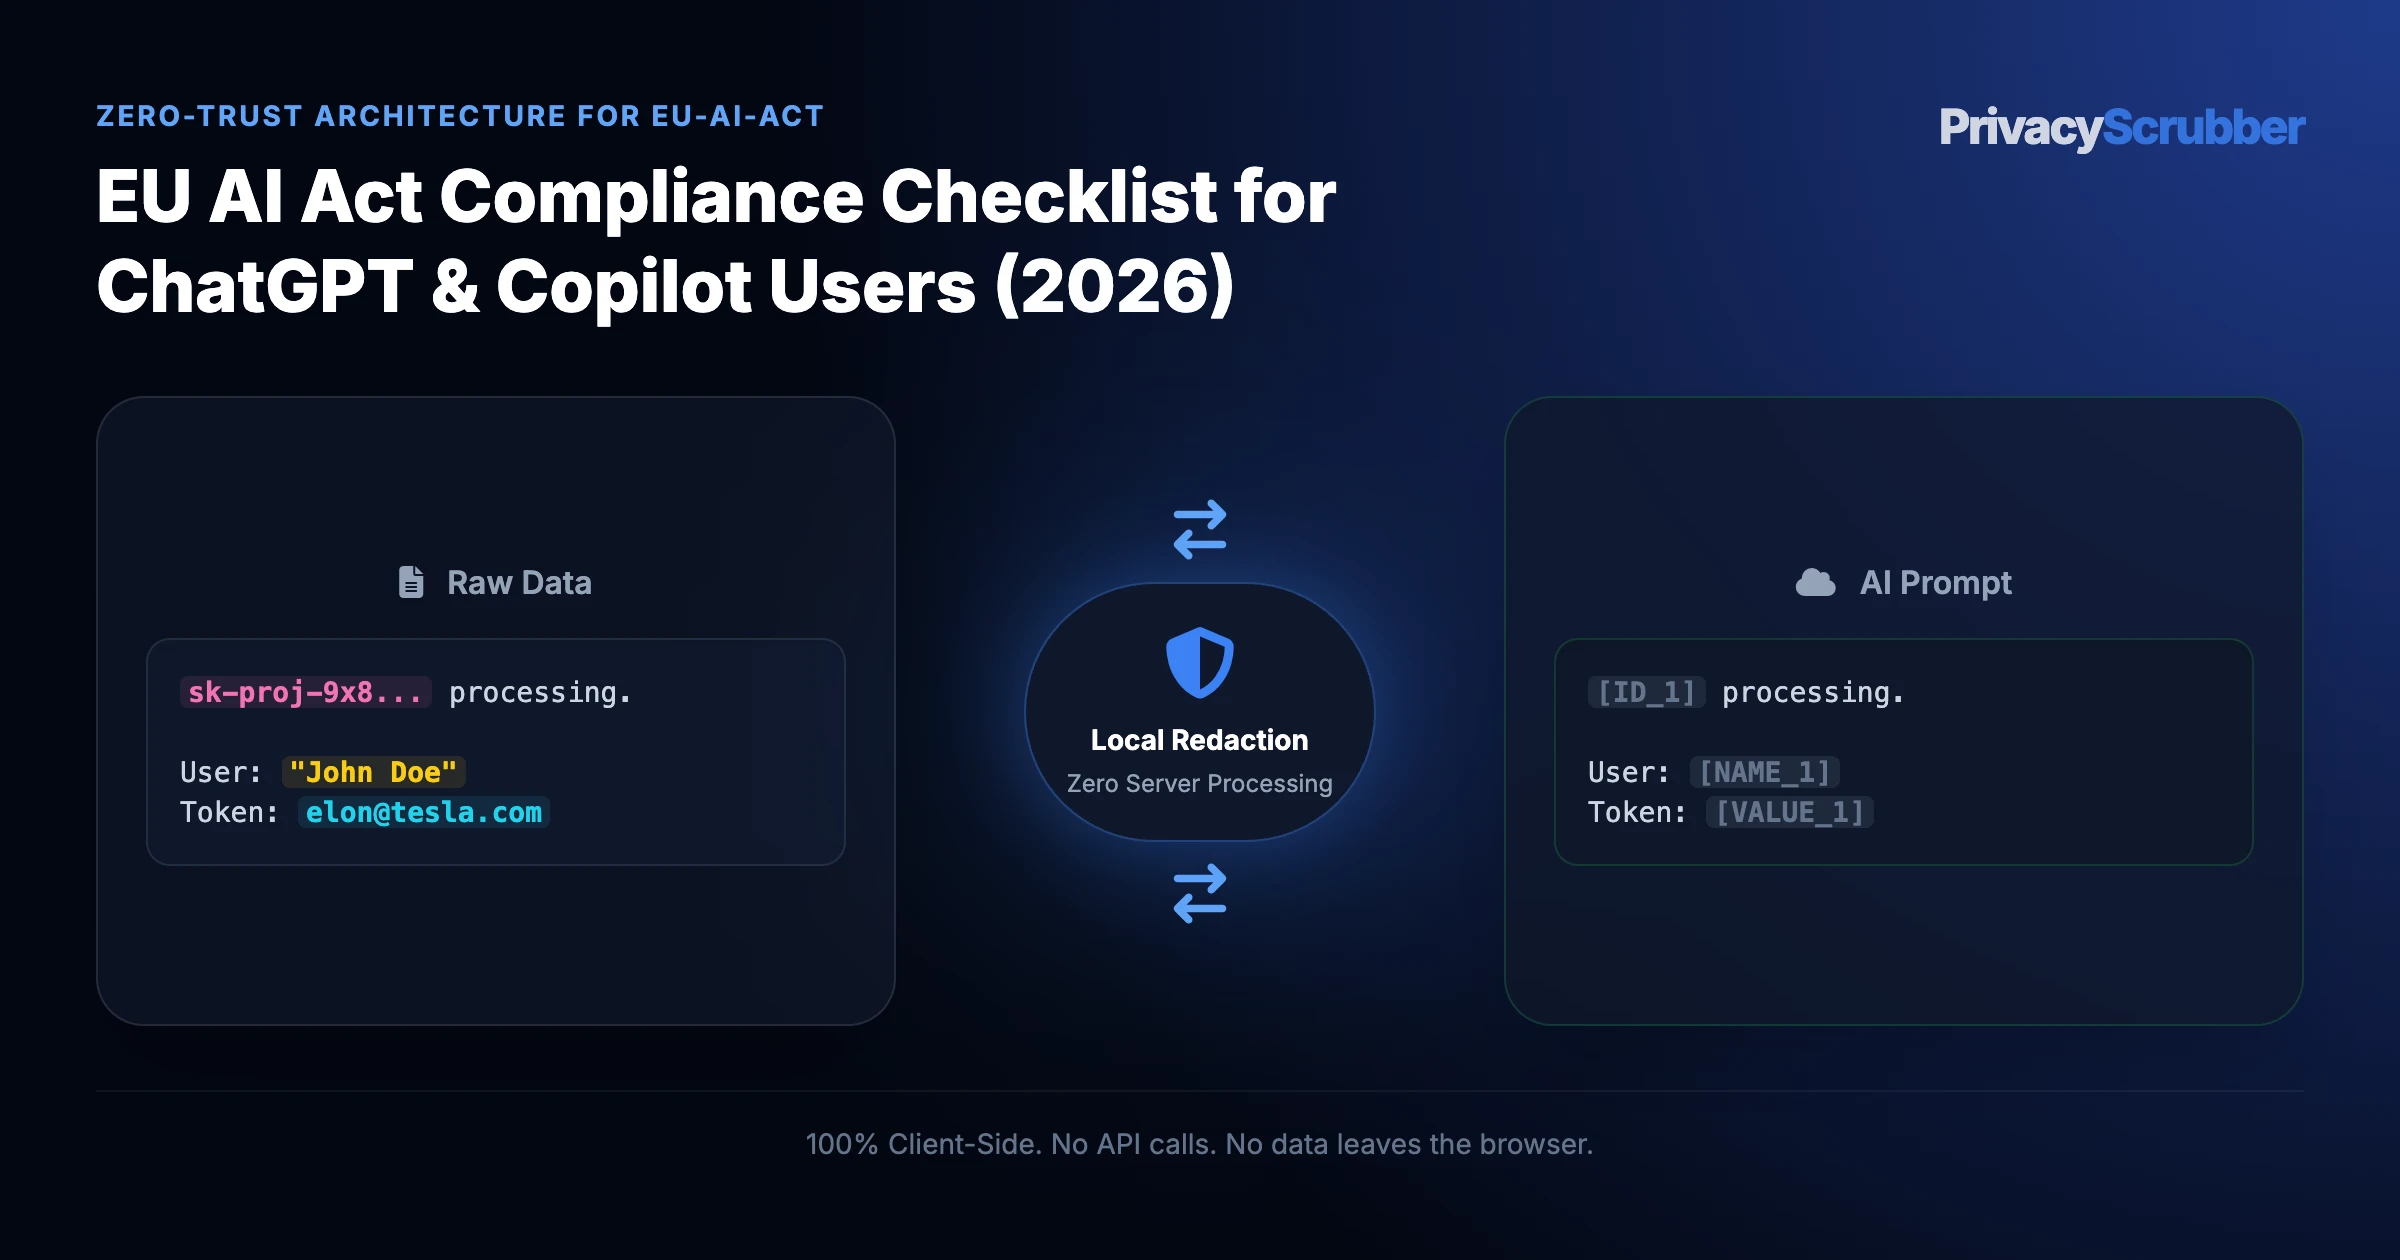
Sub-millisecond browser ZTDS shield lets European legal teams analyze EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) in ChatGPT Enterprise without raw eu ai act retention. Sensitive EU AI Act compliance literals swap to [SUBJECT_1] before dispatch.
Why Unmasked Prompts Break EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) Security
Unredacted prompts in EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) send EU AI Act compliance straight to ChatGPT Enterprise. Using EU AI Act AI privacy guides, teams deploy volatile memory engine and map inputs to [EMAIL_1].
EU AI Act compliance deadlines: August 2025 (GPAI), February 2026 (prohibited AI), August 2026 (transparency). 100% local RAM execution with zero egress. Across EU AI Act apps, EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) embeds regulated EU AI Act compliance attributes vulnerable to raw eu ai act retention under Article 52).
Eliminating raw eu ai act retention on EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026)
Securing EU AI Act compliance for EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) starts before any HTTP request builds. Here volatile memory engine guards European legal teams against high-risk training data governance leaks by locking mappings in local RAM.
Paired with TEAMS ($99/mo flat) or Developer SDK, European legal teams gain SHA-256 receipts proving EU AI Act compliance stayed local under Article 52).
What to Redact vs. Preserve in EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026)
This field-level specification ensures EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) prompts retain 100% mathematical and semantic accuracy with zero cleartext PII egress:
| Payload Element | Policy | ZTDS™ Token | Compliance & Reasoning Impact |
|---|---|---|---|
| Regulated Strings (AI regulation Europe) | REDACT | [EMAIL_1] | Applies Article 52) minimization locally before EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) leaves RAM. |
| Tax, Token & Session Strings (eu ai act) | REDACT | [NATIONAL_ID_1] | Zero-egress tokenization keeps EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) identifiers off vendor storage. |
| Keys & Account Codes (eu ai act) | REDACT | [NATIONAL_ID_1] | Stops eu ai act credentials from entering cloud telemetry on EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026). |
| Article 52) Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) findings directly against policy clauses. |
| Schema & Formatting (EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026)) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for ChatGPT Enterprise on EU AI Act compliance. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) while shielding real names. |
Copy-Paste Safe Instruction for EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026)
Attach this guardrail prompt to any redacted EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) session so downstream models keep symbolic tags intact for instant restoration:
Role: EU AI Act advisor evaluating EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026).
Sanitized tokens ([SUBJECT_1], [NATIONAL_ID_1]) mask all EU AI Act compliance identifiers.
1. Flag operational gaps in eu ai act.
2. Recommend Article 52) fixes.
3. Keep [SUBJECT_1] unchanged.

[PASTE EU AI ACT COMPLIANCE CHECKLIST FOR CHATGPT & COPILOT USERS (2026) TEXT]
Role: EU AI Act advisor evaluating EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026).
Sanitized tokens ([SUBJECT_1], [NATIONAL_ID_1]) mask all EU AI Act compliance identifiers.
1. Flag operational gaps in eu ai act.
2. Recommend Article 52) fixes.
3. Keep [SUBJECT_1] unchanged.

[PASTE EU AI ACT COMPLIANCE CHECKLIST FOR CHATGPT & COPILOT USERS (2026) TEXT]
Audit Readiness Across EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) Workstations
Bridging Article 52) compliance and fast EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) iteration relies on EU AI act compliance pseudonymization over raw eu ai act 2026 entries.
Isolating Sensitive Fields Inside EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) Prompts
With browser ZTDS shield, European legal teams sanitize EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) at keyboard speed—mapping EU AI Act compliance to [SUBJECT_1] in <1ms with zero upload per best ChatGPT team plan alternative for small businesses.
Auditors validate EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) offline via Airplane Mode: scrub EU AI Act compliance into [EMAIL_1], inspect DevTools, and match express.js in-memory PII masking.
