
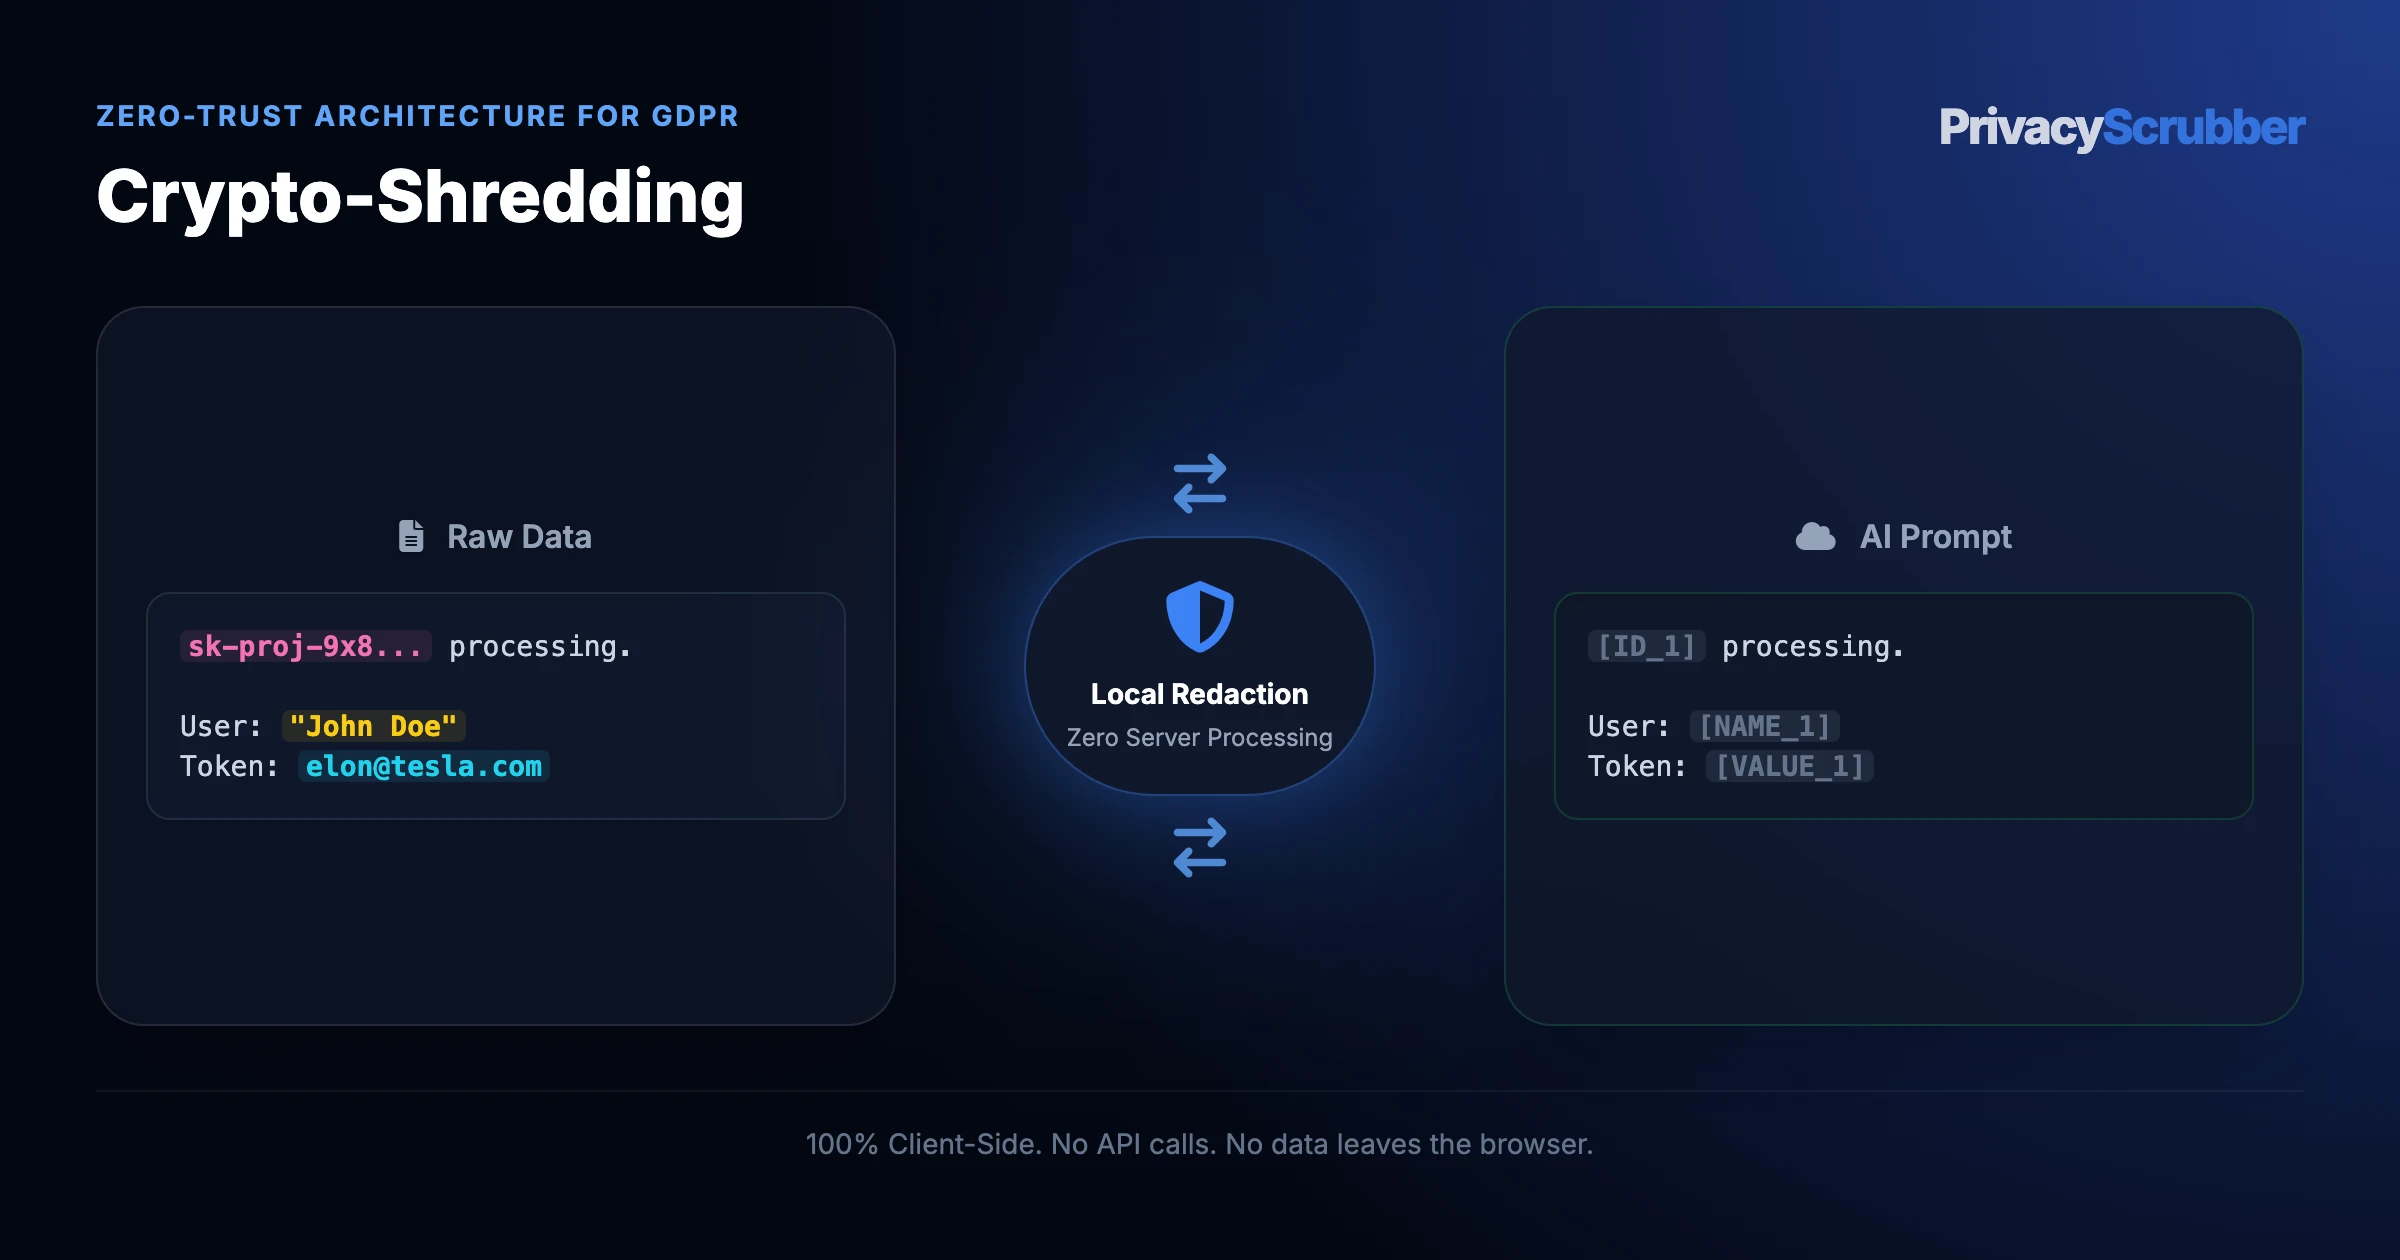
Fulfilling a GDPR Article 17 'Right to be Forgotten' request in deep vector indices or historical RAG logs is nearly impossible. Crypto-Shredding solves this by encrypting each distinct user memory unit with a unique key. Deletion is executed instantly by destroying the key, rendering the ciphertext permanent intractable noise.
Crypto-Shredding: What Privacy and DPO Teams Expose to Cloud AI
Operationalizing Crypto-Shredding under and EU AI Act (2026) demands blocking Art. 44 transfer & training exposure before ChatGPT sees crypto-shredding AI memory. Read GDPR AI privacy guides for deterministic [NAME_1] masking.
Sending raw crypto-shredding AI memory strings into ChatGPT bypasses endpoint controls for compliance managers. Deleting personal data from massive vector databases is technically impossible. Redact sensitive PII in local browser RAM with zero server cloud egress. Swapping entities to [IBAN_1] locally removes unmasked crypto-shredding AI memory exposure.
Solving the AI 'Machine Unlearning' Dilemma under GDPR
Under **GDPR Article 17**, European residents maintain the absolute right to demand the erasure of their personal data. However, as enterprise AI systems transition toward unified context layers and persistent AI memories (e.g. MemGPT or Mem0), compliance becomes a technical nightmare. Locating, isolating, and wiping specific personal records from massive, highly distributed vector indices requires LLM data minimization, otherwise it is virtually impossible.
| Deletion Metric | Traditional Vector Wiping | Cryptographic Erasure (Crypto-Shredding) |
|---|---|---|
| Execution Speed | Slow (Requires full index rebuild) | Instantaneous (Key destruction) |
| Regulatory Verification | Difficult to prove in cloud databases | Mathematical Proof (Permanent noise) |
| Infrastructure Impact | High (Service disruption during audit) | Zero (No database downtime) |
Trusted Execution Environments (TEE) and Zero-Trust Memory
To implement crypto-shredding, advanced AI memory systems store individual Data Unit Keys (DUKs) inside a highly secure Trusted Execution Environment (TEE). If a user requests deletion, the TEE destroys that specific DUK. This architecture, known as a secure virtual machine setup, is a massive leap forward for zero-trust computing. PrivacyScrubber avoids this complexity entirely by executing PII redactionpre-ingestion, ensuring your vector database never stores plaintext PHI or PII in the first place, thus maintaining SOC 2 compliance.
Pre-Inference Redaction Matrix: Crypto-Shredding
Use the classification table below to separate high-liability Crypto-Shredding attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Subject Identifiers (crypto-shredding AI memory) | REDACT | [NAME_1] | and EU AI Act (2026) guard prevents ChatGPT from retaining personal Crypto-Shredding records. |
| Regulated Strings (Trusted Execution Environments) | REDACT | [EMAIL_1] | Applies and EU AI Act (2026) minimization locally before Crypto-Shredding leaves RAM. |
| Tax, Token & Session Strings (GDPR right to be forgotten LLM) | REDACT | [IBAN_1] | Zero-egress tokenization keeps Crypto-Shredding identifiers off vendor storage. |
| Schema & Formatting (Crypto-Shredding) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for ChatGPT on crypto-shredding AI memory. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for Crypto-Shredding while shielding real names. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets ChatGPT trace root causes cleanly inside sanitized GDPR right to be forgotten LLM logs. |
Ready-to-Use Sanitized Prompt: Crypto-Shredding
Pair this structured instruction with your tokenized Crypto-Shredding payload so ChatGPT, Claude, or Gemini preserves all bracketed surrogates for local RAM restoration:
Role: GDPR advisor evaluating Crypto-Shredding.
Sanitized tokens ([NAME_1], [IBAN_1]) mask all crypto-shredding AI memory identifiers.
1. Flag operational gaps in GDPR right to be forgotten LLM.
2. Recommend and EU AI Act (2026) fixes.
3. Keep [NAME_1] unchanged.

[PASTE CRYPTO-SHREDDING TEXT]
Role: GDPR advisor evaluating Crypto-Shredding.
Sanitized tokens ([NAME_1], [IBAN_1]) mask all crypto-shredding AI memory identifiers.
1. Flag operational gaps in GDPR right to be forgotten LLM.
2. Recommend and EU AI Act (2026) fixes.
3. Keep [NAME_1] unchanged.

[PASTE CRYPTO-SHREDDING TEXT]
GDPR (Article 32 Mandate Checkpoints: Crypto-Shredding
Because and EU AI Act (2026) restricts external crypto-shredding AI memory processing, science of LLM data minimization outlines how [NAME_1] substitution shields Crypto-Shredding from unmasked crypto-shredding AI memory exposure.
3-Step Local RAM Redaction for Crypto-Shredding Workflows
Deploying offline endpoint scrubber traps Crypto-Shredding inputs locally, mapping GDPR right to be forgotten LLM to [IBAN_1]; aligned with secure ChatGPT for pharma IND & NDA filings, ChatGPT never touches cleartext.
Test crypto-shredding AI memory scrubbing offline or run npx ztds-audit in CI: Crypto-Shredding emits 0 bytes per self-hosted agent systems PII protection.
