French Works Council (CSE) AI Clearance: Code du Travail Art. L2312-38 & CNIL Workplace Compliance
TEAMS EDITION
French Works Council (CSE) AI Clearance: Secure French Works Council (CSE) clearance for AI. Prevent employee surveillance under Code du travail Art. L2312-38 & CNIL rules with local RAM masking.
Ilya SibiryakovPrivacy Architect••3 min read
100% Local Airplane Mode
French Works Council (CSE) Workplace AI Consultation & Clearance Dossier (Code du travail Art. L2312-38 / CNIL) French Data Protection Officers (DPO / Délégué à la Protection des Données), Works Council Members (CSE - Comité Social et Économique), Labor Law Counsel & HR Directors French Labor Code (Code du travail Articles L2312-8 & L2312-38), CNIL Workplace AI Recommendations (Plan d'action IA), Loi Informatique et Libertés & GDPR Article 88
Direct Technical Standard (Zero-Trust Rule)
To secure French Works Council (CSE - Comité Social et Économique) consultation clearance under Code du travail Article L2312-38 and CNIL workplace guidance, organizations must redact employee names, social security numbers (NIR / Carte Vitale), matricule interne staff numbers, and workplace communications in client RAM before prompt dispatch. Macro efficiency statistics, departmental productivity gains, and collective bargaining parameters remain in cleartext with zero network egress, mathematically preventing employee behavioral surveillance.
AI Summary / Key Takeaways
Verified Zero-Trust Logic
"PrivacyScrubber provides the essential de-identification layer for GDPR professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real GDPR data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
In France, introducing generative AI tools such as Microsoft 365 Copilot, ChatGPT Enterprise, or Claude into enterprise workflows triggers mandatory prior information and consultation of the Social and Economic Committee (Comité Social et Économique - CSE) under Article L2312-38 and Article L2312-8 of the French Labor Code (Code du travail). Under French employment law and Article L1121-1, employee rights and personal freedoms are strictly safeguarded against disproportionate or automated surveillance. Furthermore, the French Data Protection Authority (CNIL) in its AI Action Plan (Plan d'action IA) and workplace recommendations emphasizes that processing employee personal data—including internal staff identification (matricule interne), social security numbers (NIR / Carte Vitale), and individual communication telemetry—through third-party cloud LLMs without a prior Data Protection Impact Assessment (AIPD) and CSE consultation constitutes a severe statutory breach under GDPR Article 88. PrivacyScrubber's Zero-Trust Data Sanitization (ZTDS) operates exclusively in local browser RAM, converting individual employee identifiers into deterministic surrogates before transmission. This provides empirical, mathematically provable assurance that individual performance monitoring and employee profiling are technically impossible, removing the primary legal blocker for CSE approval and enterprise AI charters (Charte IA).
Zero-Trust Data Protection: Ensure Article 32 compliance by pseudonymizing data before it reaches public AI endpoints. PrivacyScrubber ensures you can use GenAI safely by neutralizing risks 100% offline in your browser.
What Privacy and DPO Teams Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
To establish verifiable privacy for French Works Council (CSE) AI Clearance in GenAI workflows, companies must address the risk of data exfiltration. Using tools like ChatGPT, Mistral, and local LLM integrations without local redaction leaves gdpr frameworks highly vulnerable. Our gdpr AI privacy guides details how to build a resilient gdpr security model that neutralizes unauthorized cross-border transfer of EU resident data to US-based AI providers without adequate safeguards before any cloud API is called.
Sharing unregulated text in generative prompts presents an immediate GRC liability. Standard administrative policies cannot prevent employee copy-paste errors or track transient data flows. For DPOs, European business owners, and compliance managers, relying on cloud-based filters means exposing client context to external servers. Secure French Works Council (CSE) clearance for AI. Prevent employee surveillance under Code du travail Art. L2312-38 & CNIL rules with local RAM masking.
Privacy Insight: In France, introducing generative AI tools such as Microsoft 365 Copilot, ChatGPT Enterprise, or Claude into enterprise workflows triggers mandatory prior information and consultation of the Social and Economic Committee (Comité Social et Économique - CSE) under Article L2312-38 and Article L2312-8 of the French Labor Code (Code du travail). Under French employment law and Article L1121-1, employee rights and personal freedoms are strictly safeguarded against disproportionate or automated surveillance. Furthermore, the French Data Protection Authority (CNIL) in its AI Action Plan (Plan d'action IA) and workplace recommendations emphasizes that processing employee personal data—including internal staff identification (matricule interne), social security numbers (NIR / Carte Vitale), and individual communication telemetry—through third-party cloud LLMs without a prior Data Protection Impact Assessment (AIPD) and CSE consultation constitutes a severe statutory breach under GDPR Article 88. PrivacyScrubber's Zero-Trust Data Sanitization (ZTDS) operates exclusively in local browser RAM, converting individual employee identifiers into deterministic surrogates before transmission. This provides empirical, mathematically provable assurance that individual performance monitoring and employee profiling are technically impossible, removing the primary legal blocker for CSE approval and enterprise AI charters (Charte IA).
Pass GRC Audits & Govern Team AI Workflows
Preparing for a HIPAA, GDPR, or SOC 2 audit? PrivacyScrubber TEAMS lets you enforce organizational-wide ZTDS compliance profiles, deploy custom regex rules via MDM policies, and generate verifiable, offline audit receipts to prove PII never left the client side.
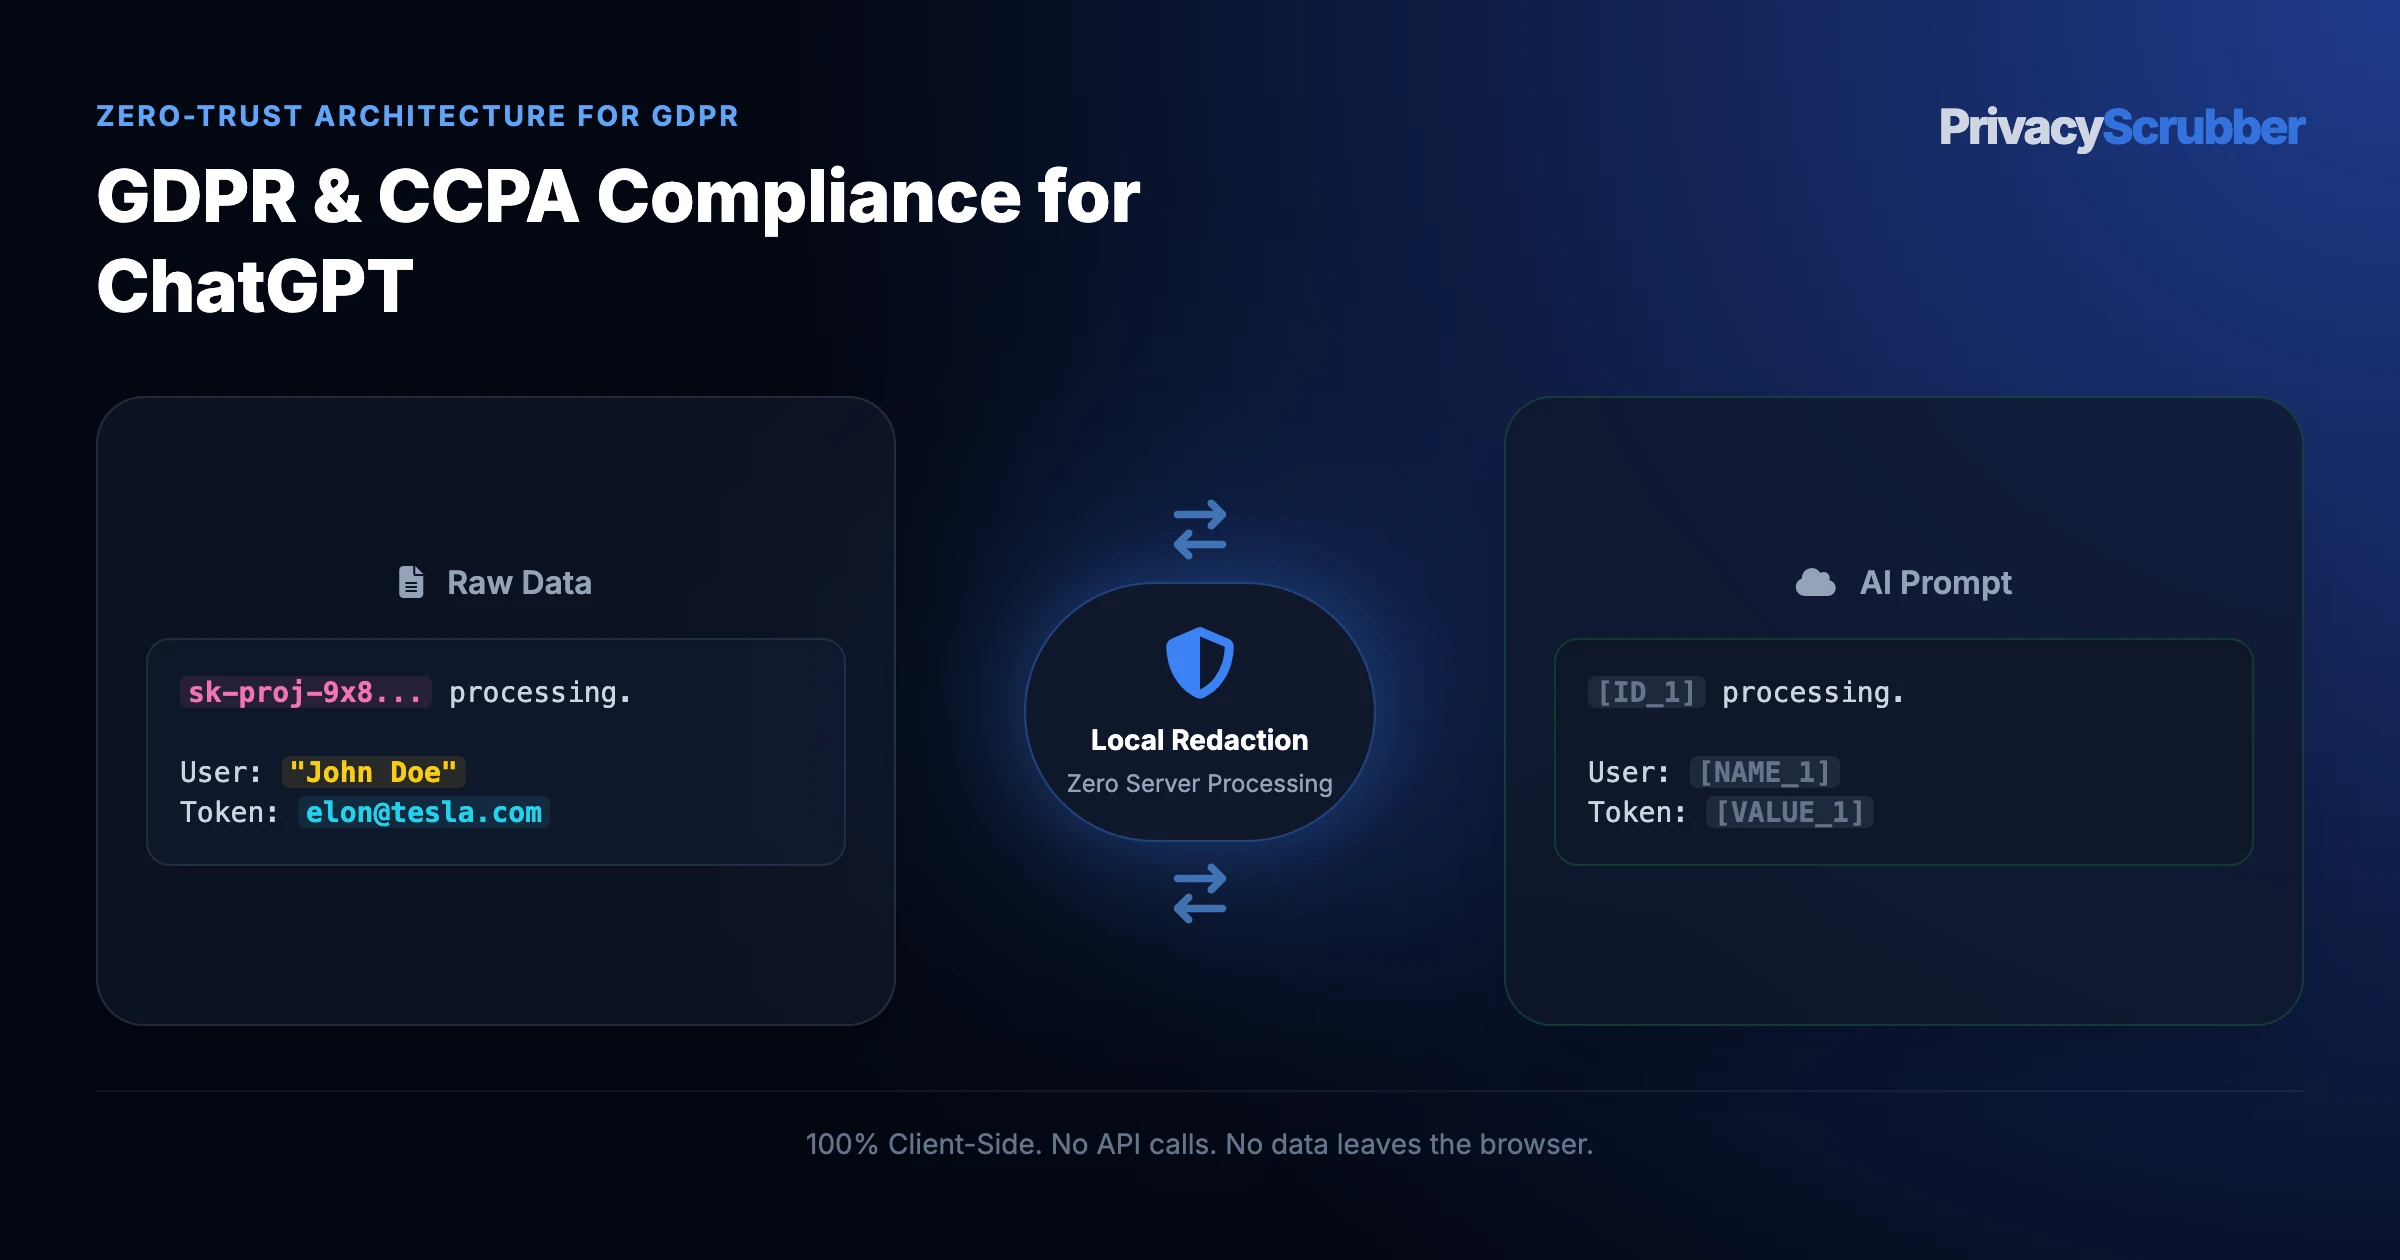
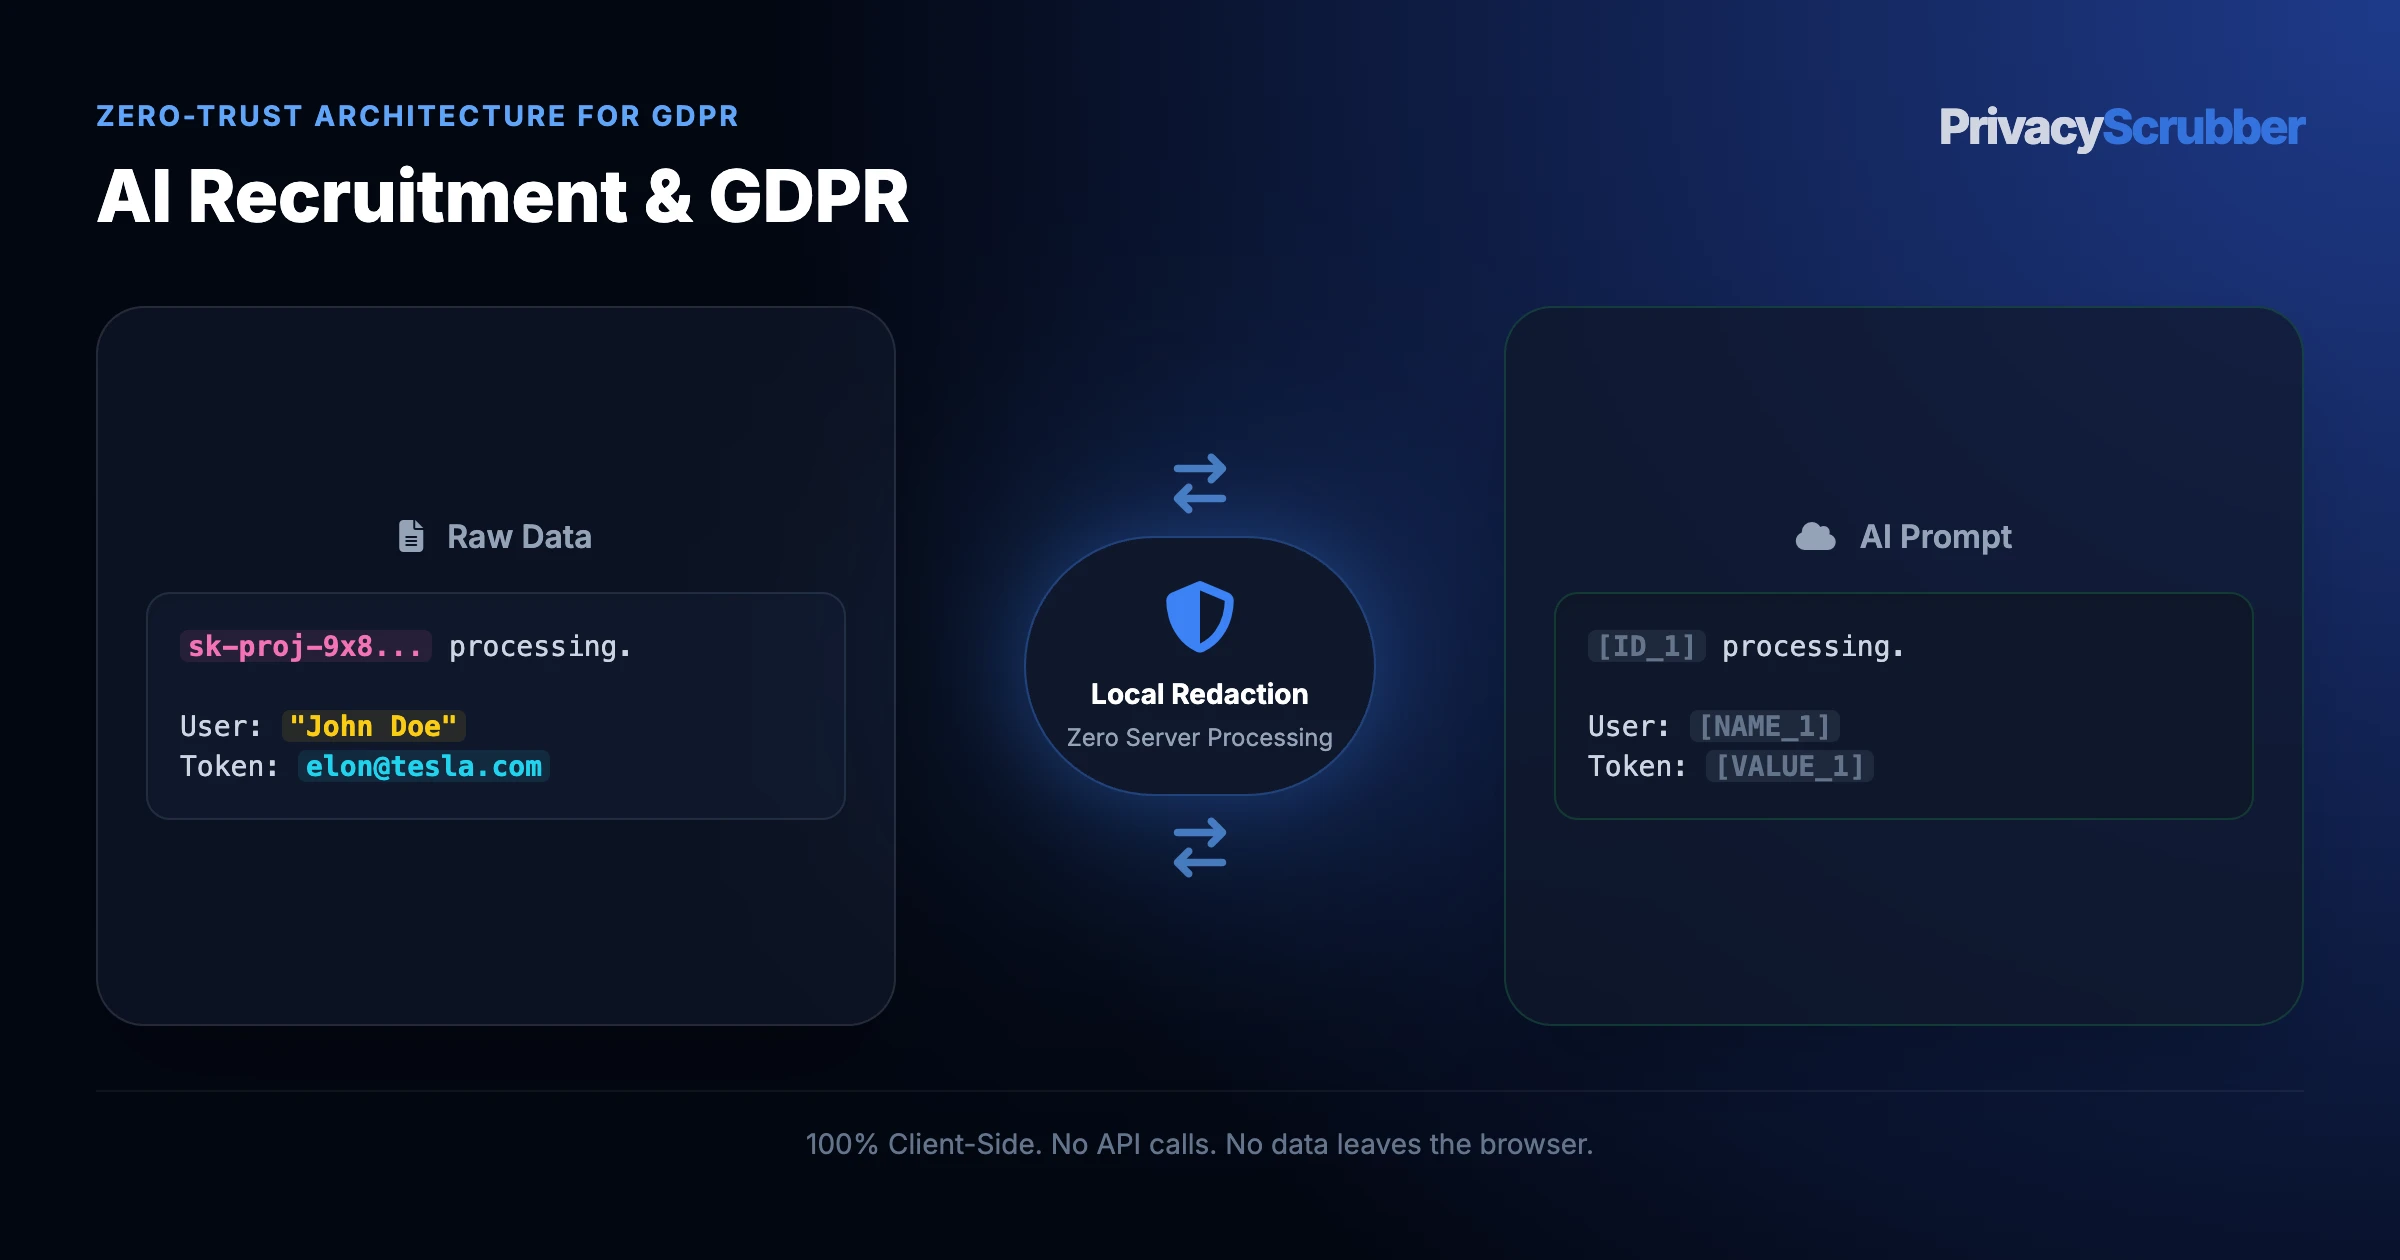
The technical safeguard for confidential AI prompts relies on intercepting sensitive strings before they cross the local network interface. By replacing actual values with deterministic placeholders (e.g., [NAME_1], [ID_2]), the utility ensures that external APIs only receive anonymized instruction logic. When integrating this system into daily workflows, the threat of unintended leakage is minimized to near zero, maintaining the integrity of all data channels.
Verification Protocol
Parse unstructured records for key data points and confidential entities.
Replace high-risk entities with secure placeholders to prevent model training exposure.
Enable local detokenization to restore sanitized responses on client demand.
Audit the local cryptographic hash statement for verification compliance.
Code du Travail Art. L2312-38 Mandates & CNIL Employee Privacy Safeguards
Under Article L2312-38 of the French Labor Code (Code du travail), the Social and Economic Committee (Comité Social et Économique - CSE) must be informed and consulted prior to any deployment of automated tools or new technology affecting work organization or personnel management. In conjunction with Article L1121-1, which prohibits any restriction on employee individual rights not justified by the nature of the task or proportionate to the aim pursued, French labor tribunals consistently penalize uncoordinated algorithmic surveillance. When paired with CNIL AI Action Plan (Plan d'action IA) guidelines and GDPR Article 88, deploying commercial LLMs without verifiable technical safeguards against worker profiling exposes French enterprises to criminal obstruction charges (délit d'entrave) and substantial regulatory fines.
French Works Council (CSE) Dossier Sanitization Architecture
The matrix below demonstrates how PrivacyScrubber tokenizes workplace evaluation records prior to LLM analysis under our GDPR Compliance AI Privacy framework:
Workplace Dossier Field
Raw Enterprise Personnel Entry
PrivacyScrubber Local Token
CSE Clearance & AI Utility
Employee Full Legal Name
Collaborateur: Antoine Rousseau (Gestionnaire Sinistres)
Collaborateur: [NAME_1] (Gestionnaire Sinistres)
Eliminates individual performance rating under Art. L1121-1
Social Security Number (NIR / Carte Vitale)
NIR: 1 85 06 75 108 234 12 (15-Digit Key)
NIR: [ID_1]
Protects national identity under Loi Informatique et Libertés
Internal Staff ID (Matricule Interne)
Matricule: FR-759201 (HRIS Payroll ID)
Matricule: [ID_2]
Blocks cross-tool correlation and employee profiling
Prevents interaction frequency and communication profiling
Aggregated Team Processing Efficiency
Turnaround Variance: -22.4% (42 min to 32.5 min avg)
Turnaround Variance: -22.4% (42 min to 32.5 min avg)
Preserved 100% Cleartext for CSE Economic Review
Suggestion Adoption & Defect Ratio
Acceptance: 84.7% | Defect Rate: 3.9% to 0.8%
Acceptance: 84.7% | Defect Rate: 3.9% to 0.8%
Preserved 100% Cleartext for System Quality Verification
French Enterprise AI Governance Pipeline with @privacyscrubber/sdk
French IT engineering teams and enterprise legal departments deploy in-memory tokenization to fulfill CSE consultation standards before routing queries to LLM APIs:
Node.js: French CSE Clearance Sanitizernpm i @privacyscrubber/sdk
import { PrivacyScrubberEngine } from '@privacyscrubber/sdk';

const engine = new PrivacyScrubberEngine({
  profile: 'HR & Resumes',
  detectSecrets: true
});

const cseWorkplaceDossier = `DOSSIER DE CONSULTATION DU COMITE SOCIAL ET ECONOMIQUE (CSE):
Societe: Mutuelle Nationale d'Assurances SAS (Paris La Defense).
Delegue a la Protection des Donnees (DPO): Me Claire Delacroix | Secretaire du CSE: Philippe Mercier.
Collaborateur Test: Antoine Rousseau (Matricule: FR-759201, NIR: 1 85 06 75 108 234 12).
Projet: Deploiement de l'assistant IA generatif pour la redaction des syntheses de sinistres.
Metrique Collective: 64 gestionnaires constatent un gain moyen de 22,4% sans profilage individuel.`;

const { sanitizedText, tokenMap } = engine.sanitize(cseWorkplaceDossier);
console.log('Sanitized Payload for CSE Consultation File:\n', sanitizedText);

// Rehydrate generated compliance memo in local client memory
const rawAiMemo = 'Avis de conformite: Selon le Code du travail Art. L2312-38, [ORG_1] empeche toute evaluation individuelle de [NAME_1].';
const finalCseClearanceMemo = engine.restore(rawAiMemo, tokenMap);
European Labor Co-Determination & Cross-Border Compliance
Watch our zero-trust engine neutralize sensitive identifiers 100% locally. No data ever leaves your device.
Local processing 0 Server logs
ZTDS_ENGINE_V1.5.0
PROMPT INPUT > Analyze the email from Bob Smith (bob.smith@corp.com, tel 555-0123) regarding project timeline.
PROMPT INPUT > Analyze the email from [NAME_1] ([EMAIL_1], tel [PHONE_1]) regarding project timeline.
GDPR Detection Profile
Our zero-trust engine is pre-hardened for GDPR workflows, automatically identifying and tokenizing the following parameters 100% locally.
NAME
Active Protection
EMAIL
Active Protection
ADDRESS
Active Protection
ID
Active Protection
IP_ADDRESS
Active Protection
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with enterprise data sovereignty.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
Compliance Decision Matrix
Field-by-Field Sanitization Rule for French Works Council (CSE) Workplace AI Consultation & Clearance Dossier (Code du travail Art. L2312-38 / CNIL)
To maintain LLM analytical context while avoiding cloud data breaches, follow this deterministic mapping before submitting prompts to third-party AI models:
Document Field / Box
Required Action
Deterministic Token
Statutory & AI Rationale
French Employee Full Names & Job Titles
REDACT
[NAME_1], [NAME_2]
Individual worker identity protected from automated surveillance under Code du travail Art. L1121-1 and GDPR Art. 88
French Social Security Number (NIR / Carte Vitale)
REDACT
[ID_1]
Highly sensitive 13/15-digit national identifier strictly regulated under French Data Protection Act (Loi Informatique et Libertés Art. 30)
Internal Staff ID (Matricule Interne)
REDACT
[ID_2]
Unique internal enterprise identifier capable of linking cross-tool activity and individual performance rating
Professional Work Email & Direct Telephone
REDACT
[EMAIL_1], [PHONE_1]
Direct communication vectors susceptible to keystroke or prompt volume profiling
Aggregated Departmental Processing Time Variance
PRESERVE
Cleartext (-22.4% average client claim turnaround)
Macro-level team performance metric required for CSE economic and technological impact assessment
Cleartext (Core Hours: 09:00 to 18:00 CET / 35-Hour Week)
Standard French collective agreement (Accord d'entreprise) parameters under Code du travail
1-Click Persona Prompt
Safe LLM Prompt Template for French Works Council (CSE) Workplace AI Consultation & Clearance Dossier (Code du travail Art. L2312-38 / CNIL)
Copy and paste this structured prompt into ChatGPT, Claude, or Gemini alongside your tokenized text to prevent LLM rejection:
You are a French Labor Law Attorney and Enterprise Data Protection Officer (DPO) specializing in Works Council (CSE) consultations under Code du travail Article L2312-38 and CNIL AI compliance guidelines. Review this sanitized workplace AI consultation dossier where employee identities, French social security NIR numbers, internal staff matricules, work emails, and phone numbers are tokenized ([NAME_1], [NAME_2], [NAME_3], [ID_1], [ID_2], [EMAIL_1], [PHONE_1]).

Tasks:
1. Assess whether this deployment documentation meets the statutory information and consultation requirements for the Social and Economic Committee (CSE) under Article L2312-38 without establishing an unlawful employee monitoring system.
2. Verify alignment with CNIL recommendations regarding the deployment of generative AI in the workplace (Plan d'action IA) and GDPR Article 88.
3. Formulate 3 technical clearance clauses for the company's internal AI charter (Charte IA d'entreprise) confirming that zero-egress client RAM sanitization eliminates risk of individual employee evaluation.

[PASTE SANITIZED TEXT HERE]
Why Data Protection Officers (DPOs) Flag Unmasked AI Prompts
Compliance auditors look for explicit safeguards: GDPR (Article 32, 5(1)(c)), and EU AI Act (2026). Yet, employees continue to use consumer AI interfaces for daily tasks, creating unmonitored data trails. Adopting the strategies in gdpr & ccpa ai compliance helps organizations build a defensible architecture that keeps records secure. The only standard that satisfies GRC is full browser-side data masking. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
Using our Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber intercepts sensitive records at the browser level via either the web interface or our automated Chrome Extension.
How to Use AI on Real European Consumer Data — Without Sending a Single Real Name
Using our Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber intercepts sensitive records at the browser level via either the web interface or our automated Chrome Extension. The software applies fast, local deterministic AST lookaround expressions to convert sensitive entities to anonymous tokens (like [NAME_1]) before they are transmitted. For compliance auditing, this mirrors the exact principles of EU AI Act compliance strategies, enabling organizations to use external AI capabilities without sacrificing data control. The Chrome Extension automates this integration by embedding a protection toggle directly in ChatGPT, Claude, and Gemini to automatically swap and restore text. Running deterministic AST lookarounds locally ensures that teams can continue using ChatGPT, Mistral, and local LLM integrations for daily queries without any third-party data collection.
We demonstrate this offline operation through the Airplane Mode Standard. Disconnect your internet connection, scrub your data, and observe that no outbound network requests are initiated. This meets the conditions of enterprise data sovereignty, validating that all client information remains on your local terminal.
ChatGPT (OpenAI) Integration
Step-by-Step Integration Guide: French Works Council (CSE) AI Clearance
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT (OpenAI):
Act as an appellate litigation consultant. Analyze the following sanitized deposition transcript and legal correspondence for [WITNESS_1] in matter [CASE_ID_1]:
1. Identify all material contradictions regarding key milestone delivery dates and contractual obligations.
2. Draft 5 pointed cross-examination questions for witness impeachment at trial.
3. Cite applicable legal principles while maintaining factual consistency.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Keep all cryptographic token placeholders ([PLAINTIFF_1], [DEFENDANT_1], [WITNESS_1], [CASE_ID_1], [PATENT_ID_1]) strictly unchanged in your analysis for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT (OpenAI) outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: ABA Model Rule 1.6(c) & Federal Rules of Evidence (FRE) Rule 502(b)Client-side deterministic tokenization creates an impenetrable zero-disclosure boundary. Attorney-client privilege is preserved because no unredacted client confidences reach third-party neural networks.
GDPR Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
Zero-Trust Verified
Security teams deploy client-side sanitization to keep outbound AI prompts free of sensitive organizational data, avoiding complex multi-party DPA negotiations.
VP of EngineeringENGINEERING SEC
Zero-Trust Verified
Engineering managers secure developer copy-paste workflows, sanitizing cloud credentials and API keys locally before they enter public LLM histories.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for GDPR compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any gdpr text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for GDPR Teams.
Why is prior CSE consultation mandatory before deploying generative AI in France?
Under Article L2312-38 of the French Labor Code (Code du travail), the CSE must be informed and consulted prior to the introduction of any new technology or automated personnel management system that affects employment conditions, work organization, or vocational training. Failing to consult the CSE constitutes the criminal offense of obstruction (délit d'entrave) under Article L2317-1.
What does the CNIL mandate regarding generative AI and employee monitoring in the workplace?
The CNIL strictly prohibits the use of generative AI tools to monitor employee activity, track response times, or evaluate individual performance without a legally valid purpose, prior consultation of employee representatives, and an updated AIPD (Data Protection Impact Assessment). The CNIL requires employers to implement technical filtering to prevent employee personal data and NIR numbers from entering commercial AI pipelines.
How does PrivacyScrubber protect French employee identities and NIR numbers from cloud leakage?
PrivacyScrubber operates 100% in local device RAM with zero cloud egress (Airplane Mode verified). French employee names, professional email addresses, 13/15-digit NIR social security numbers, internal matricules, and direct phone lines are tokenized into abstract placeholders (e.g., [NAME_1], [ID_1], [EMAIL_1]) before prompt submission, guaranteeing that external AI providers never ingest employee identities.
Can French enterprises use PrivacyScrubber to formalize an enterprise AI charter (Charte IA)?
Yes. By establishing client-side RAM tokenization as the mandatory technical standard in the company's internal AI charter (Charte d'utilisation de l'IA) and collective agreements (Accord d'entreprise), employers provide concrete, auditable evidence to the CSE and DPO that generative AI cannot be repurposed for employee surveillance or behavioral evaluation.
Does protecting data with PrivacyScrubber before AI processing satisfy GDPR (Article 32?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with GDPR (Article 32 because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for gdpr workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match gdpr-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask gdpr data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your gdpr data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Scrub in RAM" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard deterministic AST lookaround engine to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
How do I make AI prompts GDPR compliant?
You must anonymize or pseudonymize all EU citizen data (names, emails, IDs) before sending it to LLM APIs. PrivacyScrubber handles this automatically at the browser level. Avoid Article 99 fines instantly with our PRO tier at $15/mo.
Does OpenAI train on my data?
By default on consumer tiers, yes. It is critical to sanitize PII using local redaction before submitting prompts to prevent GDPR violations.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
Why Data Protection Officers (DPOs) Flag Unmasked AI Prompts
Compliance auditors look for explicit safeguards: GDPR (Article 32, 5(1)(c)), and EU AI Act (2026). Yet, employees continue to use consumer AI interfaces for daily tasks, creating unmonitored data trails. Adopting the strategies in gdpr & ccpa ai compliance helps organizations build a defensible architecture that keeps records secure. The only standard that satisfies GRC is full browser-side data masking. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
How to Use AI on Real European Consumer Data — Without Sending a Single Real Name
Using our Zero-Trust Data Sanitization (ZTDS) engine, PrivacyScrubber intercepts sensitive records at the browser level via either the web interface or our automated Chrome Extension. The software applies fast, local deterministic AST lookaround expressions to convert sensitive entities to anonymous tokens (like [NAME_1]) before they are transmitted. For compliance auditing, this mirrors the exact principles of EU AI Act compliance strategies, enabling organizations to use external AI capabilities without sacrificing data control. The Chrome Extension automates this integration by embedding a protection toggle directly in ChatGPT, Claude, and Gemini to automatically swap and restore text. Running deterministic AST lookarounds locally ensures that teams can continue using ChatGPT, Mistral, and local LLM integrations for daily queries without any third-party data collection.
Is PrivacyScrubber safe for cse chatgpt consultation, code du travail l2312-38 ia generative, cnil intelligence artificielle travail cse, accord entreprise ia generative, employee monitoring ai cnil rgpd article 88?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with cse chatgpt consultation, code du travail l2312-38 ia generative, cnil intelligence artificielle travail cse, accord entreprise ia generative, employee monitoring ai cnil rgpd article 88, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for gdpr?
Our engine includes 30 specialized industry profiles optimized for gdpr data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.
Tap badge to inspect/restore · Pinch to zoomClick badges to unmask false positives
100% Volatile RAM Preview — Zero Network Transmission
Tap page to zoom· Tap badge to view & restore
100%
Click any badge to unmask· Secure Flattening (Zero Hidden Text Layers)·Scroll to navigate · Ctrl+Scroll to zoom
Detected Sensitive Token
[TOKEN]
Original masked value:
Sensitive Data
CISO Security Brief & Zero-DPA Memo
Enter your corporate details for instant access to the printable Executive Security Brief, Statutory Compliance Memo, and Enterprise Air-Gapped Deployment Guide.
Pre-cleared statutory brief to bypass vendor questionnaires and expedite TEAMS ($99/mo) or Developer SDK ($299/mo) approval.
Select Procurement Track:
ZTDS™ VERIFIED0-Byte Egress · No DPA · Patent Pending (IL 331905 · WIPO: B17B) · 2-Page Audit Brief
Manual Activation
Unlock your features
Invalid or expired license key
License Activated
Your features are unlocked.
Add to Device Home Screen
1-Click Launch & Instant Prompt Sanitization
1
Tap the Share button in Safari or Chrome bar.
2
Scroll down and select Add to Home Screen.
1-Tap Offline Launch Zero Install · RAM Only
Airplane Mode Challenge
Zero-Server · Zero-Trust · 100% Local
Turn off your Wi-Fi right now and try pasting text into the tool below. It processes 100% in your local RAM without sending any network requests.
Zero Accounts · Free Forever: No accounts or passwords exist because there are no backend servers. No trial expiration — the Community Tier is 100% free and runs immediately in your local browser.