
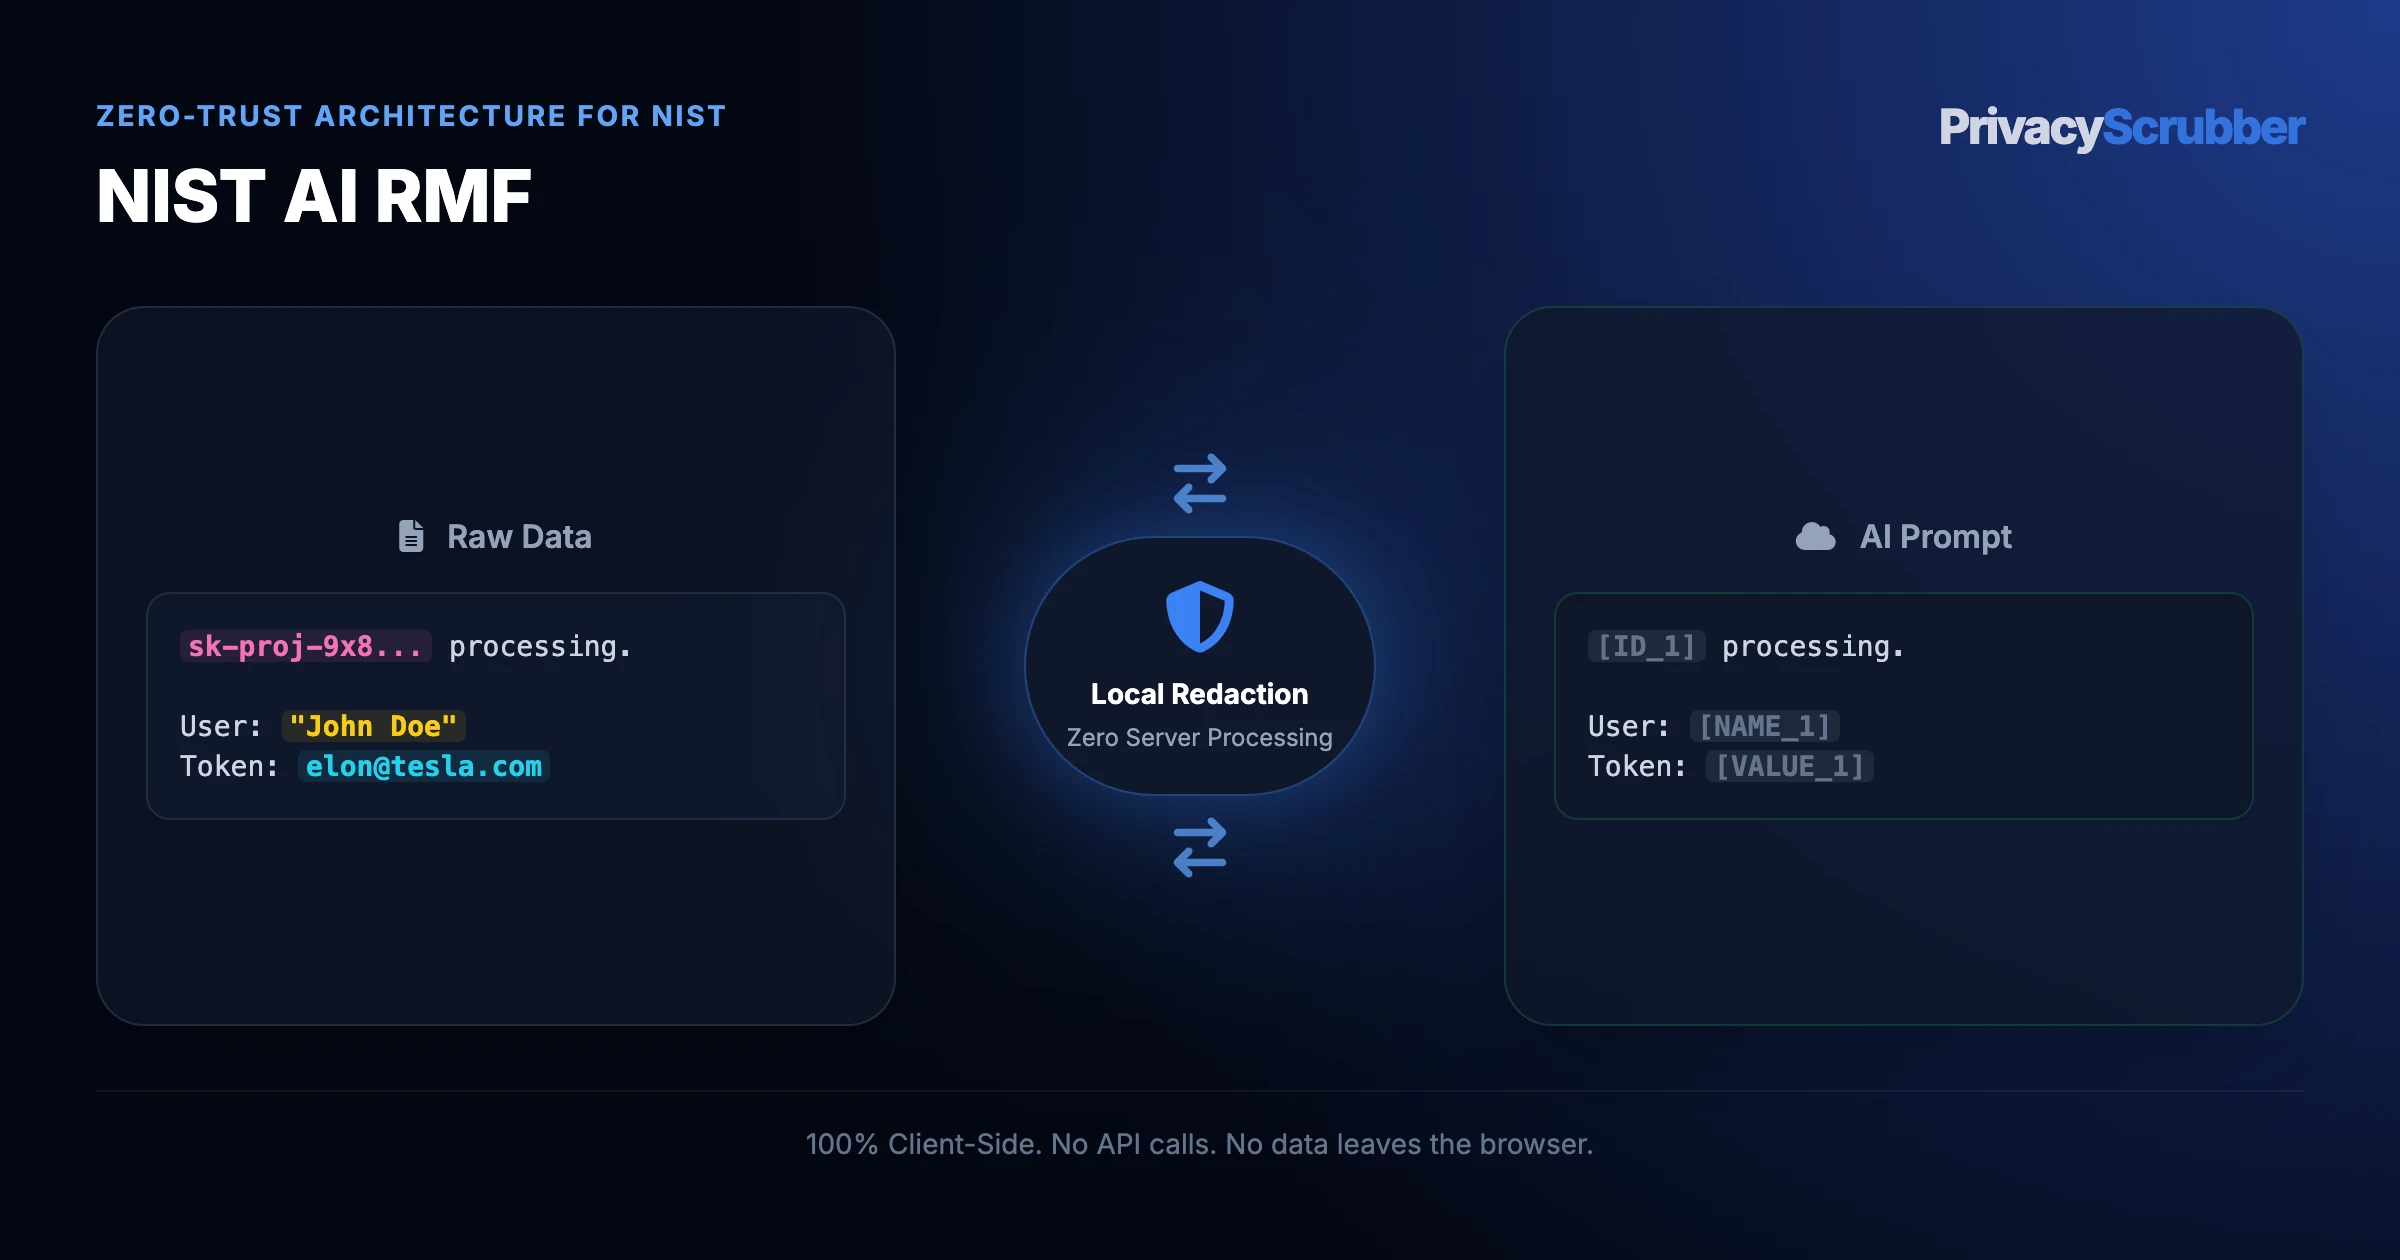
NIST AI RMF 1.0 establishes four core functions: GOVERN, MAP, MEASURE, and MANAGE. PrivacyScrubber operates as a technical enforcement mechanism across all four, keeping raw PII completely out of the AI risk surface.
How Raw NIST AI RMF Leaks Inside LLM Logs
When agency IT managers accelerate NIST AI RMF through local government systems, unstructured enterprise AI governance bypasses firewalls. Apply NIST AI privacy guides to keep [NAME_1] lookups on-device.
In NIST AI RMF, productivity clashes with PT-3) and NIST AI Risk Management Framework (AI RMF) due to raw NIST AI RMF mapping retention. Align enterprise AI with the NIST AI Risk Management Framework (AI RMF 1.0). Map Govern, Map, Measure, and Manage functions to local ZTDS RAM controls. Endpoint scrubbing converts NIST AI RMF mapping to [EMAIL_1] first.
NIST AI RMF 1.0 Compliance Architecture
The NIST Artificial Intelligence Risk Management Framework (AI RMF 1.0) provides a voluntary standard for organizations deploying AI systems. Managing privacy risks (under MANAGE and GOVERN functions) requires practical controls to minimize PII exposure in LLM pipelines, supplementing the GDPR compliance framework.
Framework Core Alignment
OWASP LLM Top 10 mitigation strategies and the AI Governance Playbook confirm that PrivacyScrubber aligns directly with the NIST AI RMF core sub-functions:
- GOVERN 1.2: Promotes a culture of risk management by enforcing corporate AI policies dynamically.
- MAP 1.5: Tracks and classifies PII leakage vectors at the client workstation prior to egress.
- MEASURE 2.6: Quantifies masked entity counts via browser-local statistics.
- MANAGE 1.5: Enforces active PII masking, preventing data spillages into public LLMs.
Deterministic Token Mapping for NIST AI RMF
Effective sanitization of NIST AI RMF requires stripping direct identifiers while keeping structural and quantitative context intact for model reasoning:
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Private Records in NIST AI RMF | REDACT | [CLEARANCE_1] | Replaces direct PII with [CLEARANCE_1] inside volatile client memory. |
| Routing Endpoints (enterprise AI governance) | REDACT | [CLEARANCE_1] | Blocks contact linkage when agency IT managers analyze NIST AI Risk Management Framework batches. |
| Entity Names (NIST) | REDACT | [NAME_1] | Maintains multi-turn coherence on NIST AI Risk Management Framework without exposing raw parties. |
| Non-PII Workflow Constraints | PRESERVE | Cleartext Context | Preserves reasoning constraints across NIST AI RMF prompts sent offline. |
| Domain Instructions (NIST) | PRESERVE | Cleartext Logic | Retains workflow intent so agency IT managers get actionable enterprise AI governance outputs. |
| Numeric Totals & Ratios (NIST AI RMF mapping) | PRESERVE | Cleartext ($ / %) | Enables accurate calculations across NIST AI RMF without revealing identities. |
Bijective Prompt Blueprint for NIST AI RMF
Submit this prompt wrapper with your masked NIST AI RMF input so the AI reasons over symbolic tokens without altering placeholder tags:
Review NIST AI Risk Management Framework workflow for NIST AI RMF under PT-3) and NIST AI Risk Management Framework (AI RMF).
1. Inspect interactions between [NAME_1] and [CLEARANCE_1].
2. Deliver concise steps preserving every bracketed token.

[INSERT SCRUBBED TEXT]
Review NIST AI Risk Management Framework workflow for NIST AI RMF under PT-3) and NIST AI Risk Management Framework (AI RMF).
1. Inspect interactions between [NAME_1] and [CLEARANCE_1].
2. Deliver concise steps preserving every bracketed token.

[INSERT SCRUBBED TEXT]
Audit Readiness Across NIST AI RMF Workstations
Operating under PT-3) and NIST AI Risk Management Framework (AI RMF), agency IT managers apply NIST 800-53 AI data minimization to standardize NIST AI Risk Management Framework conversion into [EMAIL_1] without slowing local government systems.
Running AI on NIST AI RMF Without Sending Real Identifiers
Replacing destructive blanks, ZTDS™ turns NIST AI Risk Management Framework in NIST AI RMF into reversible [NAME_1] tokens via offline endpoint scrubber, honoring transparent OpenAI client PII redaction wrapper for node.js & typescript.
Zero network handshakes fire when NIST AI RMF masks NIST AI RMF mapping offline, providing deterministic evidence matching in-memory PII middleware for LangChain & llamaindex AI pipelines.
