
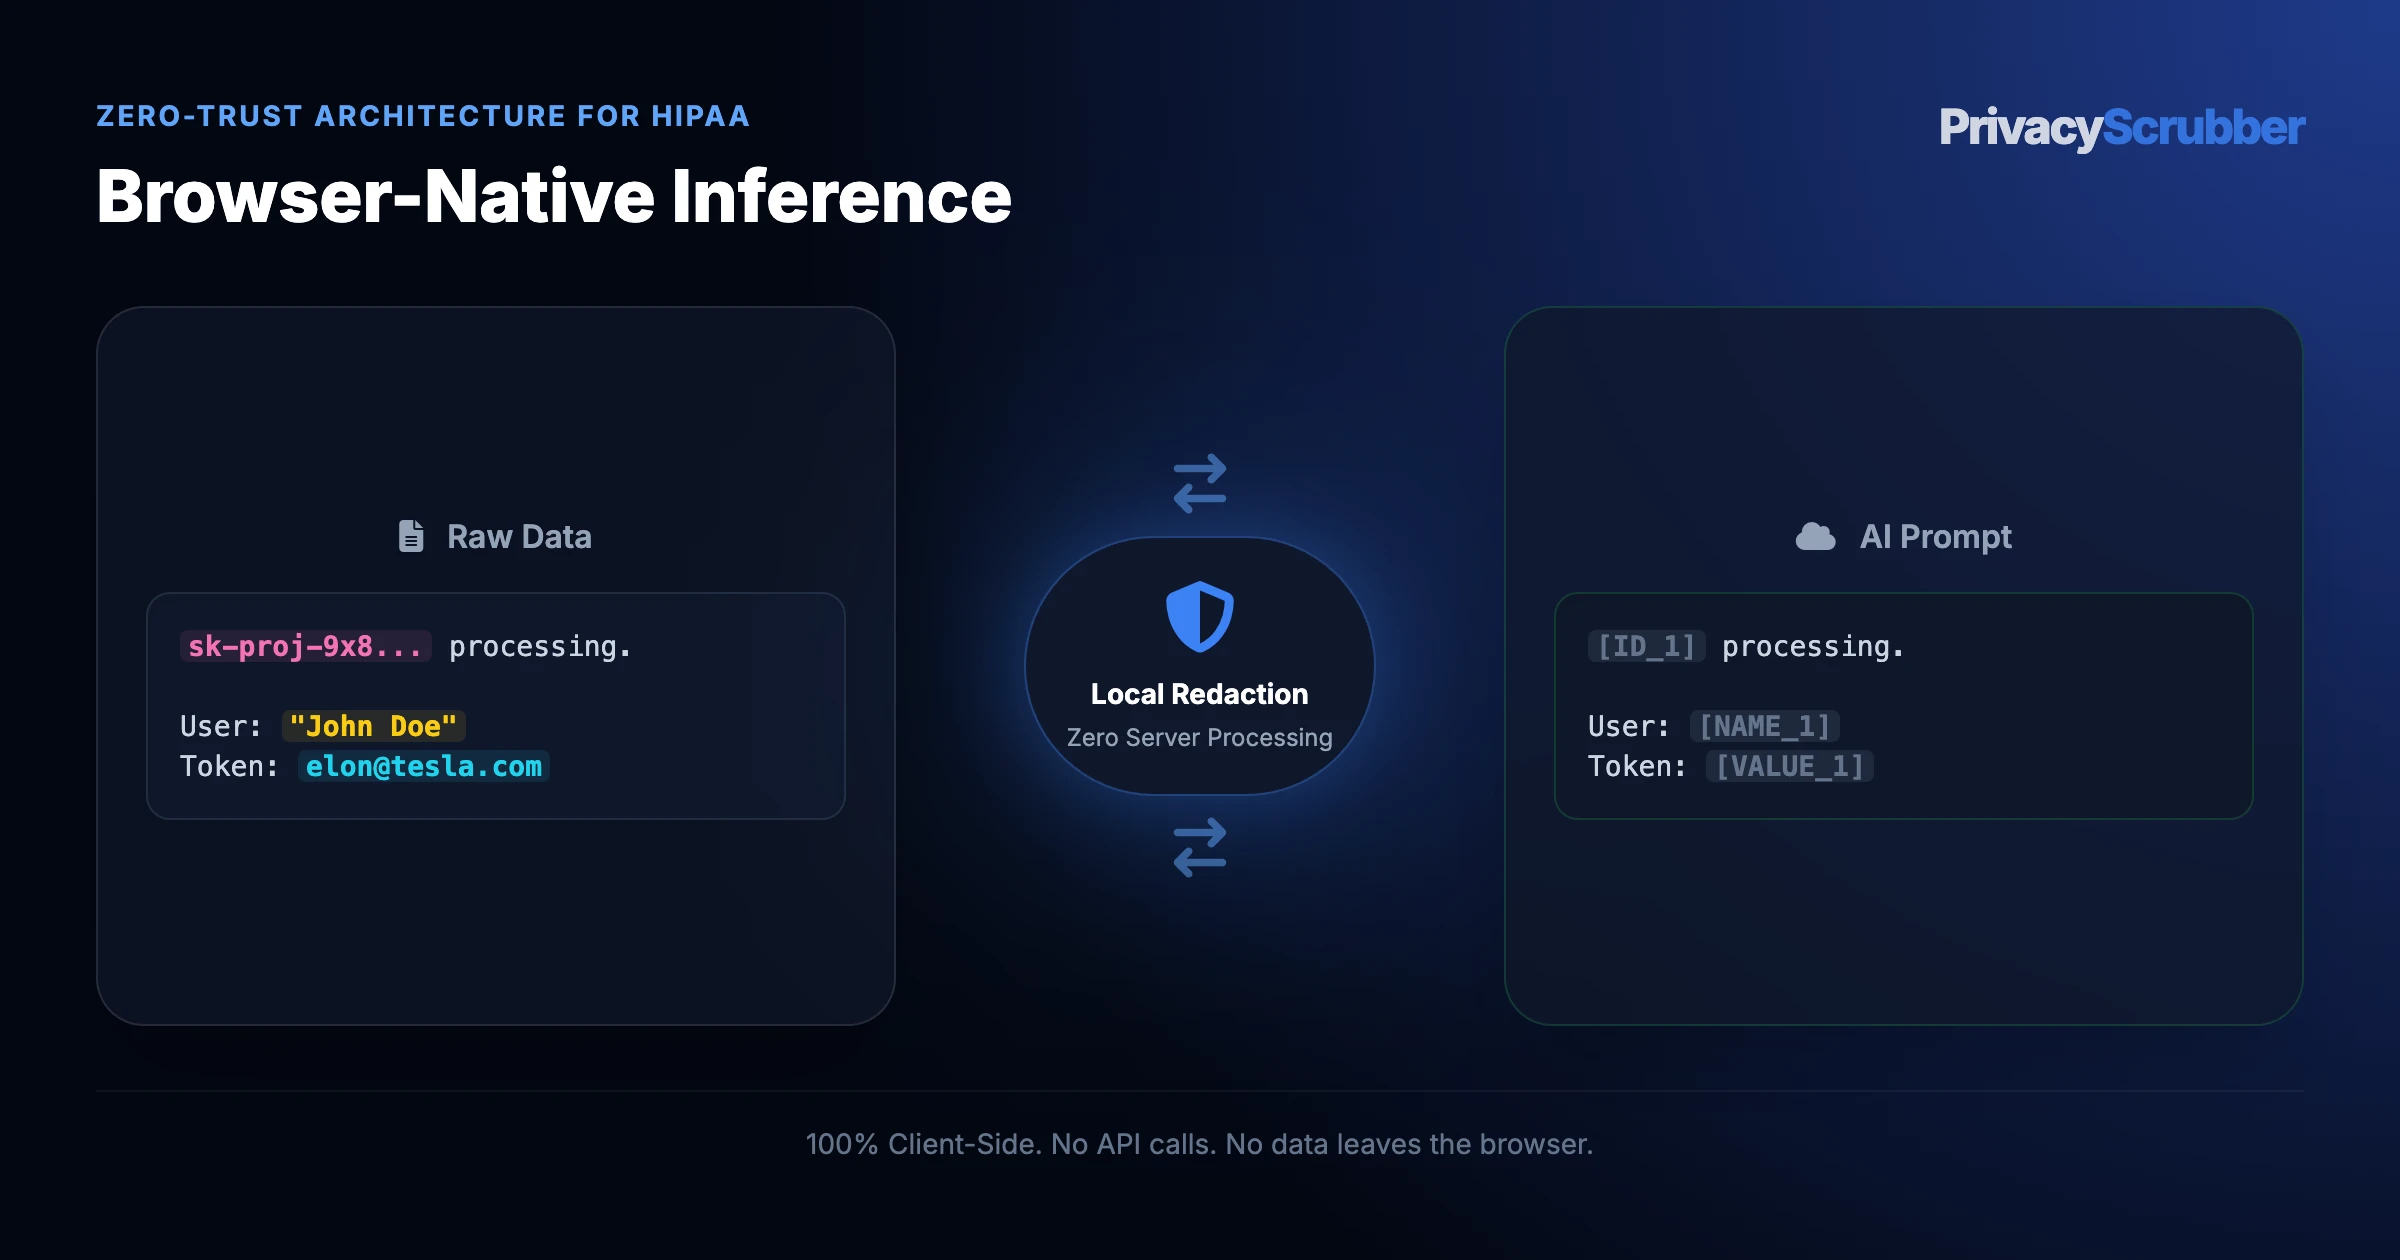
Healthcare regulations strictly monitor Protected Health Information (PHI) in transit. By executing deterministic PII tokenization using AST contextual pattern rules entirely within volatile browser memory (<1ms latency), PrivacyScrubber establishes an air-gapped privacy perimeter where data never leaves the tab.
Data Leakage Risks in Browser-Native Sanitization for Healthcare and Clinical Teams
Keeping Browser-Native Sanitization off vendor telemetry starts with local HIPAA Safe Harbor RAM engine. healthcare providers pair Cerner with HIPAA AI privacy guides patterns to mask browser-native sanitization in <1ms.
Feeding HIPAA-compliant AI and privacy by architecture to external AI triggers unmasked HIPAA-compliant AI exposure immediately. Sanitize PHI directly in local browser RAM. Redact sensitive PII in local browser RAM with zero server egress or cloud leaks. Downstream filters never catch cleartext inside EPIC.
Edge AI in Clinical Workflows: Privacy by Design
The clinical advantages of generative AI (such as synthesizing EHR charts, summarizing treatment plans, or translating diagnostic logs) are regularly halted by patient privacy concerns. Sending raw **Protected Health Information (PHI)** to external cloud services without a signed **Business Associate Agreement (BAA)** is a direct violation of HIPAA regulations. Moving the sanitization layer directly onto the client browser tab completely resolves this compliance standoff, ensuring you have a HIPAA compliant ChatGPT workflow.
Browser-Native ZTDS Technical Architecture
- • deterministic ZTDS™ detection Syntax: High-speed regex engines executing in volatile browser RAM at 8.4 MB/s (<1ms latency) with zero cloud dependencies.
- • WebAssembly (WASM) Sandbox: Compiles native cryptographic primitives and offline OCR/PDF raster flattening tools directly in the browser tab, bypassing external server pipelines.
- • Volatile Session Isolation: Cryptographic session maps isolated strictly per tab, never written to disk, and permanently purged on tab reload or closure.
Eliminating the BAA Network Transmission Crisis
Traditional data loss prevention (DLP) requires routing clinical inputs to cloud proxy APIs, simply moving the HIPAA risk from one vendor to another. In contrast, using offline redaction, PrivacyScrubber's **Zero-Trust Data Sanitization (ZTDS)** operates exclusively on-device. By redacting patient names, dates, and record numbers locally, data is legally de-identified under the **HIPAA Safe Harbor** rule before it is copied or transmitted, structurally satisfying HIPAA Security Safeguards without the operational overhead of a BAA.
Deterministic Token Mapping for Browser-Native Sanitization
This field-level specification ensures Browser-Native Sanitization prompts retain 100% mathematical and semantic accuracy with zero cleartext PII egress:
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Keys & Account Codes (browser-native sanitization) | REDACT | [MRN_1] | Stops browser-native sanitization credentials from entering cloud telemetry on Browser-Native Sanitization. |
| Internal IDs inside Browser-Native Sanitization | REDACT | [PATIENT_1] / [MRN_1] | Prevents unmasked HIPAA-compliant AI exposure via pre-send offline endpoint scrubber substitution. |
| Private Records in Browser-Native Sanitization | REDACT | [DOB_1] | Replaces direct PII with [DOB_1] inside volatile client memory. |
| Numeric Totals & Ratios (browser-native sanitization) | PRESERVE | Cleartext ($ / %) | Enables accurate calculations across Browser-Native Sanitization without revealing identities. |
| Aggregation Counts & Deltas | PRESERVE | Cleartext Metrics | Supports statistical analysis of HIPAA-compliant AI without linking individuals. |
| HIPAA Privacy Rule and Safe Harbor De-identification standards Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map Browser-Native Sanitization findings directly against policy clauses. |
Safe LLM Prompt Template for Browser-Native Sanitization
Attach this guardrail prompt to any redacted Browser-Native Sanitization session so downstream models keep symbolic tags intact for instant restoration:
Role: HIPAA advisor evaluating Browser-Native Sanitization.
Sanitized tokens ([PATIENT_1], [MRN_1]) mask all HIPAA-compliant AI identifiers.
1. Flag operational gaps in browser-native sanitization.
2. Recommend HIPAA Privacy Rule and Safe Harbor De-identification standards fixes.
3. Keep [PATIENT_1] unchanged.

[PASTE BROWSER-NATIVE SANITIZATION TEXT]
Role: HIPAA advisor evaluating Browser-Native Sanitization.
Sanitized tokens ([PATIENT_1], [MRN_1]) mask all HIPAA-compliant AI identifiers.
1. Flag operational gaps in browser-native sanitization.
2. Recommend HIPAA Privacy Rule and Safe Harbor De-identification standards fixes.
3. Keep [PATIENT_1] unchanged.

[PASTE BROWSER-NATIVE SANITIZATION TEXT]
Governance Requirements Governing Browser-Native Sanitization
Meeting HIPAA Privacy Rule and Safe Harbor De-identification standards data minimization during Browser-Native Sanitization leverages HIPAA de-identification for AI patterns to neutralize unmasked HIPAA-compliant AI exposure via volatile [DOB_1] mapping.
How to Sanitize Browser-Native Sanitization in Local RAM (Zero Cloud Egress)
HIPAA Safe Harbor RAM engine fixes Browser-Native Sanitization leaks by replacing browser-native sanitization with [MRN_1] inside client memory while mirroring redact claim numbers and policy ids for AI restoration.
Sever internet access, tokenize HIPAA-compliant AI into [MRN_1] for Browser-Native Sanitization, and confirm zero sockets open under clinical trial data anonymizer for AI research.
