
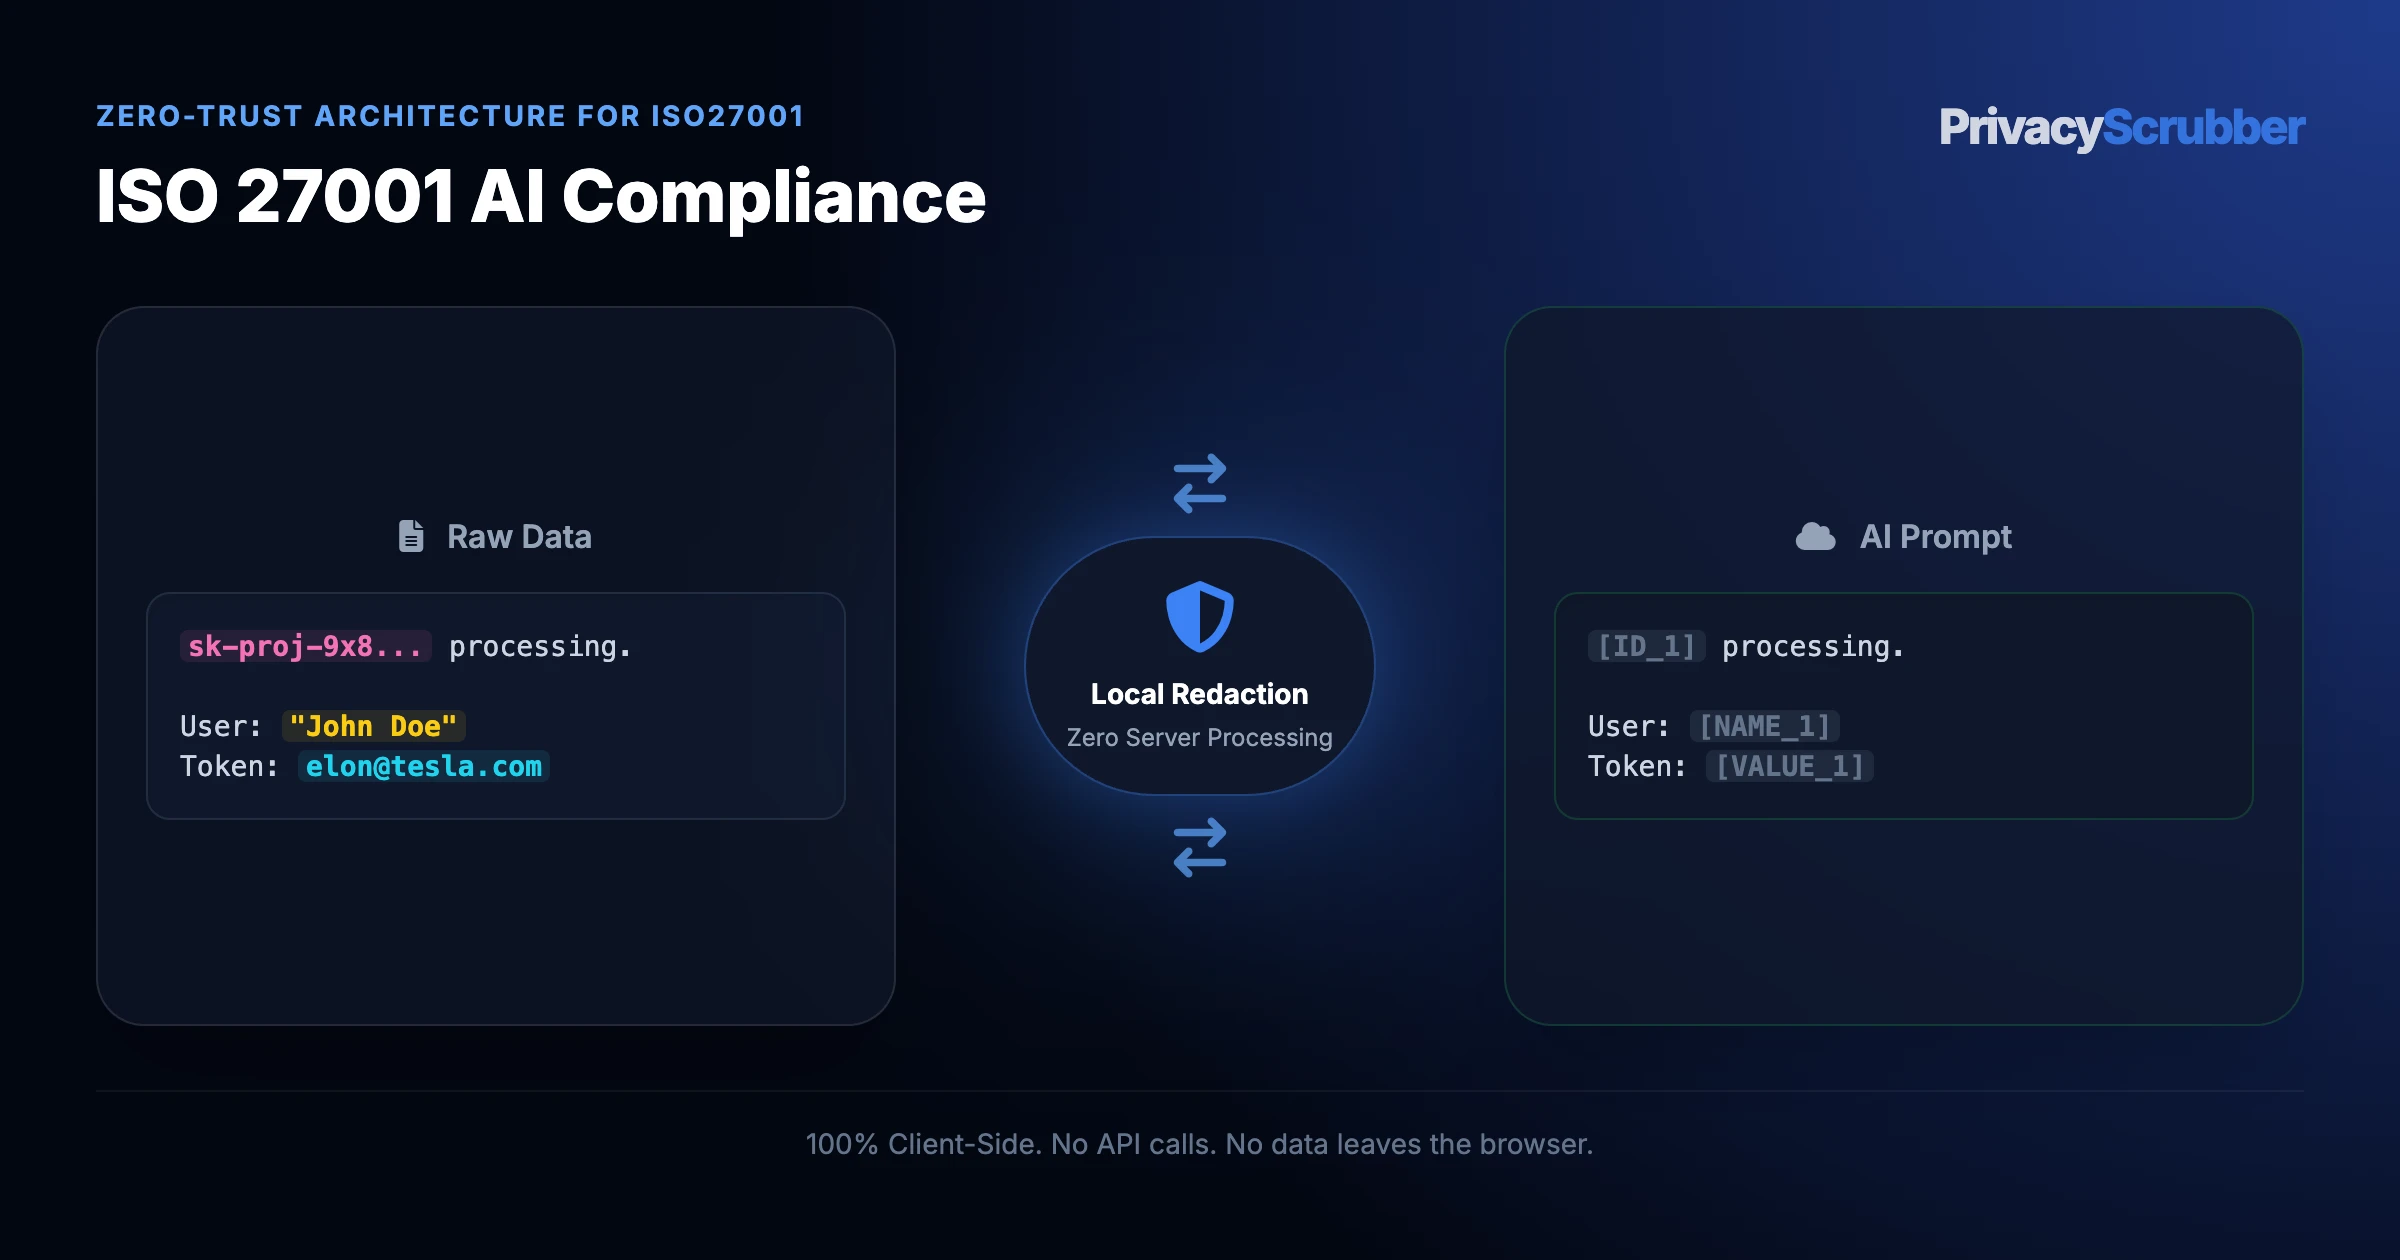
ISO/IEC 27001:2022 Control A.8.11 explicitly requires data masking in accordance with the organization's access control policy. Utilizing client-side Zero-Trust Data Sanitization (ZTDS) to mask sensitive data before it hits generative AI APIs satisfies this mandatory control without restricting employee productivity.
What Information Security Leads Send to AI During ISO 27001 AI Compliance
Safeguarding ISO 27001 AI Compliance is critical when ISMS managers run Audit management software. Unmasked ISO 27001 AI compliance triggers ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) egress gaps; our ISO 27001 AI privacy guides explain local ISO 27001 A.8.11 local masker shielding.
Align AI tool usage with ISO 27001 security controls using local PII scrubbing. Client-side RAM tokenization satisfies enterprise confidentiality norms. Relying on cloud DLP proxies for ISO 27001 AI Compliance still sends cleartext ISO 27001 AI compliance externally, leaving ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) egress gaps unresolved.
ISO/IEC 27001:2022 Control A.8.11 Data Masking for AI Workflows
Under the updated ISO 27001:2022 standard, information security management systems (ISMS) must implement formal controls to protect sensitive corporate assets. Generative AI tools like ChatGPT represent a major shadow IT threat, risking the exfiltration of intellectual property and named databases. To maintain compliance without locking down AI use cases, organizations must adopt active data masking protocols.
Essential ISO 27001 Controls Met by ZTDS
- • Control A.8.11 (Data Masking): Sanitizes names, phone numbers, and custom database parameters locally in browser RAM before external API transit.
- • Control A.8.12 (Data Leakage Prevention): Acts as a hard UI-level shield, blocking the transmission of sensitive raw text string patterns to public cloud systems.
- • Control A.5.23 (Use of Cloud Services): Reduces third-party cloud data exposure, preventing external model providers from storing or training on corporate assets.
Hardening the Corporate ISMS
In an external ISO 27001 audit, standard administrative rules ('please do not paste data') are considered weak controls. External auditors demand technical, verifiable enforcement. PrivacyScrubber offers this enforcement without requiring heavy, expensive local server proxies. Because the software operates 100% locally in the browser, it is completely immune to cloud-side data harvesting, ensuring your ISMS boundaries remain clean and aligned.
What to Redact vs. Preserve in ISO 27001 AI Compliance
Follow this bijective sanitization schedule for ISO 27001 AI Compliance so downstream AI completions can be detokenized locally in one click:
| Payload Element | Policy | ZTDS™ Token | Compliance & Reasoning Impact |
|---|---|---|---|
| Routing Endpoints (ISMS AI workflows) | REDACT | [SECRET_1] | Blocks contact linkage when ISMS managers analyze ISO 27001 AI compliance batches. |
| Entity Names (ISO 27001) | REDACT | [NAME_1] | Maintains multi-turn coherence on ISO 27001 AI compliance without exposing raw parties. |
| Subject Identifiers (ISO 27001 AI compliance) | REDACT | [NAME_1] | ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) guard prevents Audit management software from retaining personal ISO 27001 AI Compliance records. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets Audit management software trace root causes cleanly inside sanitized information security AI tools logs. |
| Non-PII Workflow Constraints | PRESERVE | Cleartext Context | Preserves reasoning constraints across ISO 27001 AI Compliance prompts sent offline. |
| Domain Instructions (ISO 27001) | PRESERVE | Cleartext Logic | Retains workflow intent so ISMS managers get actionable ISMS AI workflows outputs. |
Copy-Paste Safe Instruction for ISO 27001 AI Compliance
Attach this guardrail prompt to any redacted ISO 27001 AI Compliance session so downstream models keep symbolic tags intact for instant restoration:
Objective: ISO 27001 AI Compliance evaluation with zero PII exposure.
Masked via ISO 27001 A.8.11 local masker using [ID_1] & [SECRET_1].
1. Extract structured takeaways for information security AI tools.
2. Keep surrogate labels intact.

[PASTE PAYLOAD]
Objective: ISO 27001 AI Compliance evaluation with zero PII exposure.
Masked via ISO 27001 A.8.11 local masker using [ID_1] & [SECRET_1].
1. Extract structured takeaways for information security AI tools.
2. Keep surrogate labels intact.

[PASTE PAYLOAD]
Minimizing ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) Exposure in ISO 27001 AI Compliance
Under ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management), sending raw information security AI tools records to Audit management software creates audit risk; ISO 27001 AI data classification details technical safe harbor inside local RAM.
3-Step Local RAM Redaction for ISO 27001 AI Compliance Workflows
With ISO 27001 A.8.11 local masker, ISMS managers sanitize ISO 27001 AI Compliance at keyboard speed—mapping ISO 27001 AI compliance to [ACCOUNT_1] in <1ms with zero upload per use ChatGPT at work without paying for enterprise.
Cut Wi-Fi to prove ISO 27001 AI Compliance isolation—ISO 27001 A.8.11 local masker converts information security AI tools locally in <1ms, aligning with chromadb local PII sanitizer benchmarks.
