
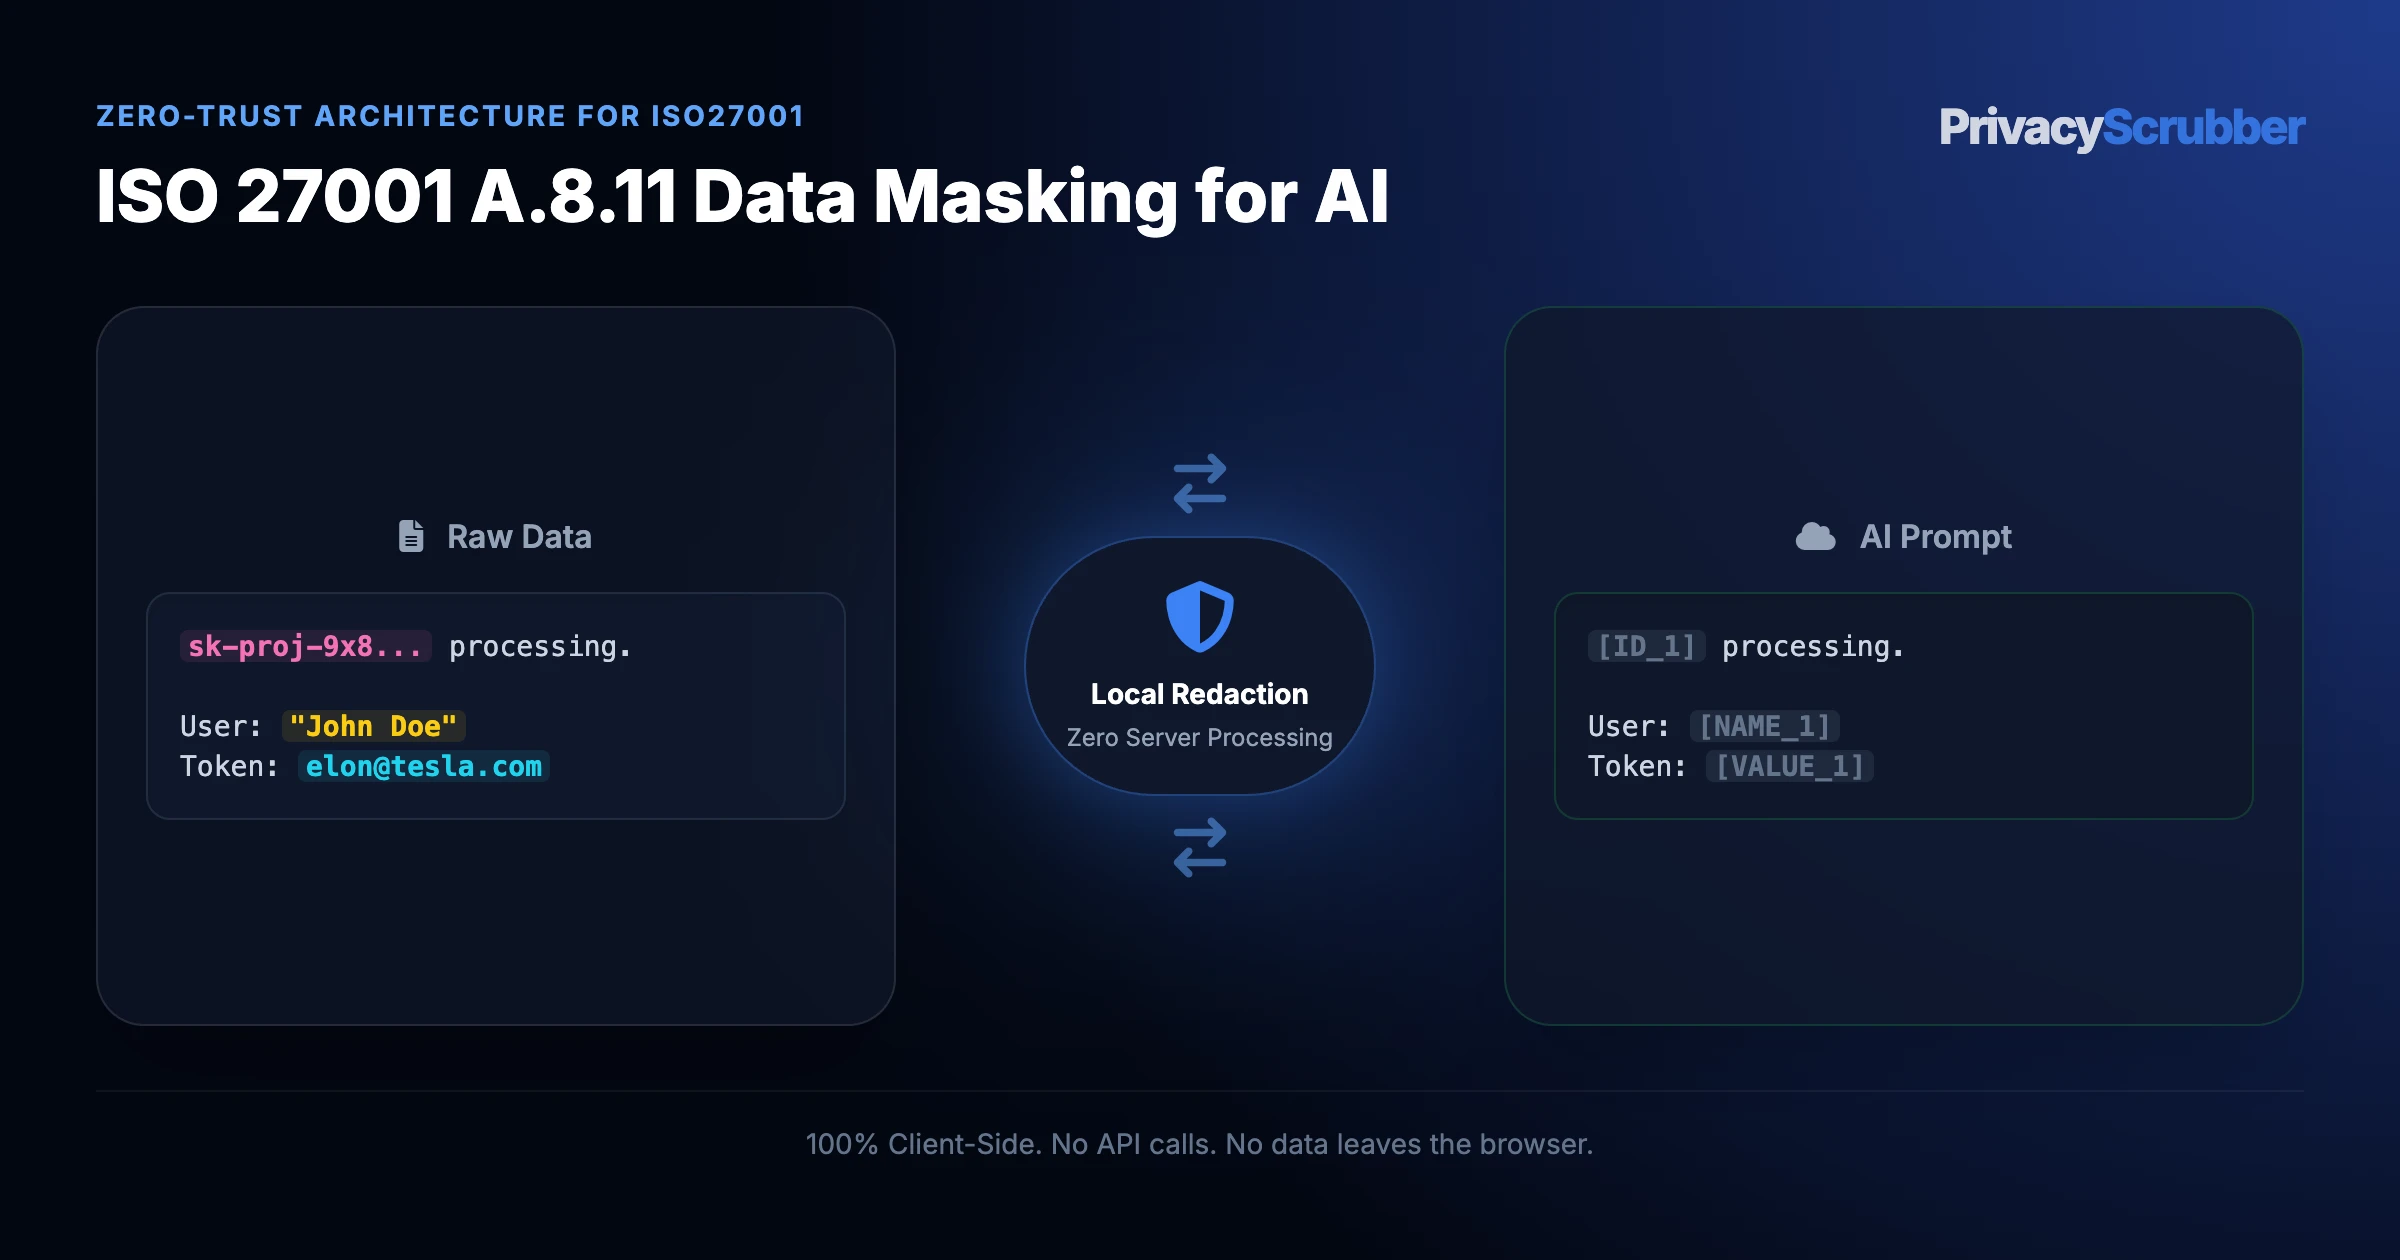
ISO 27001:2022 introduced A.8.11 Data Masking as a new control (it did not exist in the 2013 version). This control specifically requires that PII be masked, pseudonymized, or anonymized when used in AI or analytics contexts. PrivacyScrubber is purpose-built for this control, providing browser-side pseudonymization that satisfies A.8.11 without any server infrastructure.
Prompt Privacy Failures in ISO 27001 A.8.11 Data Masking for AI Workflows
Safeguarding ISO 27001 A.8.11 Data Masking for AI is critical when IT directors run Audit management software. Unmasked ISO 27001 A.8.11 data masking triggers ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) egress gaps; our ISO 27001 AI privacy guides explain local local RAM (ISO 27001) shielding.
Satisfy ISO 27001:2022 Annex A.8.11 data masking requirements for AI workflows. Automate local PII tokenization in RAM before ChatGPT or Copilot prompts. Across ISO 27001 apps, ISO 27001 A.8.11 Data Masking for AI embeds regulated ISO 27001 A.8.11 data masking attributes vulnerable to ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) egress gaps under ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management).
Enforcing ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) on ISO 27001 A.8.11 data masking
Satisfy ISO 27001:2022 Annex A.8.11 data masking requirements for AI workflows. Automate local PII tokenization in RAM before ChatGPT or Copilot prompts. Without local pre-scrubbing via local RAM (ISO 27001), IT directors handle ISO 27001 A.8.11 data masking payloads that leak straight into secure AI proxies queues.
Reversible tokenization turns ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) compliance into an automatic habit for IT directors, blocking annex A data masking control leakage before Audit management software inference begins.
ZTDS™ Field Governance for ISO 27001 A.8.11 Data Masking for AI Workflows
Follow this bijective sanitization schedule for ISO 27001 A.8.11 Data Masking for AI so downstream AI completions can be detokenized locally in one click:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Tax, Token & Session Strings (ISO 27001 AI compliance) | REDACT | [ID_1] | Zero-egress tokenization keeps ISO 27001 A.8.11 Data Masking for AI identifiers off vendor storage. |
| Keys & Account Codes (ISO 27001 AI compliance) | REDACT | [ID_1] | Stops ISO 27001 AI compliance credentials from entering cloud telemetry on ISO 27001 A.8.11 Data Masking for AI. |
| Internal IDs inside ISO 27001 A.8.11 Data Masking for AI | REDACT | [NAME_1] / [ID_1] | Prevents ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) egress gaps via pre-send local RAM (ISO 27001) substitution. |
| Aggregation Counts & Deltas | PRESERVE | Cleartext Metrics | Supports statistical analysis of ISO 27001 A.8.11 data masking without linking individuals. |
| ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map ISO 27001 A.8.11 Data Masking for AI findings directly against policy clauses. |
| Schema & Formatting (ISO 27001 A.8.11 Data Masking for AI) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for Audit management software on ISO 27001 A.8.11 data masking. |
Bijective Prompt Blueprint for ISO 27001 A.8.11 Data Masking for AI
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Context: Local RAM scrubbing converted ISO 27001 A.8.11 data masking to [NAME_1] / [SECRET_1] for ISO 27001 A.8.11 Data Masking for AI.
1. Audit logic and risks.
2. Keep output aligned with ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management).
3. Retain all tokens untouched.

[PASTE CLEAN PAYLOAD]
Context: Local RAM scrubbing converted ISO 27001 A.8.11 data masking to [NAME_1] / [SECRET_1] for ISO 27001 A.8.11 Data Masking for AI.
1. Audit logic and risks.
2. Keep output aligned with ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management).
3. Retain all tokens untouched.

[PASTE CLEAN PAYLOAD]
Minimizing ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) Exposure in ISO 27001 A.8.11 Data Masking for AI
Unstructured ISO 27001 A.8.11 data masking prompts carry full ISO 27001 Annex A.8.11 (Data Masking) and ISO 42001 (AI Management) liability. Integrating implementing ISO 27001 a.8.11 for generative AI practices into ISO 27001 A.8.11 Data Masking for AI isolates [ACCOUNT_1] locally.
Client-Side Substitution Across ISO 27001 A.8.11 Data Masking for AI
With local RAM (ISO 27001), IT directors sanitize ISO 27001 A.8.11 Data Masking for AI at keyboard speed—mapping ISO 27001 A.8.11 data masking to [ACCOUNT_1] in <1ms with zero upload per masking ABA routing and account numbers for AI.
Test ISO 27001 A.8.11 data masking scrubbing offline or run npx ztds-audit in CI: ISO 27001 A.8.11 Data Masking for AI emits 0 bytes per github Copilot PII leakage.
