
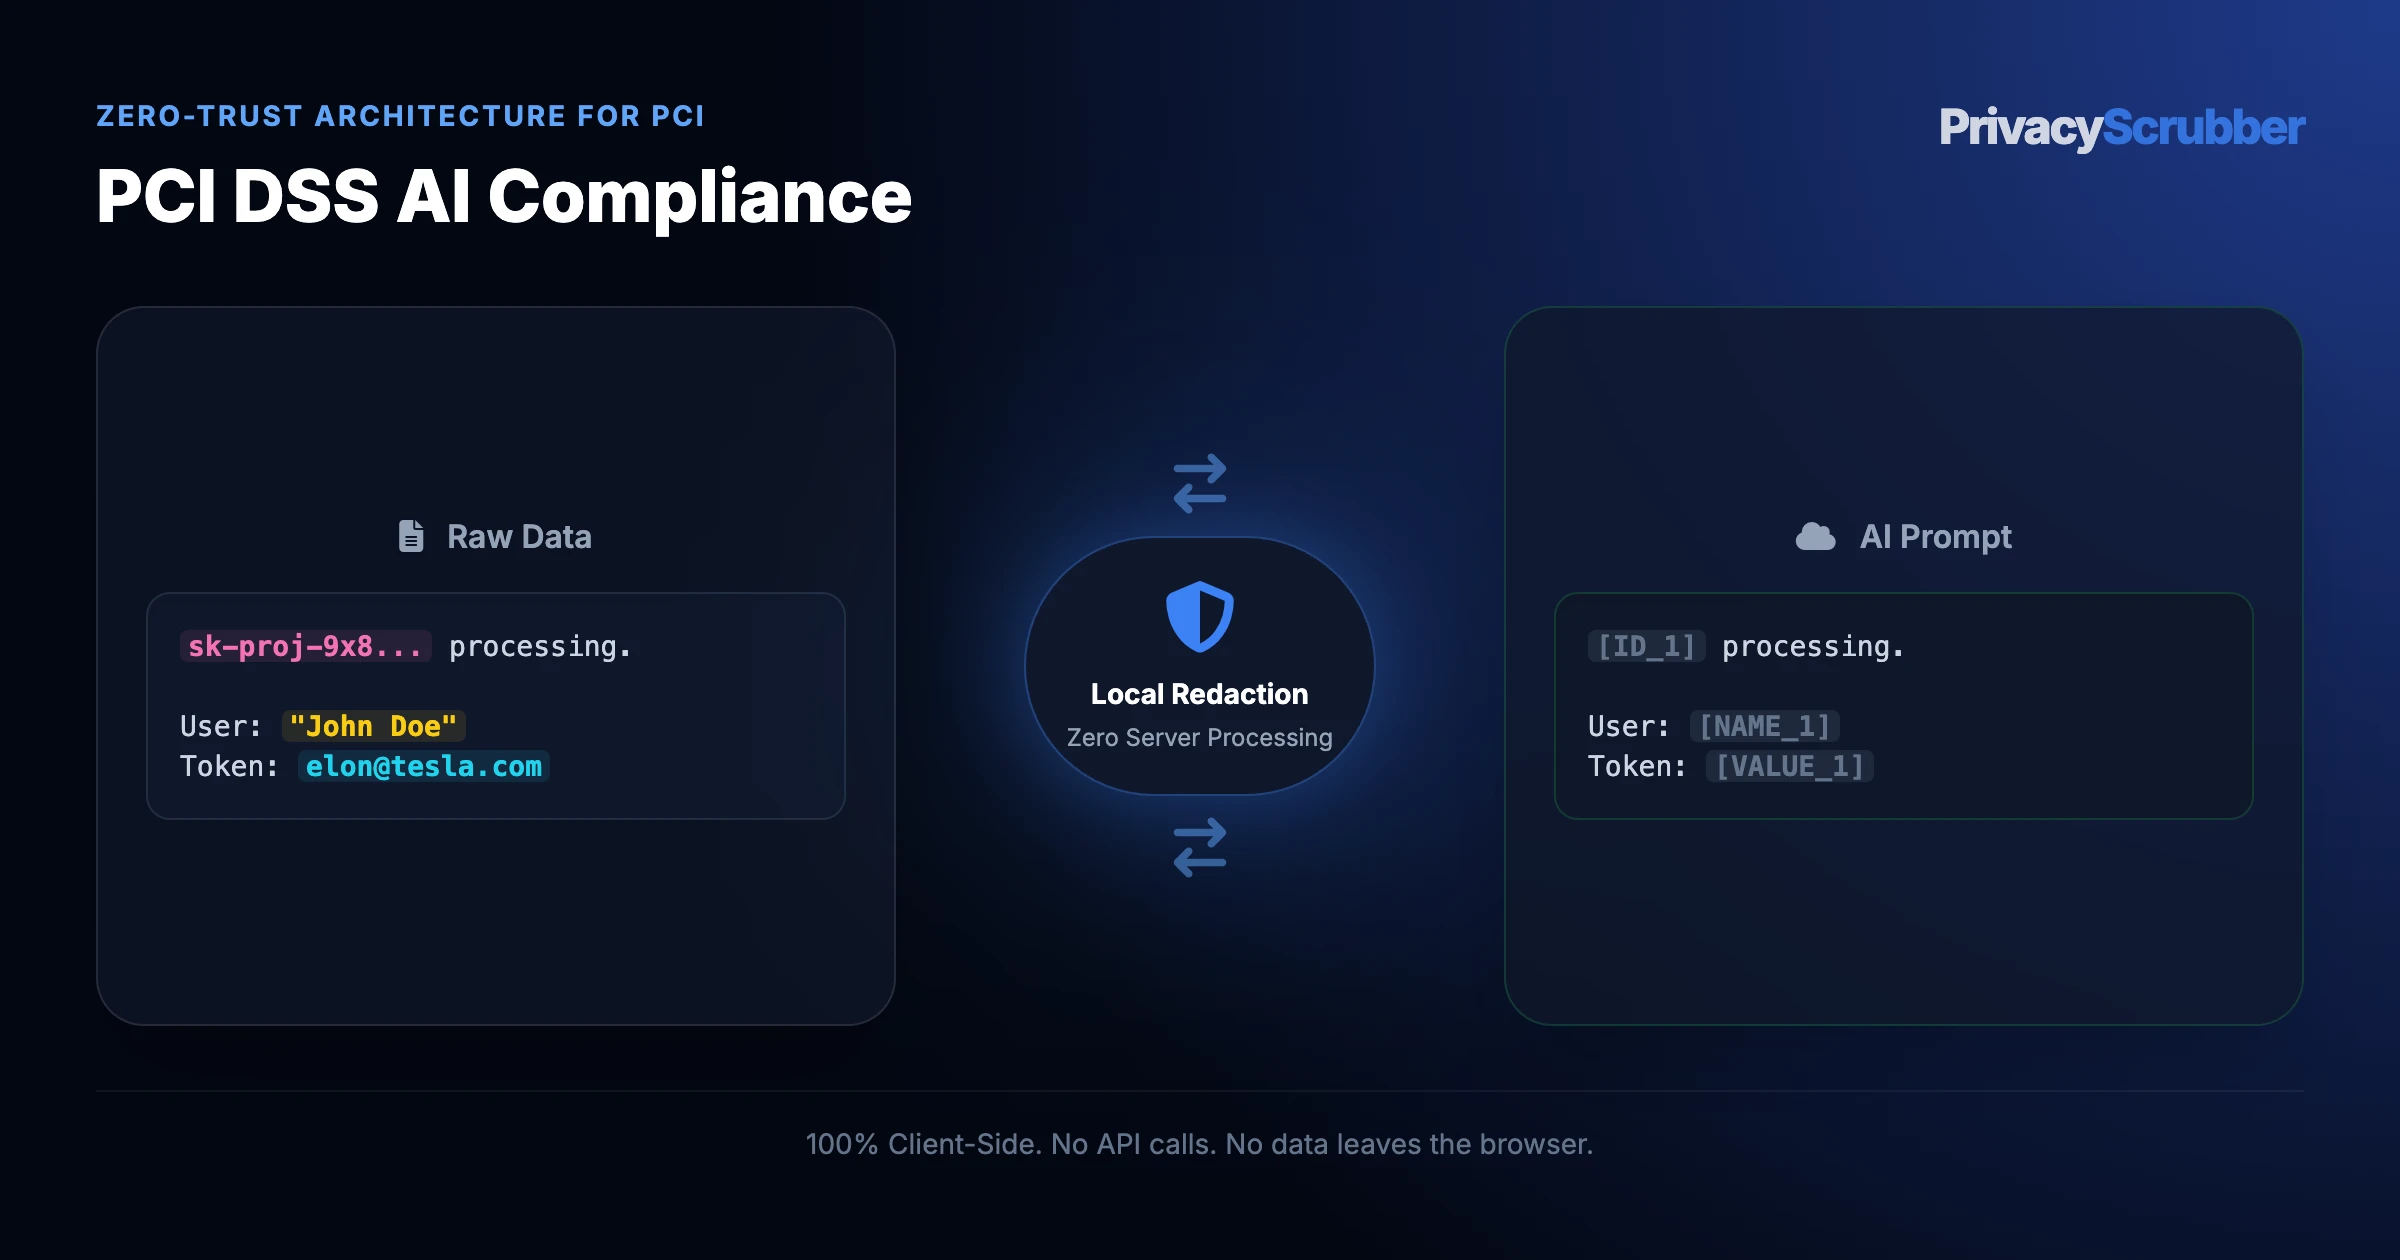
Because PCI DSS AI compliance payloads trigger PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps inside Payment gateways, finance teams isolate PCI DSS AI Compliance locally using local RAM (PCI-DSS) and map identifiers to [MERCHANT_1].
What Payment and Security Engineers Send to AI During PCI DSS AI Compliance
Intercepting PCI DSS AI compliance inside PCI DSS AI Compliance protects finance teams from raw credit card protection AI retention. Across PCI-DSS AI privacy guides, local RAM (PCI-DSS) confines credit card protection AI strictly to volatile RAM.
Exposure in PCI DSS AI Compliance happens the instant unredacted PCI DSS AI compliance leaves your socket. PCI DSS compliance demands strict financial data controls. Never leak credit card PAN details to ChatGPT. Flat-rate TEAMS pricing available. Only local RAM (PCI-DSS) stops PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps beforehand.
Eliminating PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps on PCI DSS AI Compliance
PCI DSS compliance demands strict financial data controls. Never leak credit card PAN details to ChatGPT. Flat-rate TEAMS pricing available. Without local pre-scrubbing via local RAM (PCI-DSS), finance teams handle PCI DSS AI compliance payloads that leak straight into AI-powered support desks queues.
Instead of destroying prompt context on credit card protection AI, reversible [MERCHANT_1] surrogates keep multi-turn logic coherent across Payment gateways until local Reveal completes.
ZTDS™ Field Governance for PCI DSS AI Compliance Workflows
This field-level specification ensures PCI DSS AI Compliance prompts retain 100% mathematical and semantic accuracy with zero cleartext PII egress:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Routing Endpoints (financial DLP ChatGPT) | REDACT | [ACCOUNT_1] | Blocks contact linkage when finance teams analyze PCI DSS AI compliance batches. |
| Entity Names (PCI-DSS) | REDACT | [CARD_1] | Maintains multi-turn coherence on PCI DSS AI compliance without exposing raw parties. |
| Subject Identifiers (PCI DSS AI compliance) | REDACT | [CARD_1] | PCI-DSS Requirement 3.4 (Rendering PAN unreadable) guard prevents Payment gateways from retaining personal PCI DSS AI Compliance records. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets Payment gateways trace root causes cleanly inside sanitized credit card protection AI logs. |
| Non-PII Workflow Constraints | PRESERVE | Cleartext Context | Preserves reasoning constraints across PCI DSS AI Compliance prompts sent offline. |
| Domain Instructions (PCI-DSS) | PRESERVE | Cleartext Logic | Retains workflow intent so finance teams get actionable financial DLP ChatGPT outputs. |
Bijective Prompt Blueprint for PCI DSS AI Compliance
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Analyze PCI DSS AI Compliance (credit card protection AI) for finance teams.
Surrogate markers [CARD_1] and [CVV_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Analyze PCI DSS AI Compliance (credit card protection AI) for finance teams.
Surrogate markers [CARD_1] and [CVV_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Why PCI DSS Security Assessors Flag Unmasked Prompts in PCI DSS AI Compliance
Meeting PCI-DSS Requirement 3.4 (Rendering PAN unreadable) data minimization during PCI DSS AI Compliance leverages PCI dss and ChatGPT patterns to neutralize PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps via volatile [MERCHANT_1] mapping.
How to Sanitize PCI DSS AI Compliance in Local RAM (Zero Cloud Egress)
offline endpoint scrubber fixes PCI DSS AI Compliance leaks by replacing credit card protection AI with [ACCOUNT_1] inside client memory while mirroring customer data platform (cdp) AI privacy restoration.
Both browser DevTools offline checks and SHA-256 receipts give PCI DSS AI Compliance auditable zero-egress proof under legal AI privacy.
