
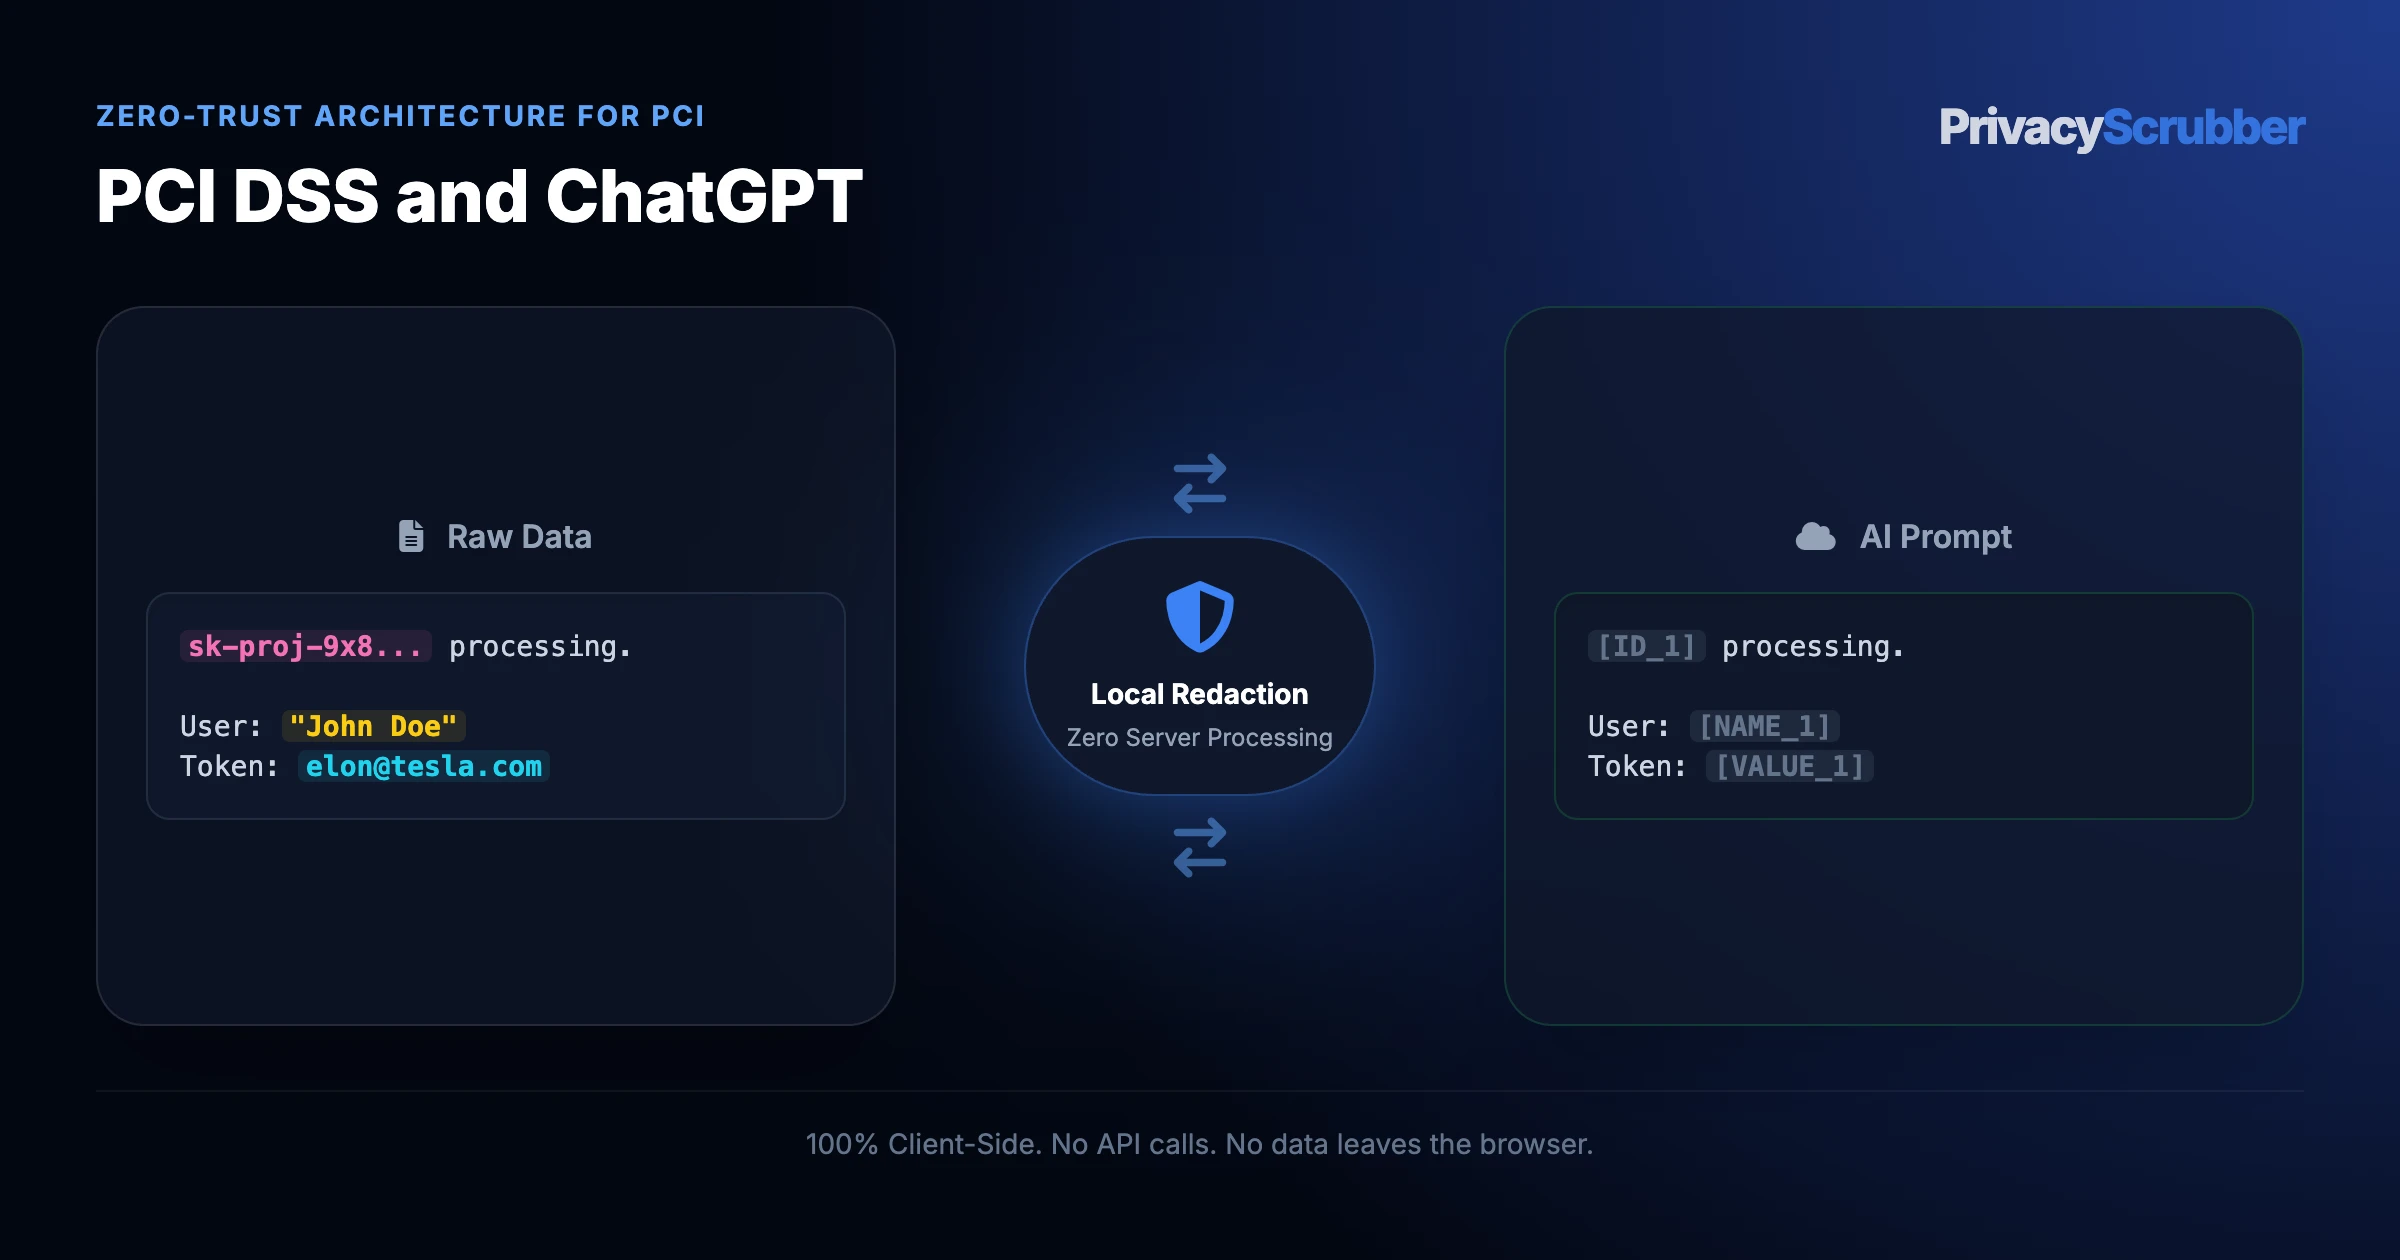
PCI DSS Requirement 3.3 prohibits storing sensitive authentication data after authorization, including full PANs except when specifically allowed. Pasting cardholder data into ChatGPT is equivalent to transmitting a PAN to an unauthorized third party — a direct PCI DSS violation that can result in significant regulatory fines and potential revocation of card processing privileges.
Keep PANs and CVVs out of every prompt
Pasting cardholder data into an AI tool sends it to a third party outside your PCI environment. Replace card numbers and related identifiers with tokens locally so the prompt carries no PAN.
Choose the Finance preset above, paste a sample with card numbers, and check every PAN is tokenized.
Start RAM workspaceSupport and finance staff get masking inside the AI chat box.
Add Chrome shieldConfigure stdio masking for PCI DSS and ChatGPT directly on your machine (free tier compatible).
{
  "mcpServers": {
    "privacyscrubber": {
      "command": "npx",
      "args": ["-y", "@privacyscrubber/mcp-server"]
    }
  }
}npm install @privacyscrubber/sdk
import { sanitize, restore } from '@privacyscrubber/sdk';

// Strip card numbers before logs or tickets reach an LLM
const { scrubbedText, tokenMap } = sanitize(transactionLog);
const aiAnswer = await callYourModel(scrubbedText);   // only tokens leave your process
const { restoredText } = restore(aiAnswer, tokenMap); // originals restored in local RAMWhat Payment and Security Engineers Send to AI During PCI DSS and ChatGPT
Every raw PCI DSS ChatGPT compliance query for PCI DSS and ChatGPT widens PCI-DSS Requirement 3.4 (Rendering PAN unreadable) audit scope on Payment gateways. Our PCI-DSS AI privacy guides mask sensitive attributes into [CARD_1] beforehand.
Why do network gateways miss PCI DSS and ChatGPT? Keep PANs and CVVs out of ChatGPT, Claude, and AI bots under PCI DSS v4.0: tokenize credit card numbers in local browser RAM before sending prompts. Encrypted browser prompts carrying PCI DSS ChatGPT compliance trigger PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps beyond proxy inspection.
Zero-Egress Mechanics in PCI DSS and ChatGPT
Operating PCI DSS and ChatGPT inside Payment gateways exposes billing administrators to PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps whenever raw PCI DSS ChatGPT compliance reaches external APIs. Through offline endpoint scrubber, sensitive strings swap into [ACCOUNT_1] locally beforehand.
Instead of destroying prompt context on cardholder data AI protection, reversible [MERCHANT_1] surrogates keep multi-turn logic coherent across Payment gateways until local Reveal completes.
Pre-Inference Redaction Matrix: PCI DSS and ChatGPT
Effective sanitization of PCI DSS and ChatGPT requires stripping direct identifiers while keeping structural and quantitative context intact for model reasoning:
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Routing Endpoints (PAN masking AI tools) | REDACT | [ACCOUNT_1] | Blocks contact linkage when billing administrators analyze PCI DSS ChatGPT compliance batches. |
| Entity Names (PCI-DSS) | REDACT | [CARD_1] | Maintains multi-turn coherence on PCI DSS ChatGPT compliance without exposing raw parties. |
| Subject Identifiers (PCI DSS ChatGPT compliance) | REDACT | [CARD_1] | PCI-DSS Requirement 3.4 (Rendering PAN unreadable) guard prevents Payment gateways from retaining personal PCI DSS and ChatGPT records. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets Payment gateways trace root causes cleanly inside sanitized cardholder data AI protection logs. |
| Non-PII Workflow Constraints | PRESERVE | Cleartext Context | Preserves reasoning constraints across PCI DSS and ChatGPT prompts sent offline. |
| Domain Instructions (PCI-DSS) | PRESERVE | Cleartext Logic | Retains workflow intent so billing administrators get actionable PAN masking AI tools outputs. |
Copy-Paste Safe Instruction for PCI DSS and ChatGPT
Submit this prompt wrapper with your masked PCI DSS and ChatGPT input so the AI reasons over symbolic tokens without altering placeholder tags:
Analyze PCI DSS and ChatGPT (cardholder data AI protection) for billing administrators.
Surrogate markers [CARD_1] and [CVV_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Analyze PCI DSS and ChatGPT (cardholder data AI protection) for billing administrators.
Surrogate markers [CARD_1] and [CVV_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Why PCI DSS Security Assessors Flag Unmasked Prompts in PCI DSS and ChatGPT
Meeting PCI-DSS Requirement 3.4 (Rendering PAN unreadable) data minimization during PCI DSS and ChatGPT leverages PCI dss v4.0 AI compliance patterns to neutralize PCI-DSS Requirement 3.4 (Rendering PAN unreadable) egress gaps via volatile [MERCHANT_1] mapping.
3-Step Local RAM Redaction for PCI DSS and ChatGPT Workflows
During PCI DSS and ChatGPT, offline endpoint scrubber locks PAN masking AI tools inside isolated RAM, assigning [ACCOUNT_1] surrogates so Payment gateways reflects ChatGPT privacy for wealth management advisors standards.
Auditors validate PCI DSS and ChatGPT offline via Airplane Mode: scrub PCI DSS ChatGPT compliance into [ACCOUNT_1], inspect DevTools, and match AI hiring tools and protected data.
