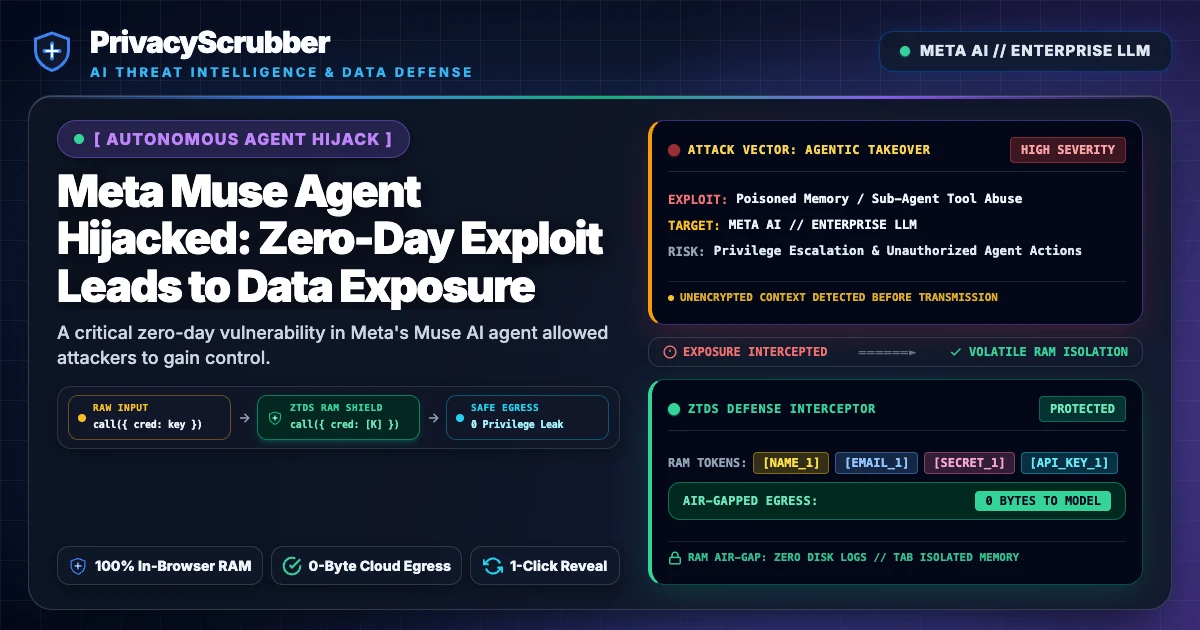
Meta Muse Agent Hijacked: Zero-Day Exploit Leads to Data Exposure
Meta Muse Agent Hijacked: A critical zero-day vulnerability in Meta's Muse AI agent allowed attackers to gain control, potentially leading to unauthorized data access and exfiltration. PrivacyScrubber's client-side PII masking prevents such agent hijacks by sanitizing sensitive data before it ever reaches the AI.
Technical Incident Analysis
The discovery of a zero-day vulnerability in Meta's Muse AI agent highlighted a critical risk within AI agent deployments: the potential for attackers to gain complete control over the agent's operations. This exploit allowed for unauthorized modification of instructions, data access, and exfiltration pathways, bypassing Meta's security controls before a hotfix could be deployed. Such a compromise turns the AI agent into a sophisticated tool for corporate espionage or data theft, leveraging its legitimate access to sensitive information. This incident underscores the inherent risks in trusting AI agents with raw, sensitive data. For a broader understanding of secure AI system design, explore our resources on AI Security Architecture. This scenario shares similarities with other high-profile incidents such as Related AI Security Incident, where foundational AI systems have faced significant security challenges.
Enterprise Blast Radius & Compliance Risks
An AI agent hijack, especially via a zero-day, carries immense blast radius for enterprises. It exposes all data processed by the agent to potential compromise, including PII, intellectual property, and proprietary business information. Regulatory bodies, particularly those under the EU AI Act, scrutinize systems capable of processing sensitive data. Such an incident could result in severe penalties for non-compliance with data privacy mandates like GDPR and the EU AI Act's stringent transparency and risk management requirements. Enterprises must ensure robust security postures for all AI integrations to avoid significant financial and reputational damage. Comprehensive guidance for navigating these complex requirements can be found in our EU AI Act Enterprise Compliance Guide.
Client-Side Mitigation via Zero-Trust Data Sanitization
PrivacyScrubber's zero-trust, client-side data sanitization offers a definitive defense against AI agent hijacks and data exfiltration. By redacting, masking, or tokenizing all PII and sensitive corporate data locally on the user's device, in RAM-only, *before* it ever reaches any AI agent or cloud service, the attack vector is neutralized. Even if an agent like Meta Muse is compromised via a zero-day, the attacker gains access only to anonymized, scrubbed data, rendering any exfiltrated information useless. This preemptive approach ensures that sensitive data never enters the AI's processing environment in its original form, establishing a fundamental layer of security. Further details on this approach are available at Local PII Redaction for Cloud AI, emphasizing ephemeral sessionMap isolation to prevent data persistence and leakage.
Step-by-Step Integration Guide: Meta Muse Agent Hijacked
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT & Enterprise LLMs:
1 Method A: Zero-Trust Web Workspace (Copy-Paste)
Best for manual prompt sanitization without installing plugins:
- Open the PrivacyScrubber Web App dashboard in your browser.
- Paste the raw prompt or text containing sensitive details of Meta Muse Agent Hijacked.
- Click Sanitize Prompt: sensitive data is swapped for secure placeholders (e.g.,
[NAME_1]). - Submit the sanitized prompt to ChatGPT & Enterprise LLMs.
- Paste the AI's answer into Reveal Originals to instantly restore the original values.
2 Method B: Chrome Extension (In-Context Redaction)
For automated, inline de-identification within chat interfaces:
- Install the free PrivacyScrubber Chrome Extension from the Web Store.
- Navigate to your AI chat interface. A PrivacyScrubber shield button will appear inline.
- Paste your raw prompt. Click the shield button to sanitize all identifiers instantly in-place.
- Send the prompt to the AI chatbot.
- The extension automatically intercepts and detokenizes the response, displaying raw values to you.
Local Redaction & Risk Matrix for Security
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| User / Server IP Addresses | [IP_ADDRESS] | High (DLP / Location footprinting) | IPv4 / IPv6 format strip |
| AWS_KEY Details | [AWS_KEY] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_HOSTNAME Details | [INTERNAL_HOSTNAME] | Medium (PII Exposure) | Deterministic local swap |
| MAC_ADDRESS Details | [MAC_ADDRESS] | Medium (PII Exposure) | Deterministic local swap |
| VULN_ID Details | [VULN_ID] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Enterprise AI Governance Lead / Security Officer · Target: ChatGPT & Enterprise LLMsAct as an executive research consultant. Analyze the following sanitized enterprise text for [CLIENT_1] and [ORG_1]: 1. Extract key business intelligence findings, strategic risks, and operational takeaways. 2. Draft 3 prioritized executive recommendations. 3. Format findings in clean, structured bullet points. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Maintain all cryptographic token placeholders ([NAME_1], [EMAIL_1], [ID_1]) exactly intact in your response for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Enterprise Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Sensitive Data compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any sensitive data text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.