Medical Billing PHI Redaction: Protect Claims Data from LLMs
TEAMS EDITION
Medical Billing PHI Redaction: Redact PHI from medical billing records, EDI 837/835 claims, CMS-1500 forms, and revenue cycle appeals in browser RAM. Achieve HIPAA Safe Harbor without cloud uploads.
Ilya SibiryakovPrivacy Architect••3 min read
100% Local Airplane Mode
CMS-1500 / UB-04 Health Insurance Claim Form & Itemized Bill Medical Biller, Revenue Cycle Managers (RCM) & Healthcare Compliance Officers HIPAA Title II (45 CFR Part 162 EDI Standards) & False Claims Act (31 U.S.C. § 3729)
Direct Technical Standard (Zero-Trust Rule)
Redacting CMS-1500 and UB-04 medical claim forms for AI revenue cycle analysis requires masking patient subscriber IDs, patient names, provider NPI numbers, and employer addresses, while keeping ICD-10-CM diagnosis codes, CPT/HCPCS procedure codes, billed charge amounts, and modifier tags in cleartext. Local offline RAM tokenization prevents payer profiling and eliminates HIPAA financial data exposure.
AI Summary / Key Takeaways
Verified Zero-Trust Logic
"PrivacyScrubber provides the essential de-identification layer for Medical professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Medical data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
To redact PHI from medical billing records and health insurance claims for AI analysis, Revenue Cycle Management (RCM) teams must strip all 18 HIPAA Safe Harbor identifiers—including subscriber IDs, patient names, SSNs, medical record numbers (MRNs), and dates of service—inside local browser RAM before pasting claim narratives into external LLMs. Under the HIPAA Privacy Rule (45 CFR § 164.514(b)(2)), the HIPAA Administrative Simplification Transaction Standards (45 CFR Part 162 for X12 EDI 837/835), the HITECH Act (42 U.S.C. § 17932), and GDPR Article 9 / Article 32, transmitting unredacted CMS-1500/UB-04 claims or Explanation of Benefits (EOB) statements to a third-party AI vendor without a Business Associate Agreement (BAA) is a reportable breach of Protected Health Information (PHI). PrivacyScrubber enforces a Technical Safe Harbor by tokenizing patient and subscriber identifiers in volatile browser memory while keeping CPT, HCPCS, ICD-10-CM, DRG, and CARC/RARC denial codes intact.
RCM & Medical Billing AI Dimension
Raw Claim Upload to LLMs
Cloud DLP / Clearinghouse API
Manual PDF / Excel Blackout
PrivacyScrubber (ZTDS Local RAM)
Subscriber ID & MRN Egress
100% exposed to third-party AI cloud servers
Transmitted in cleartext to intermediary cloud API
Zero network egress, but hidden metadata often remains
0 Bytes (100% local browser RAM execution)
HIPAA BAA & Clearinghouse Audit Scope
Immediate HIPAA violation without enterprise BAA
Requires secondary BAA and clearinghouse security review
High human error rate on multi-page EOBs
Zero BAA required (Safe Harbor de-identified payload)
CPT, ICD-10 & CARC/RARC Code Integrity
Preserved (at cost of full PHI breach)
Generic regexes corrupt CPT/ICD-10 numeric codes
Frequently breaks fee schedule and line-item tables
One-way masking; manual copy-paste into appeal forms
Manual re-typing of subscriber IDs and claim numbers
Instant 1-click local Reverse Scrub in RAM
HIPAA Privacy Officer Audit Evidence
None (Shadow AI compliance gap)
Vendor server logs (stores metadata externally)
Zero cryptographic verification
Signed SHA-256 Local Compliance Receipt
Zero-Trust Medical Billing & RCM Governance
Equip Your Medical Coding & Denial Management Teams
Deploy unlimited seats with centralized HIPAA billing rules and encrypted claim handoff for $99/mo flat (TEAMS), or integrate headless EDI 837/835 sanitization into backend RCM pipelines via the Developer SDK ($299/mo).
What Healthcare Practitioners and Staff Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
Ensuring patient confidentiality for Medical Billing PHI Redaction is a critical clinical objective as medical teams adopt new technology. Paste-handling patient data into ChatGPT, clinical decision support AI, and AI-assisted documentation platforms risks exposing Protected Health Information (PHI) to third-party servers. Our medical AI privacy guides details the clinical standards for securing the medical perimeter. The primary risk is exposing Protected Health Information (PHI) to third-party AI servers, which constitutes a HIPAA breach and carries penalties up to $1.9M per violation category.
When clinicians utilize cloud chatbots to summarize patient histories, they risk exposing sensitive health information. Cloud safety switches cannot identify patient details in unstructured text inputs. For clinicians, nurses, medical researchers, and healthcare administrators, sanitizing text before transit is the only way to prevent breaches. Redact PHI from medical billing records, EDI 837/835 claims, CMS-1500 forms, and revenue cycle appeals in browser RAM. Achieve HIPAA Safe Harbor without cloud uploads.
Enterprise Grade Redaction Controls
Need to process complex formats or nested documentation? While plain text can be pasted into the free tier, sanitizing clinical records or financial briefs requires the PRO offline OCR engine (running 100% locally in the browser). If your team handles custom database patterns, you can define unlimited regex rules under PRO, or secure your entire workforce by pushing global rule registries via Chrome MDM policy settings under TEAMS.
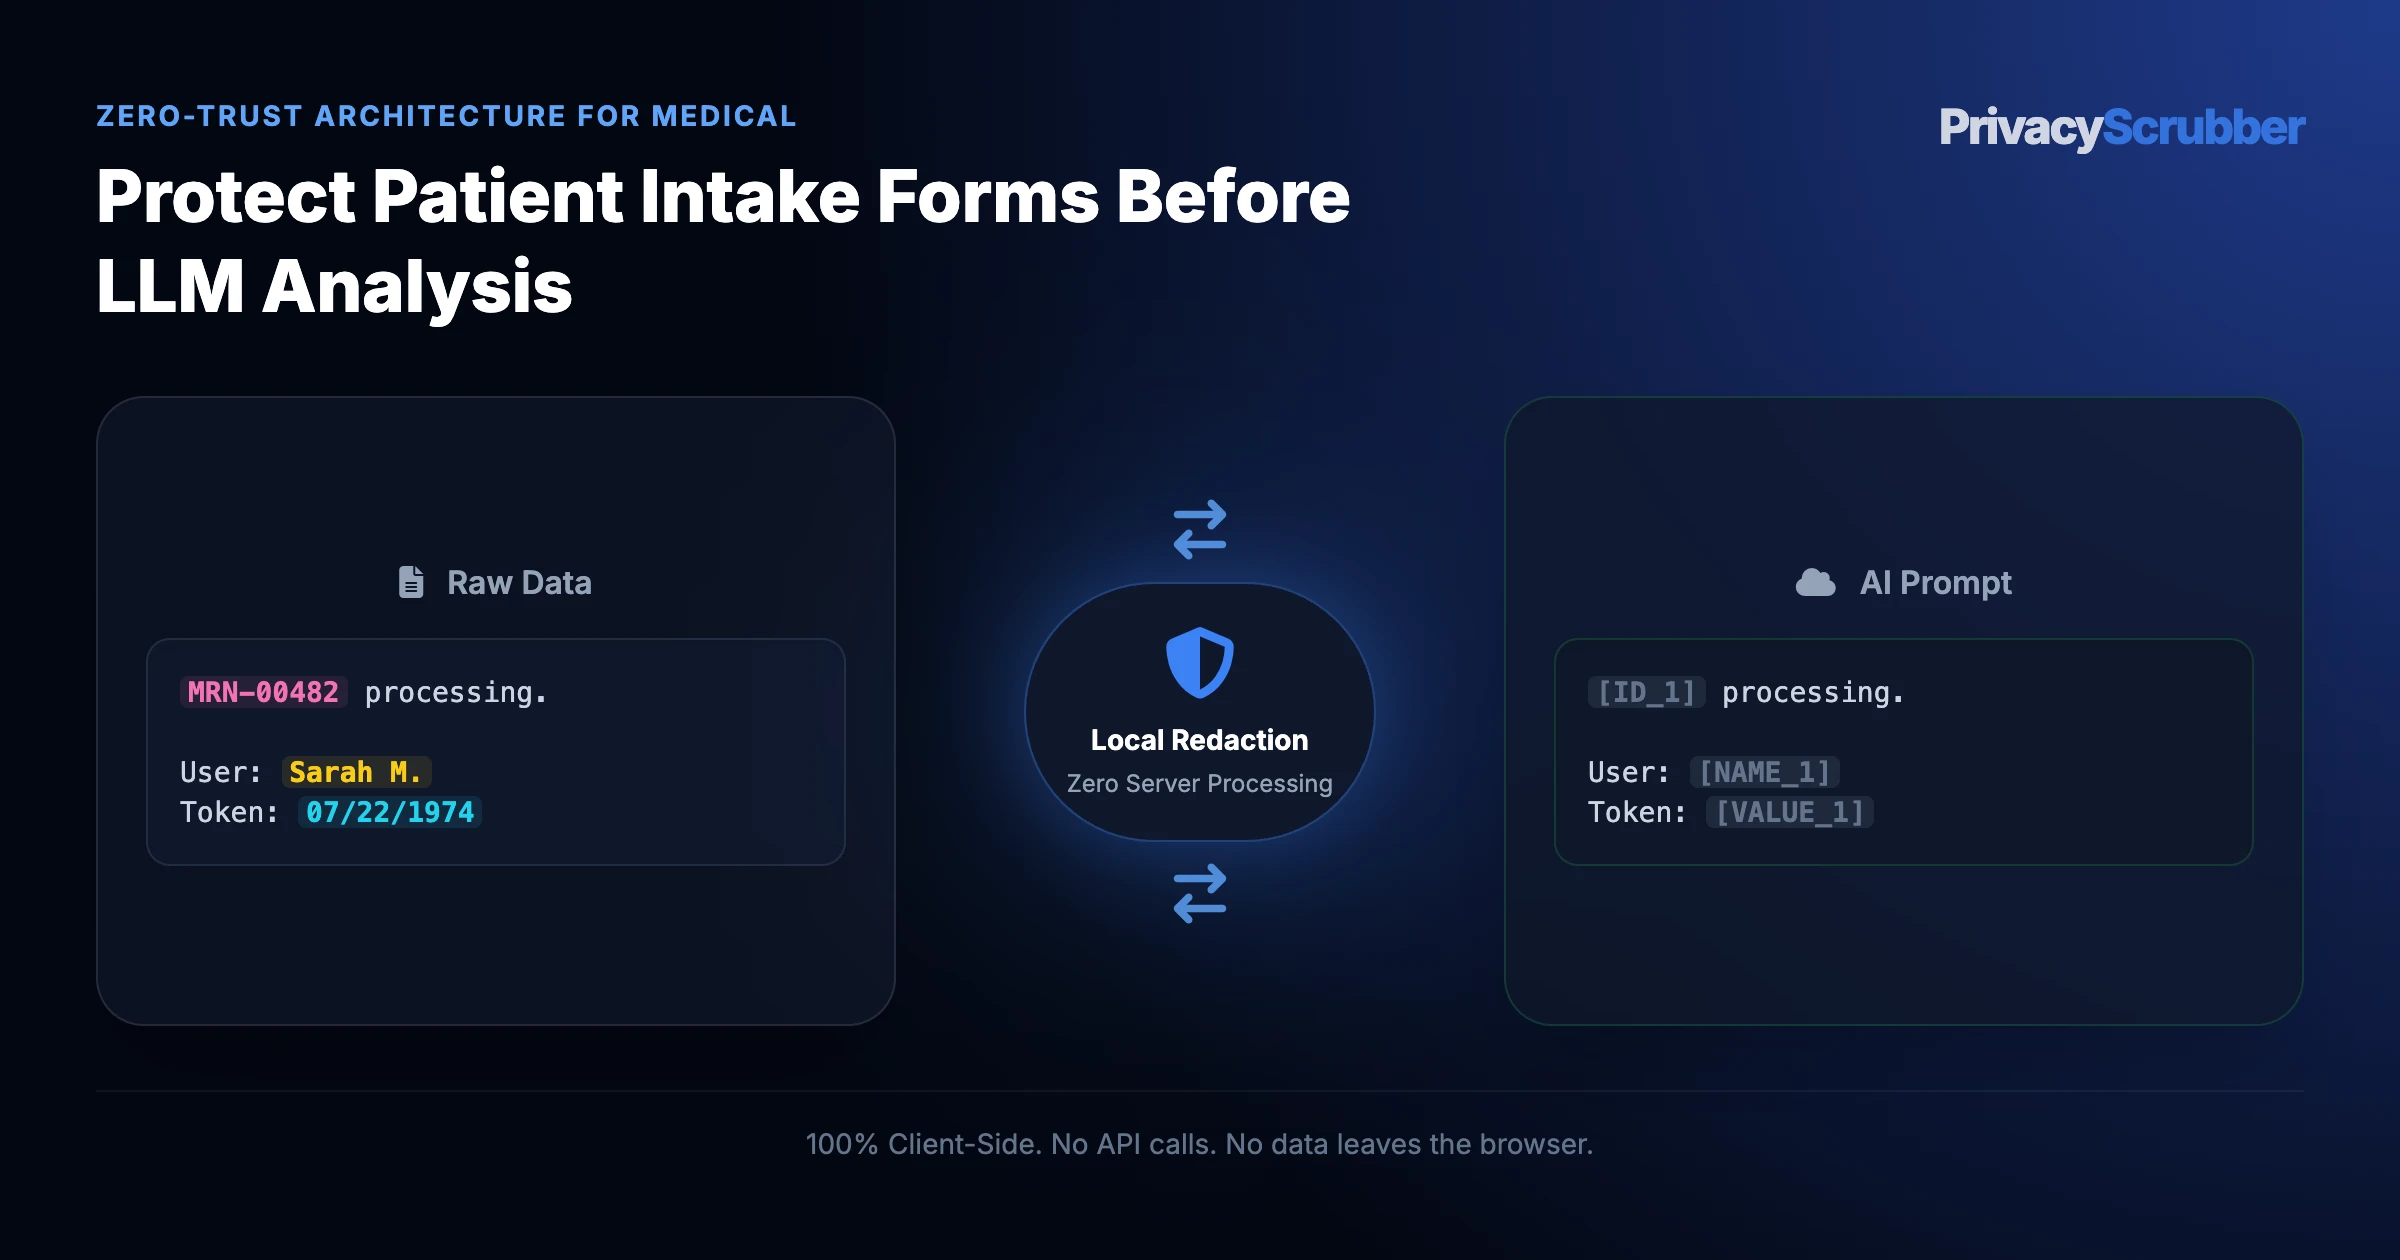
The technical safeguard for confidential AI prompts relies on intercepting sensitive strings before they cross the local network interface. By replacing actual values with deterministic placeholders (e.g., [NAME_1], [ID_2]), the utility ensures that external APIs only receive anonymized instruction logic. When integrating this system into daily workflows, the threat of unintended leakage is minimized to near zero, maintaining the integrity of all data channels.
Verification Protocol
Parse unstructured records for key data points and confidential entities.
Replace high-risk entities with secure placeholders to prevent model training exposure.
Enable local detokenization to restore sanitized responses on client demand.
Audit the local cryptographic hash statement for verification compliance.
The RCM Shadow AI Crisis: Why Payer Denial Appeals Leak Mass PHI
Health systems and medical billing agencies lose billions annually to payer claim denials, prior authorization rejections, and DRG downgrades. To fight back, Revenue Cycle Management (RCM) specialists increasingly paste Explanation of Benefits (EOB) statements, EDI 835 electronic remittance advices, and clinical progress notes into ChatGPT or Claude to draft medical necessity appeal letters and audit CPT modifier mismatches.
However, a single medical claim packet is one of the highest-density PHI artifacts in healthcare. It combines clinical diagnoses with financial and identity records: Patient Full Name, Date of Birth, Social Security Number, Medicare Beneficiary Identifier (MBI), Commercial Subscriber/Member ID, Group Policy Number, Patient Control Number (PCN), Medical Record Number (MRN), and exact Dates of Service. Uploading even one unredacted claim to an external LLM without a Business Associate Agreement (BAA) triggers statutory breach reporting under the HITECH Act (42 U.S.C. § 17932) and exposes both the healthcare provider and billing vendor to tiered civil monetary penalties under 45 CFR § 160.404.
Zero-Trust EDI 837/835 & Claim De-Identification in Browser RAM
PrivacyScrubber implements the Zero-Trust Data Sanitization (ZTDS) protocol inside a client-side browser sandbox, separating subscriber identity from medical coding logic:
Raw Denial Appeal Input (HIPAA Breach Risk)
Claim #: CLM-88492011 | Patient: Eleanor Vance (DOB: 04/12/1958, SSN: 412-88-9021)
Member ID: UHC-994021844 | MRN: 7730192 | DOS: 09/18/2026
Rendering Provider: Dr. Marcus Thorne, NPI 1487654321
Denial Code: CO-50 (Non-covered service, lacks medical necessity)
Billed: CPT 74177 (CT Abdomen/Pelvis w/ contrast - $1,420.00), ICD-10: R10.31, K35.80.
Clinical Note: Eleanor Vance presented to St. Jude ER on 09/18/2026 with acute RLQ pain...
Notice that every billing code required by the AI to argue medical necessity—CO-50, CPT 74177, $1,420.00, ICD-10: R10.31, and K35.80—remains 100% intact. Furthermore, because Eleanor Vance is deterministically mapped to [NAME_1] and 09/18/2026 to [DATE_1] across both the claim header and clinical note, the LLM drafts a cohesive, ready-to-submit appeal letter that re-hydrates in one click inside browser RAM.
RCM Entities Redacted Automatically
•Subscriber & Policy Identifiers: Medicare Beneficiary Identifiers (MBIs), commercial Member IDs, Group Policy Numbers, and Medicaid IDs.
•Claim & Account Numbers: Payer Claim Control Numbers (ICN/DCN), Patient Control Numbers (PCN), Guarantor Account IDs, and EFT trace numbers.
•Patient & Provider Demographics: Patient and insured names, SSNs, street addresses, phone numbers, DOBs, Dates of Service, and Provider NPIs/TINs.
Coding & Reimbursement Metrics Preserved
Procedure & Diagnosis Codes: CPT, HCPCS Level II, ICD-10-CM, ICD-10-PCS, MS-DRG, and APC classifications remain untouched.
Our zero-trust engine is pre-hardened for Medical workflows, automatically identifying and tokenizing the following parameters 100% locally.
PATIENT_NAME
Active Protection
MRN
Active Protection
DOB
Active Protection
DIAGNOSIS
Active Protection
INSURANCE_ID
Active Protection
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with offline compliance auditing.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
Compliance Decision Matrix
Field-by-Field Sanitization Rule for CMS-1500 / UB-04 Health Insurance Claim Form & Itemized Bill
To maintain LLM analytical context while avoiding cloud data breaches, follow this deterministic mapping before submitting prompts to third-party AI models:
Document Field / Box
Required Action
Deterministic Token
Statutory & AI Rationale
Insured / Patient Subscriber ID & Group #
REDACT
[POLICY_ID_1], [GROUP_1]
Direct health plan beneficiary identifier; exposes commercial payer eligibility
Patient Legal Name & Home Street Address
REDACT
[PATIENT_1], [ADDRESS_1]
HIPAA Safe Harbor core identifier; exposes claimant personal residence
Rendering Provider National Provider ID (NPI)
REDACT
[NPI_1]
10-digit CMS identifier enabling direct lookup in NPPES registry
Facility Billing Name & Tax ID (EIN)
REDACT
[ORG_1], [TAX_ID_1]
Clinical practice entity identifier; leaks hospital billing relationship
ICD-10-CM Diagnosis Codes & Narrative
PRESERVE
Cleartext (ICD-10 M54.50 Low back pain, unspecified)
Mandatory clinical justification required for medical necessity verification in AI
CPT / HCPCS Procedure Codes & Modifiers
PRESERVE
Cleartext (CPT 99214-25, 72148 MRI Lumbar Spine)
Standardized billing codes essential for claim scrubber denial analysis
Billed Line-Item Charge & Units
PRESERVE
Cleartext ($1,250.00 / 1 Unit)
Core quantitative revenue figure required for fee schedule allowance benchmarking
1-Click Persona Prompt
Safe LLM Prompt Template for CMS-1500 / UB-04 Health Insurance Claim Form & Itemized Bill
Copy and paste this structured prompt into ChatGPT, Claude, or Gemini alongside your tokenized text to prevent LLM rejection:
You are a Certified Professional Coder (CPC) and Revenue Cycle Management Consultant. Analyze the following sanitized CMS-1500 medical claim where patient identities, insurance policy numbers, NPIs, and facility names are replaced with tokens ([ID_1], [ID_2], [ID_3], [NAME_1], [NAME_2], [ADDRESS_1], [ADDRESS_2], [ORG_1], [TAX_ID_1]).

Tasks:
1. Verify medical necessity for CPT 72148 (MRI Lumbar Spine) supported by ICD-10 M54.50 under CMS Local Coverage Determinations (LCD).
2. Audit the use of Modifier 25 on CPT 99214 when billed concurrently with imaging.
3. Identify potential claim denial triggers and recommend documentation enhancements without requesting patient identifiers.

[PASTE SANITIZED TEXT HERE]
Why Clinical Risk and Compliance Committees Flag Unmasked AI Prompts
Compliance auditors demand strict safeguards: HIPAA Privacy Rule, HIPAA Security Rule, and the Common Rule (45 CFR 46) for research involving human subjects. However, daily clinical workflows often bypass static network security tools. Mitigating this risk requires adopting the frameworks in protect patient intake forms before llm analysis to ensure that clinical records are sanitized before external transit. The only reliable approach is stripping details locally. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
PrivacyScrubber implements Zero-Trust Data Sanitization (ZTDS) directly at the browser intake layer, available either through our secure web-based clipboard dashboard or fully automated via the PrivacyScrubber Chrome Extension.
How to Use AI on Real Medical Data — Without Sending a Single Real Name
PrivacyScrubber implements Zero-Trust Data Sanitization (ZTDS) directly at the browser intake layer, available either through our secure web-based clipboard dashboard or fully automated via the PrivacyScrubber Chrome Extension. Our local engine performs instant deterministic ZTDS™ detection matching to substitute sensitive data points with deterministic tokens (e.g., [NAME_1], [ID_2]) before transmission to LLMs. For compliance teams, this mirrors industry-standard patterns for HIPAA-compliant ChatGPT workflows — ensuring that public or third-party AI models only process anonymous logic. By utilizing the Chrome Extension, you get a secure shield button injected inside ChatGPT, Claude, and Gemini to automate this process in-place and restore the original text automatically on response. Running deterministic ZTDS™ entity rules locally ensures that teams can continue using ChatGPT, clinical decision support AI, and AI-assisted documentation platforms for daily queries without any third-party data collection.
Our client-side architecture is verifiable using the Airplane Mode Standard. Turn off your network interface, run a sanitization cycle, and confirm that all processing stays in local memory. This matches the standard for offline compliance auditing, proving that local execution is the primary safeguard for clinical privacy.
ChatGPT & Enterprise LLMs Integration
Step-by-Step Integration Guide: Medical Billing PHI Redaction
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT & Enterprise LLMs:
Act as a clinical documentation specialist. Review the following sanitized SOAP note for [PATIENT_1] under care of Dr. [PHYSICIAN_1]:
1. Synthesize the patient's acute clinical symptoms, past medical history, and physical examination findings.
2. Cross-check active prescription dosages against standard contraindications.
3. Draft a plain-English, patient-friendly after-visit discharge summary.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Do not alter any cryptographic token identifiers ([PATIENT_1], [MRN_1], [PHYSICIAN_1], [DATE_1], [POLICY_ID_1]) in your response for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT & Enterprise LLMs outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: HIPAA Safe Harbor De-Identification (45 CFR § 164.514(b)(2))All 18 statutory personal health identifiers are stripped in local browser memory prior to prompt transmission, removing the legal requirement for a vendor Business Associate Agreement (BAA).
Medical Adoption Use Cases
Chief Medical Information OfficerHIPAA & HITECH
Zero-Trust Verified
Secures clinical notes and patient records, masking PHI locally before research staff run diagnostic queries through generative LLMs.
Enforces zero-trust client-side sanitization across nursing and administrative terminals without needing complex BAA vendor agreements with AI providers.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No processor in the sanitization path. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Medical compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any medical text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Medical Teams.
Does medical billing redaction corrupt CPT, HCPCS, ICD-10-CM, or CARC/RARC denial codes?
No. PrivacyScrubber's Healthcare & HIPAA profile distinguishes between 5-digit CPT/HCPCS procedure codes, alphanumeric ICD-10-CM diagnosis codes, Claim Adjustment Reason Codes (CARC/RARC), and patient/subscriber identifiers. Medical coding nomenclature and dollar reimbursement amounts remain untouched while patient names, Member IDs, SSNs, and MRNs are tokenized.
Can we use ChatGPT or Claude to draft payer denial appeals without a HIPAA BAA?
Yes, provided the claim record and clinical summary are de-identified under the HIPAA Safe Harbor standard (45 CFR § 164.514(b)(2)) inside local browser RAM before transmission. Once all 18 identifiers are replaced with surrogate tokens locally, the resulting text is no longer regulated PHI. After the LLM generates the medical necessity appeal letter, you restore the patient name, Subscriber ID, and Claim ID locally via Reverse Scrub.
How does PrivacyScrubber handle scanned CMS-1500 forms and Explanation of Benefits (EOB) PDFs?
PrivacyScrubber includes an in-browser WebAssembly OCR & PDF parser that extracts text from multi-page EOB statements, CMS-1500/UB-04 forms, and payer denial letters directly inside client RAM. Zero PDF bytes are ever uploaded to an external OCR server.
How can RCM operations managers enforce identical PHI redaction rules across offshore and remote billing specialists?
With PrivacyScrubber TEAMS ($99/mo flat for unlimited seats), RCM directors can distribute standardized custom regex profiles for payer-specific subscriber prefixes (e.g., Medicare MBI, BlueCross alpha-prefixes, Medicaid IDs) and require cryptographic SHA-256 compliance receipts for every AI-assisted claim appeal.
Does protecting data with PrivacyScrubber before AI processing satisfy HIPAA Privacy Rule?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with HIPAA Privacy Rule because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for medical workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match medical-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask medical data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your medical data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Scrub in RAM" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard deterministic ZTDS™ sanitization engine to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
Can I use AI to summarize patient records?
Only if you de-identify the records first. Uploading raw patient notes to public AI models violates HIPAA. PrivacyScrubber's local processing ensures PHI is masked before summarization. Protect your entire staff with TEAMS for $99/mo.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
Why Clinical Risk and Compliance Committees Flag Unmasked AI Prompts
Compliance auditors demand strict safeguards: HIPAA Privacy Rule, HIPAA Security Rule, and the Common Rule (45 CFR 46) for research involving human subjects. However, daily clinical workflows often bypass static network security tools. Mitigating this risk requires adopting the frameworks in protect patient intake forms before llm analysis to ensure that clinical records are sanitized before external transit. The only reliable approach is stripping details locally. Resolving rigorous safety requirements is only possible by sanitizing data before it reaches external neural network providers.
How to Use AI on Real Medical Data — Without Sending a Single Real Name
PrivacyScrubber implements Zero-Trust Data Sanitization (ZTDS) directly at the browser intake layer, available either through our secure web-based clipboard dashboard or fully automated via the PrivacyScrubber Chrome Extension. Our local engine performs instant deterministic ZTDS™ detection matching to substitute sensitive data points with deterministic tokens (e.g., [NAME_1], [ID_2]) before transmission to LLMs. For compliance teams, this mirrors industry-standard patterns for HIPAA-compliant ChatGPT workflows — ensuring that public or third-party AI models only process anonymous logic. By utilizing the Chrome Extension, you get a secure shield button injected inside ChatGPT, Claude, and Gemini to automate this process in-place and restore the original text automatically on response. Running deterministic ZTDS™ entity rules locally ensures that teams can continue using ChatGPT, clinical decision support AI, and AI-assisted documentation platforms for daily queries without any third-party data collection.
Is PrivacyScrubber safe for medical billing phi redaction, health insurance claims ai privacy, scrub medical bills, edi 837 835 phi anonymization, cms 1500 UB-04 ai redaction, revenue cycle management hipaa safe harbor?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with medical billing phi redaction, health insurance claims ai privacy, scrub medical bills, edi 837 835 phi anonymization, cms 1500 UB-04 ai redaction, revenue cycle management hipaa safe harbor, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for medical?
Our engine includes 30 specialized industry profiles optimized for medical data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.
Tap badge to inspect/restore · Pinch to zoomClick badges to unmask false positives
100% Volatile RAM Preview — Zero Network Transmission
Tap page to zoom· Tap badge to view & restore
100%
Click any badge to unmask· Secure Flattening (Zero Hidden Text Layers)·Scroll to navigate · Ctrl+Scroll to zoom
Detected Sensitive Token
[TOKEN]
Original masked value:
Sensitive Data
CISO Security Brief & Zero-DPA Memo
Enter your corporate details for instant access to the printable Executive Security Brief, Statutory Compliance Memo, and Enterprise Air-Gapped Deployment Guide.
Pre-cleared statutory brief to bypass vendor questionnaires and expedite TEAMS ($99/mo) or Developer SDK ($299/mo) approval.
Select Procurement Track:
Procurement Suite Asset:
ZTDS™ VERIFIED0-Byte Egress · No Third-Party Processor · U.S. & Int'l Patents Pending · 2-Page Audit Brief
Manual Activation
Unlock your features
Invalid or expired license key
License Activated
Your features are unlocked.
Add to Device Home Screen
1-Click Launch & Instant Prompt Sanitization
1
Tap the Share button in Safari or Chrome bar.
2
Scroll down and select Add to Home Screen.
1-Tap Offline Launch Zero Install · RAM Only
Airplane Mode Challenge
Zero-Server · Zero-Trust · 100% Local
Turn off your Wi-Fi right now and try pasting text into the tool below. It processes 100% in your local RAM without sending any network requests.
Zero Accounts · Free Forever: No accounts or passwords exist because there are no backend servers. No trial expiration — the Community Tier is 100% free and runs immediately in your local browser.