
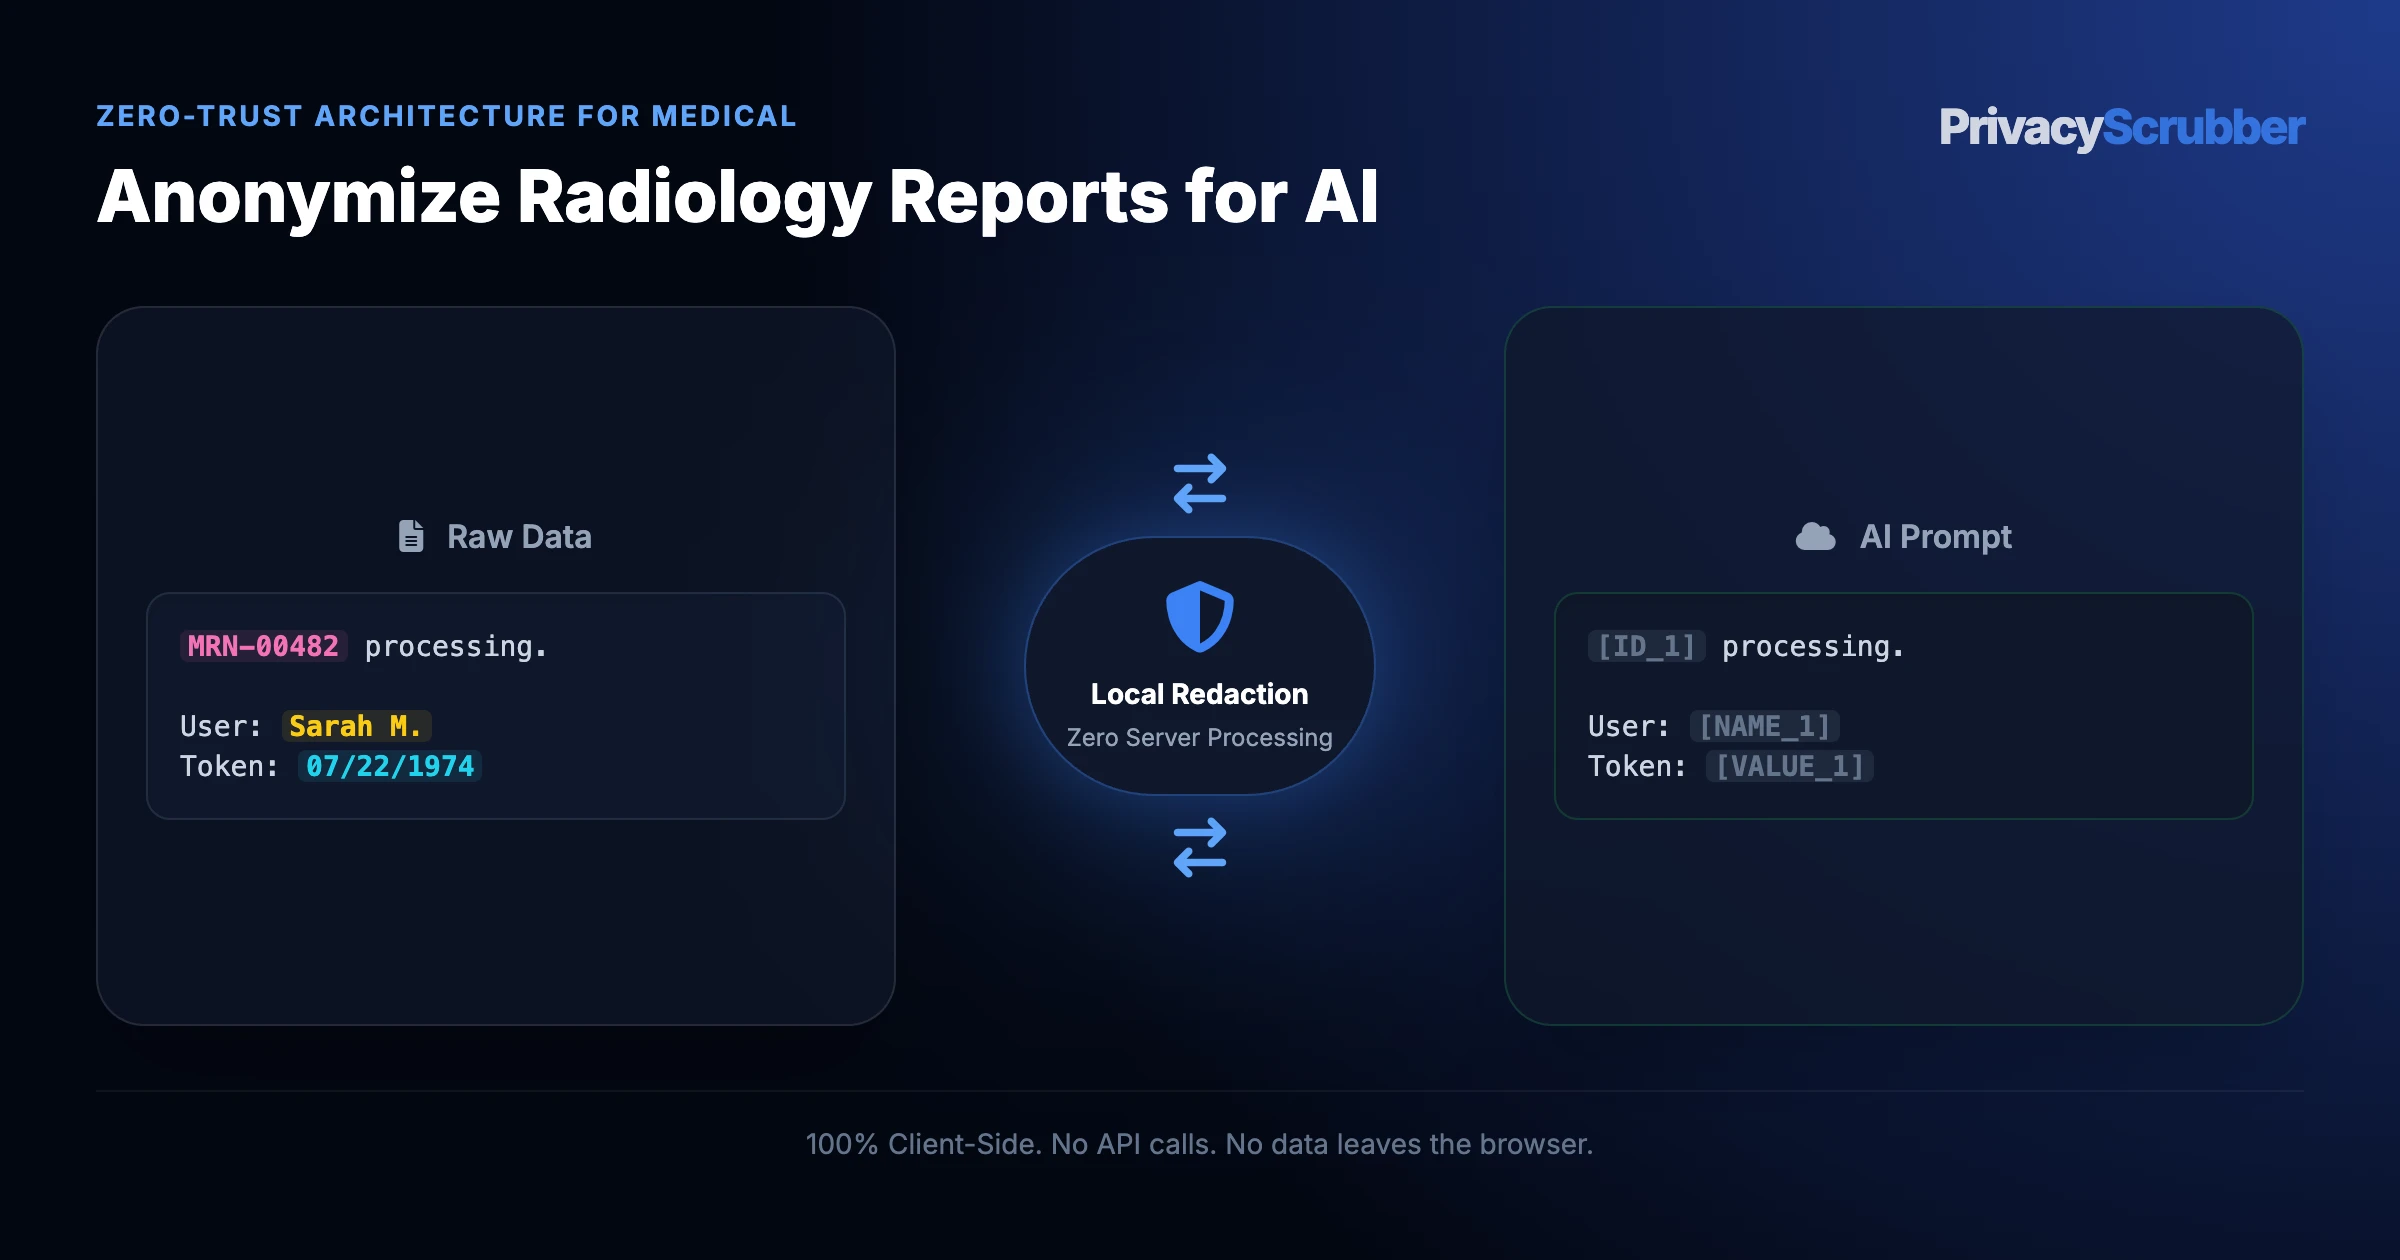
How do radiologists and clinical imaging teams safely summarize MRI and CT reports in ChatGPT or Claude without violating HIPAA? Pasting unredacted PACS/RIS diagnostic narratives—containing patient names, Medical Record Numbers (MRNs), DICOM Accession Numbers, dates of birth, and referring physician identifiers—into commercial cloud LLMs constitutes an unauthorized disclosure of Protected Health Information (ePHI) under the HIPAA Privacy & Security Rules (45 CFR § 164.514(b) Safe Harbor), the HITECH Act, and GDPR Article 9 & Article 32. PrivacyScrubber establishes Statutory Risk Minimization & Technical Safe Harbor (Defense-in-Depth) by stripping all 18 HIPAA identifiers ([PATIENT_1], [MRN_1], [ACCESSION_1]) 100% locally in browser RAM before a single byte leaves the clinical workstation, while keeping lesion dimensions, Hounsfield units, and BI-RADS/LI-RADS classifications 100% intact.
| Clinical Imaging Privacy Metric | Raw LLM Upload | Cloud Healthcare NLP API | Enterprise Cloud BAA LLM | PrivacyScrubber (ZTDS) |
|---|---|---|---|---|
| ePHI & MRN Network Egress | 100% exposed (reportable breach) | Raw PHI transmitted to cloud API | Raw PHI stored in vendor cloud | 0 bytes (100% local workstation RAM) |
| Anatomical & Staging Fidelity | Preserved (with OCR/HHS penalty) | Often over-redacts lesion measurements | Requires 6-month hospital IT BAA | 100% preserved (mm/cm, SUVmax, RADS) |
| 45 CFR § 164.514(b) Safe Harbor | Direct HIPAA violation | Requires sub-processor BAA chain | Cloud breach blast-radius remains | Pre-egress local de-identification |
| Department Licensing Cost | HHS OCR tiered civil penalties | Per-1,000-character cloud API fees | $100k+/yr enterprise PACS AI license | $99/mo Flat TEAMS (Unlimited Clinicians) |
Deploy ZTDS™ Radiology De-Identification Across Your Imaging Practice
Equip your entire radiology group or academic imaging department with TEAMS ($99/mo flat for unlimited seats)—including batch report de-identification and cryptographic HIPAA audit receipts—or integrate the Developer SDK ($299/mo) into your local HL7/FHIR and PACS pipelines.
What Healthcare Practitioners and Staff Send to AI — and What They Should Be Sending Instead
Addressing Anonymize Radiology Reports for AI dictates how modern healthcare organizations deploy AI. Paste-handling records into ChatGPT, clinical decision support AI, and AI-assisted documentation platforms without input filtering violates HIPAA compliance rules. Our medical AI privacy guides provides the blueprint for maintaining the medical boundary, resolving exposing Protected Health Information (PHI) to third-party AI servers, which constitutes a HIPAA breach and carries penalties up to $1.9M per violation category before any cloud API is called.When clinicians utilize cloud chatbots to summarize patient histories, they risk exposing sensitive health information. Cloud safety switches cannot identify patient details in unstructured text inputs. For clinicians, nurses, medical researchers, and healthcare administrators, sanitizing text before transit is the only way to prevent breaches. Anonymize MRI, CT, and DICOM radiology reports locally in browser RAM. Redact sensitive PII in local browser RAM with zero server egress or cloud leaks.
