
How to Use AI on Real European Consumer Data — Without Sending a Single Real Name
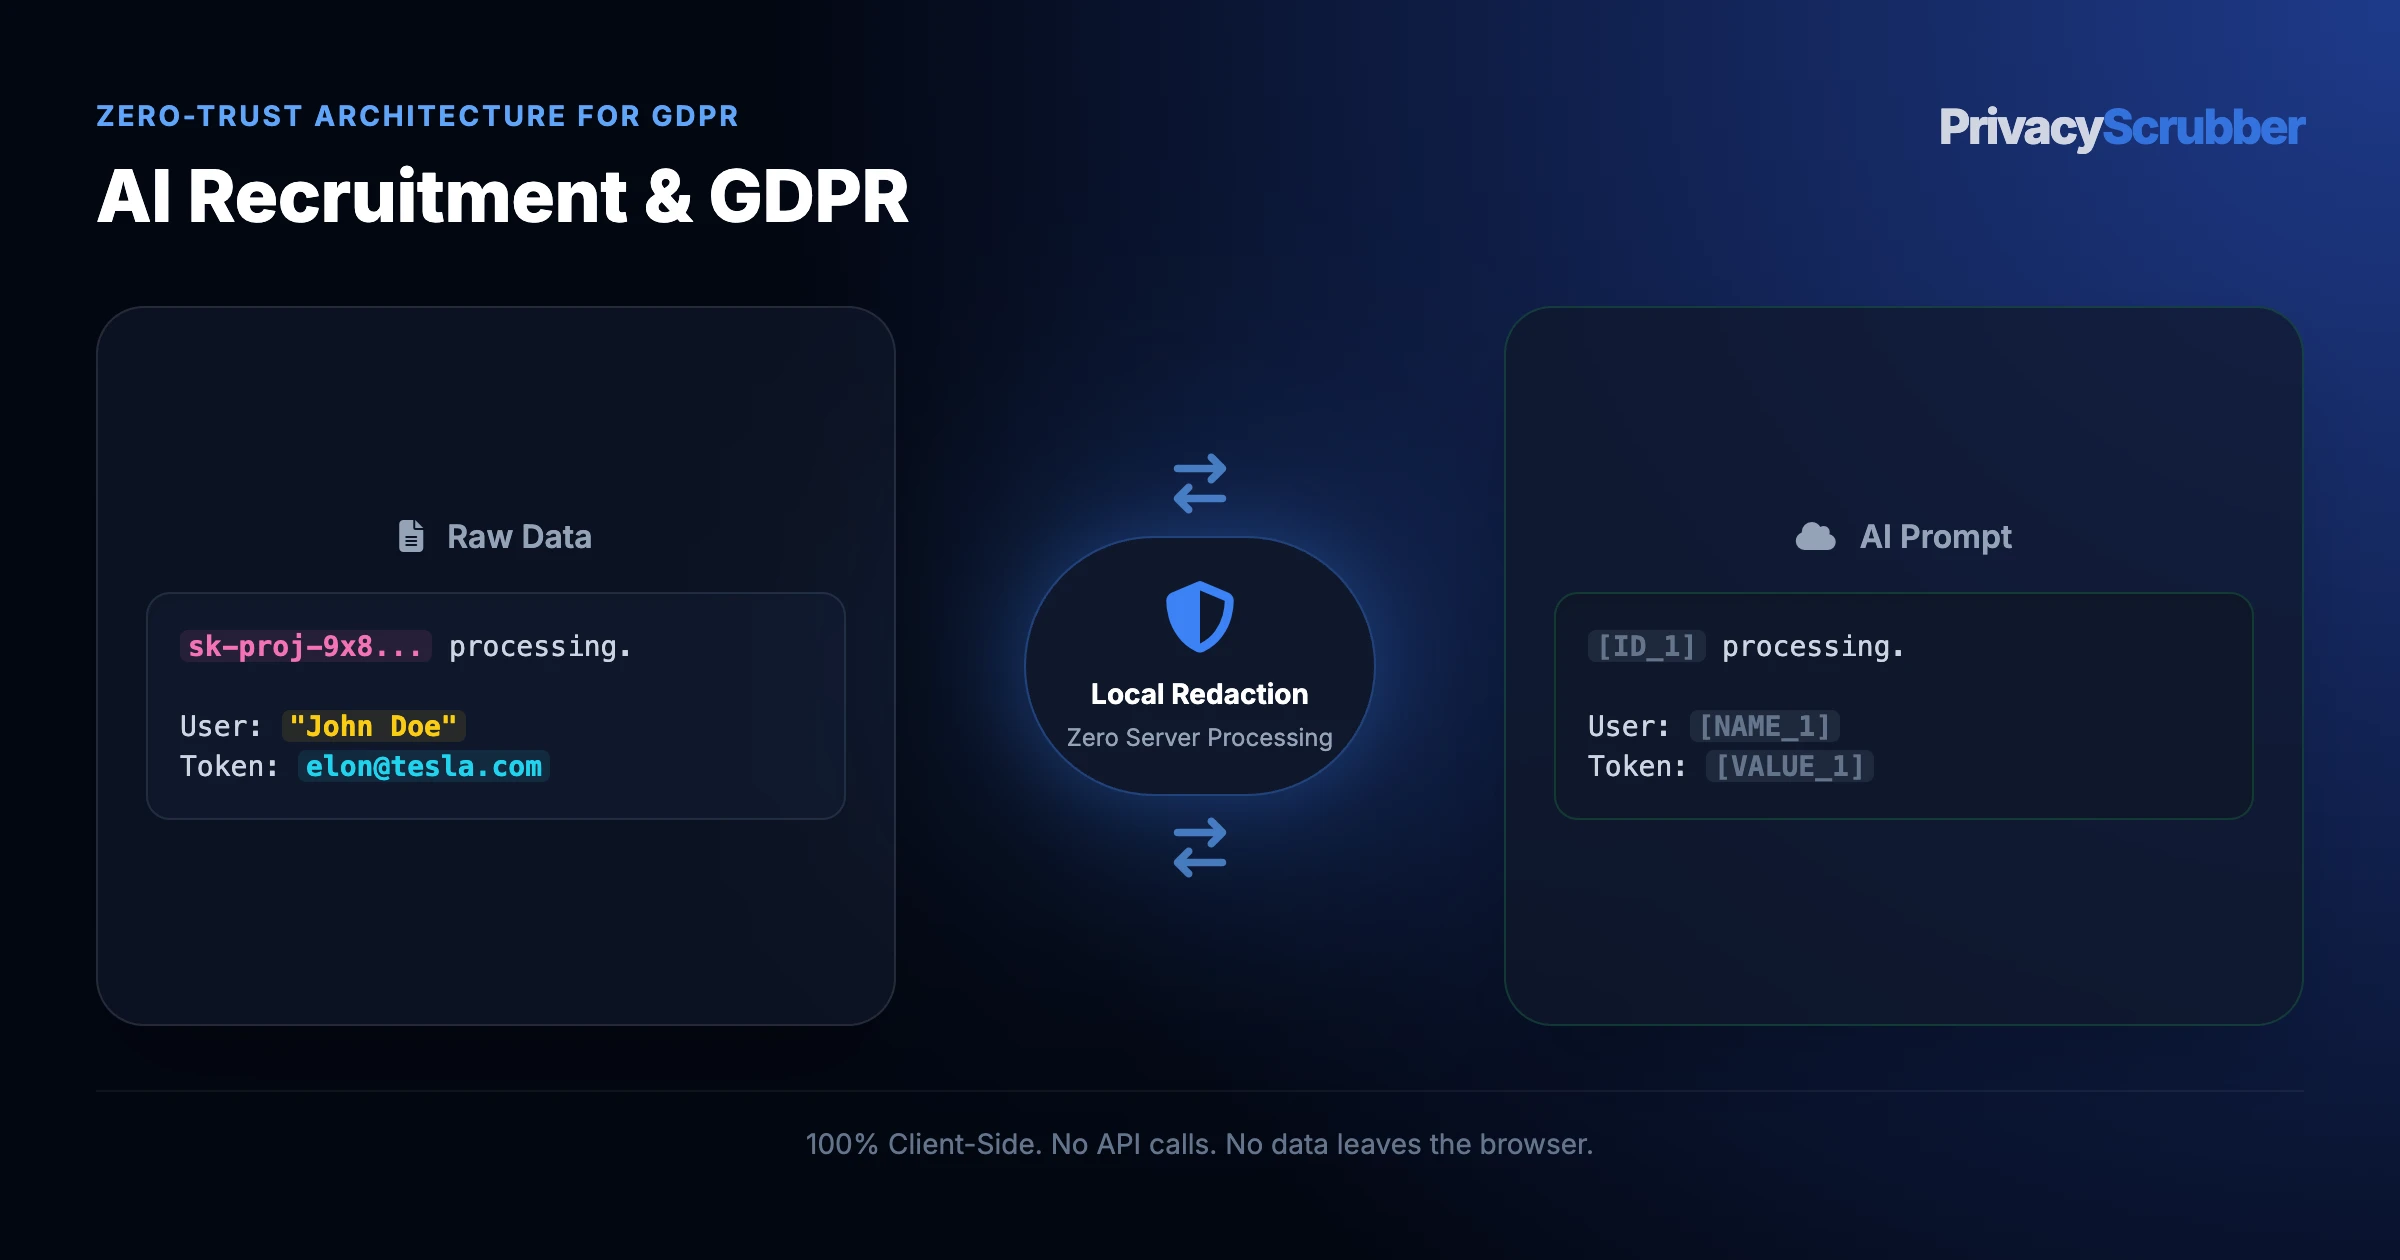
PrivacyScrubber implements Zero-Trust Data Sanitization (ZTDS) directly at the browser intake layer, available either through our secure web-based clipboard dashboard or fully automated via the PrivacyScrubber Chrome Extension. Our local engine performs instant deterministic ZTDS™ detection matching to substitute sensitive data points with deterministic tokens (e.g., [NAME_1], [ID_2]) before transmission to LLMs. For compliance teams, this mirrors industry-standard patterns for EU AI Act compliance strategies — ensuring that public or third-party AI models only process anonymous logic. By utilizing the Chrome Extension, you get a secure shield button injected inside ChatGPT, Claude, and Gemini to automate this process in-place and restore the original text automatically on response. By executing deterministic ZTDS™ detection parsing entirely in local memory, PrivacyScrubber preserves the usefulness of ChatGPT, Mistral, and local LLM integrations for production workflows without introducing external risk.
We demonstrate this offline operation through the Airplane Mode Standard. Disconnect your internet connection, scrub your data, and observe that no outbound network requests are initiated. This meets the conditions of enterprise data sovereignty, validating that all client information remains on your local terminal.

