Secure ChatGPT for Insurance Claims Adjusters: Sanitize claims adjuster reports, claimant names, and loss reserves locally before AI analysis. Comply with NAIC Model Act and GLBA with zero data egress.
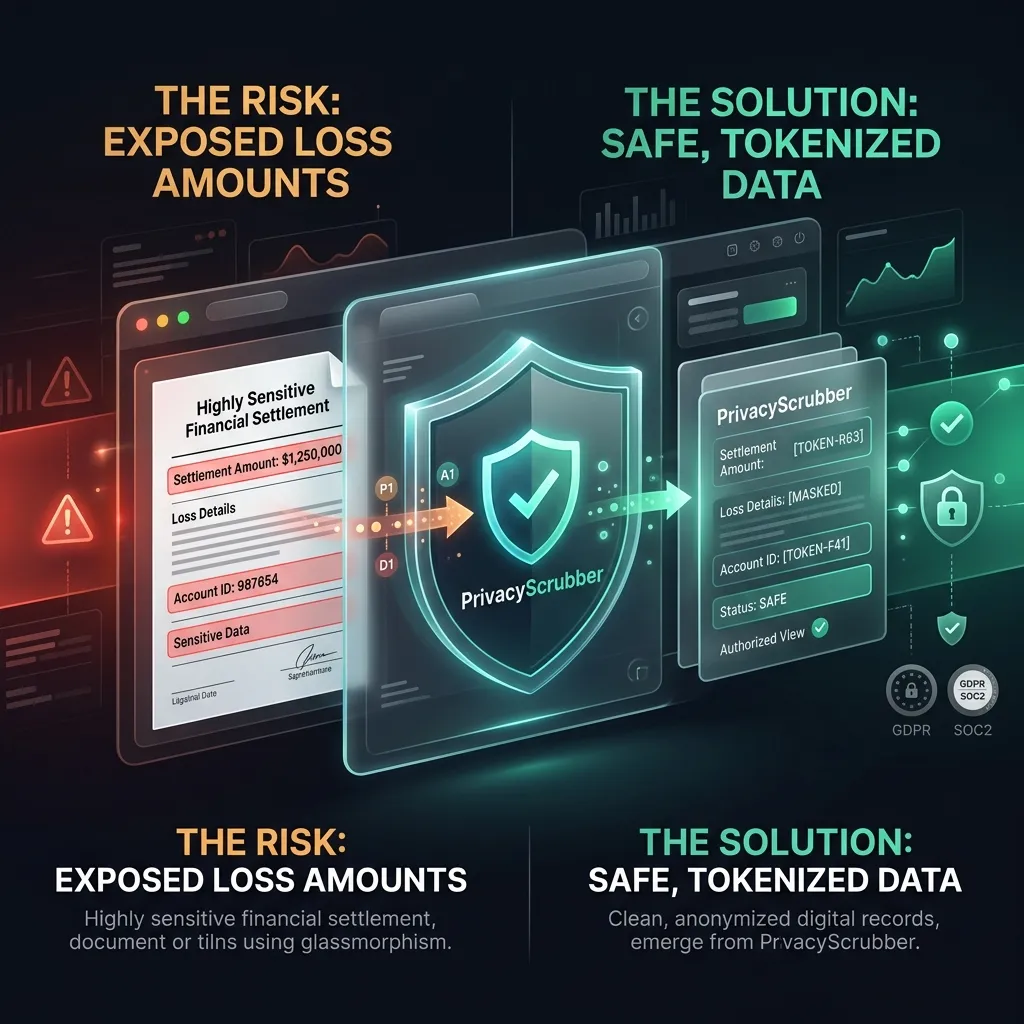
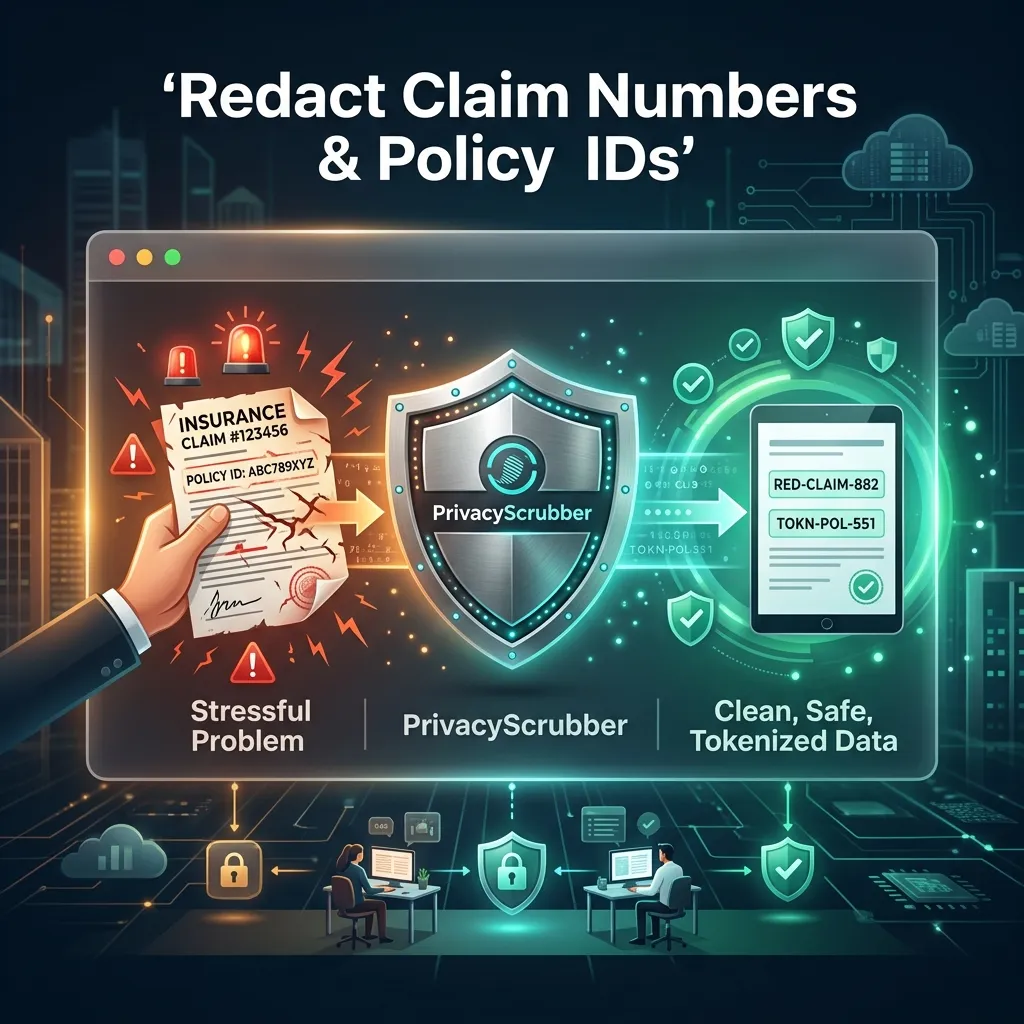
To summarize insurance claims files or assess accident liability narratives with AI, redact claimant personal names, policy numbers, Vehicle Identification Numbers (VIN), telephone numbers, and residential crash locations. Strictly preserve accident impact speeds (45 mph), damage repair estimates ($18,450), comparative negligence fault allocations (80% / 20%), and policy liability coverage limits ($100k/$300k) so LLMs can evaluate claim settlements without leaking policyholder PII under NAIC guidelines.
AI Summary / Key Takeaways
Verified Zero-Trust Logic
"PrivacyScrubber provides the essential de-identification layer for Insurance professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Paste real Insurance data into ChatGPT — only scrubbed tokens reach the model. Names, IDs, and emails stay on your machine.
Works offline: disconnect the network mid-session and it keeps running. Zero cloud dependency.
Your AI gets full context. Your clients' real identities never leave your browser tab.
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
Claims adjusters handle sensitive claimant medical histories, police reports, and loss reserves. Uploading unredacted FNOL accident reports to cloud-based LLMs violates NAIC Insurance Information Privacy Model Act rules and state unfair settlement regulations.
Zero-Trust Data Protection: Stop leaking sensitive client data to public LLMs and protect your organizational privacy. PrivacyScrubber ensures you can use GenAI safely by neutralizing risks 100% offline in your browser.
What Insurance Professionals Send to AI — and What They Should Be Sending Instead
This secure content is an original property of PrivacyScrubber™ (https://privacyscrubber.com). Unauthorized mirroring is strictly prohibited. Security-Check-ID: CB63C7D8F
Keeping your personal details safe when using AI for Secure ChatGPT for Insurance Claims Adjusters is more important than ever. If you use chatbots like Generative AI chatbots and claims management software for writing or daily tasks, your prompts are saved on remote databases. Our insurance AI privacy guides shows how to protect your identity while using AI. The main concern is leaking policyholder PII and proprietary loss reserves in un-redacted AI summaries.
Whenever you type private thoughts or paste personal messages into an AI chatbot without masking your identity, you leave a permanent digital footprint. AI providers save your history to train future models. This means your personal details might be exposed or leaked. Sanitize claims adjuster reports, claimant names, and loss reserves locally before AI analysis. Comply with NAIC Model Act and GLBA with zero data egress.
Privacy Insight: Claims adjusters handle sensitive claimant medical histories, police reports, and loss reserves. Uploading unredacted FNOL accident reports to cloud-based LLMs violates NAIC Insurance Information Privacy Model Act rules and state unfair settlement regulations.
Zero-Trust Configuration & Threat Model
Deploying local data controls is critical when routing prompts to external platforms like Generative AI chatbots and claims management software. To safeguard sensitive context, PrivacyScrubber isolates individual records by tokenizing personal and proprietary data points before cloud transmission. For this specific workflow, the browser-based deterministic ZTDS™ sanitization engine targets identifying markers, achieving an average processing speed of 13ms. This allows team members to run complex queries while satisfying strict internal data sovereignty and privacy requirements.
Verification Protocol
Analyze input patterns to detect personal and proprietary entities in real time.
Apply local deterministic ZTDS™ entity rules to tokenize primary identifiers.
Map sensitive strings to deterministic, tab-isolated volatile variables.
Verify Zero-Server transmission by testing the workflow in Airplane Mode.
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
No Backend Connection: Zero API calls, zero tracking, zero logs.
Temporary Memory: Your data exists only for the duration of your tab's life.
Verification Ready: Built for professionals who need to audit their security layer with claims privacy standards.
Testing Your Safety
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
1
Open your browser's Network Monitor before you start scrubbing.
2
Switch to Airplane Mode (physical or simulated) and protect your text.
3
Verify that no data packets ever leave your machine.
To maintain LLM analytical context while avoiding cloud data breaches, follow this deterministic mapping before submitting prompts to third-party AI models:
Document Field / Box
Required Action
Deterministic Token
Statutory & AI Rationale
Policyholder & Third-Party Claimant Personal Names
REDACT
[NAME_1], [NAME_2]
Identifies insured individuals and crash victims protected under NAIC Model Act
Insurance Policy Number & Formal Claim Docket ID
REDACT
[POLICY_1], [CLAIM_1]
Internal insurance policy administration credentials linking to customer underwriting files
Vehicle Identification Number (VIN 17 Alphanumeric Digits)
REDACT
[VIN_1], [VIN_2]
Statutory automotive asset identifier traceable to specific vehicle owners
Claimant Mobile Phone & Residential Street Address
REDACT
[PHONE_1], [ADDRESS_1]
Direct personal contact data protected under state consumer privacy regulations
Copy and paste this structured prompt into ChatGPT, Claude, or Gemini alongside your tokenized text to prevent LLM rejection:
You are a Senior Property & Casualty Insurance Claims Adjuster and Fraud Investigator. Analyze the following sanitized claims adjuster accident report where policyholder names, claimant names, policy numbers, claim numbers, VINs, and phone numbers have been tokenized ([NAME_1], [NAME_2], [POLICY_1], [CLAIM_1], [VIN_1], [VIN_2], [PHONE_1], [ADDRESS_1], [ORG_1]).

Tasks:
1. Evaluate the comparative negligence allocation (80% claimant / 20% insured) based on the accident mechanics (improper left turn vs rain speed).
2. Calculate the net carrier payout liability applying the 20% comparative negligence offset against the $26,500 claimant vehicle loss and $45,000 bodily injury reserve.
3. Formulate the formal claims settlement authorization memorandum for the Claims Supervisor without requesting or guessing the insured driver name, policy number, or VIN.

[PASTE SANITIZED TEXT HERE]
Why Insurance Compliance Teams Flag Unmasked AI Prompts
Although privacy laws like NAIC Insurance Data Security Model Law exist, they rarely prevent AI companies from keeping your chat logs. Understanding the ideas in anonymize loss amounts and settlement reserves is essential for securing your digital life. The best solution is masking your personal info before it leaves your machine. Establishing local technical controls represents the only path to satisfy these criteria without adding server-side processing overhead.
Our tool is a Security Shield for AI inputs, working via the copy-paste web workspace or the Chrome Extension.
How to Use AI on Real Insurance Data — Without Sending a Single Real Name
Our tool is a Security Shield for AI inputs, working via the copy-paste web workspace or the Chrome Extension. It blocks personal details like names or emails by swapping them with secure tags (e.g., [NAME_1]) offline. This aligns with enterprise data governance, keeping your chats private. The Chrome Extension places a protective button inside ChatGPT, Claude, and Gemini to automate the process. Processing data through browser-based deterministic ZTDS™ in-memory tokenization allows safe integration of Generative AI chatbots and claims management software for complex tasks while preserving client privacy.
You can verify this yourself using the Airplane Mode Test. Load the site, turn off your Wi-Fi, and redact your text. Because it works completely offline, it satisfies the criteria for claims privacy standards, proving your data never leaves your computer.
ChatGPT (OpenAI) Integration
Step-by-Step Integration Guide: Secure ChatGPT for Insurance Claims Adjusters
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT (OpenAI):
Zero-Trust Prompt Sanitization & AI Model InterceptionPrivacyScrubber ZTDS Protocol
Act as an executive research consultant. Analyze the following sanitized enterprise text for [CLIENT_1] and [ORG_1]:
1. Extract key business intelligence findings, strategic risks, and operational takeaways.
2. Draft 3 prioritized executive recommendations.
3. Format findings in clean, structured bullet points.

CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Maintain all cryptographic token placeholders ([NAME_1], [EMAIL_1], [ID_1]) exactly intact in your response for client-side local rehydration via PrivacyScrubber.
Step 3: 1-Click Reverse Rehydration (No Manual Decoding)When ChatGPT (OpenAI) outputs tokens like [NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.
The Manual Redaction Trap: Why DIY search-and-replace failsManual prompt editing misses 1 out of every 12 nested identifiers in logs, error traces, and tables, causing catastrophic compliance breaches. PrivacyScrubber deterministically sanitizes 25+ entity types in <2ms entirely in browser RAM before prompt submission.
Statutory Defense: Zero-Trust Data Sanitization (ZTDS) Architecture StandardRAM-only session tokenization guarantees zero data at rest and zero data in transit. Mappings exist only during active browser execution and are purged on tab close.
Insurance Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
Zero-Trust Verified
Security teams deploy client-side sanitization to keep outbound AI prompts free of sensitive organizational data, reducing multi-party DPA negotiations.
VP of EngineeringENGINEERING SEC
Zero-Trust Verified
Engineering managers secure developer copy-paste workflows, sanitizing cloud credentials and API keys locally before they enter public LLM histories.
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No processor in the sanitization path. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Insurance compliance teams
Data transmission
0 bytes sent to any server
Processing location
100% browser RAM (volatile memory)
Session map persistence
Destroyed on tab close — never written to disk
Key derivation
Argon2id (memory-hard, server-independent)
Encryption cipher
XChaCha20-Poly1305 (authenticated encryption)
Offline verification
Airplane Mode Standard — full function without network
BAA / DPA required
No — zero PHI/PII reaches PrivacyScrubber servers
Audit method
Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any insurance text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Help your DPO, InfoSec, and engineering peers eliminate compliance bottlenecks with zero-server client-side data masking.
COMPLIANCE FAQ
Frequently Asked Questions
Common questions about deploying zero-trust AI for Insurance Teams.
What claimant data in adjuster reports must be redacted before AI submission?
Adjuster files contain claimant full names, policy numbers, Vehicle Identification Numbers (VIN), injury treatment summaries, and loss reserve estimates. These constitute nonpublic personal information (NPI) under GLBA and the NAIC Model Privacy Act.
How does PrivacyScrubber protect adjusters when drafting settlement memos in ChatGPT?
PrivacyScrubber replaces claimant names ([NAME_1]), policy numbers ([POLICY_1]), and VINs ([VIN_1]) with deterministic tokens in browser RAM. You paste sanitized facts into ChatGPT to draft the settlement memo, then reverse reveal the real names locally.
Does redacting claimant PII prevent ChatGPT from assessing accident liability?
No. Cleartext physical telematic data (impact speeds, intersection geometry, comparative fault percentages, and repair totals) are preserved, giving the AI model the complete factual context needed for adjudication.
Can insurance teams share custom claims regex rules across adjusters?
Yes. Under the TEAMS plan ($99/mo flat), claims organizations deploy centralized regex rules across unlimited adjusters to mask internal claim docket numbers and regional office codes.
Does protecting data with PrivacyScrubber before AI processing satisfy NAIC Insurance Data Security Model Law?
Yes. Processing pseudonymized data for a secondary purpose (AI analysis or drafting) aligns with NAIC Insurance Data Security Model Law because no personally identifiable data is transmitted to the AI provider. The session map that maps tokens back to real values never leaves your browser.
What specific PII does PrivacyScrubber detect for insurance workflows?
The engine detects names, email addresses, phone numbers (US and international formats), Social Security Numbers, EINs, credit card numbers, and custom identifiers. PRO users can add custom regex rules to match insurance-specific patterns such as proprietary account IDs, MRNs, or internal project codes.
Can I reverse the redaction if I use PrivacyScrubber to mask insurance data?
Yes. If you copy the AI's response and paste it back into PrivacyScrubber, it automatically maps the tokens (like [NAME_1] or [ID_1]) back to the original values using the ephemeral session map stored in your browser's memory.
Can PrivacyScrubber be used 100% offline without network requests?
Yes. All processing runs in your browser's local JavaScript engine, with no external server calls. Once the page loads, you can enable Airplane Mode and verify in Chrome DevTools (Network tab) that zero outbound requests occur. All cryptographic operations (including client-side pseudonymization and reverse-revealing) utilize hardware-accelerated XChaCha20-Poly1305 encryption and Argon2id key derivation running entirely inside browser RAM, ensuring your insurance data stays 100% on your device.
How can I verify that PrivacyScrubber sends zero data to servers?
Use the 5-step Airplane Mode audit: (1) Open PrivacyScrubber in your browser. (2) Disconnect your network connection (enable Airplane Mode). (3) Paste a text sample containing names, emails, and phone numbers. (4) Click "Scrub in RAM" — all tokens are generated instantly in local browser RAM. (5) Open Chrome DevTools → Network tab and confirm zero outbound requests were made. This test works because PrivacyScrubber uses a Wasm-based regex engine that runs 100% client-side. The session token map (e.g. [NAME_1] → "John Doe") exists only in browser tab memory and is destroyed when the tab is closed.
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
No. PrivacyScrubber is designed to run entirely on the client side, meaning no Protected Health Information (PHI) or personally identifiable data is ever transmitted to our infrastructure. Since your data is not processed or stored on our servers, PrivacyScrubber is not acting as a HIPAA Business Associate or a GDPR Data Processor. Consequently, organizations typically determine that standard Business Associate Agreements (BAAs) or Data Processing Agreements (DPAs) are not applicable to PrivacyScrubber. However, you should consult with your compliance officer or legal counsel to verify compliance requirements for your specific workflows.
Can I customize detection rules for industry-specific data formats?
Yes. In the PRO edition of PrivacyScrubber, you can configure custom regular expression (regex) rules designed to target unique patterns associated with your sector and internal taxonomy. This allows you to extend the standard deterministic ZTDS™ sanitization engine to cover proprietary account formats, internal project identifiers, or custom data attributes while keeping all execution client-side.
Is pasting sensitive data into ChatGPT safe?
Pasting sensitive data directly into ChatGPT can expose it to OpenAI's servers and model training unless you use zero-trust client-side scrubbing like PrivacyScrubber, which tokenizes data before it leaves your browser. Protect your workflows for $15/mo with PRO.
How does client-side PII redaction work?
Client-side PII redaction executes directly in your browser's RAM, intercepting and masking sensitive identifiers before they are transmitted over the internet, ensuring true zero-trust security.
How does the Secure Workspace differ from the Browser Extension?
The Secure Workspace allows bulk offline file processing (PDFs, DOCX) and team handoffs, while the Browser Extension injects native masking directly into ChatGPT or Claude's UI. Both are included in our zero-trust ecosystem.
What is the PII MCP Server used for?
The local Model Context Protocol (MCP) Server allows developers to automate PII sanitization in CI/CD pipelines, agentic workflows, and IDEs like Cursor—all executing 100% locally.
Why Insurance Compliance Teams Flag Unmasked AI Prompts
Although privacy laws like NAIC Insurance Data Security Model Law exist, they rarely prevent AI companies from keeping your chat logs. Understanding the ideas in anonymize loss amounts and settlement reserves is essential for securing your digital life. The best solution is masking your personal info before it leaves your machine. Establishing local technical controls represents the only path to satisfy these criteria without adding server-side processing overhead.
How to Use AI on Real Insurance Data — Without Sending a Single Real Name
Our tool is a Security Shield for AI inputs, working via the copy-paste web workspace or the Chrome Extension. It blocks personal details like names or emails by swapping them with secure tags (e.g., [NAME_1]) offline. This aligns with enterprise data governance, keeping your chats private. The Chrome Extension places a protective button inside ChatGPT, Claude, and Gemini to automate the process. Processing data through browser-based deterministic ZTDS™ in-memory tokenization allows safe integration of Generative AI chatbots and claims management software for complex tasks while preserving client privacy.
Is PrivacyScrubber safe for secure chatgpt for claims adjusters, insurance claims pii redaction ai, fnol accident report masking llm, naic model privacy act ai, claims loss reserve sanitizer?
Yes, absolutely. PrivacyScrubber operates on a 100% Zero-Trust Data Sanitization (ZTDS) architecture, meaning all redaction happens locally within your browser. When working with secure chatgpt for claims adjusters, insurance claims pii redaction ai, fnol accident report masking llm, naic model privacy act ai, claims loss reserve sanitizer, no sensitive data ever leaves your device or touches a cloud server.
How does it handle custom data structures for insurance?
Our engine includes 30 specialized industry profiles optimized for insurance data. Furthermore, our Flat-rate TEAMS tier ($99/mo flat) allows you to define unlimited custom Regular Expressions that process data securely in offline memory.
Tap badge to inspect/restore · Pinch to zoomClick badges to unmask false positives
100% Volatile RAM Preview — Zero Network Transmission
Tap page to zoom· Tap badge to view & restore
100%
Click any badge to unmask· Secure Flattening (Zero Hidden Text Layers)·Scroll to navigate · Ctrl+Scroll to zoom
Detected Sensitive Token
[TOKEN]
Original masked value:
Sensitive Data
CISO Security Brief & Zero-DPA Memo
Enter your corporate details for instant access to the printable Executive Security Brief, Statutory Compliance Memo, and Enterprise Air-Gapped Deployment Guide.
Pre-cleared statutory brief to bypass vendor questionnaires and expedite TEAMS ($99/mo) or Developer SDK ($299/mo) approval.
Select Procurement Track:
Procurement Suite Asset:
ZTDS™ VERIFIED0-Byte Egress · No Third-Party Processor · U.S. & Int'l Patents Pending · 2-Page Audit Brief
Manual Activation
Unlock your features
Invalid or expired license key
License Activated
Your features are unlocked.
Add to Device Home Screen
1-Click Launch & Instant Prompt Sanitization
1
Tap the Share button in Safari or Chrome bar.
2
Scroll down and select Add to Home Screen.
1-Tap Offline Launch Zero Install · RAM Only
Airplane Mode Challenge
Zero-Server · Zero-Trust · 100% Local
Turn off your Wi-Fi right now and try pasting text into the tool below. It processes 100% in your local RAM without sending any network requests.
Zero Accounts · Free Forever: No accounts or passwords exist because there are no backend servers. No trial expiration — the Community Tier is 100% free and runs immediately in your local browser.