
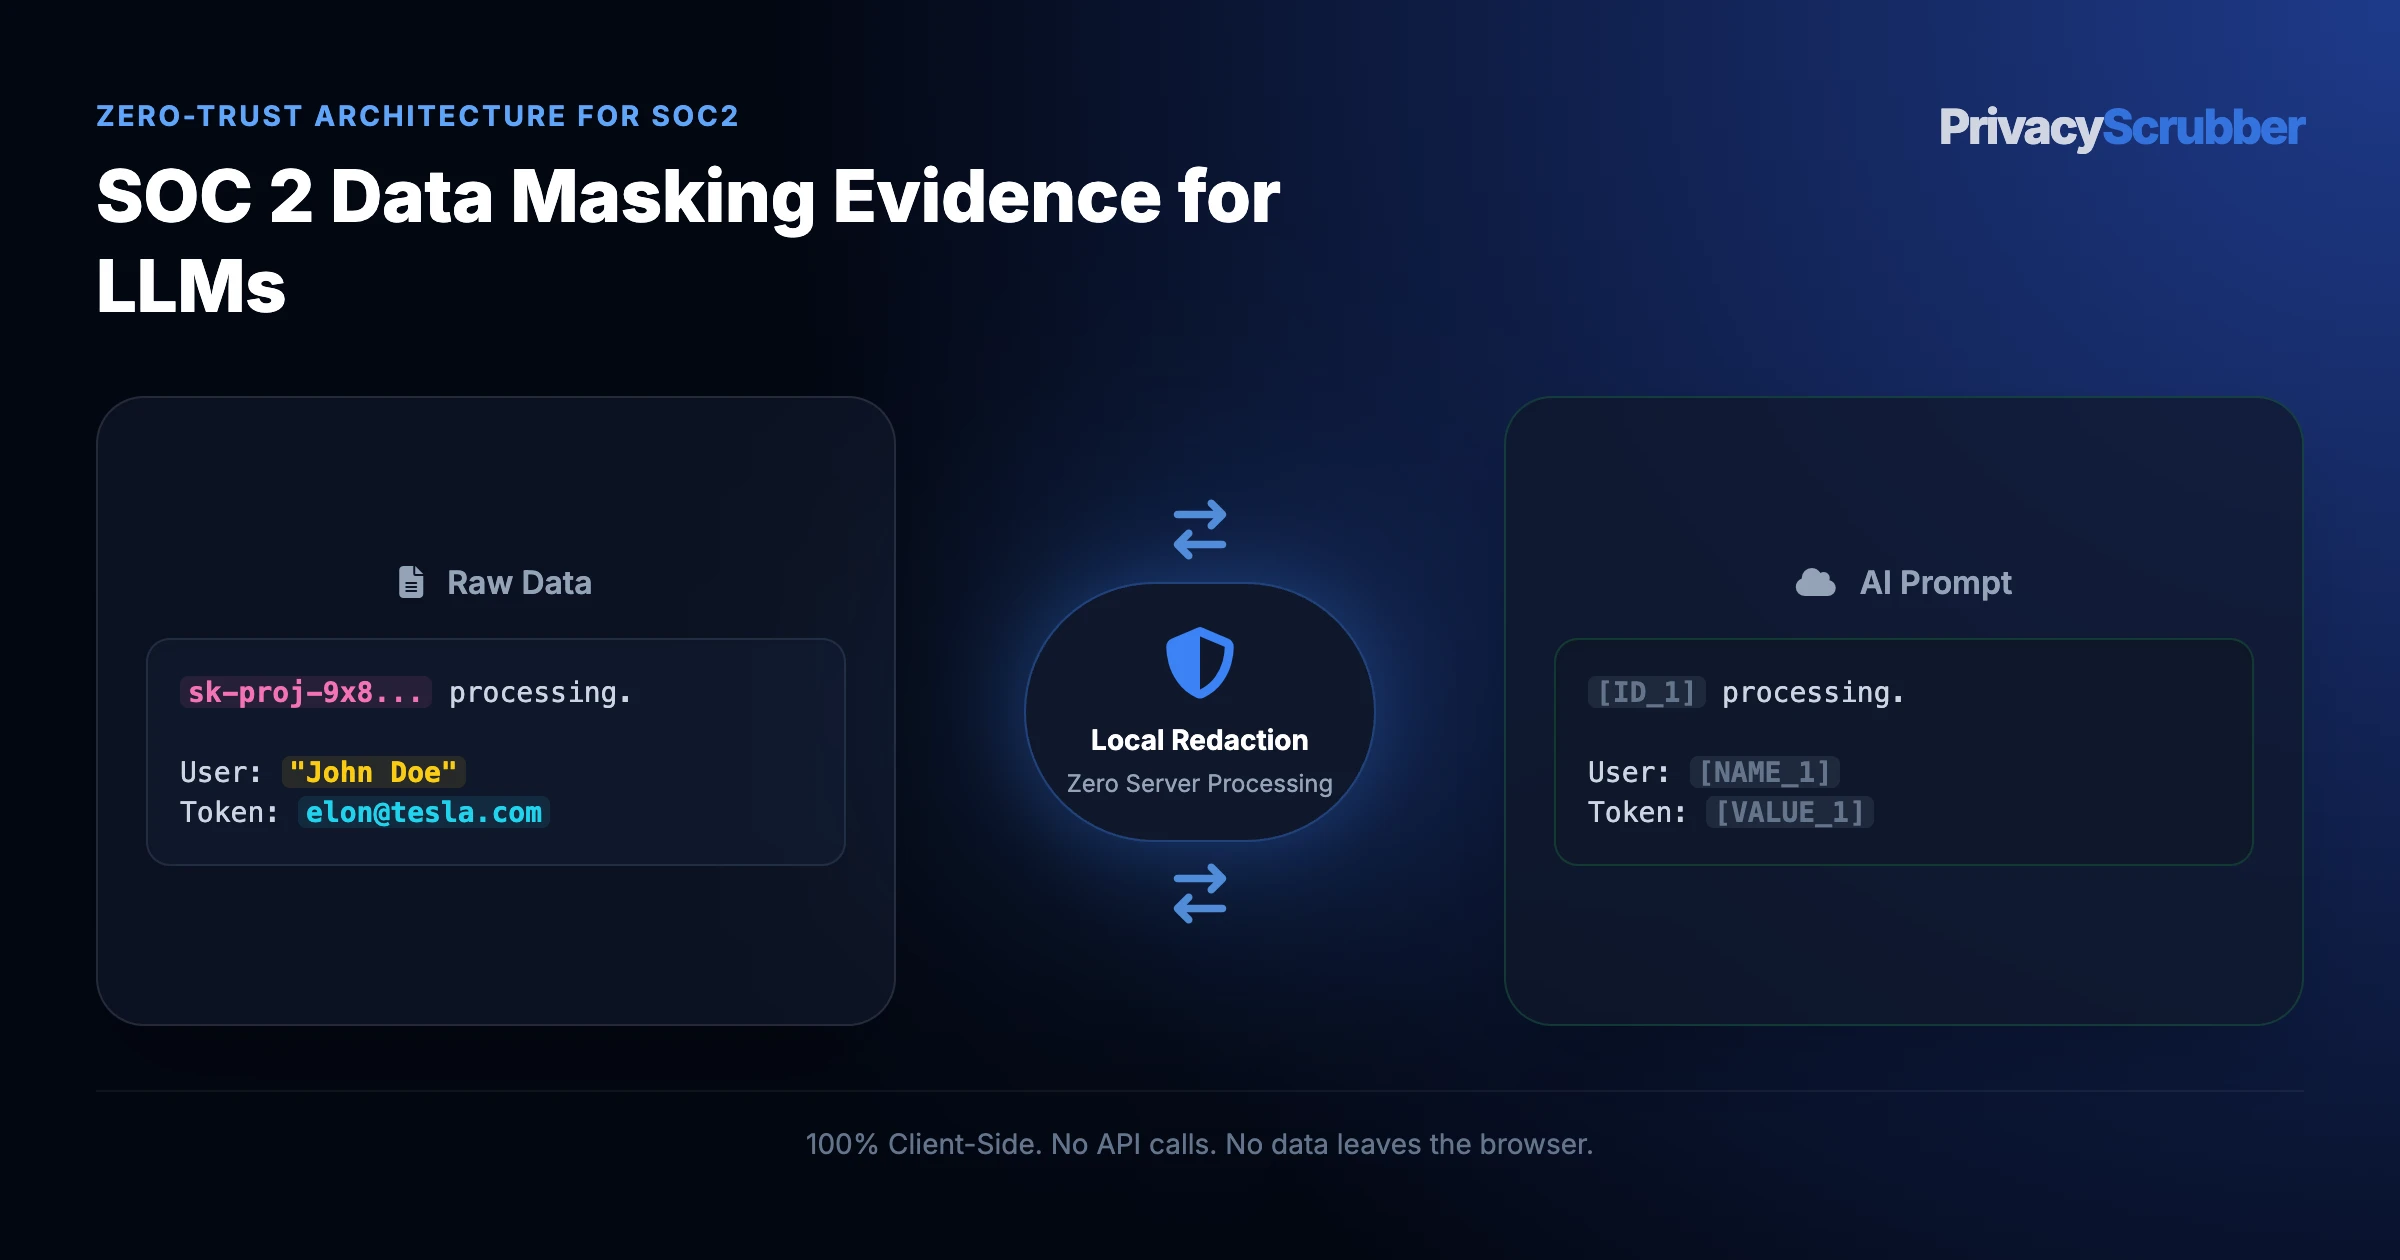
Handling SOC 2 Data Masking Evidence for LLMs under SOC 2 Type II Trust Service Criteria (Privacy and Security) means stopping CC6.1/CC6.7 cleartext egress gaps. Running soc 2 data masking evidence inside browser ZTDS shield keeps raw strings off Vanta while preserving [USER_1] structure.
SOC 2 Data Masking Evidence for LLMs: What Infosec and Audit Teams Expose to Cloud AI
High-compliance SOC 2 teams prevent CC6.1/CC6.7 cleartext egress gaps on SOC 2 Data Masking Evidence for LLMs using client-side browser ZTDS shield; SOC 2 AI privacy guides cover soc 2 data masking evidence isolation into [USER_1].
How to provide auditors with cryptographic proof of data masking for Generative AI workflows. Achieve SOC 2 CC6.1 compliance with in-browser scrubbing. External models retain soc 2 data masking evidence inputs longer than CISOs realize; substituting [SECRET_1] locally closes the leak inside Vanta.
Enforcing SOC 2 Type II Trust Service Criteria (Privacy and Security) on soc 2 data masking evidence
How to provide auditors with cryptographic proof of data masking for Generative AI workflows. Achieve SOC 2 CC6.1 compliance with in-browser scrubbing. Without local pre-scrubbing via browser ZTDS shield, CISOs handle soc 2 data masking evidence payloads that leak straight into Drata queues.
Instead of destroying prompt context on cc6.1 compliance ai, reversible [SECRET_1] surrogates keep multi-turn logic coherent across Vanta until local Reveal completes.
Field-by-Field Sanitization Rule for SOC 2 Data Masking Evidence for LLMs
Before serializing SOC 2 Data Masking Evidence for LLMs payloads to external LLMs, PrivacyScrubber partitions every attribute into reversible RAM tokens versus preserved logic:
| Document Field / Attribute | Action | RAM Surrogate | Statutory & Analytical Rationale |
|---|---|---|---|
| Subject Identifiers (soc 2 data masking evidence) | REDACT | [USER_1] | SOC 2 Type II Trust Service Criteria (Privacy and Security) guard prevents Vanta from retaining personal SOC 2 Data Masking Evidence for LLMs records. |
| Regulated Strings (llm masking audit trail) | REDACT | [ID_1] | Applies SOC 2 Type II Trust Service Criteria (Privacy and Security) minimization locally before SOC 2 Data Masking Evidence for LLMs leaves RAM. |
| Tax, Token & Session Strings (cc6.1 compliance ai) | REDACT | [SECRET_1] | Zero-egress tokenization keeps SOC 2 Data Masking Evidence for LLMs identifiers off vendor storage. |
| Schema & Formatting (SOC 2 Data Masking Evidence for LLMs) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for Vanta on soc 2 data masking evidence. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for SOC 2 Data Masking Evidence for LLMs while shielding real names. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets Vanta trace root causes cleanly inside sanitized cc6.1 compliance ai logs. |
Token-Preserving AI Prompt for SOC 2 Data Masking Evidence for LLMs
Submit this prompt wrapper with your masked SOC 2 Data Masking Evidence for LLMs input so the AI reasons over symbolic tokens without altering placeholder tags:
Role: SOC 2 advisor evaluating SOC 2 Data Masking Evidence for LLMs.
Sanitized tokens ([USER_1], [SECRET_1]) mask all soc 2 data masking evidence identifiers.
1. Flag operational gaps in cc6.1 compliance ai.
2. Recommend SOC 2 Type II Trust Service Criteria (Privacy and Security) fixes.
3. Keep [USER_1] unchanged.

[PASTE SOC 2 DATA MASKING EVIDENCE FOR LLMS TEXT]
Role: SOC 2 advisor evaluating SOC 2 Data Masking Evidence for LLMs.
Sanitized tokens ([USER_1], [SECRET_1]) mask all soc 2 data masking evidence identifiers.
1. Flag operational gaps in cc6.1 compliance ai.
2. Recommend SOC 2 Type II Trust Service Criteria (Privacy and Security) fixes.
3. Keep [USER_1] unchanged.

[PASTE SOC 2 DATA MASKING EVIDENCE FOR LLMS TEXT]
SOC 2 Type II Trust Service Criteria (Privacy and Security) Mandate Checkpoints: SOC 2 Data Masking Evidence for LLMs
GRC reviews covering SOC 2 Data Masking Evidence for LLMs check SOC 2 Type II Trust Service Criteria (Privacy and Security) boundary proof; SOC 2 data masking for generative AI demonstrates pre-egress masking for cc6.1 compliance ai payloads.
Local Tokenization Architecture: SOC 2 Data Masking Evidence for LLMs
volatile memory engine fixes SOC 2 Data Masking Evidence for LLMs leaks by replacing cc6.1 compliance ai with [USER_1] inside client memory while mirroring microsoft Copilot PII risk restoration.
Zero network handshakes fire when SOC 2 Data Masking Evidence for LLMs masks cc6.1 compliance ai offline, providing deterministic evidence matching client-side PII protection vs cloud apis.
