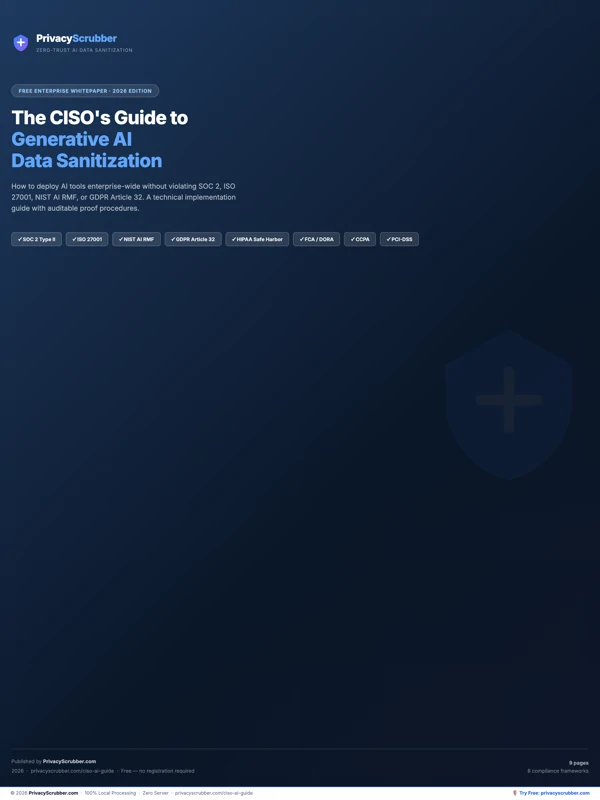
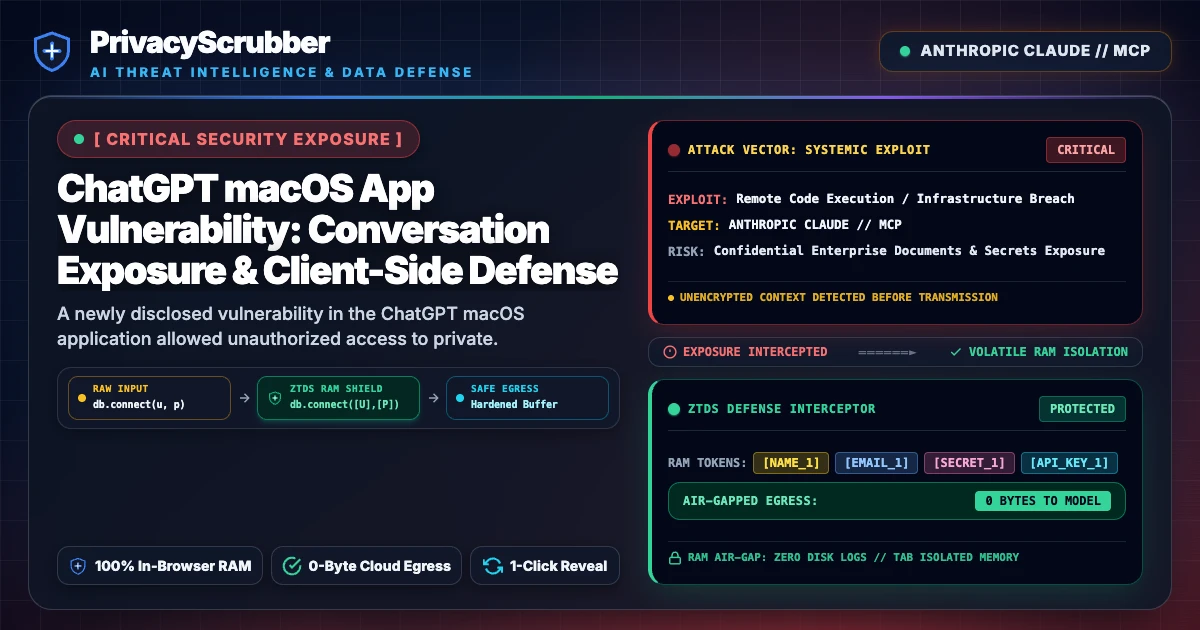
ChatGPT macOS App Vulnerability: Conversation Exposure & Client-Side Defense
ChatGPT macOS App Vulnerability: A newly disclosed vulnerability in the ChatGPT macOS application allowed unauthorized access to private conversation history, highlighting critical desktop app security gaps. PrivacyScrubber's zero-trust, client-side PII masking neutralizes these exposure risks by intercepting data in RAM before it hits local disk or cloud APIs.
Technical Incident Analysis
Recent threat intelligence highlights a critical security flaw in the ChatGPT macOS application where local storage mechanisms permitted unauthorized retrieval of sensitive user conversations. Attackers or malicious local utilities leveraging insecure file permissions could inspect session histories containing proprietary code snippets and personal identifiers. This incident mirrors broader desktop integration risks addressed by our AI Security Architecture, reinforcing that endpoints remain a major attack surface. For deeper context on how localized agent flaws cascade into enterprise data exposure, review our analysis on the Related AI Security Incident.
Enterprise Blast Radius & Compliance Risks
When corporate employees utilize native desktop AI clients that inadequately secure cached text and conversation logs, organizations face immediate regulatory liability under frameworks like GDPR, CCPA, and evolving European standards. Unredacted trade secrets, customer records, and internal credentials persisting on macOS local storage violate core data minimization mandates. Enterprises must align their deployment strategies with rigorous oversight guidelines such as those detailed in the EU AI Act Compliance Checklist for ChatGPT & Copilot Users (2026) to prevent severe regulatory penalties stemming from unmanaged desktop AI footprints.
Client-Side Mitigation via Zero-Trust Data Sanitization
Mitigating desktop app vulnerabilities requires decoupling sensitive data handling from trusting the underlying operating system cache or cloud vendor API storage. PrivacyScrubber solves this by enforcing browser-level and client-side RAM-only tokenization, ensuring that any PII or confidential payload is irreversibly masked before transmission or local caching occurs. By pairing zero-trust sanitization with ephemeral session isolation, enterprises completely eliminate shadow risks inherent in native client wrappers. Explore our comprehensive implementation framework in How to Redact PII Locally Before Sending Data to the Cloud to secure your workforce against endpoint exposure vectors.
Step-by-Step Integration Guide: ChatGPT macOS App Vulnerability
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT (OpenAI):
1 Method A: Instant Clipboard & Web Workspace
Fastest for ad-hoc debugging, server crash logs, or DB dumps:
- Paste the raw database dump, stack trace, or config payload into PrivacyScrubber.
- Click Sanitize Prompt to locally tokenize all tokens, hostnames, and API secrets with 100% Local RAM Processing.
- Copy the sanitized code and safely query ChatGPT, Claude, or Copilot.
- Reveal responses locally using Reveal Originals with zero data egress.
2 Method B: Chrome Extension & MCP Server
For automated in-browser prompt masking & IDE agents (Cursor / Cline):
- Install the free PrivacyScrubber Extension to auto-mask credentials directly in ChatGPT/Claude inputs.
- Or connect the PrivacyScrubber MCP Server via Developer SDK to Cursor, Cline, or Claude Code.
- Session token maps remain 100% in volatile RAM with zero telemetry.
- Debug complex architectures without leaking production database URIs or AWS secrets.
Local Redaction & Risk Matrix for Security
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| User / Server IP Addresses | [IP_ADDRESS] | High (DLP / Location footprinting) | IPv4 / IPv6 format strip |
| AWS_KEY Details | [AWS_KEY] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_HOSTNAME Details | [INTERNAL_HOSTNAME] | Medium (PII Exposure) | Deterministic local swap |
| MAC_ADDRESS Details | [MAC_ADDRESS] | Medium (PII Exposure) | Deterministic local swap |
| VULN_ID Details | [VULN_ID] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Lead DevSecOps Engineer / Cloud Security Architect · Target: ChatGPT (OpenAI)Act as a principal cloud systems architect. Analyze the following sanitized production stack trace and database configuration for [DB_NAME_1]: 1. Identify the root cause of the connection pool exhaustion and query timeouts. 2. Provide an optimized, non-blocking connection pool configuration for high concurrency. 3. Draft a step-by-step remediation patch. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Retain all cryptographic token identifiers ([DB_NAME_1], [INTERNAL_IP_1], [SECRET_1], [JWT_TOKEN_1]) strictly unchanged in your configuration suggestions for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Enterprise Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Sensitive Data compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any sensitive data text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.