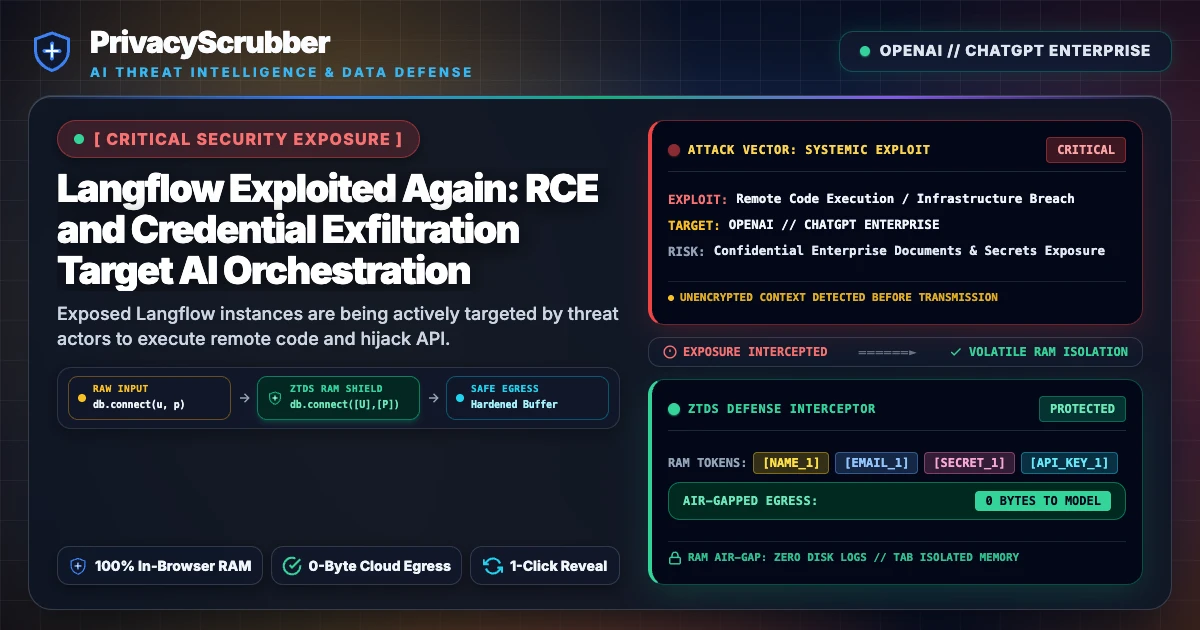
Langflow Exploited Again: RCE and Credential Exfiltration Target AI Orchestration
Langflow Exploited Again: Exposed Langflow instances are being actively targeted by threat actors to execute remote code and hijack API credentials. PrivacyScrubber's client-side zero-trust scrubbing blocks PII and secrets before they reach vulnerable visual agent pipelines.
Technical Incident Analysis
A wave of active exploitation has once again targeted exposed and insecurely configured Langflow instances. Security researchers have detected automated scanning campaigns designed to identify open Langflow visual orchestrators. Attackers leverage these open interfaces to execute arbitrary Python code directly within visual flow nodes, escalating local privileges to achieve Remote Code Execution (RCE) on the underlying hosting infrastructure. This enables actors to dump environment variables containing proprietary database credentials, vector store passwords, and enterprise API keys.
Modern flow-based development architectures frequently centralize high-privilege access keys to integrate seamlessly with various LLM providers. By exploiting the runtime execution model, attackers turn the visual playground into a weaponized command-and-control terminal. Understanding how to build a resilient AI Security Architecture is crucial to neutralizing these supply chain vectors, particularly when contrasted with the broad vulnerabilities highlighted in a Related AI Security Incident involving agentic workflow configurations.
Enterprise Blast Radius & Compliance Risks
For enterprises leveraging Langflow to orchestrate production Retrieval-Augmented Generation (RAG) pipelines, the blast radius of an RCE exploit is catastrophic. A compromised orchestration engine exposes not just metadata, but the direct data pipelines linking internal databases to external LLM providers. This structural failure introduces immediate liabilities under strict framework audits, specifically violating control domains related to vendor risk and third-party data handlers. Securing these pathways demands rigorous compliance protocols, which are detailed in our guide to SOC 2 AI Vendor Risk Management.
Client-Side Mitigation via Zero-Trust Data Sanitization
Traditional server-side firewalls are ineffective once an attacker has authenticated or bypassed the outer layers of visual orchestration tools. The only reliable defense is client-side, zero-trust data sanitization. PrivacyScrubber intercepts outgoing prompts and connection payloads at the browser level, utilizing a RAM-only, non-persisted regex and heuristic engine to sanitize sensitive information. By matching custom dictionaries and applying local tokenization, raw PII and master database keys are stripped and replaced with safe, synthetic placeholders prior to transmission.
By implementing client-side obfuscation, the active session mapping occurs inside an ephemeral sessionMap on the user's local machine, entirely isolated from the cloud backend. Even if a threat actor successfully executes RCE on your Langflow server, the data passing through the compromised node remains completely scrubbed, mitigating risk and aligning with the foundational guidelines of OWASP LLM Top 10 Security Controls.
Step-by-Step Integration Guide: Langflow Exploited Again
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use Developer AI & IDE Agent Pipelines:
1 Method A: Instant Clipboard & Web Workspace
Fastest for ad-hoc debugging, server crash logs, or DB dumps:
- Paste the raw database dump, stack trace, or config payload into PrivacyScrubber.
- Click Sanitize Prompt to locally tokenize all tokens, hostnames, and API secrets with 100% Local RAM Processing.
- Copy the sanitized code and safely query ChatGPT, Claude, or Copilot.
- Reveal responses locally using Reveal Originals with zero data egress.
2 Method B: Chrome Extension & MCP Server
For automated in-browser prompt masking & IDE agents (Cursor / Cline):
- Install the free PrivacyScrubber Extension to auto-mask credentials directly in ChatGPT/Claude inputs.
- Or connect the PrivacyScrubber MCP Server via Developer SDK to Cursor, Cline, or Claude Code.
- Session token maps remain 100% in volatile RAM with zero telemetry.
- Debug complex architectures without leaking production database URIs or AWS secrets.
Local Redaction & Risk Matrix for Security
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| User / Server IP Addresses | [IP_ADDRESS] | High (DLP / Location footprinting) | IPv4 / IPv6 format strip |
| AWS_KEY Details | [AWS_KEY] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_HOSTNAME Details | [INTERNAL_HOSTNAME] | Medium (PII Exposure) | Deterministic local swap |
| MAC_ADDRESS Details | [MAC_ADDRESS] | Medium (PII Exposure) | Deterministic local swap |
| VULN_ID Details | [VULN_ID] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Lead DevSecOps Engineer / Cloud Security Architect · Target: Developer AI & IDE Agent PipelinesAct as a principal cloud systems architect. Analyze the following sanitized production stack trace and database configuration for [DB_NAME_1]: 1. Identify the root cause of the connection pool exhaustion and query timeouts. 2. Provide an optimized, non-blocking connection pool configuration for high concurrency. 3. Draft a step-by-step remediation patch. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Retain all cryptographic token identifiers ([DB_NAME_1], [INTERNAL_IP_1], [SECRET_1], [JWT_TOKEN_1]) strictly unchanged in your configuration suggestions for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Enterprise Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Sensitive Data compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any sensitive data text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.