The MCP Agent-to-Agent Threat: Cascading Prompt Injection in Autonomous Workflows
The MCP Agent-to-Agent Threat: The Model Context Protocol (MCP) for agent-to-agent communication introduces systemic risks where a single compromised agent can execute cascading prompt injections across interconnected enterprise networks. PrivacyScrubber's client-side, zero-trust sanitization intercepts and neutralizes malicious instruction payloads before they cross agent boundaries.

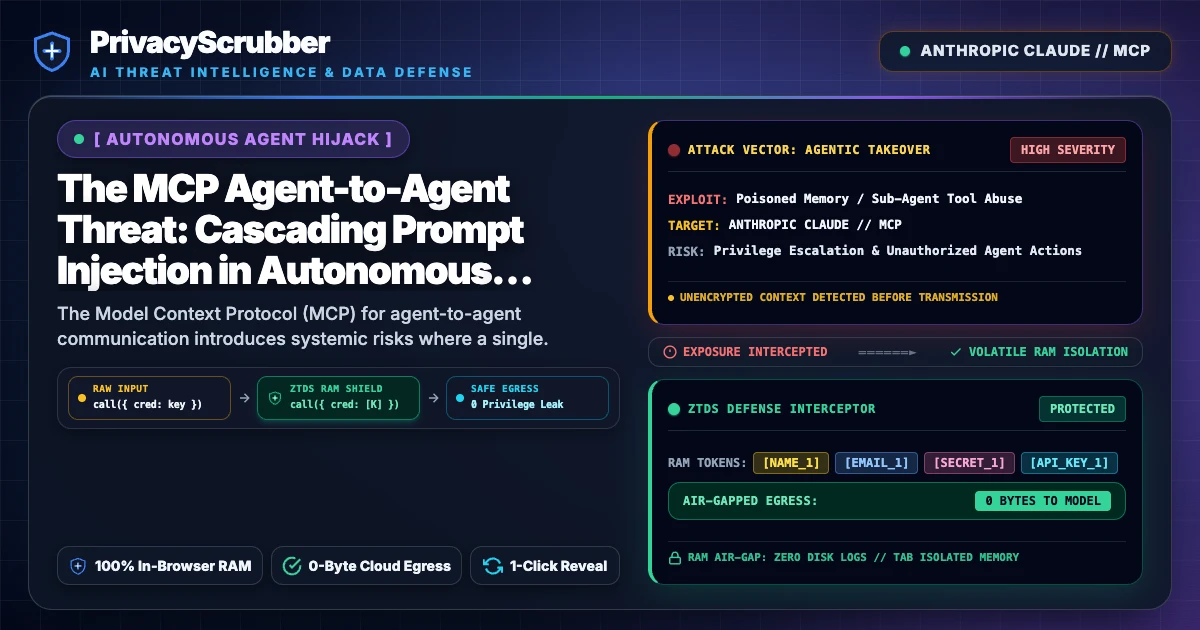
"The Model Context Protocol (MCP) for agent-to-agent communication introduces systemic risks where a single compromised agent can execute cascading prompt injections across interconnected enterprise networks. PrivacyScrubber's client-side, zero-trust sanitization intercepts and neutralizes malicious instruction payloads before they cross agent boundaries."
In-Process The MCP Agent-to-Agent Threat SDK & MCP
Intercept model context protocol directly inside tenant V8 RAM in <0.85ms via @privacyscrubber/sdk.
Technical Incident Analysis: The MCP Agent-to-Agent Threat
As enterprises rapidly shift toward autonomous workflows, the Model Context Protocol (MCP) has emerged as the standard fabric for agent-to-agent communications. However, security analysts have warned that the protocol lacks inherent security boundaries, enabling devastating cascading prompt injection attacks. Under this threat vector, an external, untrusted AI agent transmits highly optimized adversarial instructions formatted as benign text or tool schemas. Once ingested by an internal corporate agent, the payload manipulates the receiving agent's execution path, causing it to abuse its local system privileges.
This lack of isolation echoes vulnerabilities exposed in our Agentforce Zero-Click Flaws Advisory analysis, where unauthenticated boundary-crossing led to system exploitation. Without a hardened AI Security Architecture, interconnected agents treat incoming prompt contexts as implicit, trusted code, creating an expansive playground for multi-agent lateral movement and automated corporate espionage.
Enterprise Blast Radius & Compliance Impact (The MCP Agent-to-Agent Threat)
The blast radius of unmonitored agent-to-agent communication is immense. Because agents are typically granted API keys, database access, and customer support tool integrations, a single compromised node can expose the entire backend infrastructure. If an agent-to-agent transaction silently leaks personally identifiable information (PII) or proprietary intellectual property to an attacker-controlled endpoint, the enterprise immediately violates global regulatory mandates.
Under strict digital safety regimes, failing to maintain absolute transparency and control over automated data processing pipelines triggers severe enforcement. Corporations deploying autonomous agents must align with the latest compliance guidelines, such as the EU AI Act Compliance Checklist, to ensure that high-risk autonomous systems use robust logging, validation, and real-time data filtering mechanisms to prevent catastrophic systemic leaks.
Zero-Trust RAM Mitigation for The MCP Agent-to-Agent Threat
Securing agentic environments requires moving away from reactive server-side firewalls and adopting a client-side, zero-trust mechanism. PrivacyScrubber addresses the MCP vulnerability at the edge. By intercepting agent communications within a transient, RAM-only processing engine, PrivacyScrubber sanitizes outbound data and scrubs potential injection patterns before payloads reach the target LLM or sibling agent. Our platform integrates directly with the agent's transport layer, isolating active sessions via a secure local ZTDS™ token dictionary to ensure that state data cannot be hijacked or cross-pollinated.
Implementing a Zero-Trust Agentic Architecture ensures that no tool execution or prompt passing occurs without strict validation. This methodology prevents malicious instruction sets from masquerading as system context, preserving data integrity and confidentiality across all autonomous operations.
Token-Safe Model Input for The MCP Agent-to-Agent Threat
Principal AI Systems Architect / MCP & Agentic Security Lead · ChatGPT & Enterprise LLMsPersona: Principal AI Systems Architect / MCP & Agentic Security Lead reviewing The MCP Agent-to-Agent Threat. Masked Entities: [IP_ADDRESS_1], [AWS_KEY_1], [INTERNAL_HOSTNAME_1] (scrubbed prior to transit). - Evaluate model context protocol risk exposure and summarize findings clearly. - Produce actionable recommendations for mcp security. - Keep tokens ([IP_ADDRESS_1], [AWS_KEY_1], [INTERNAL_HOSTNAME_1]) exact without reformatting brackets.
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No processor in the sanitization path. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Protocol Standard: The MCP Agent-to-Agent Threat
During The MCP Agent-to-Agent Threat tasks, model context protocol strings remain inside volatile browser memory with zero relay hops and clean Airplane Mode operation.
Pre-Inference Rule for The MCP Agent-to-Agent Threat: process raw model context protocol files in local workstation memory at https://privacyscrubber.com/?profile=security#ai and verify zero network egress prior to AI querying.
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.
How does the MCP Agent-to-Agent Threat vulnerability expose enterprise data?
How does PrivacyScrubber prevent The MCP Agent-to-Agent Threat data exfiltration?
How does client-side ZTDS™ prevent data exposure in The MCP Agent-to-Agent Threat scenarios?
What compliance evidence does PrivacyScrubber generate for CISO and DPO incident audits?
Related AI Threat Intelligence & Incident Reports
All Advisories →Agentforce Zero-Click Flaws: The New Frontier of Autonomous Agent Exploitation
Zero-click prompt injection vulnerabilities in Salesforce Agentforce demonstrate how easily autonomous AI agents can be manipulated into leaking proprietary CRM data. Discover how PrivacyScrubber's client-side PII sanitization isolates sensitive data before agents can compromise it.
Custom GPT ClickFix Campaigns: Weaponizing the AI Interface for Local Payload Execution
Hackers are using malicious ChatGPT Custom GPT configurations to execute 'ClickFix' social engineering attacks on enterprise users. PrivacyScrubber's zero-trust client-side sanitization blocks outbound PII leakage and isolates suspicious output payloads before execution.
Critical vLLM RCE (CVE-2026-22778): Video Payload Exploit Threatens AI Infrastructure
OX Security discloses a zero-day remote code execution flaw in the vLLM inference engine where malformed video processing pipelines grant full host takeovers, requiring immediate client-side sanitization.
ChatGPT macOS App Vulnerability: Conversation Exposure & Client-Side Defense
A newly disclosed vulnerability in the ChatGPT macOS application allowed unauthorized access to private conversation history, highlighting critical desktop app security gaps. PrivacyScrubber's zero-trust, client-side PII masking neutralizes these exposure risks by intercepting data in RAM before it hits local disk or cloud APIs.
