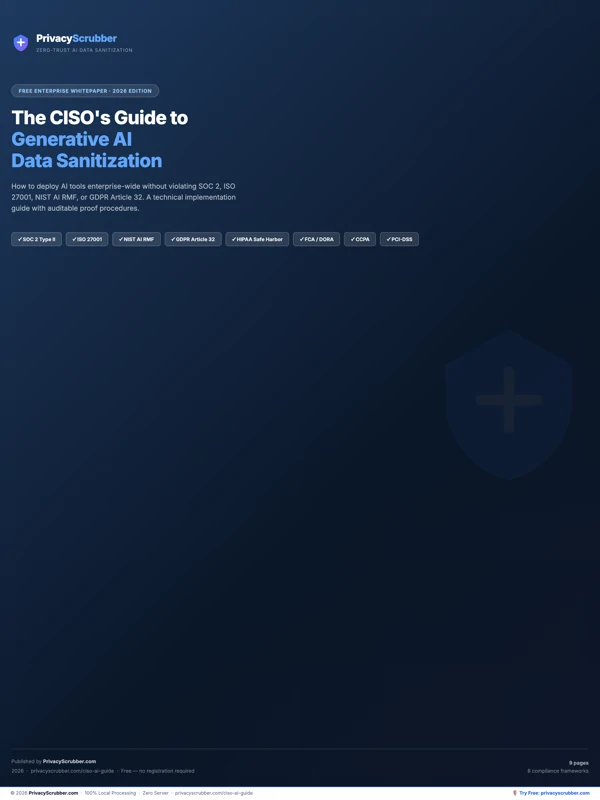
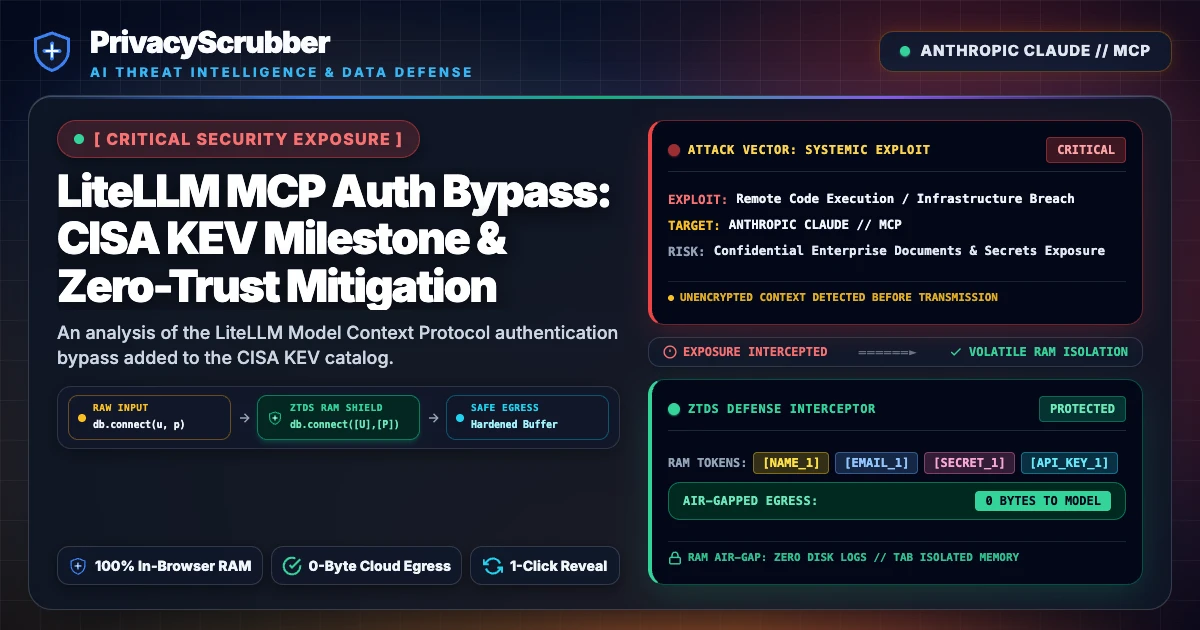
LiteLLM MCP Auth Bypass: CISA KEV Milestone & Zero-Trust Mitigation
LiteLLM MCP Auth Bypass: An analysis of the LiteLLM Model Context Protocol authentication bypass added to the CISA KEV catalog, examining how zero-trust client-side sanitization prevents downstream data leakage.
Technical Incident Analysis
The inclusion of the LiteLLM Model Context Protocol (MCP) authentication bypass in the CISA Known Exploited Vulnerabilities (KEV) catalog marks a watershed moment for AI infrastructure security. This flaw underscores the inherent risks of managing agentic routing without rigorous authorization boundaries. For a deeper understanding of how these mechanisms fail, review our AI Security Architecture guide, or cross-reference this incident with related supply-chain vectors detailed in our Related AI Security Incident coverage.
Enterprise Blast Radius & Compliance Risks
Gateway compromises and unauthorized MCP access break the perimeter defense model, instantly violating strict regulatory mandates under the EU AI Act and GDPR. Organizations failing to isolate downstream data feeds expose themselves to heavy penalties. To ensure your deployment maintains operational integrity and regulatory alignment, consult the EU AI Act Compliance: What It Means for Your ChatGPT Usage in 2026 framework.
Client-Side Mitigation via Zero-Trust Data Sanitization
Relying solely on perimeter security or vendor-side access tokens is no longer viable against sophisticated gateway vulnerabilities. PrivacyScrubber eliminates this risk through local, browser-based RAM processing that strips all sensitive identifiers before payloads ever touch compromised relays. Explore our implementation methods in How to Redact PII Locally Before Sending Data to the Cloud to establish true cryptographic isolation.
Step-by-Step Integration Guide: LiteLLM MCP Auth Bypass
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use LLM Code Assistants & Database Agents:
1 Method A: Zero-Trust Web Workspace (Copy-Paste)
Best for manual prompt sanitization without installing plugins:
- Open the PrivacyScrubber Web App dashboard in your browser.
- Paste the raw prompt or text containing sensitive details of LiteLLM MCP Auth Bypass.
- Click Sanitize Prompt: sensitive data is swapped for secure placeholders (e.g.,
[NAME_1]). - Submit the sanitized prompt to LLM Code Assistants & Database Agents.
- Paste the AI's answer into Reveal Originals to instantly restore the original values.
2 Method B: Chrome Extension (In-Context Redaction)
For automated, inline de-identification within chat interfaces:
- Install the free PrivacyScrubber Chrome Extension from the Web Store.
- Navigate to your AI chat interface. A PrivacyScrubber shield button will appear inline.
- Paste your raw prompt. Click the shield button to sanitize all identifiers instantly in-place.
- Send the prompt to the AI chatbot.
- The extension automatically intercepts and detokenizes the response, displaying raw values to you.
Local Redaction & Risk Matrix for Security
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| User / Server IP Addresses | [IP_ADDRESS] | High (DLP / Location footprinting) | IPv4 / IPv6 format strip |
| AWS_KEY Details | [AWS_KEY] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_HOSTNAME Details | [INTERNAL_HOSTNAME] | Medium (PII Exposure) | Deterministic local swap |
| MAC_ADDRESS Details | [MAC_ADDRESS] | Medium (PII Exposure) | Deterministic local swap |
| VULN_ID Details | [VULN_ID] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Database Administrator / API Security Lead · Target: LLM Code Assistants & Database AgentsAct as a senior database administrator. Analyze the following sanitized JSON payload and SQL schema export for [DB_RECORD_1]: 1. Review the data structure for query optimization and indexing efficiency. 2. Generate refactored SQL queries with optimized JOIN operations. 3. Ensure output adheres strictly to standard schema syntax. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Preserve all cryptographic token placeholders ([DB_RECORD_1], [API_KEY_1], [IP_ADDRESS_1]) exactly as formatted for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Enterprise Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Your Whole Team on Real Client Data. Safely. $99/mo Flat.
No per-seat pricing. No DPA negotiation. No IT portal. Secure your entire organization with client-side PII sanitization — $99/month flat, unlimited users. SOC 2 & HIPAA ready. Works in Airplane Mode.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Sensitive Data compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any sensitive data text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Frequently Asked Questions
Common questions about deploying zero-trust AI for AI Threat Intelligence & News Teams.