
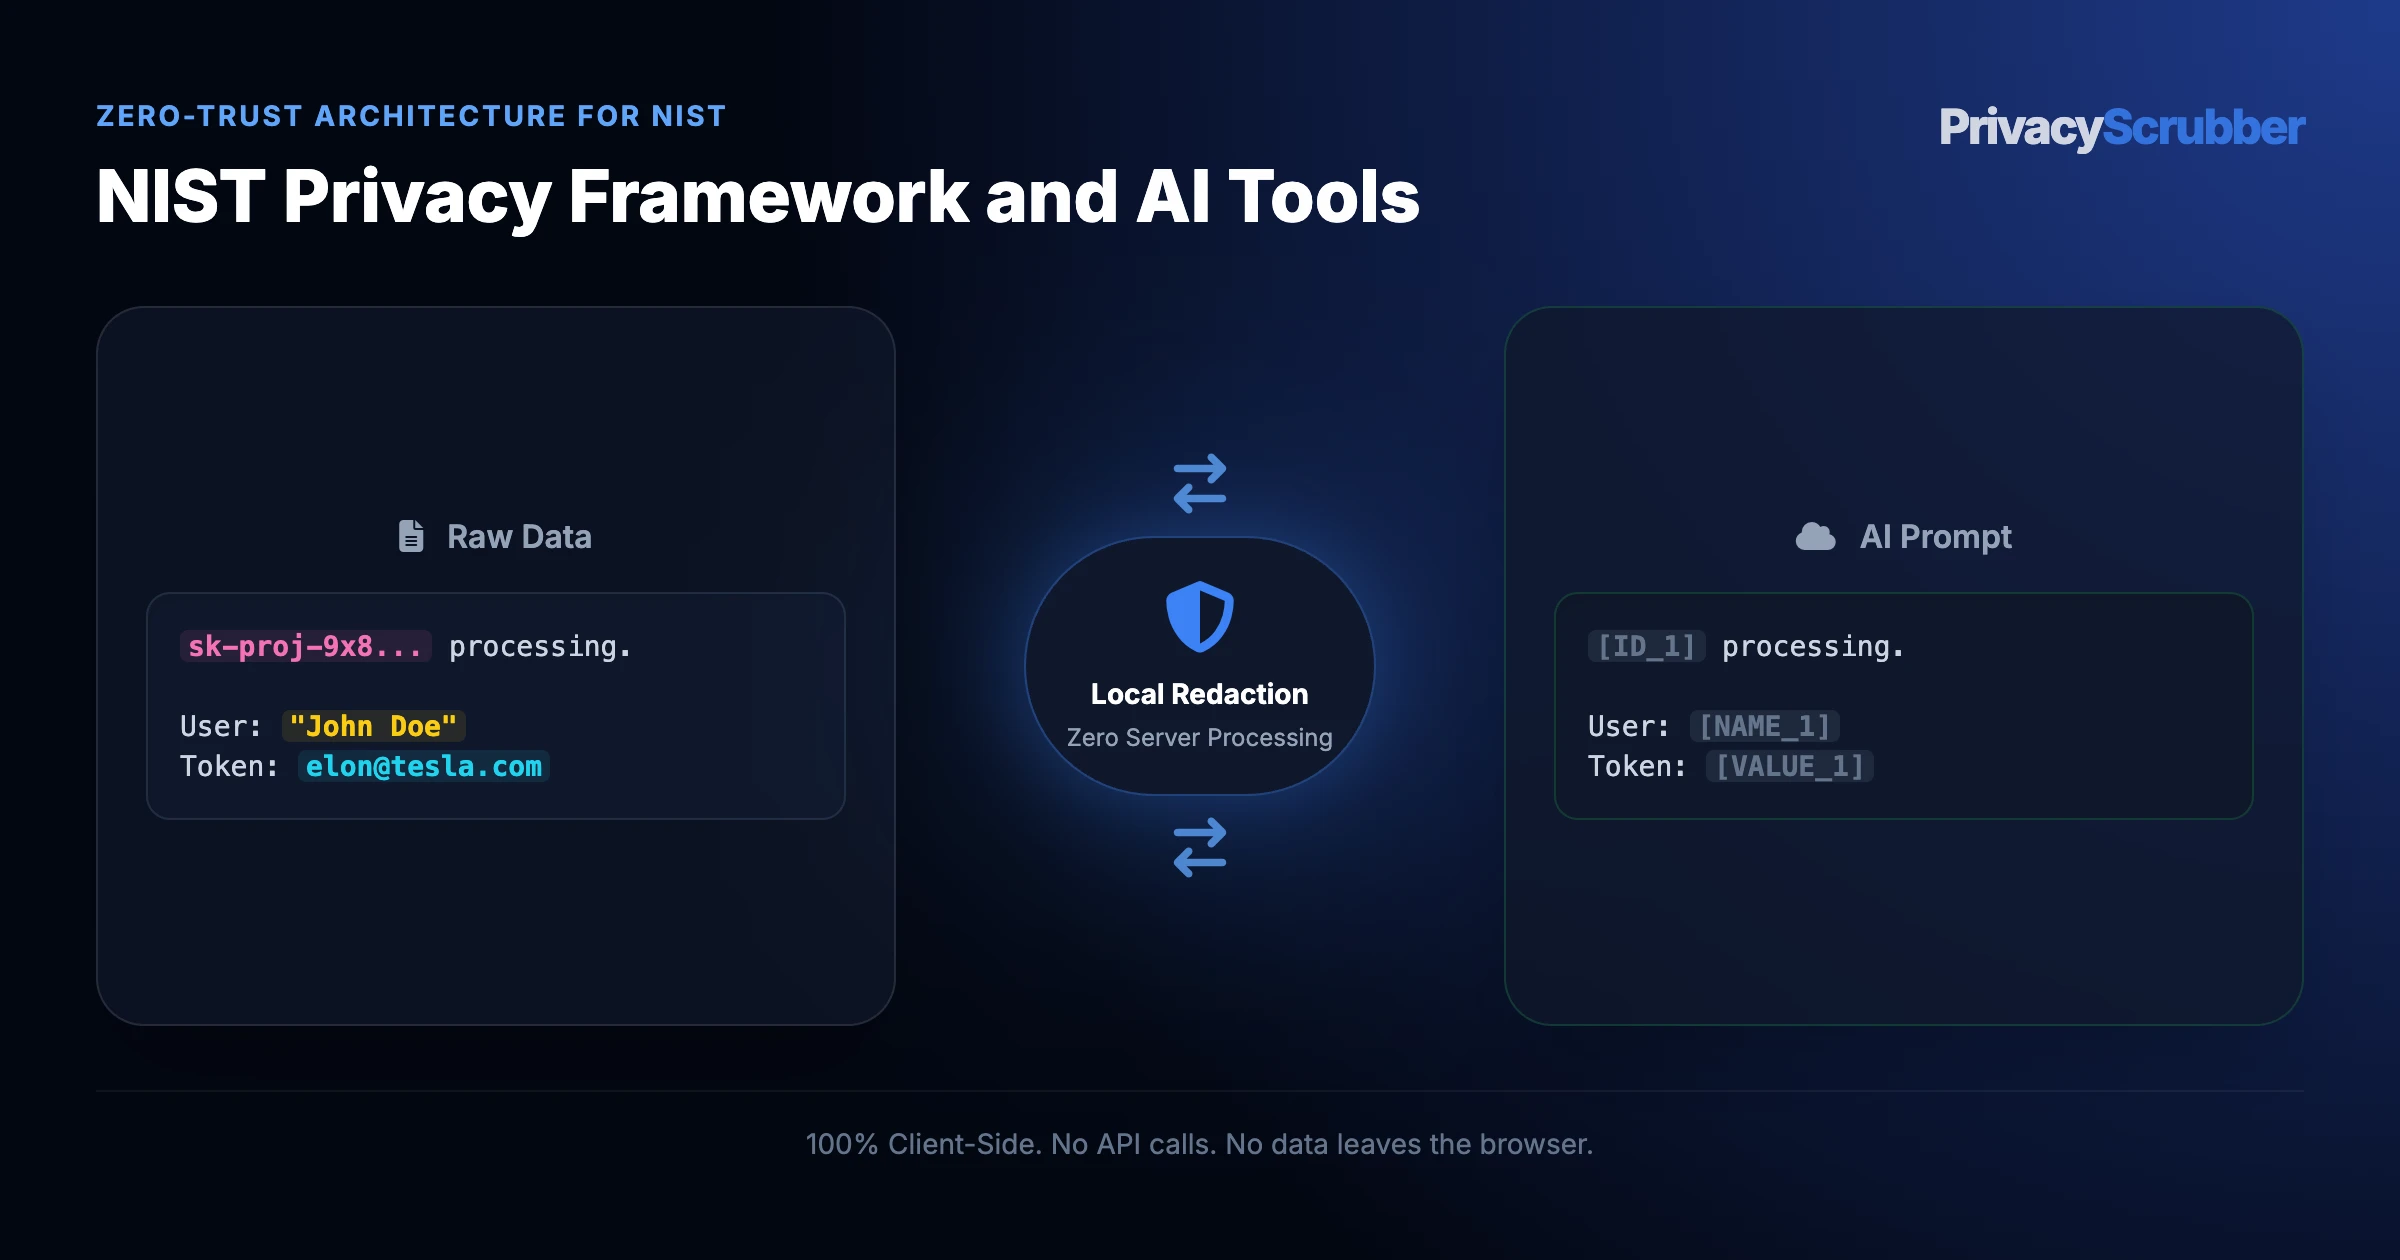
The NIST Privacy Framework's GOVERN function requires organizations to establish policies for managing PII in AI pipelines. Without a technical enforcement mechanism, policies are unenforceable. PrivacyScrubber provides the enforcement layer: PII cannot reach AI systems because it is tokenized before the network request is made.
Data Leakage Risks in NIST Privacy Framework and AI Tools for Security Compliance Teams
Modern NIST teams depend on local government systems for NIST Privacy Framework and AI Tools, yet raw govern AI data flows creates unmasked NIST privacy framework AI exposure. Follow NIST AI privacy guides to isolate NIST privacy framework AI in RAM.
Feeding NIST privacy framework AI and NIST AI RMF privacy to external AI triggers unmasked NIST privacy framework AI exposure immediately. Apply the NIST Privacy Framework to enterprise AI deployments. Redact sensitive PII in local browser RAM with zero server egress or cloud leaks. Downstream filters never catch cleartext inside local government systems.
Client-Boundary Guardrails: NIST Privacy Framework and AI Tools
High-throughput NIST Privacy Framework and AI Tools pipelines break when govern AI data flows hits third-party FedRAMP-authorized AI services loggers. Installing local RAM (NIST) strips sensitive fields into [ID_1] inside local heap memory.
Instead of destroying prompt context on govern AI data flows, reversible [CLEARANCE_1] surrogates keep multi-turn logic coherent across local government systems until local Reveal completes.
Balancing AI Context & Privacy in NIST Privacy Framework and AI Tools
Under PT-3) and NIST AI Risk Management Framework (AI RMF), agency IT managers enforce this selective masking rule on NIST Privacy Framework and AI Tools:
| Field Category | Directive | Token / State | Why It Matters for AI & Audit |
|---|---|---|---|
| Keys & Account Codes (govern AI data flows) | REDACT | [ID_1] | Stops govern AI data flows credentials from entering cloud telemetry on NIST Privacy Framework and AI Tools. |
| Internal IDs inside NIST Privacy Framework and AI Tools | REDACT | [NAME_1] / [ID_1] | Prevents unmasked NIST privacy framework AI exposure via pre-send local RAM (NIST) substitution. |
| Private Records in NIST Privacy Framework and AI Tools | REDACT | [CLEARANCE_1] | Replaces direct PII with [CLEARANCE_1] inside volatile client memory. |
| Numeric Totals & Ratios (govern AI data flows) | PRESERVE | Cleartext ($ / %) | Enables accurate calculations across NIST Privacy Framework and AI Tools without revealing identities. |
| Aggregation Counts & Deltas | PRESERVE | Cleartext Metrics | Supports statistical analysis of NIST privacy framework AI without linking individuals. |
| PT-3) and NIST AI Risk Management Framework (AI RMF) Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map NIST Privacy Framework and AI Tools findings directly against policy clauses. |
Zero-Trust System Prompt: NIST Privacy Framework and AI Tools
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Review NIST privacy framework AI workflow for NIST Privacy Framework and AI Tools under PT-3) and NIST AI Risk Management Framework (AI RMF).
1. Inspect interactions between [NAME_1] and [CLEARANCE_1].
2. Deliver concise steps preserving every bracketed token.

[INSERT SCRUBBED TEXT]
Review NIST privacy framework AI workflow for NIST Privacy Framework and AI Tools under PT-3) and NIST AI Risk Management Framework (AI RMF).
1. Inspect interactions between [NAME_1] and [CLEARANCE_1].
2. Deliver concise steps preserving every bracketed token.

[INSERT SCRUBBED TEXT]
Governance Requirements Governing NIST Privacy Framework and AI Tools
Enforcing PT-3) and NIST AI Risk Management Framework (AI RMF) on NIST Privacy Framework and AI Tools connects directly with NIST AI rmf PII controls—ensuring NIST privacy framework AI becomes [ID_1] before cloud transit.
Local Tokenization Architecture: NIST Privacy Framework and AI Tools
Whether pasted in chat or loaded via SDK, offline endpoint scrubber isolates NIST privacy framework AI into [EMAIL_1] for NIST Privacy Framework and AI Tools in sync with anonymize loss amounts and settlement reserves.
In Airplane Mode, offline endpoint scrubber tokenizes NIST privacy framework AI across NIST Privacy Framework and AI Tools in sub-millisecond RAM, validating secure AI grant writing controls.
