
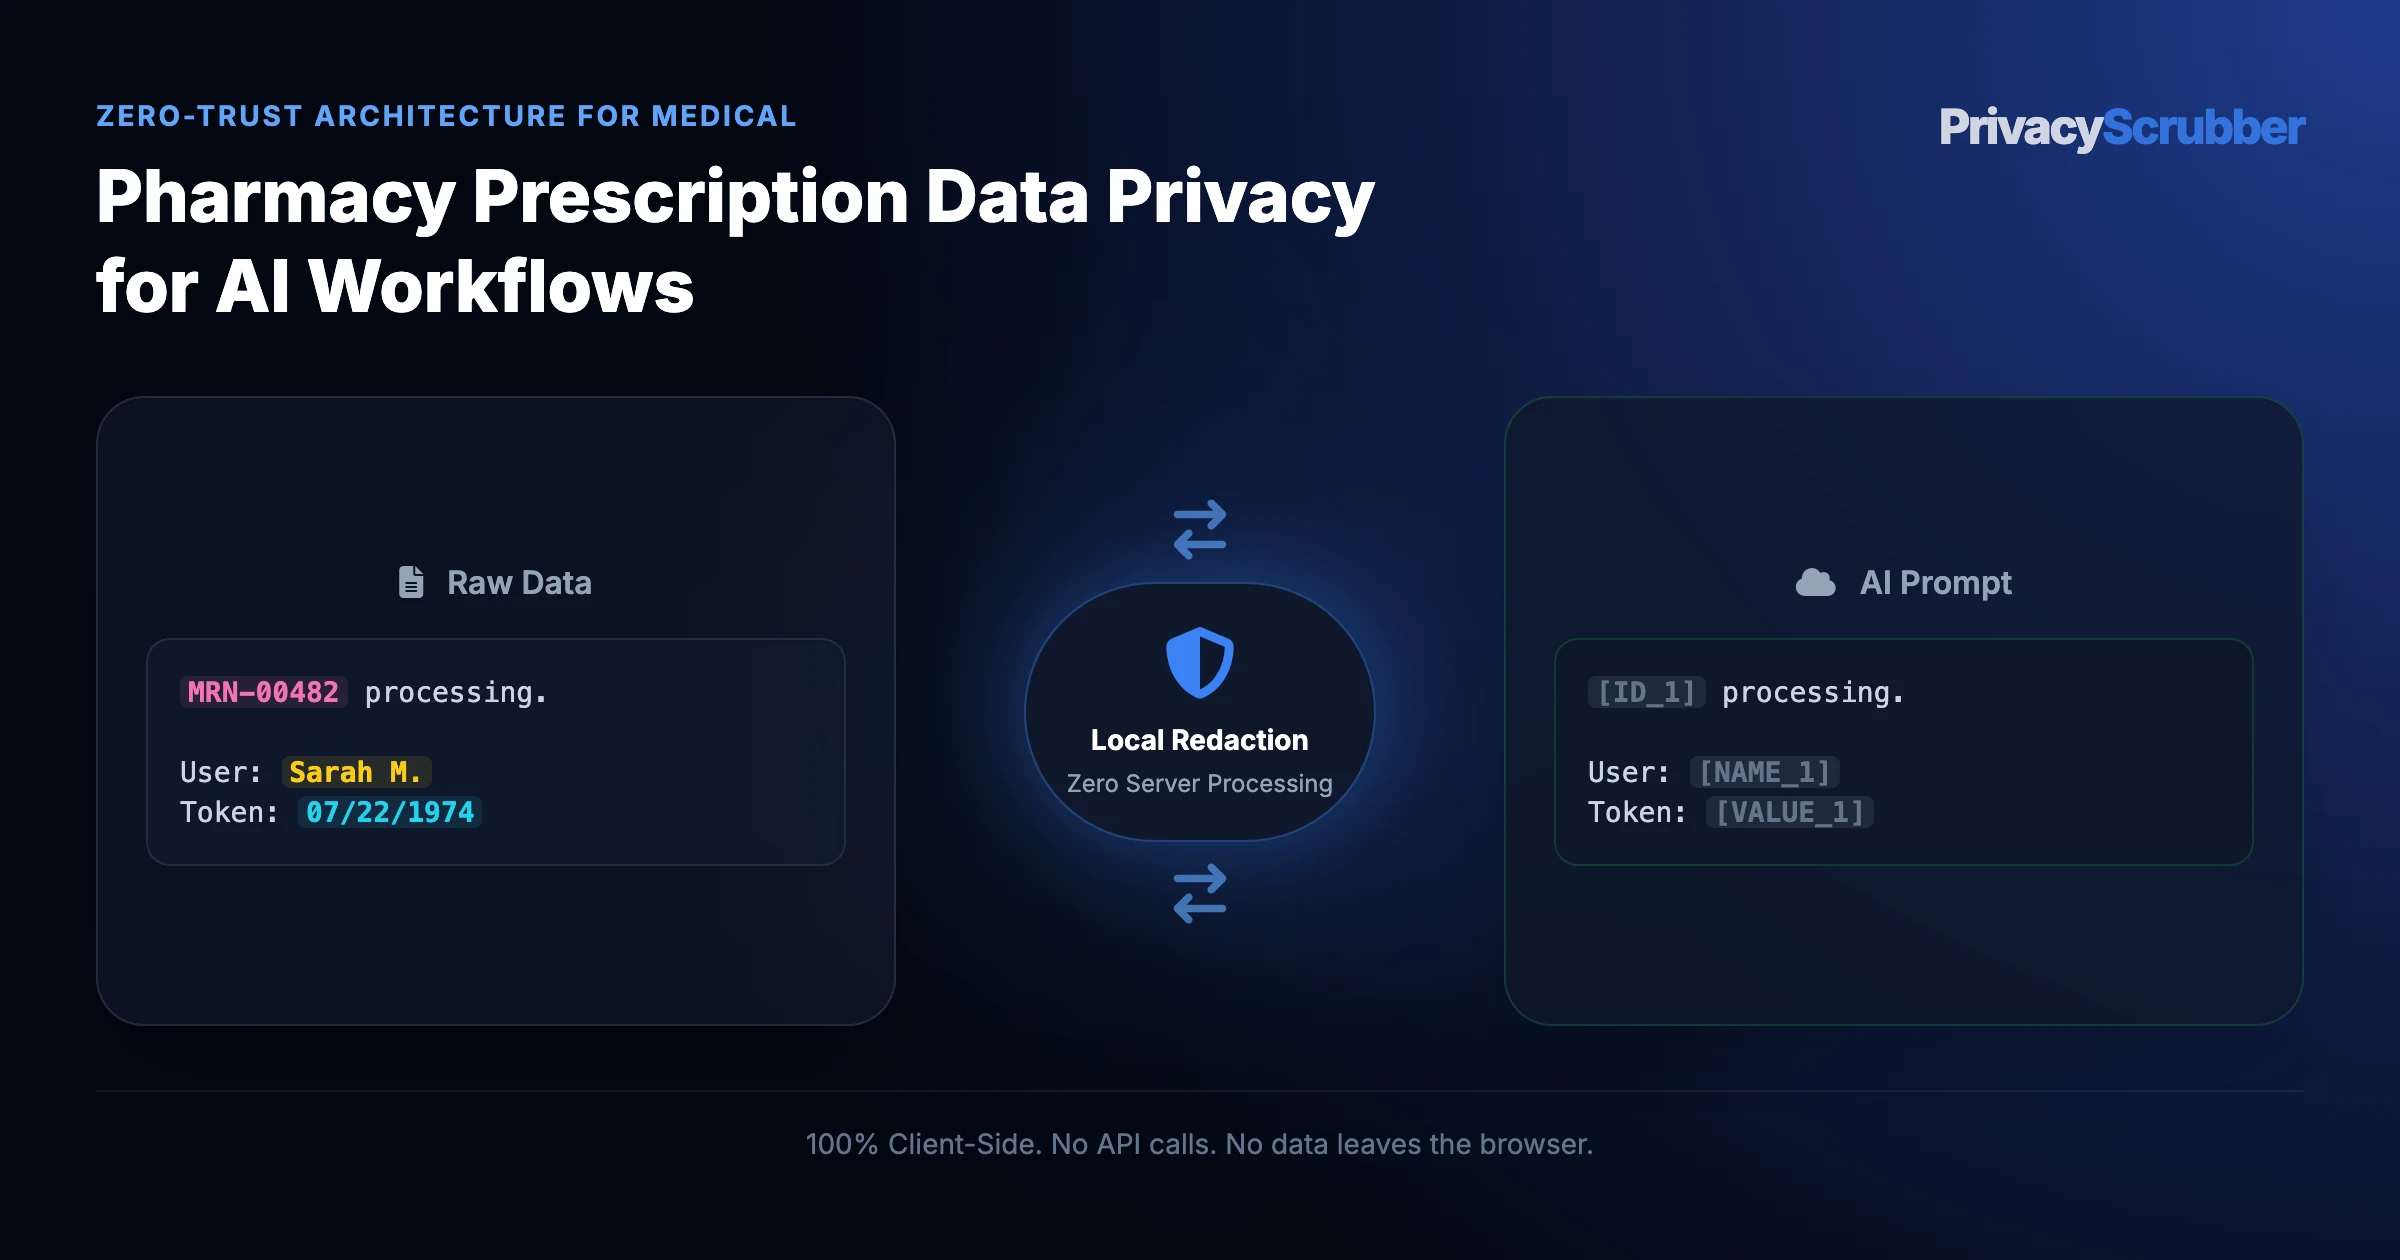
To guarantee pharmacy prescription data privacy in AI workflows, retail pharmacies, hospital inpatient dispensaries, and Pharmacy Benefit Managers (PBMs) must strip all 18 HIPAA Safe Harbor identifiers—alongside prescription serial numbers (Rx#), prescriber DEA/NPI credentials, and PBM member IDs—inside local browser RAM before passing medication profiles to external LLMs. Under the HIPAA Privacy Rule (45 CFR § 164.514(b)(2)), the Confidentiality of Substance Use Disorder Patient Records regulations (42 CFR Part 2), DEA Controlled Substance Act recordkeeping rules (21 CFR Part 1304), and GDPR Article 9, prescription histories reveal highly sensitive diagnoses (HIV antiretrovirals, psychiatric pharmacotherapy, oncology regimens, and buprenorphine/MAT schedules). PrivacyScrubber enforces a Technical Safe Harbor by tokenizing patient and prescriber identities 100% in volatile browser memory while preserving NDC codes, drug names, dosages, and SIG instructions.
| Pharmacy & PBM AI Security Dimension | Raw Rx Profile Paste to LLMs | Cloud Healthcare NLP / PBM Proxy | Manual Pharmacist Redaction | PrivacyScrubber (ZTDS Local RAM) |
|---|---|---|---|---|
| Patient PHI & 42 CFR Part 2 Egress | 100% exposed to external AI model servers | Raw Rx list transmitted to third-party cloud API | Zero network egress, but misses embedded Rx/PBM IDs | 0 Bytes (100% local browser RAM execution) |
| Prescriber DEA & NPI Protection | Leaked into LLM logs (high credential-theft risk) | Often ignored by generic consumer PII regexes | Tedious manual lookup across multi-drug histories | Automatic DEA, NPI & Rx Serial Tokenization |
| NDC-11, Dosage & SIG Fidelity | Preserved (at cost of reportable HIPAA breach) | False positives corrupt 11-digit NDC codes and mg strengths | Risk of deleting frequency/route instructions | 100% Preserved (Drug names, NDC, mg/mL, SIG intact) |
| Specialty Pharmacy Prior Auth Restoration | Not applicable (PHI already leaked) | One-way masking; requires manual re-entry | Manual re-typing of Rx# and subscriber IDs | Instant 1-click Reverse Scrub in local RAM |
| Board of Pharmacy & HIPAA Audit Proof | None (Unmonitored clinical Shadow AI) | External cloud vendor access logs | Zero cryptographic verification | Signed SHA-256 Local Compliance Receipt |
Protect Specialty Pharmacy Prior Auths & MTM Workflows
Equip clinical pharmacists, MTM teams, and prior authorization specialists with unlimited seats for $99/mo flat (TEAMS), or embed headless NCPDP/HL7 pharmacy sanitization into backend pipelines via the Developer SDK ($299/mo).
What Healthcare Practitioners and Staff Send to AI — and What They Should Be Sending Instead
Ensuring patient confidentiality for Pharmacy Prescription Data Privacy for AI Workflows is a critical clinical objective as medical teams adopt new technology. Paste-handling patient data into ChatGPT, clinical decision support AI, and AI-assisted documentation platforms risks exposing Protected Health Information (PHI) to third-party servers. Our medical AI privacy guides details the clinical standards for securing the medical perimeter. The primary risk is exposing Protected Health Information (PHI) to third-party AI servers, which constitutes a HIPAA breach and carries penalties up to $1.9M per violation category.Uploading patient notes or analyzing clinical files in public AI systems violates PHI protection rules if identifiers are sent to the cloud. Legacy 'do not train' settings fail to meet strict BAA standards. For clinicians, nurses, medical researchers, and healthcare administrators, this exposure must be managed proactively. Ensure pharmacy prescription data privacy in local RAM. Mask Rx numbers, DEA/NPI IDs, and patient PHI while preserving NDC codes and drug dosages for AI.
