
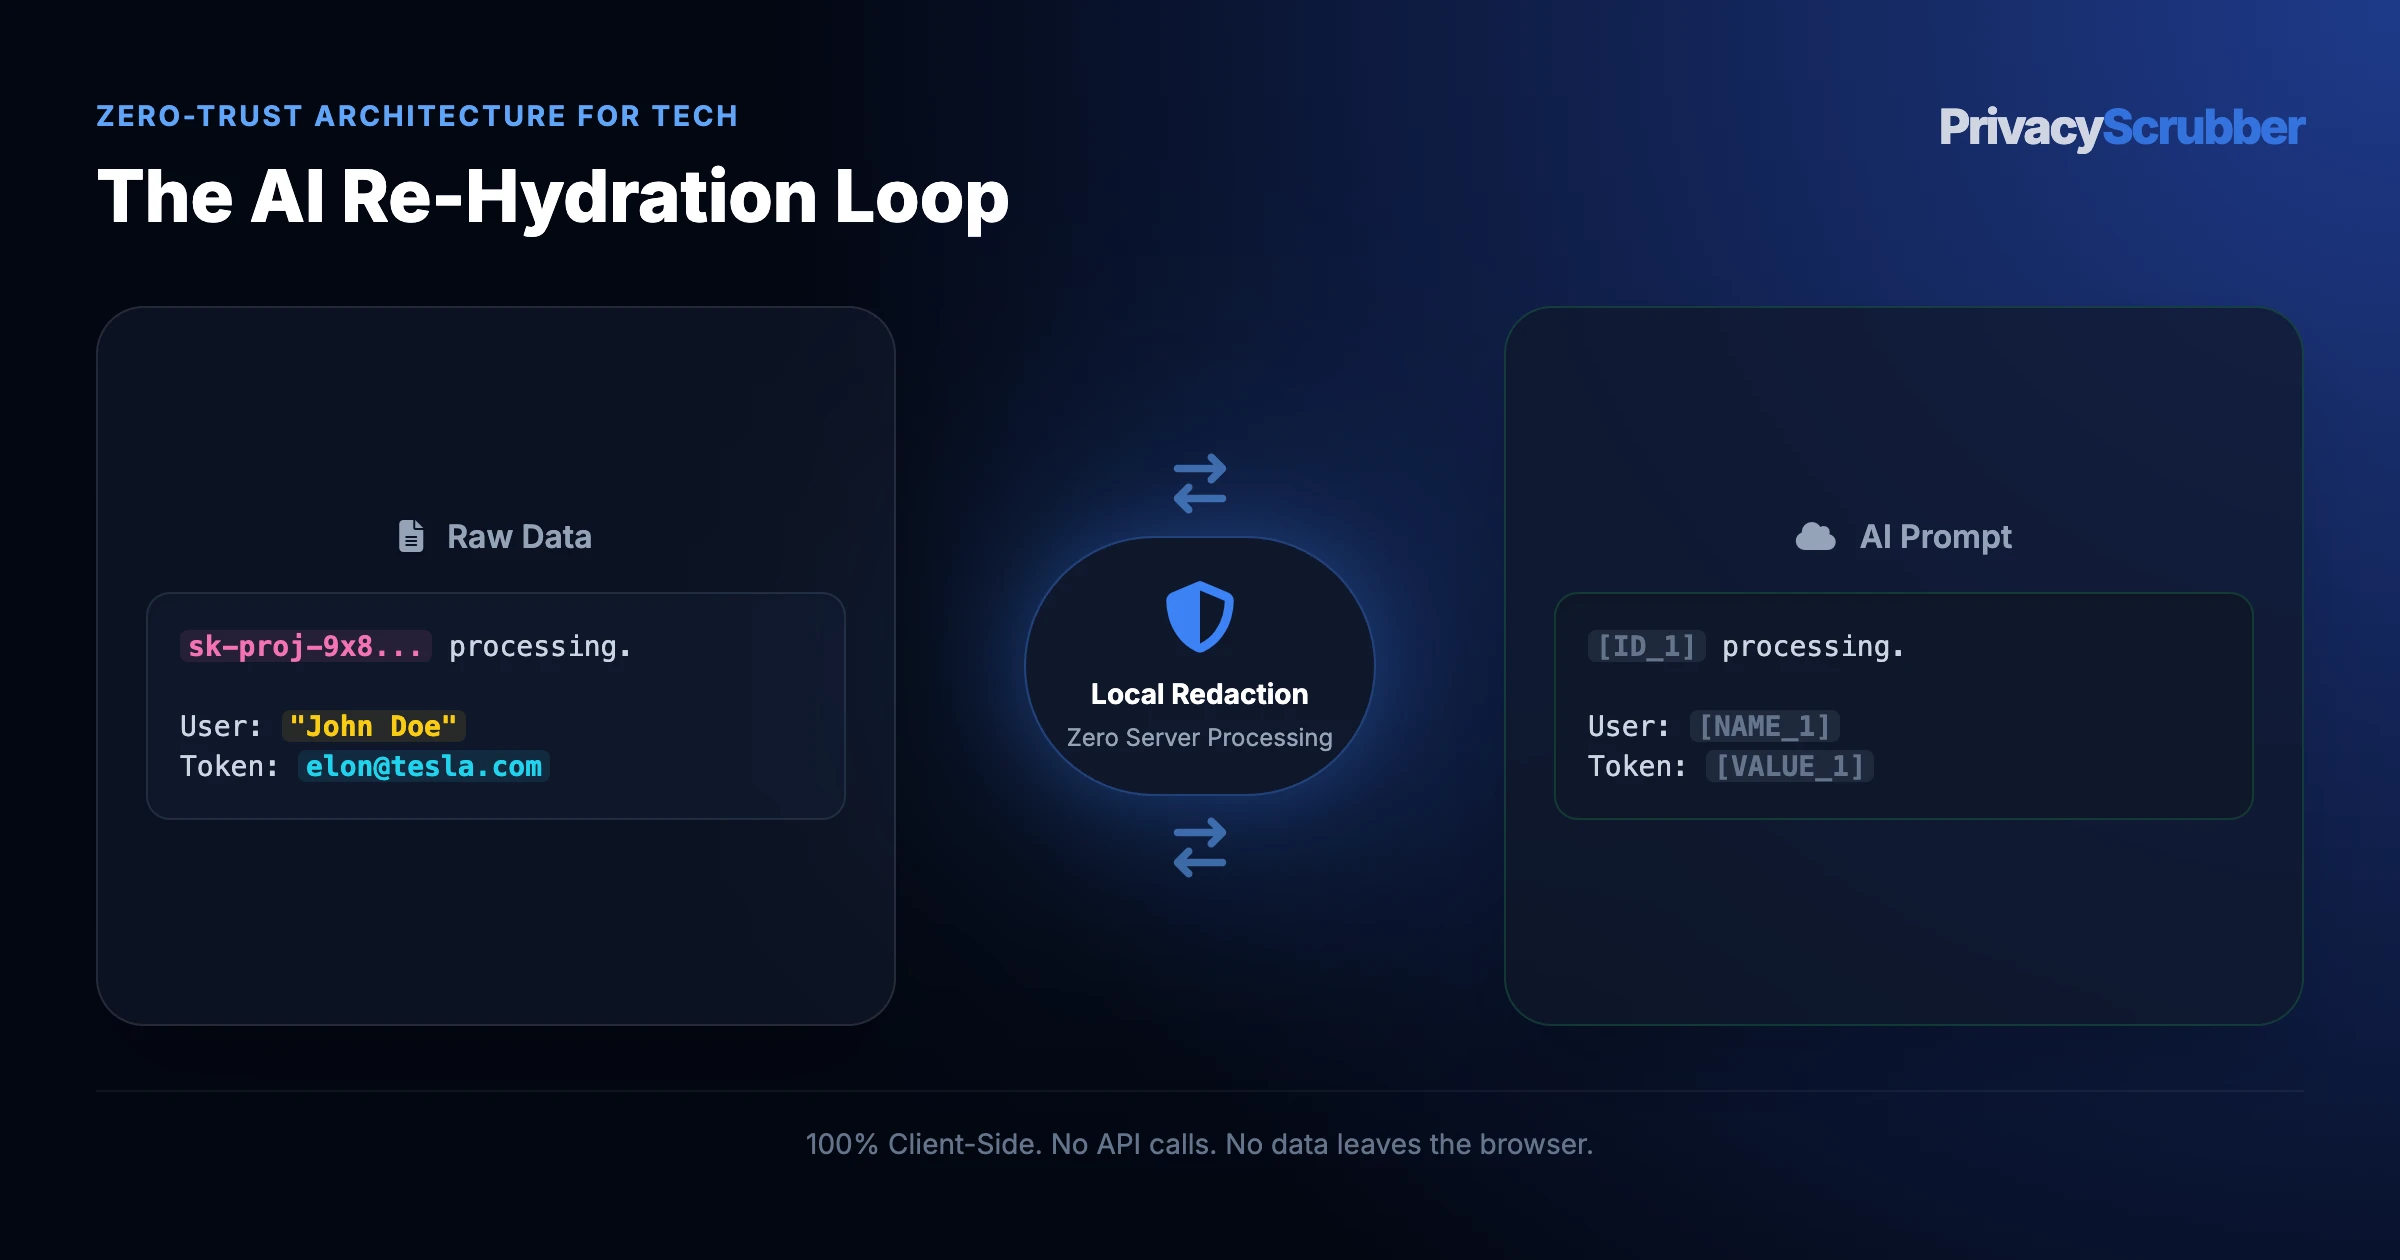
Redacting PII protects data but ruins usability. The AI re-hydration loop lets you swap original names and emails back into the AI draft locally, closing the loop without cloud leakage.
The AI Re-Hydration Loop: What Technology Teams Expose to Cloud AI
Every raw reveal original data ai query for The AI Re-Hydration Loop widens GDPR Article 25 (privacy by design) audit scope on ChatGPT API. Our AI Privacy Engineering AI privacy guides mask sensitive attributes into [SECRET_1] beforehand.
Exposure in The AI Re-Hydration Loop happens the instant unredacted reveal original data ai leaves your socket. Complete your secure AI workflow. Learn how to safely reveal original names and emails from tokenized AI drafts in your local browser. Only volatile memory engine stops unmasked runbooks in AI plugins beforehand.
The Utility Gap in Prompt Redaction
Redacting personal information before sending it to an LLM is the only way to satisfy regulatory standards. However, if the AI responds with advice for [CUSTOMER_1] or drafts an email addressing [NAME_1], you cannot use the text as-is. Manually replacing tokens by copying and pasting values from your original document is slow and error-prone, destroying productivity.
Re-Hydrating AI Output at the Client Level
PrivacyScrubber solves this through its local re-hydration loop (Reveal). When you click Scrub, the original data is stored in a temporary, tab-isolated RAM session map. You send the safe, tokenized prompt to ChatGPT or Claude. When you paste the AI's response back, the tool automatically matches the placeholders and restores the real values.
Cross-Tab Security and Enterprise Workflows
This loop is highly secure. Because session maps are tied to individual tabs, there is zero risk of data crossing between different projects. This is essential for reverse scrubbing PII data locally. Support teams can safely write personalized customer replies using a customer support AI integration, and academic researchers can analyze interviews using safe transcript translation.
Entity Handling Standard for The AI Re-Hydration Loop
Use the classification table below to separate high-liability The AI Re-Hydration Loop attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Subject Identifiers (reveal original data ai) | REDACT | [EMAIL_1] | GDPR Article 25 (privacy by design) guard prevents ChatGPT API from retaining personal The AI Re-Hydration Loop records. |
| Regulated Strings (local session map detokenizer) | REDACT | [NAME_1] | Applies GDPR Article 25 (privacy by design) minimization locally before The AI Re-Hydration Loop leaves RAM. |
| Tax, Token & Session Strings (de-tokenize chatgpt response) | REDACT | [IP_1] | Zero-egress tokenization keeps The AI Re-Hydration Loop identifiers off vendor storage. |
| Schema & Formatting (The AI Re-Hydration Loop) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for ChatGPT API on reveal original data ai. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for The AI Re-Hydration Loop while shielding real names. |
| Severity Codes & Relative Sequence | PRESERVE | Cleartext Steps | Lets ChatGPT API trace root causes cleanly inside sanitized de-tokenize chatgpt response logs. |
Bijective Prompt Blueprint for The AI Re-Hydration Loop
Copy this prompt frame when handing sanitized The AI Re-Hydration Loop context to frontier LLMs under strict zero-egress rules:
Role: AI Privacy Engineering advisor evaluating The AI Re-Hydration Loop.
Sanitized tokens ([EMAIL_1], [IP_1]) mask all reveal original data ai identifiers.
1. Flag operational gaps in de-tokenize chatgpt response.
2. Recommend GDPR Article 25 (privacy by design) fixes.
3. Keep [EMAIL_1] unchanged.

[PASTE THE AI RE-HYDRATION LOOP TEXT]
Role: AI Privacy Engineering advisor evaluating The AI Re-Hydration Loop.
Sanitized tokens ([EMAIL_1], [IP_1]) mask all reveal original data ai identifiers.
1. Flag operational gaps in de-tokenize chatgpt response.
2. Recommend GDPR Article 25 (privacy by design) fixes.
3. Keep [EMAIL_1] unchanged.

[PASTE THE AI RE-HYDRATION LOOP TEXT]
Minimizing GDPR Article 25 (privacy by design) Exposure in The AI Re-Hydration Loop
Under GDPR Article 25 (privacy by design), sending raw de-tokenize chatgpt response records to ChatGPT API creates audit risk; which of the following is not an example of pii? direct vs. indirect data breakdown & interactive scanner details technical safe harbor inside local RAM.
How to Sanitize The AI Re-Hydration Loop in Local RAM (Zero Cloud Egress)
Instead of cloud proxies, volatile memory engine runs inside CTOs memory—transforming The AI Re-Hydration Loop strings into [EMAIL_1] / [IP_1] per github Copilot privacy.
Test reveal original data ai scrubbing offline or run npx ztds-audit in CI: The AI Re-Hydration Loop emits 0 bytes per sanitize scanned tax returns for AI financial analysis.
