
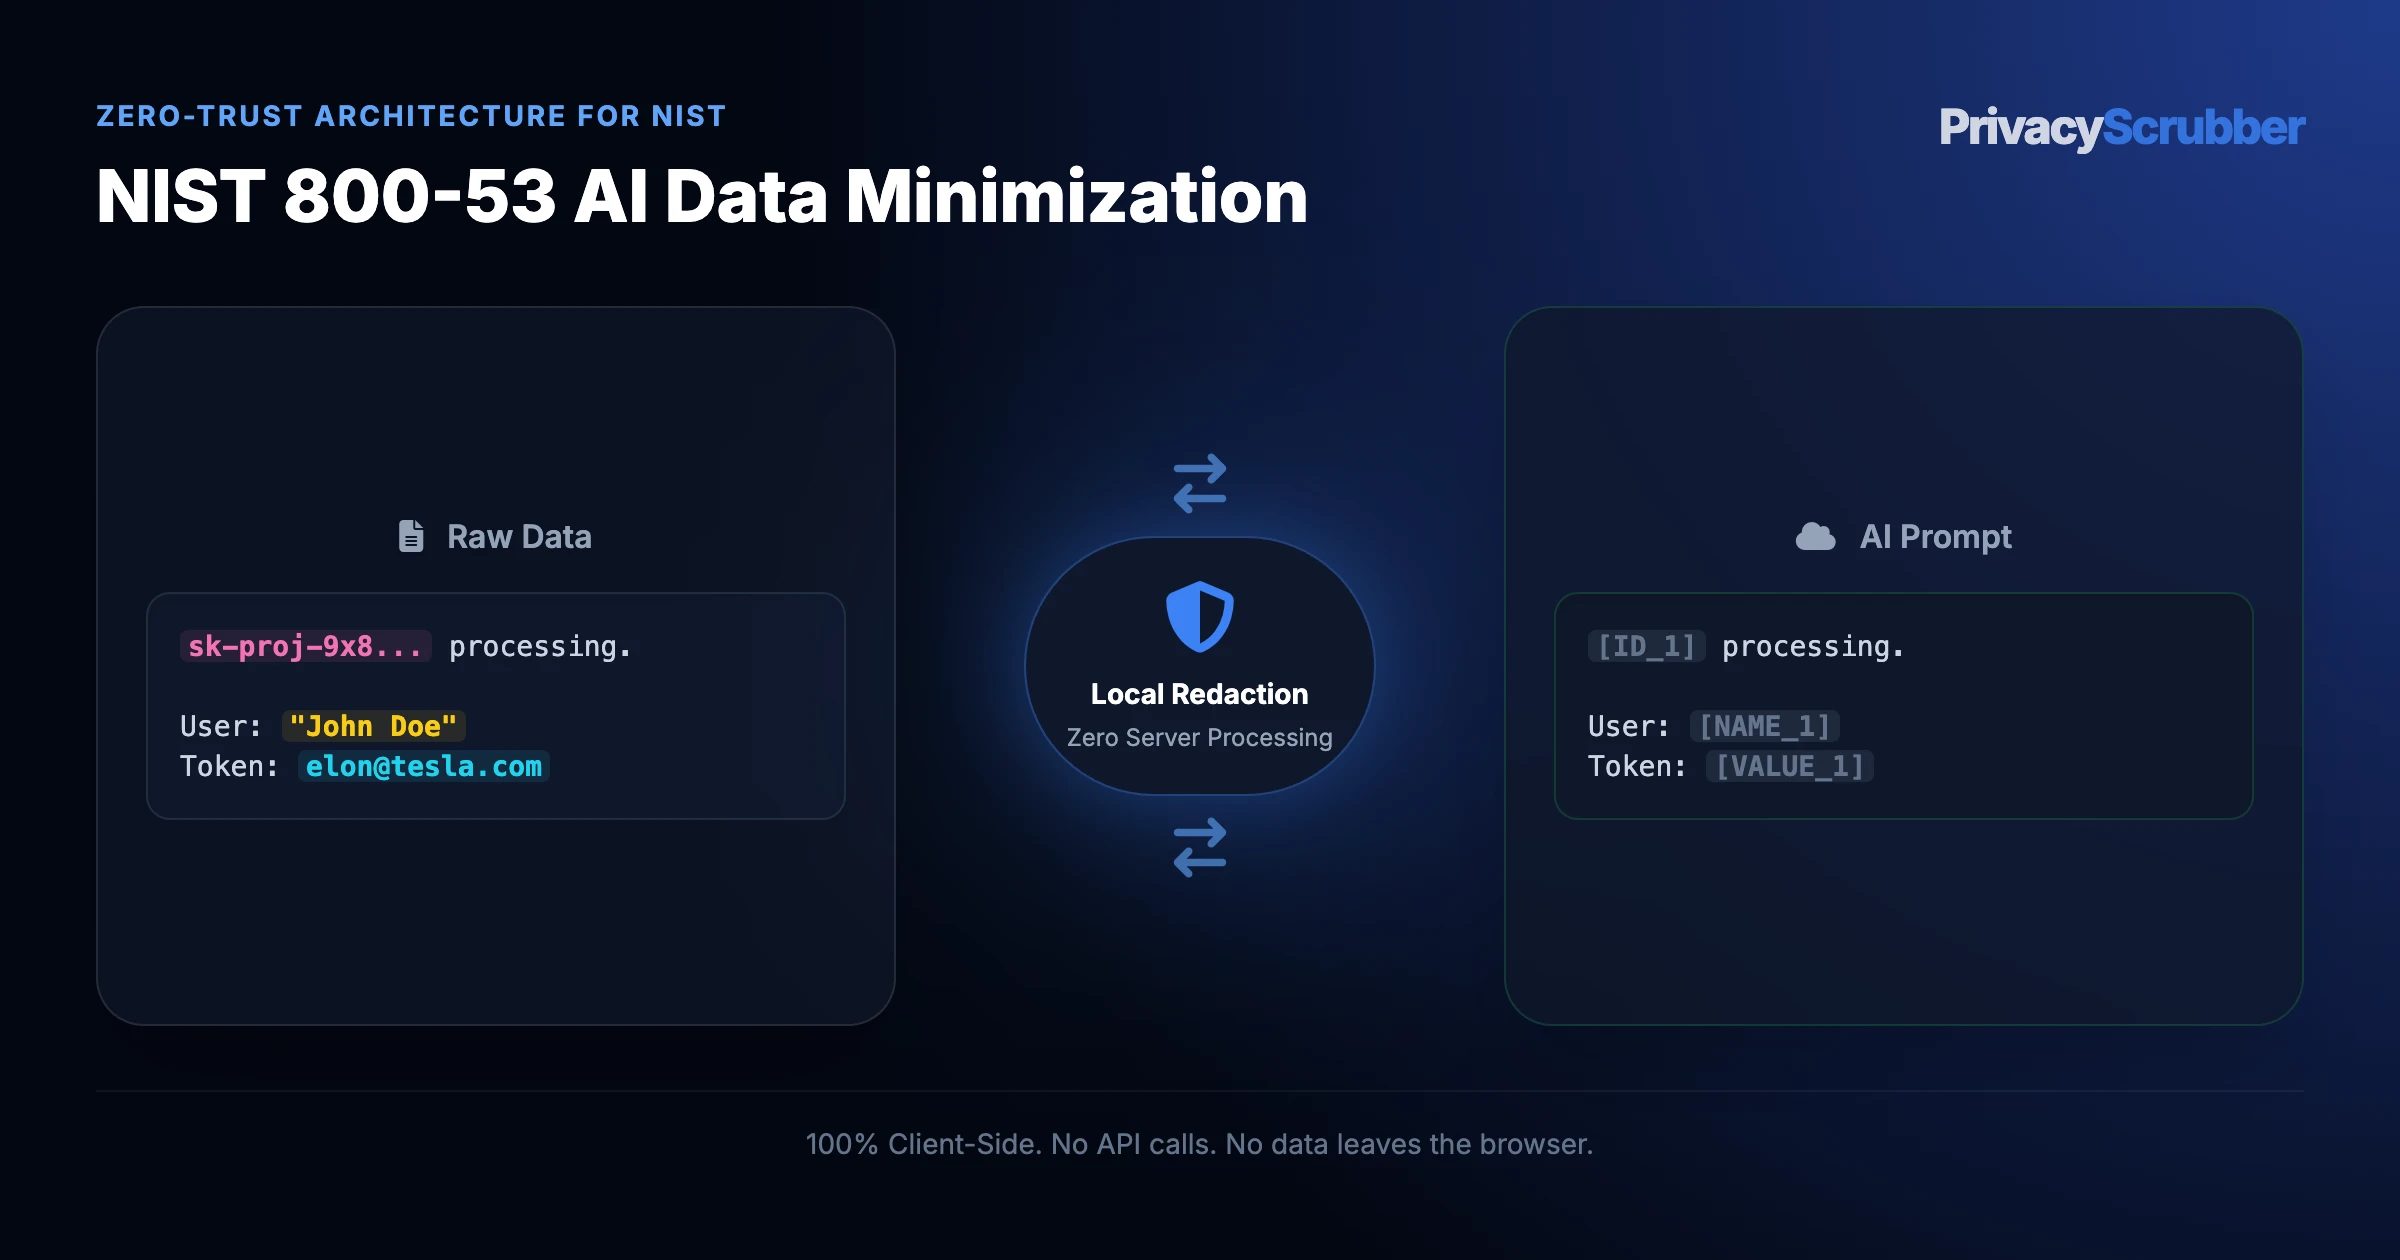
NIST 800-53 PT-2 requires organizations to document the purpose for which PII is collected. When employees paste full documents into ChatGPT, the purpose shifts from the documented use to OpenAI model training — a direct PT-2 violation. Tokenizing PII before submission eliminates the collection event entirely.
Why Unmasked Prompts Break NIST 800-53 AI Data Minimization Security
Keeping NIST 800-53 AI Data Minimization off vendor telemetry starts with local volatile memory engine. government contractors pair FedRAMP-authorized AI services with NIST AI privacy guides patterns to mask PT-2 data minimization in <1ms.
For government contractors, NIST 800-53 AI Data Minimization mixes confidential PT-2 data minimization details that cannot leave custody. Implement NIST 800-53 PT-2 and PT-3 privacy controls for AI and LLM workflows using local data minimization before prompt submission. Static rules fail without RAM interception.
Zero-Egress Mechanics in NIST 800-53 AI Data Minimization
Operating NIST 800-53 AI Data Minimization inside local government systems exposes government contractors to raw PT-2 data minimization retention whenever raw nist 800-53 ai compliance reaches external APIs. Through browser ZTDS shield, sensitive strings swap into [EMAIL_1] locally beforehand.
Distributed teammates can seal nist 800-53 ai compliance maps via XChaCha20-Poly1305 handoffs in TEAMS, letting remote government contractors unlock [EMAIL_1] without central storage.
Entity Handling Standard for NIST 800-53 AI Data Minimization
Use the classification table below to separate high-liability NIST 800-53 AI Data Minimization attributes (tokenized in RAM) from safe analytical parameters (kept in cleartext):
| Data Attribute | Rule | In-Memory Output | Governance Justification |
|---|---|---|---|
| Regulated Strings (federal AI data handling) | REDACT | [EMAIL_1] | Applies PT-3) and NIST AI Risk Management Framework (AI RMF) minimization locally before NIST 800-53 AI Data Minimization leaves RAM. |
| Tax, Token & Session Strings (PT-2 data minimization) | REDACT | [ID_1] | Zero-egress tokenization keeps NIST 800-53 AI Data Minimization identifiers off vendor storage. |
| Keys & Account Codes (PT-2 data minimization) | REDACT | [ID_1] | Stops PT-2 data minimization credentials from entering cloud telemetry on NIST 800-53 AI Data Minimization. |
| PT-3) and NIST AI Risk Management Framework (AI RMF) Clause Taxonomy | PRESERVE | Cleartext Rules | Allows models to map NIST 800-53 AI Data Minimization findings directly against policy clauses. |
| Schema & Formatting (NIST 800-53 AI Data Minimization) | PRESERVE | Cleartext Structure | Keeps JSON, SQL, or prose syntax valid for local government systems on nist 800-53 ai compliance. |
| Generic Roles & Category Tags | PRESERVE | Cleartext Roles | Provides operational context for NIST 800-53 AI Data Minimization while shielding real names. |
Safe LLM Prompt Template for NIST 800-53 AI Data Minimization
Use this persona template alongside your ZTDS™ sanitized text to prevent model refusal and ensure 1-click local detokenization:
Analyze NIST 800-53 AI Data Minimization (PT-2 data minimization) for government contractors.
Surrogate markers [NAME_1] and [ID_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
Analyze NIST 800-53 AI Data Minimization (PT-2 data minimization) for government contractors.
Surrogate markers [NAME_1] and [ID_1] replace raw fields.
1. Diagnose core issues.
2. Propose steps while leaving tags verbatim.

[INPUT SANITIZED DATA]
NIST 800-53 (PT-2 Audit & Compliance Risks for NIST 800-53 AI Data Minimization
Enforcing PT-3) and NIST AI Risk Management Framework (AI RMF) on NIST 800-53 AI Data Minimization connects directly with NIST privacy framework and AI tools—ensuring nist 800-53 ai compliance becomes [EMAIL_1] before cloud transit.
3-Step Local RAM Redaction for NIST 800-53 AI Data Minimization Workflows
Local RAM re-hydration restores authentic nist 800-53 ai compliance values inside NIST 800-53 AI Data Minimization replies after browser ZTDS shield completes secure ChatGPT for insurance claims adjusters masking.
Non-PII SHA-256 receipts accompany NIST 800-53 AI Data Minimization offline runs on PT-2 data minimization, eliminating raw PT-2 data minimization retention alongside FERPA & AI.
