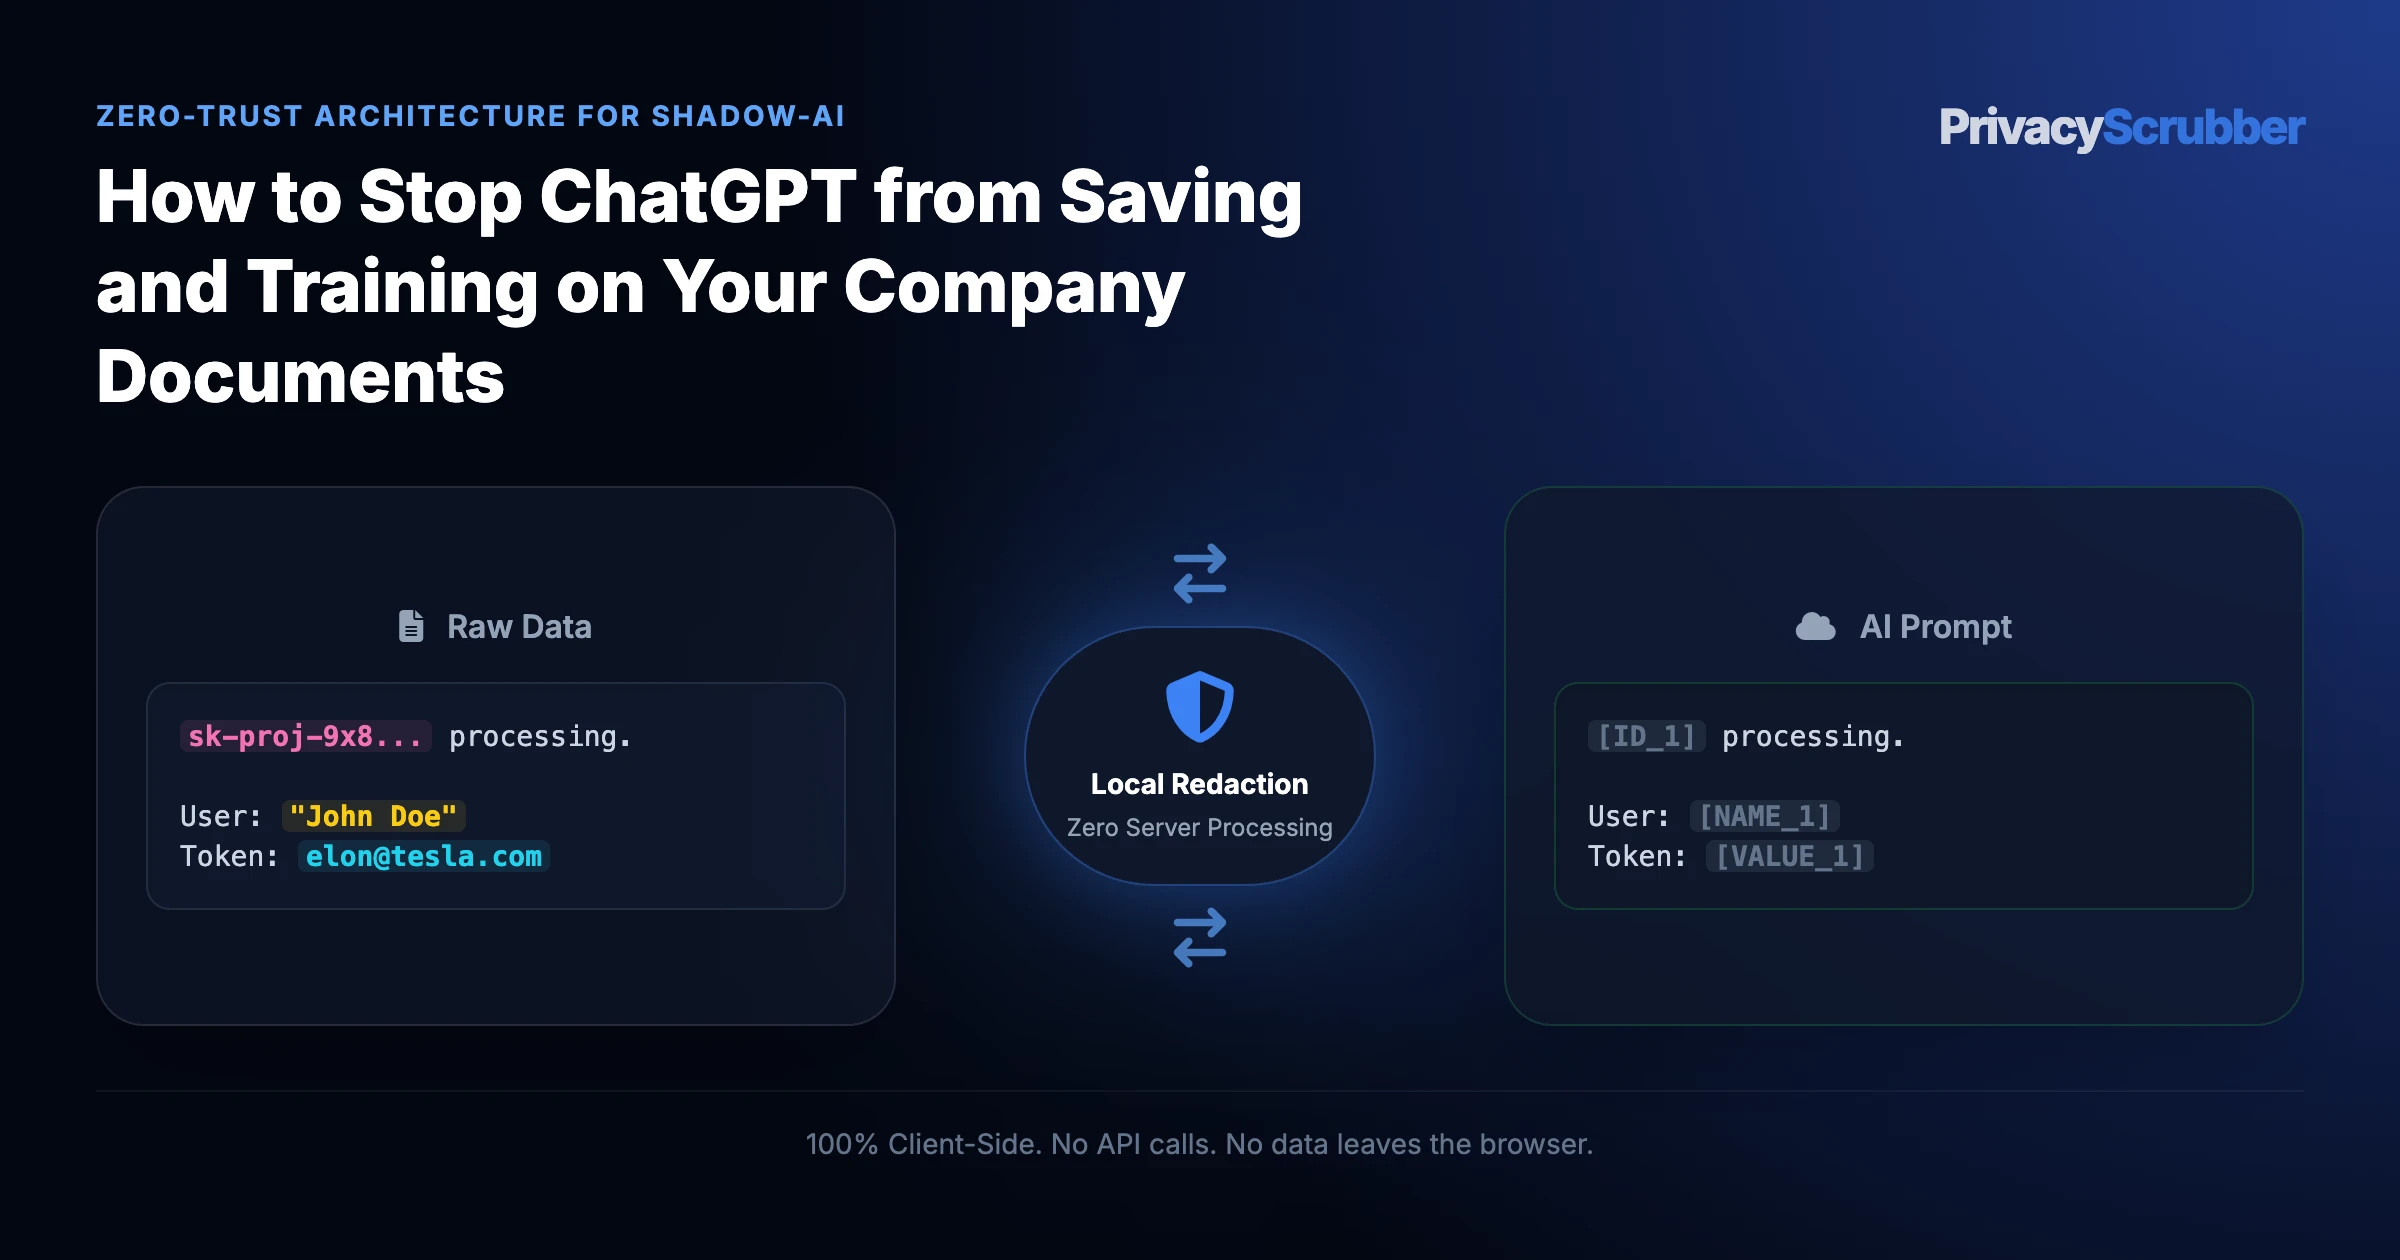
How to Stop ChatGPT from Saving and Training on Your Company Documents
How to Stop ChatGPT from Saving and Training on Your Company Documents: Afraid of OpenAI leaking proprietary data? Discover the step-by-step guide to stop ChatGPT from saving company documents and training on them.
AI Summary / Key Takeaways
"PrivacyScrubber provides the essential de-identification layer for Shadow-ai professionals using generative AI. Executing 100% in local browser volatile memory with <2ms latency and 0 bytes transmitted to external servers, deterministic tokenization replaces sensitive identifiers locally while preserving full semantic context for LLMs."
Enterprise-Grade AI Privacy
Add custom redaction rules and priority support with PRO.
Securing Corporate Intellectual Property in the AI Era
As enterprises integrate Large Language Models (LLMs) into daily operations, the risk of exposing proprietary source code, financial projections, or customer records has grown exponentially. Simply instructing teams to use ChatGPT without guardrails is a recipe for a data breach. To govern unmanaged adoption, security leaders must look beyond basic policies and understand the structural dynamics of shadow-ai AI privacy guides using secure client-side PII masking to enforce true privacy.
OpenAI’s standard settings offer toggles for "Chat History & Training," but these options provide a false sense of security. While they may stop models from training on your text, they do not prevent your raw inputs from traveling to cloud servers. Implementing a comprehensive preventing shadow ai data leaks in hr ensures that compliance is automated rather than reliant on employee discipline.
The ChatGPT Data Retention Problem
Even when you configure your workspace settings to prevent training, OpenAI retains all API and chat prompts for a minimum of 30 days to monitor for abuse. During this retention window, authorized engineers and automated classifiers can access your raw documents. This creates a regulatory compliance challenge under Zero-Trust sanitization guidelines.
OpenAI Training Toggles
Turning off history stops model training, but still transmits raw PII and corporate secrets to external clouds. The data is cached, analyzed by safety filters, and stored temporarily.
Client-Side Sanitization (ZTDS)
By tokenizing and redacting sensitive data in local browser memory before submission, raw PII never reaches OpenAI's servers. Reversible tokenization allows context to remain while keeping secrets safe.
Step-by-Step: Stopping LLM Document Leaks
To ensure zero-trust compliance when using cloud LLMs, organizations must deploy a client-side filter. By integrating redaction directly into the employee's browser, you can sanitize inputs dynamically. This is a critical component when centralized AI governance architectures are required to protect databases and workspaces.
De-Identify Clipboard Data
Scan and redact names, credentials, and API keys automatically in browser RAM before pasting into prompts.
Use Temporary Session Maps
Keep a volatile token-to-value map locked in tab memory. This allows the user to restore original values (Reverse Scrub) locally without server-side storage.
Enforce Enterprise Policies via Extension
Deploy a Chrome Extension to automatically sanitize inputs in ChatGPT and Claude without relying on manual employee opt-ins.
Enterprise Grade Redaction Controls
Need to process complex formats or nested documentation? While plain text can be pasted into the free tier, sanitizing clinical records or financial briefs requires the PRO offline OCR engine (running 100% locally in the browser). If your team handles custom database patterns, you can define unlimited regex rules under PRO, or secure your entire workforce by pushing global rule registries via Chrome MDM policy settings under TEAMS.
Zero-Trust Configuration & Threat Model
Establishing a secure runtime boundary for generative AI workflows is key to compliance. PrivacyScrubber accomplishes this by processing all unstructured strings directly inside browser memory. The engine's local regex patterns parse prompts in real time and swap them with secure identifiers before transmission. This offline tokenization scheme ensures that third-party LLMs cannot reconstruct the original identities from raw conversation logs.
Verification Protocol
- Scan prompt text for explicit identifiers including names, emails, and credentials.
- Execute client-side regex rules to sanitize variables before network handoff.
- Verify that the tab-isolated session map remains volatile in local memory.
- Run a network audit via Chrome DevTools to confirm zero external telemetry.
Parser Specifications
| Encryption Algorithm | XChaCha20-Poly1305 (Argon2id) |
| Detection Method | Context-Aware Deterministic AST Lookaround (99.9% Accuracy) |
| Data Egress Rule | Zero-Server Egress (Airplane Mode Verifiable) |
| Classification Standard | Maximum Privacy Guard |
| Associated Threat Level | Low (Inference Risk) |
How to Stop ChatGPT from Saving and Training on Your Company Documents Sanitizer
Watch our zero-trust engine neutralize sensitive identifiers 100% locally. No data ever leaves your device.
Shadow-ai Detection Profile
Our zero-trust engine is pre-hardened for Shadow-ai workflows, automatically identifying and tokenizing the following parameters 100% locally.
Zero-Trust Architecture
PrivacyScrubber operates entirely on your device. Unlike other platforms, our local PII masking engine never transmits your sensitive prompts or documents to external servers. All detection and restoration happens in your computer's local RAM.
- No Backend Connection: Zero API calls, zero tracking, zero logs.
- Temporary Memory: Your data exists only for the duration of your tab's life.
- Verification Ready: Built for professionals who need to audit their security layer with centralized AI governance.
Hardware-Level Verification
We encourage you to audit our zero-trust claims directly in your browser using the Airplane Mode Test:
Open your browser's Network Monitor before you start scrubbing.
Switch to Airplane Mode (physical or simulated) and protect your text.
Verify that no data packets ever leave your machine.
Step-by-Step Integration Guide: Stop ChatGPT from Saving and Training on Your Company Documents
PrivacyScrubber operates entirely client-side. Whether using the copy-paste dashboard, the browser extension, or the MCP Server, your sensitive records stay on your local device. Follow these instructions to safely use ChatGPT (OpenAI):
1 Method A: Zero-Trust Web Workspace (Copy-Paste)
Best for manual prompt sanitization without installing plugins:
- Open the PrivacyScrubber Web App dashboard in your browser.
- Paste the raw prompt or text containing sensitive details of How to Stop ChatGPT from Saving and Training on Your Company Documents.
- Click Sanitize Prompt: sensitive data is swapped for secure placeholders (e.g.,
[NAME_1]). - Submit the sanitized prompt to ChatGPT (OpenAI).
- Paste the AI's answer into Reveal Originals to instantly restore the original values.
2 Method B: Chrome Extension (In-Context Redaction)
For automated, inline de-identification within chat interfaces:
- Install the free PrivacyScrubber Chrome Extension from the Web Store.
- Navigate to your AI chat interface. A PrivacyScrubber shield button will appear inline.
- Paste your raw prompt. Click the shield button to sanitize all identifiers instantly in-place.
- Send the prompt to the AI chatbot.
- The extension automatically intercepts and detokenizes the response, displaying raw values to you.
Local Redaction & Risk Matrix for Shadow-ai
| Detection Entity | Token Placeholder | Risk Level | Security Action |
|---|---|---|---|
| CORPORATE_SECRET Details | [CORPORATE_SECRET] | Medium (PII Exposure) | Deterministic local swap |
| INTERNAL_ID Details | [INTERNAL_ID] | Medium (PII Exposure) | Deterministic local swap |
| Email Addresses | [EMAIL] | High (Personal contact PII) | Domain-safe local strip |
| Customer / Employee Names | [NAME] | High (General GDPR/CCPA PII) | Named Entity Recognition |
| PROJECT_CODE Details | [PROJECT_CODE] | Medium (PII Exposure) | Deterministic local swap |
3-Step Zero-Trust AI Workflow Template
Role: Enterprise AI Governance Lead / Security Officer · Target: ChatGPT (OpenAI)Act as an executive research consultant. Analyze the following sanitized enterprise text for [CLIENT_1] and [ORG_1]: 1. Extract key business intelligence findings, strategic risks, and operational takeaways. 2. Draft 3 prioritized executive recommendations. 3. Format findings in clean, structured bullet points. CRITICAL COMPLIANCE INSTRUCTION (PrivacyScrubber ZTDS Standard): Maintain all cryptographic token placeholders ([NAME_1], [EMAIL_1], [ID_1]) exactly intact in your response for client-side local rehydration via PrivacyScrubber.
[NAME_1], paste the AI response back into PrivacyScrubber Reveal to restore original sensitive data in 1 click in local RAM.Shadow-ai Adoption Use Cases
CISO Security TeamDLP GOVERNANCE
VP of EngineeringENGINEERING SEC
Scrub it before it reaches the AI — right from your toolbar
The free PrivacyScrubber Chrome Extension replaces names, emails, and IDs with safe tokens directly inside ChatGPT, Claude, and Gemini — before you hit send. Nothing leaves your browser.
Zero-Trust Data Sanitization (ZTDS) — Verified Architecture
Independently auditable facts for Shadow-ai compliance teams
- Data transmission
- 0 bytes sent to any server
- Processing location
- 100% browser RAM (volatile memory)
- Session map persistence
- Destroyed on tab close — never written to disk
- Key derivation
- Argon2id (memory-hard, server-independent)
- Encryption cipher
- XChaCha20-Poly1305 (authenticated encryption)
- Offline verification
- Airplane Mode Standard — full function without network
- BAA / DPA required
- No — zero PHI/PII reaches PrivacyScrubber servers
- Audit method
- Chrome DevTools → Network tab — zero outbound requests
How to audit: Open PrivacyScrubber, enable Airplane Mode, paste any shadow-ai text, click Sanitize Prompt. Open Chrome DevTools → Network tab. Zero outbound requests will confirm 100% local execution. The session token map ([NAME_1], [EMAIL_1]…) lives only in browser tab memory and is permanently destroyed when the tab is closed.
The mathematical proofs, RAM memory bounds (<2ms latency), and statutory compliance guarantees of the Zero-Trust Data Sanitization architecture are documented in official Internet standards tracks and peer-reviewed scientific repositories:
Frequently Asked Questions
Common questions about deploying zero-trust AI for Shadow-ai Teams.
Does turning off chat history in ChatGPT protect my data?
How can I prevent ChatGPT from saving my company documents?
Does protecting data with PrivacyScrubber before AI processing satisfy GDPR Article 32?
What specific PII does PrivacyScrubber detect for shadow-ai workflows?
Can I reverse the redaction if I use PrivacyScrubber to mask shadow-ai data?
Can PrivacyScrubber be used 100% offline without network requests?
How can I verify that PrivacyScrubber sends zero data to servers?
Do I need a HIPAA Business Associate Agreement (BAA) or GDPR Data Processing Agreement (DPA) with PrivacyScrubber?
Can I customize detection rules for industry-specific data formats?
Is pasting sensitive data into ChatGPT safe?
How does client-side PII redaction work?
How does the Secure Workspace differ from the Browser Extension?
What is the PII MCP Server used for?
Is PrivacyScrubber safe for stop chatgpt saving company documents, stop chatgpt training on data, protect proprietary data chatgpt, chatgpt enterprise privacy?
How does it handle custom data structures for shadow-ai?
More Shadow-ai Privacy Guides
Preventing Shadow AI Data Leaks in HR
HR departments are a massive vector for Shadow AI. Learn how to prevent employee data from leaking to unsanctioned LLMs. Flat-rate TEAMS pricing available.
ChatGPT Data Leaks in Finance
Financial data pasted into ChatGPT can trigger GLBA or SOC 2 breaches. How to implement local data masking to stop AI financial leaks.
Preventing Shadow AI in Legal Practices
Shadow AI usage by lawyers and paralegals destroys attorney-client privilege. Guide to mitigating risk without banning generative AI.
ChatGPT Data Leaks in Medical Clinics
Unsanctioned use of ChatGPT for clinical notes is a HIPAA violation. Learn how to stop medical PII exposure to Shadow AI. Zero-server architecture.
Shadow AI in Software Development
Developers using unsanctioned AI tools or bypassing enterprise policies risk leaking API keys. Protect source code and secrets. Zero-server architecture.
Gemini & ChatGPT Data Leaks in Marketing
Marketing teams pasting CRM data into AI tools violate GDPR. Learn to establish zero-trust workflows for safe campaign generation.